
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-39512-BigTreeCMS-v4.4.14-AccountTakeOver — Proof-of-concept exploit demonstrating unauthenticated CSRF-based account takeover via reflected DOM-XSS in BigTreeCMS v4.4.14 admin panel. | Kitploit
Tools/GitHubGitHub/giuseppesec/cve-2021-39512-bigtreecms-v4.4.14-accounttakeover
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHubgiuseppesec/cve-2021-39512-bigtreecms-v4.4.14-accounttakeover

CVE-2021-39512-BigTreeCMS-v4.4.14-AccountTakeOver

Proof-of-concept exploit demonstrating unauthenticated CSRF-based account takeover via reflected DOM-XSS in BigTreeCMS v4.4.14 admin panel.

View Repository
15 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

BigTreeCMS-v4.4.14-Unauthenticated-CSRF-AccountTakeOver

Unauthenticated CSRF Account TakeOver in BigTreeCMS v4.4.14

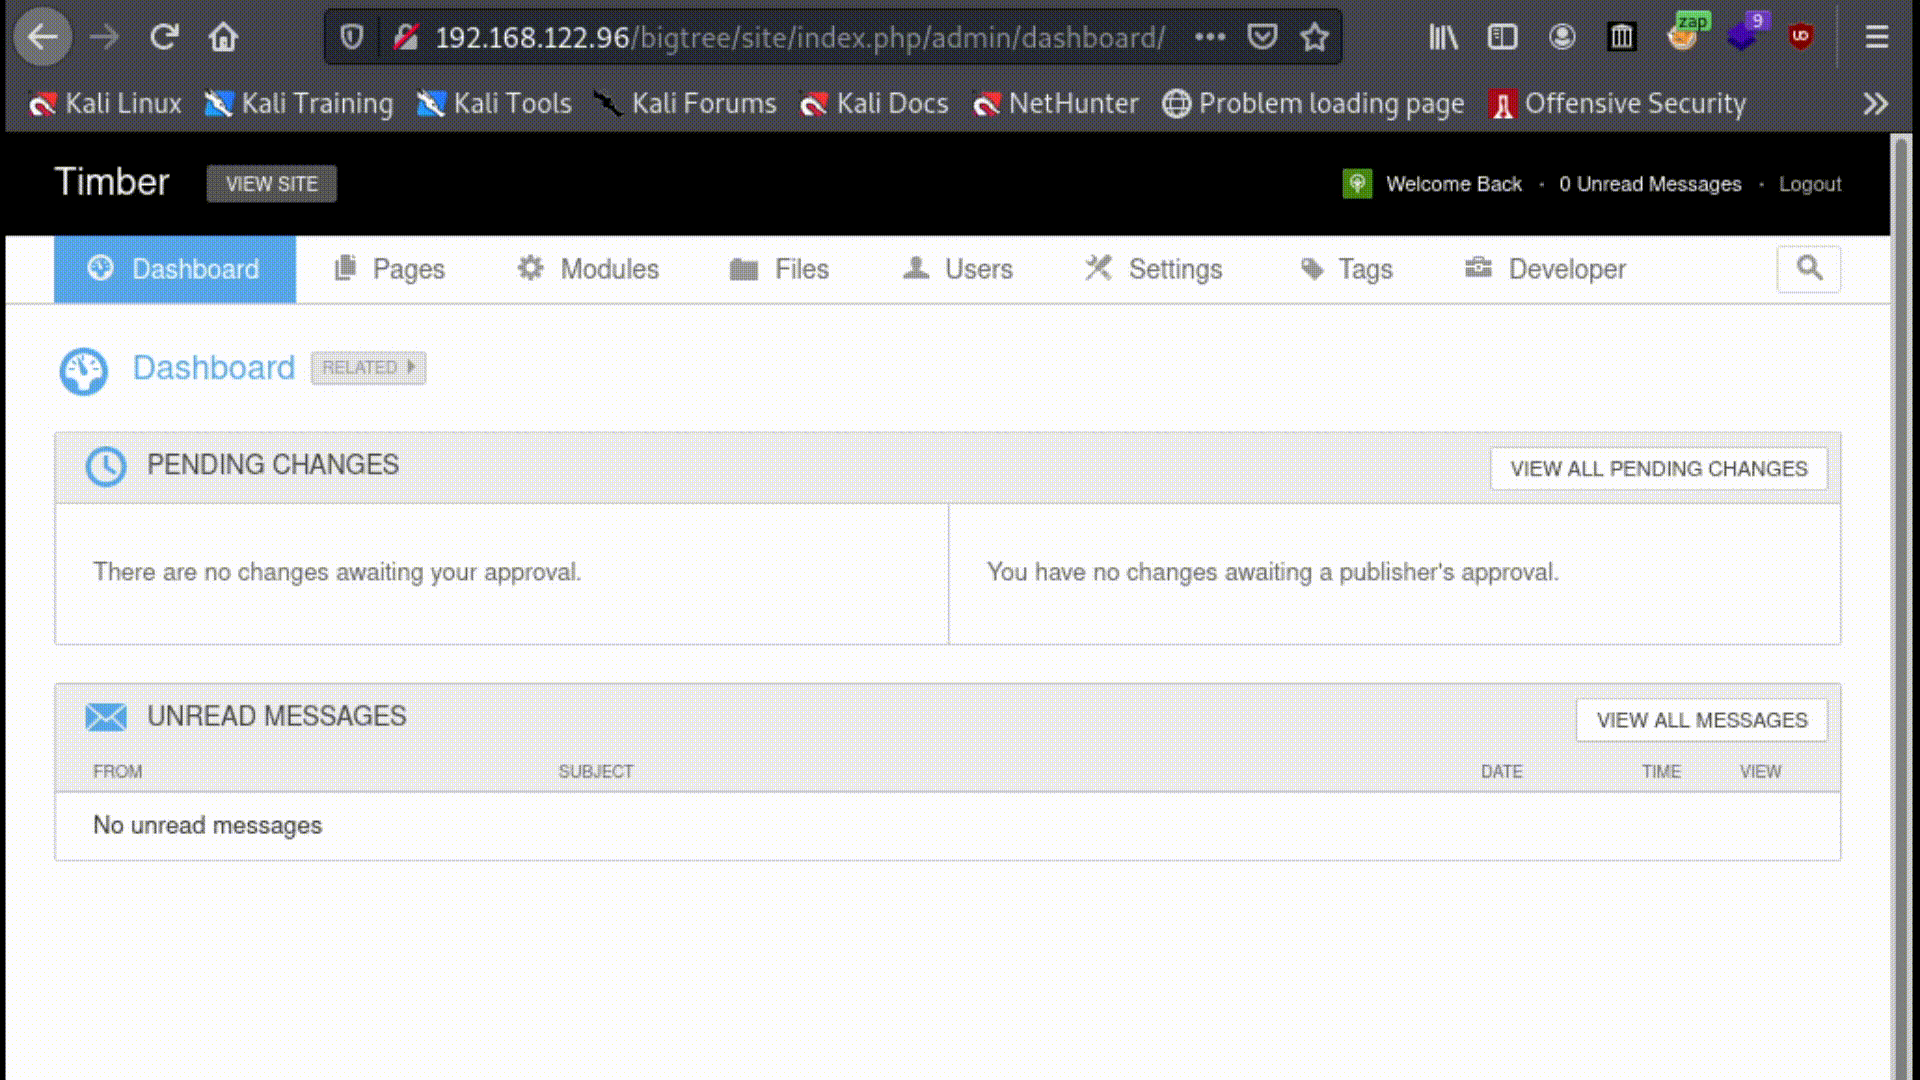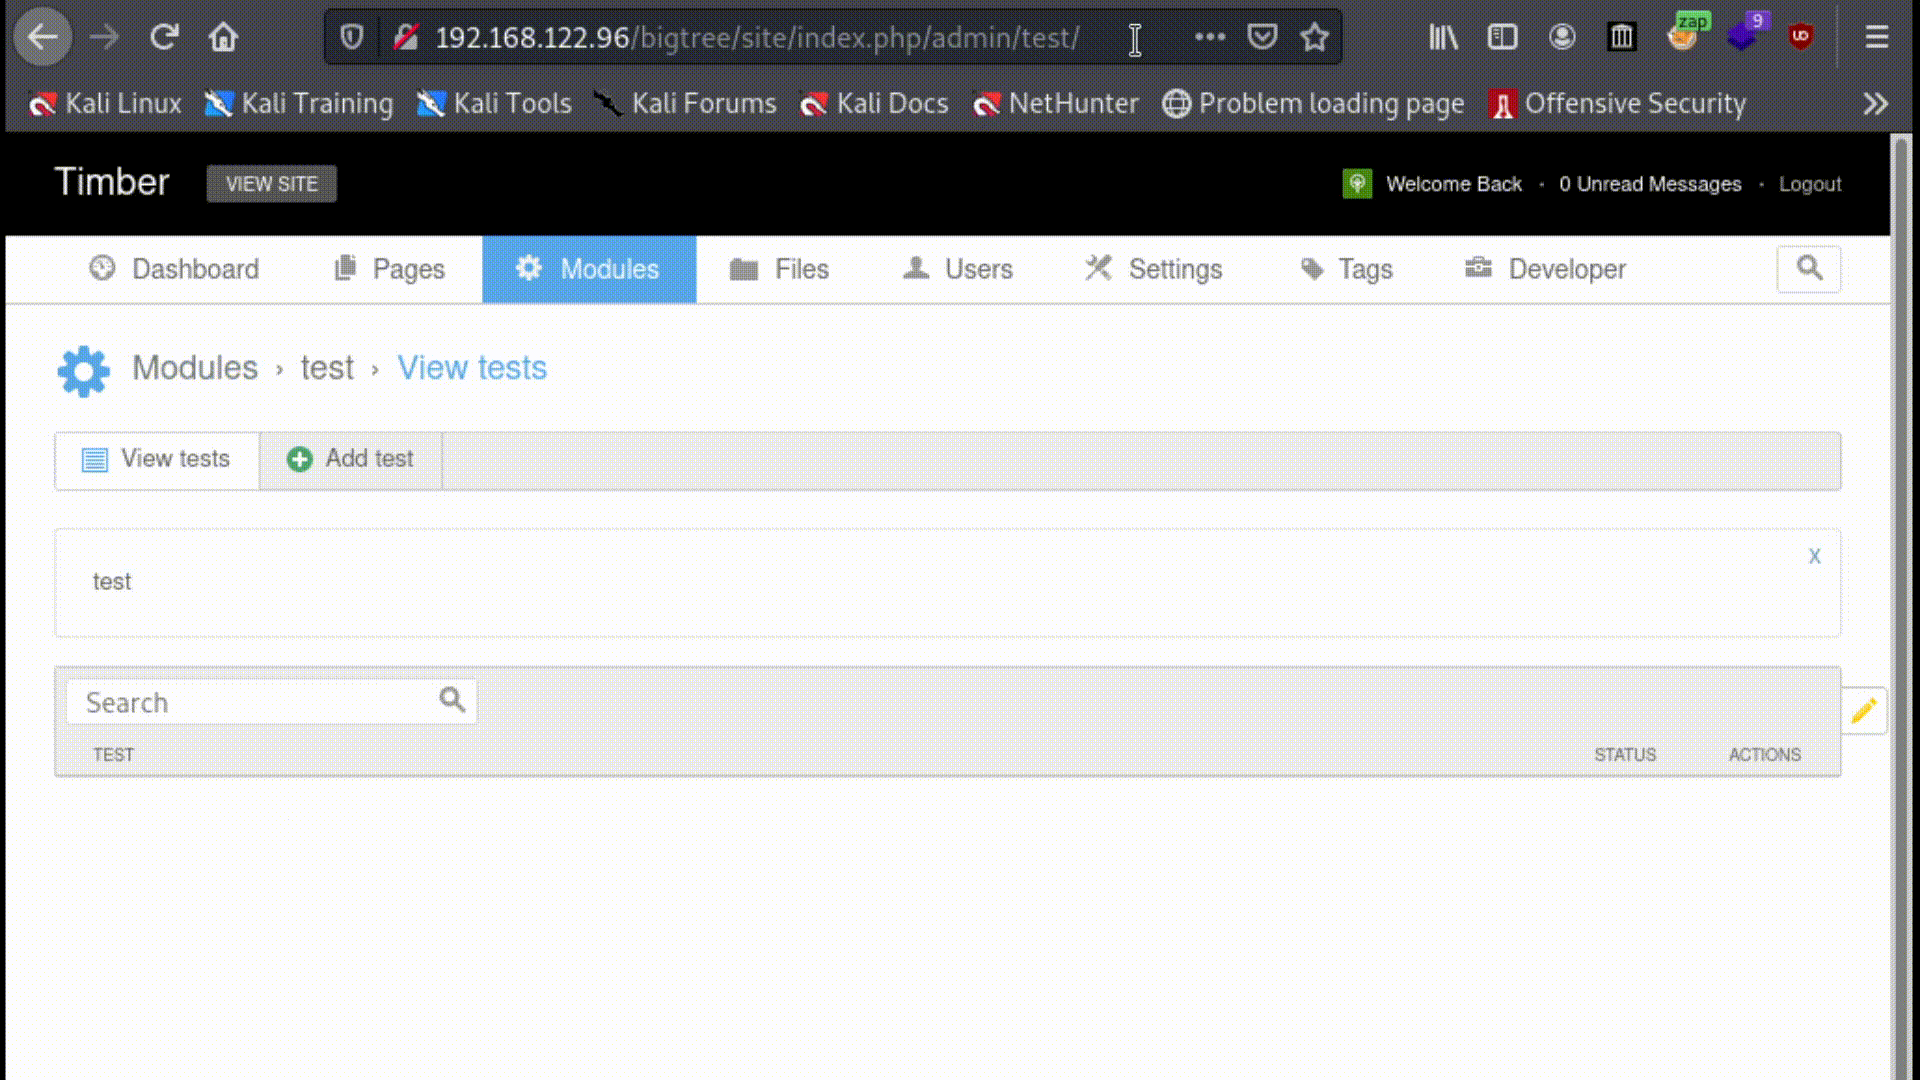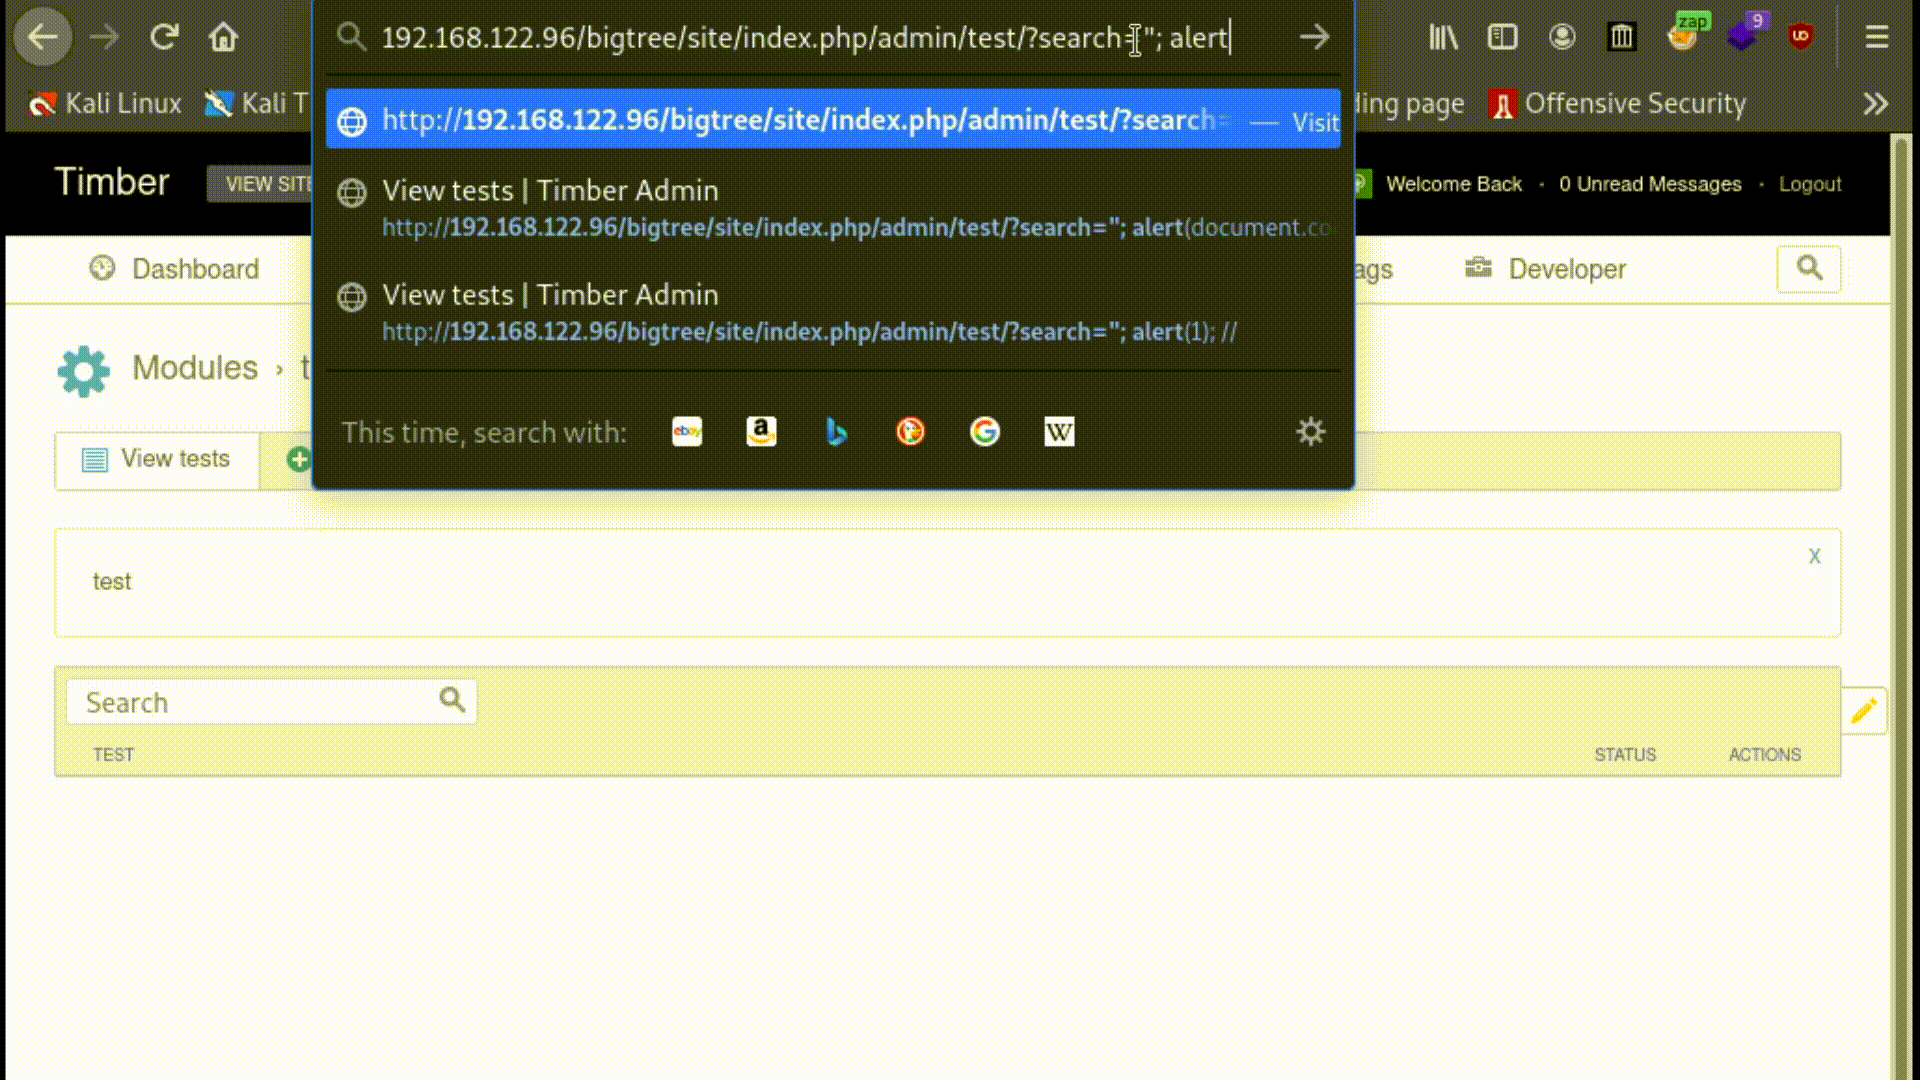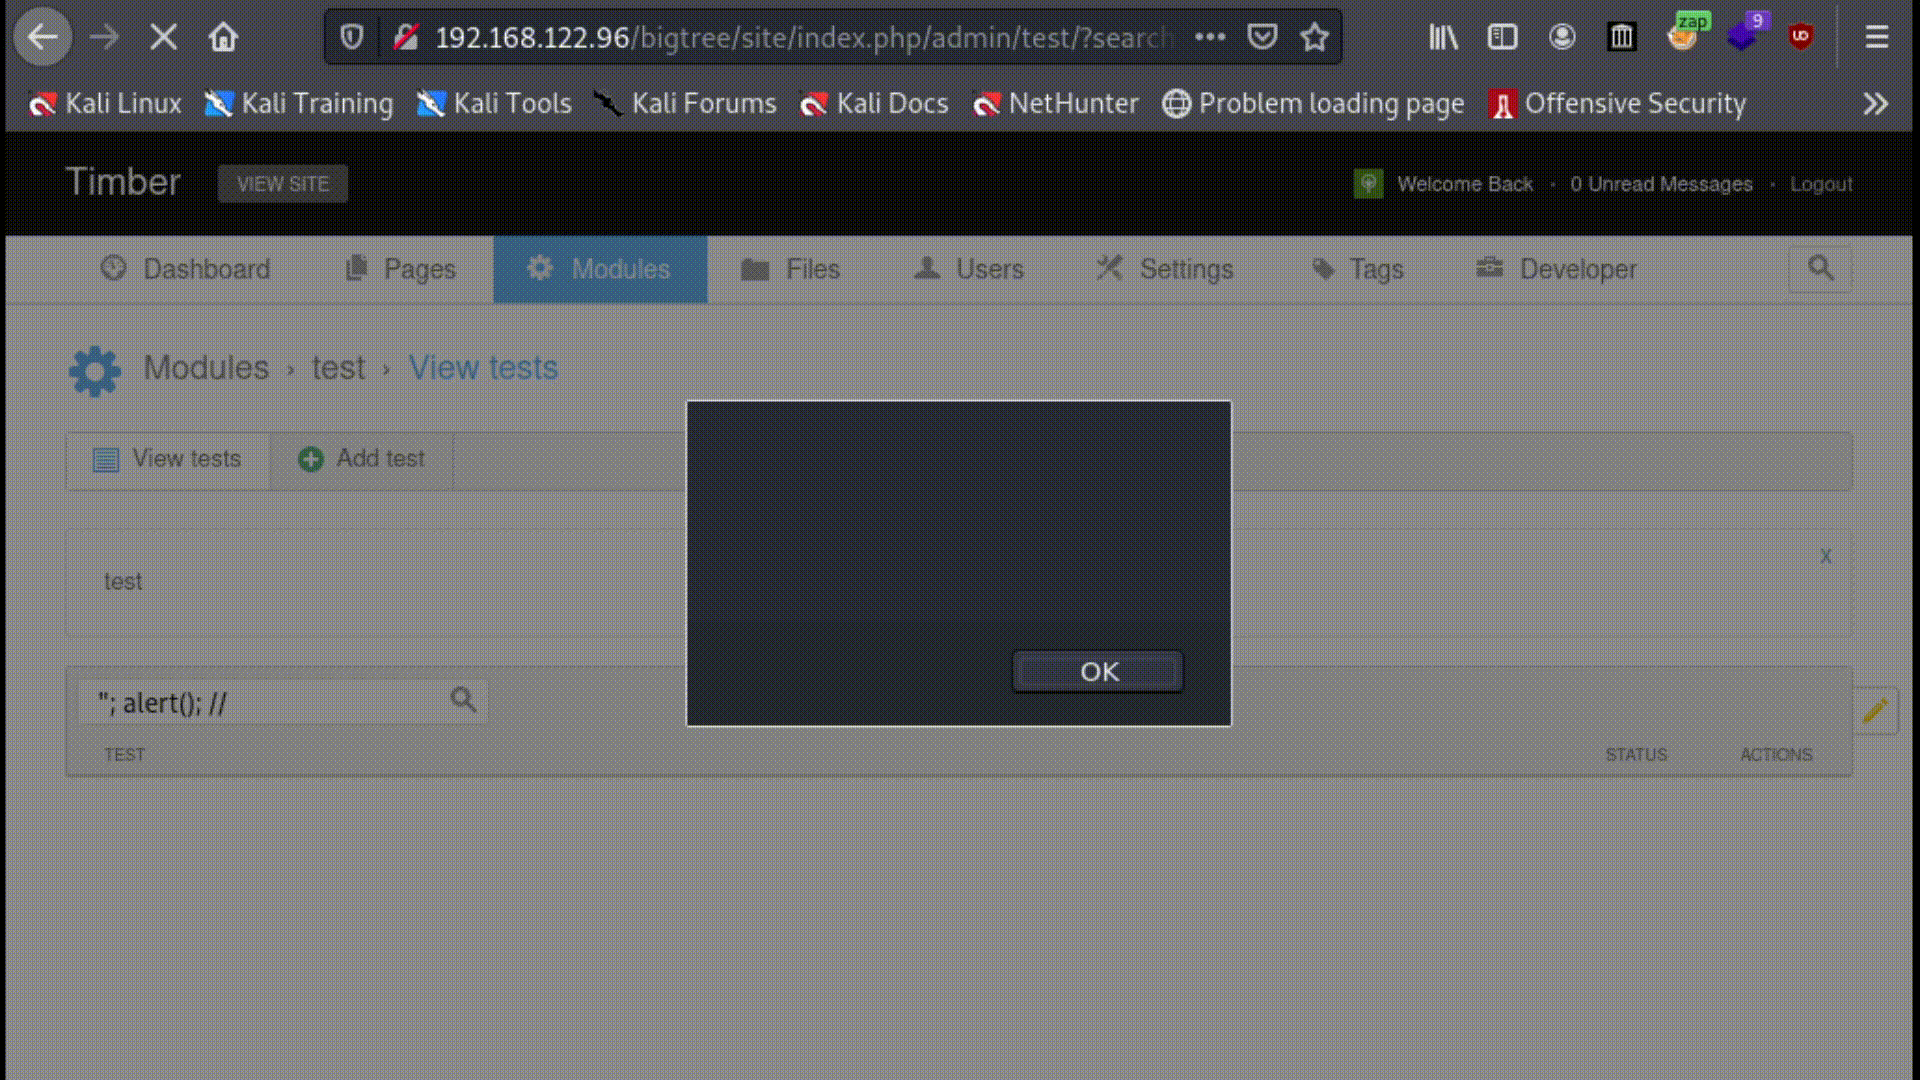
All searchable modules in the admin panel of BigTreeCMS v4.4.14 are vulnerable to reflected DOM-XSS via the URI. Search queries are reflected on the page without proper sanitization, leading to arbitrary javascript execution. CSRF Tokens are also stored within easily callable variables on all pages, making it possible for an unauthenticated attacker to forge a request as Administrator or Developer via clickjacking.

DOM-XSS

URI: /site/index.php/admin/{module_name}/?search={search_query}
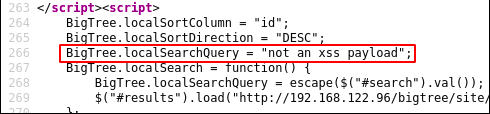
  • Search queries are reflected on the page and stored in the variable BigTree.localSearchQuery echoed search
  • This can be exploited with either a closing HTML tag, or by ending the declaration of the BigTree.localSearchQuery variable with "; and any arbitrary code. domxss

With this an attacker could create a clickjacking attack via an email, or a malicious link on a webpage they're hosting, that could forge requests as the targeted user. csrf
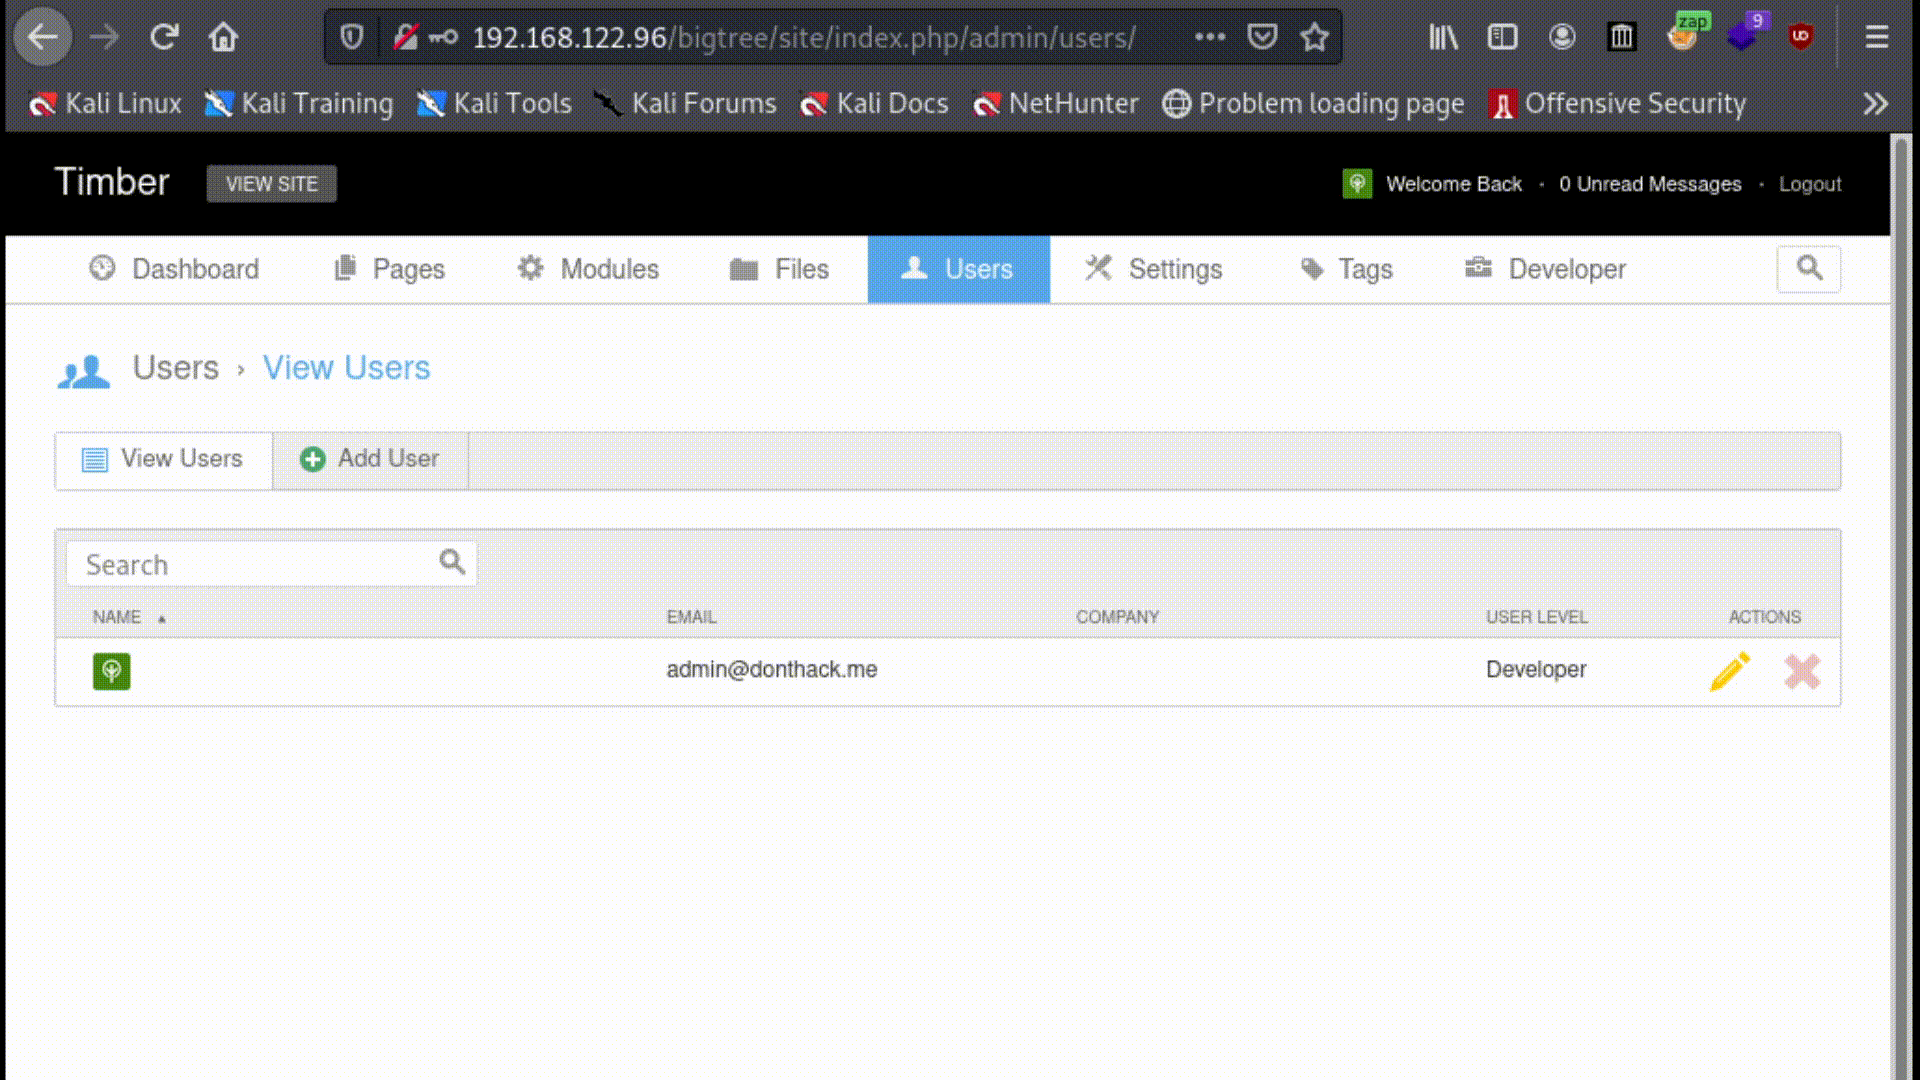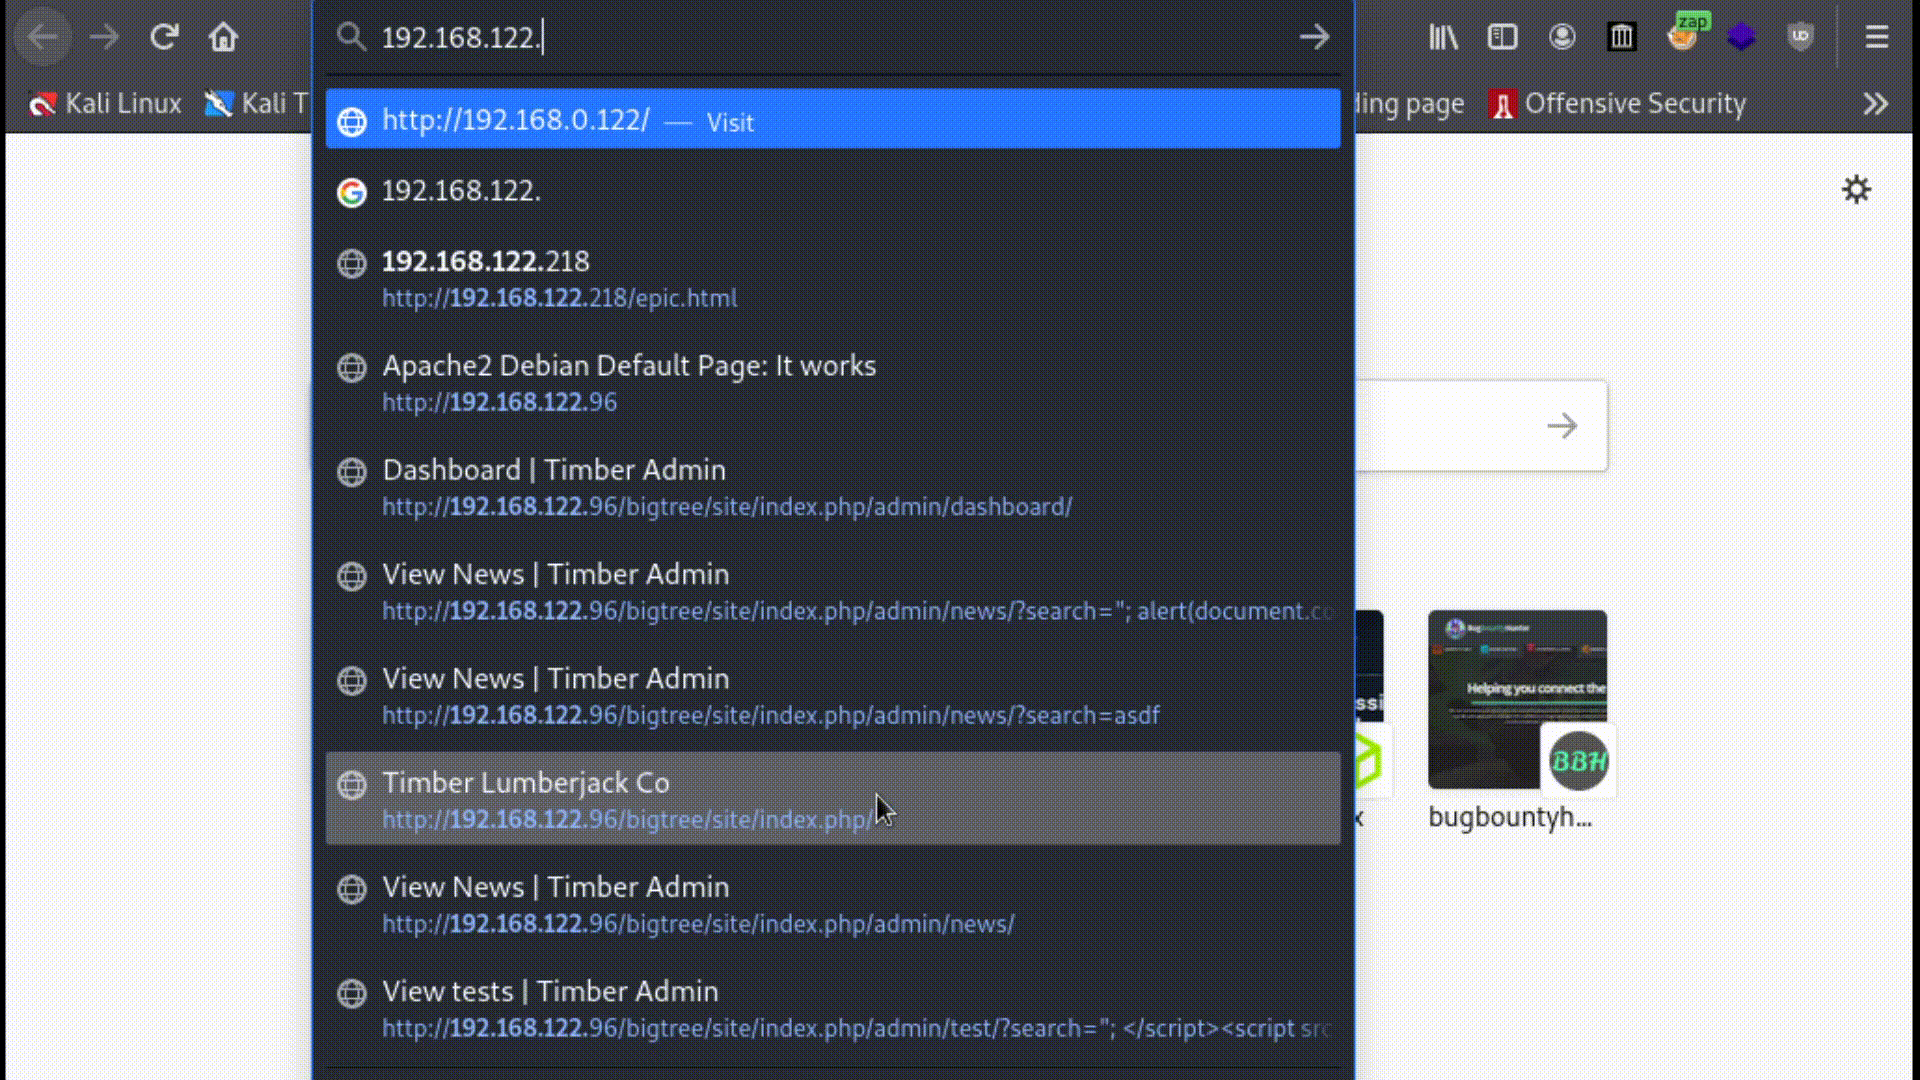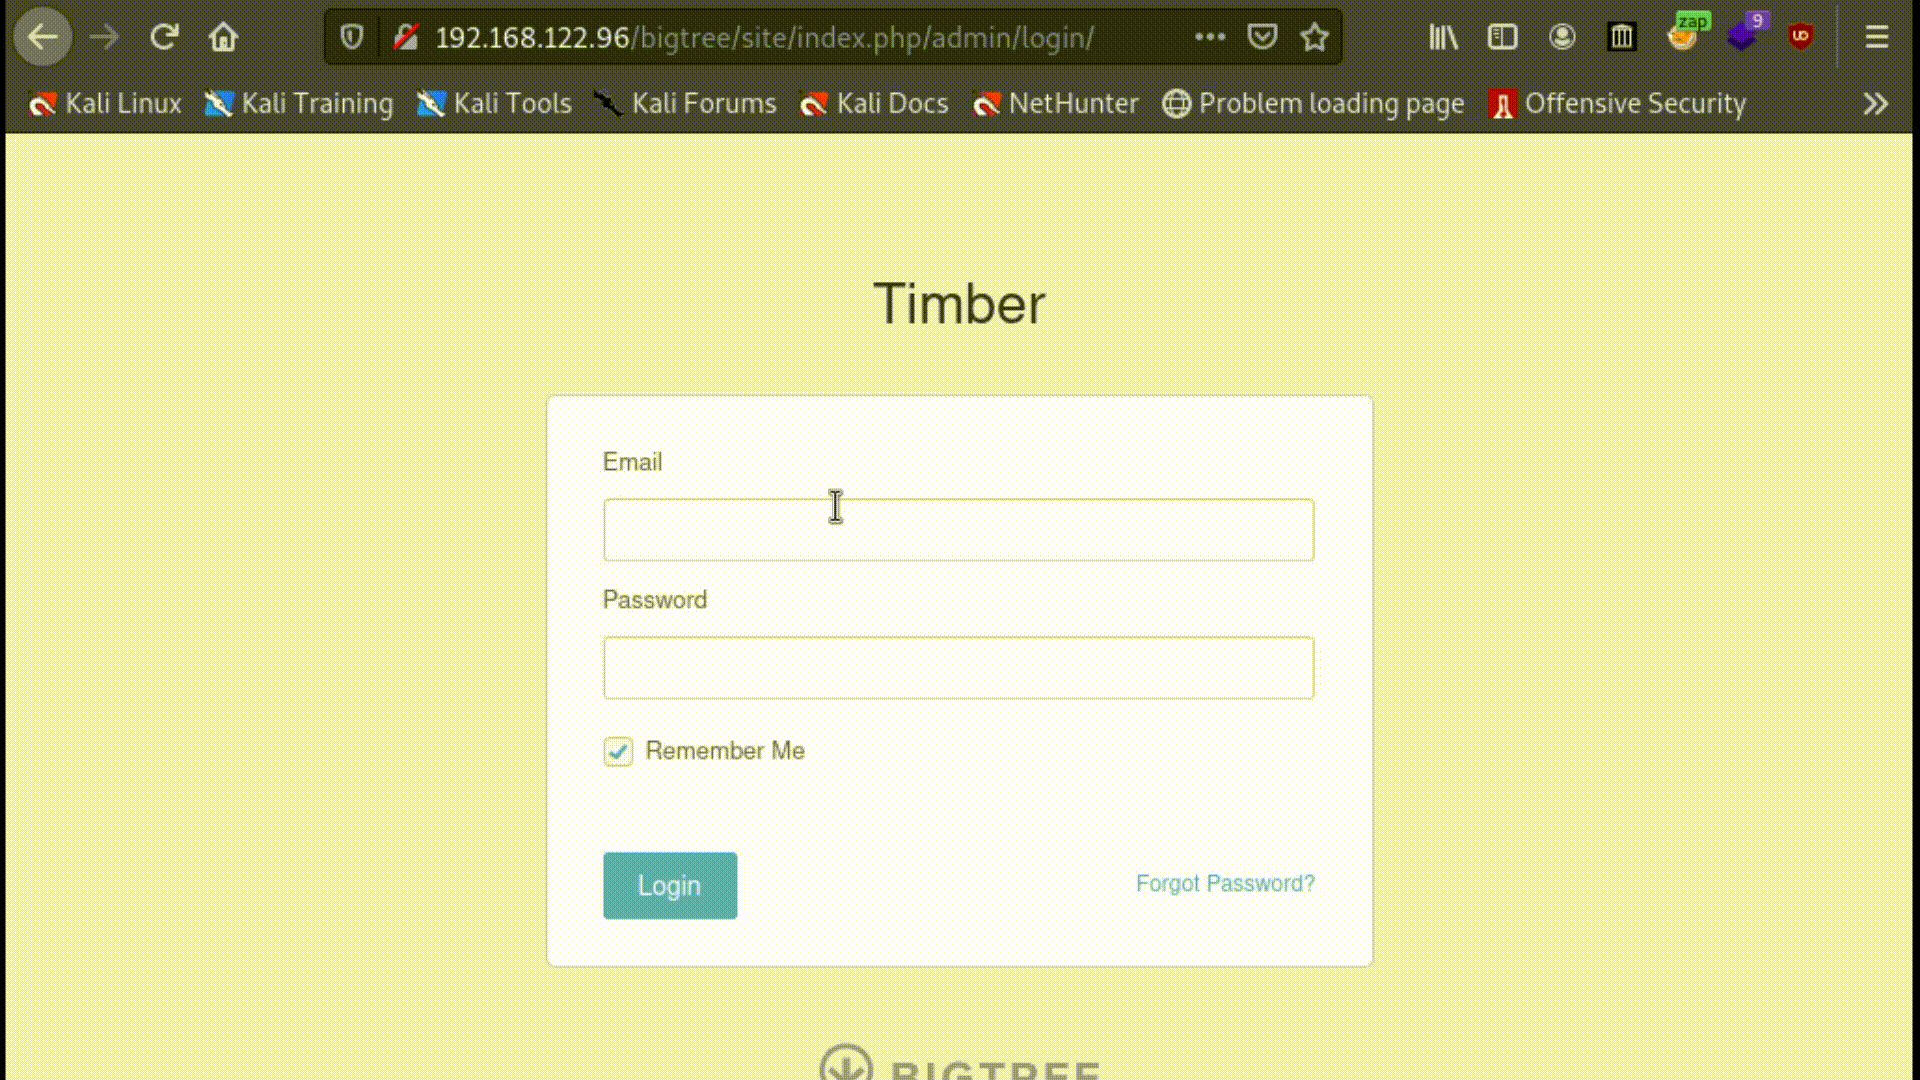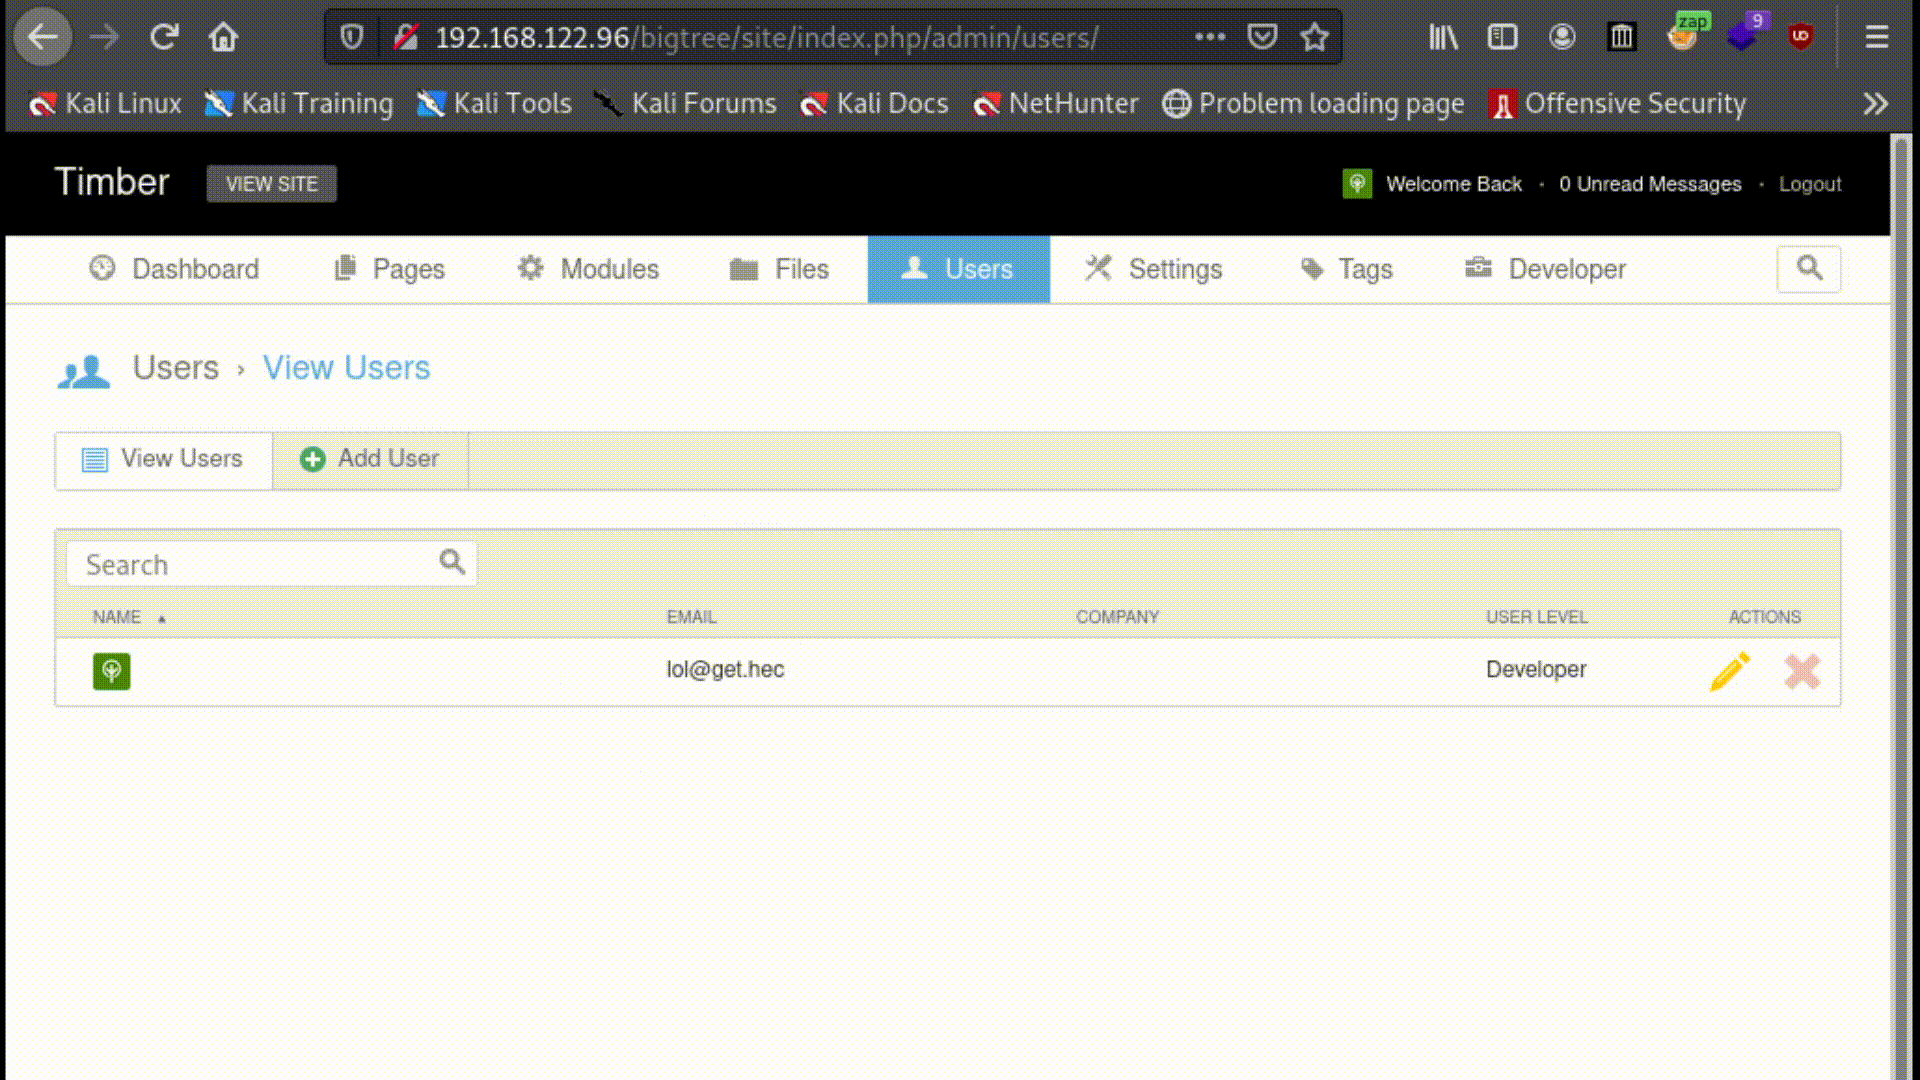
The payload provided forges a request as user id 1, and will change that user's email and password.

Discovered by @giuseppesec August 20th, 2021

Download Tool