

 💬
README_中文 •
Compile/Install/Run •
Parameter Description •
How to use •
Scenario •
POC List •
Custom Scan •
Best Practices
Features
- <a href=https://github.com/hktalent/51Pwn-Platform/blob/main/README.md>Free one id Multi-target web netcat for reverse shell
- What is scan4all: integrated vscan, nuclei, ksubdomain, subfinder, etc., fully automated and intelligent。red team tools
Code-level optimization, parameter optimization, and individual modules, such as vscan filefuzz, have been rewritten for these integrated projects.
In principle, do not repeat the wheel, unless there are bugs, problems
- Cross-platform: based on golang implementation, lightweight, highly customizable, open source, supports Linux, windows, mac os, etc.
- Support [23] password blasting, support custom dictionary, open by "priorityNmap": true
- RDP
- VNC
- SSH
- Socks5
- rsh-spx
- Mysql
- MsSql
- Oracle
- Postgresql
- Redis
- FTP
- Mongodb
- SMB, also detect MS17-010 (CVE-2017-0143, CVE-2017-0144, CVE-2017-0145, CVE-2017-0146, CVE-2017-0147, CVE-2017-0148), SmbGhost (CVE- 2020-0796)
- Telnet
- Snmp
- Wap-wsp (Elasticsearch)
- RouterOs
- HTTP BasicAuth(Authorization), contains Webdav、SVN(Apache Subversion) crack
- Weblogic, enable nuclei through enableNuclei=true at the same time, support T3, IIOP and other detection
- Tomcat
- Jboss
- Winrm(wsman)
- POP3/POP3S
- By default, http password intelligent blasting is enabled, and it will be automatically activated when an HTTP password is required, without manual intervention
- Detect whether there is nmap in the system, and enable nmap for fast scanning through priorityNmap=true, which is enabled by default, and the optimized nmap parameters are faster than masscan
Disadvantages of using nmap: Is the network bad, because the traffic network packet is too large, which may lead to incomplete results
Using nmap additionally requires setting the root password to an environment variable
export PPSSWWDD=yourRootPswd
More references: config/doNmapScan.sh
By default, naabu is used to complete port scanning -stats=true to view the scanning progress
Can I not scan Ports?
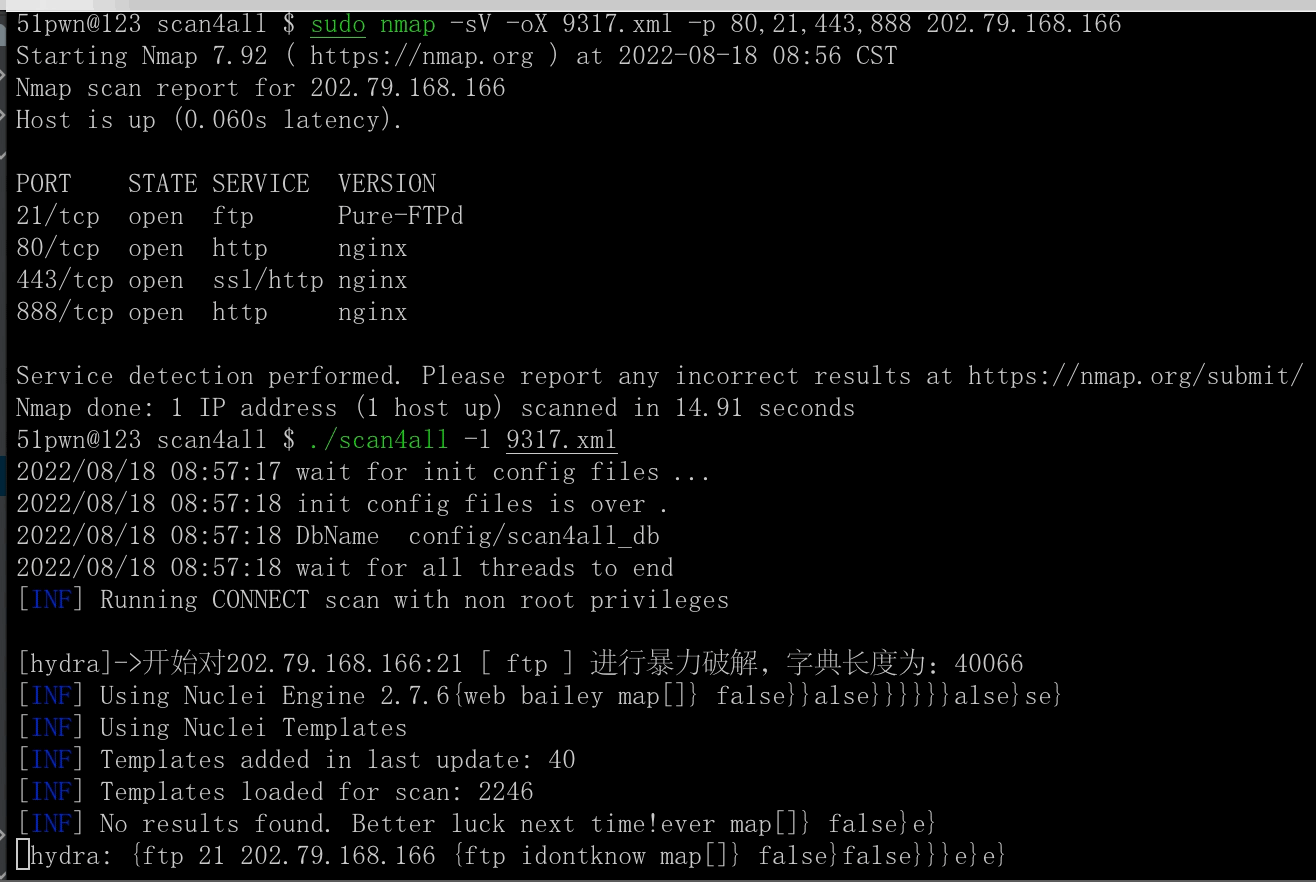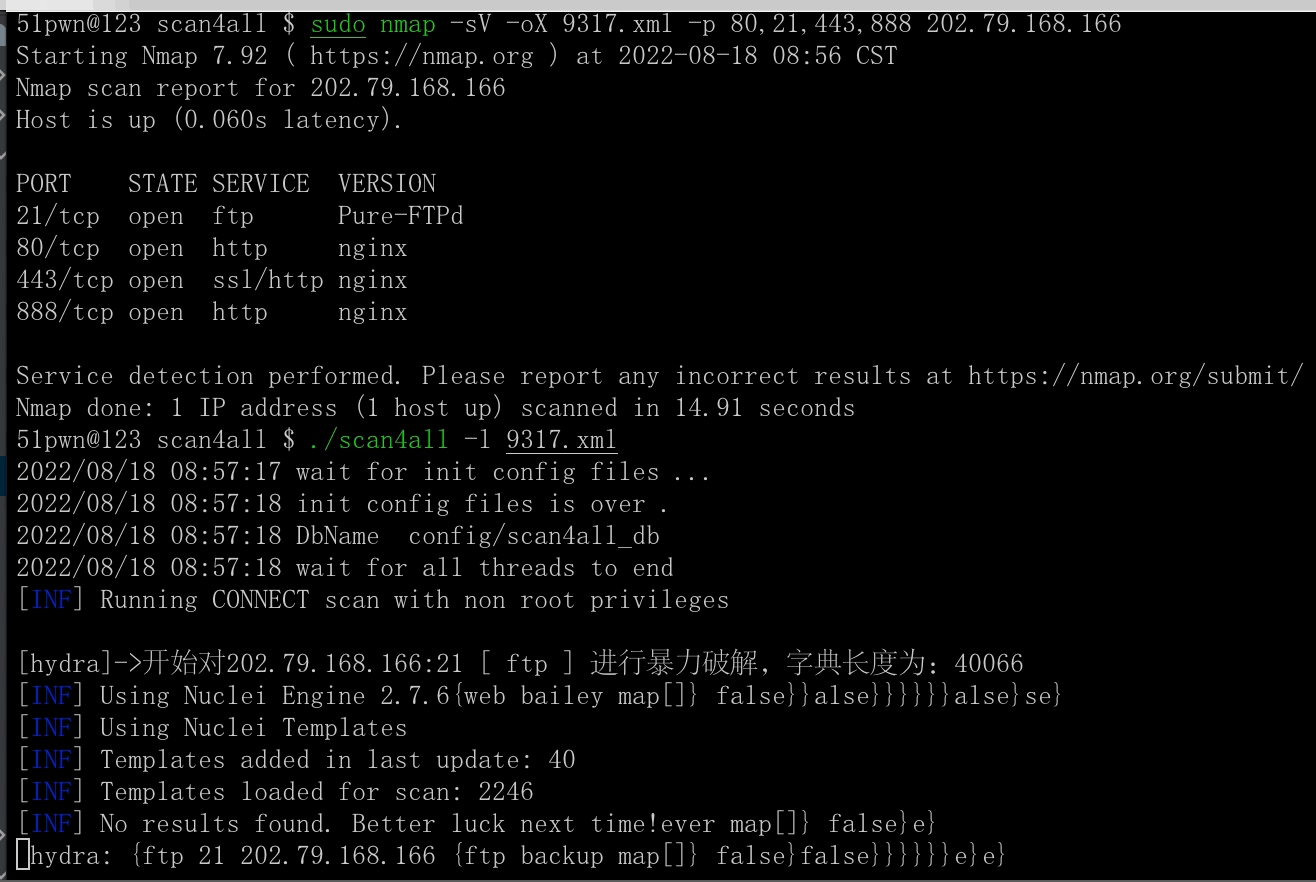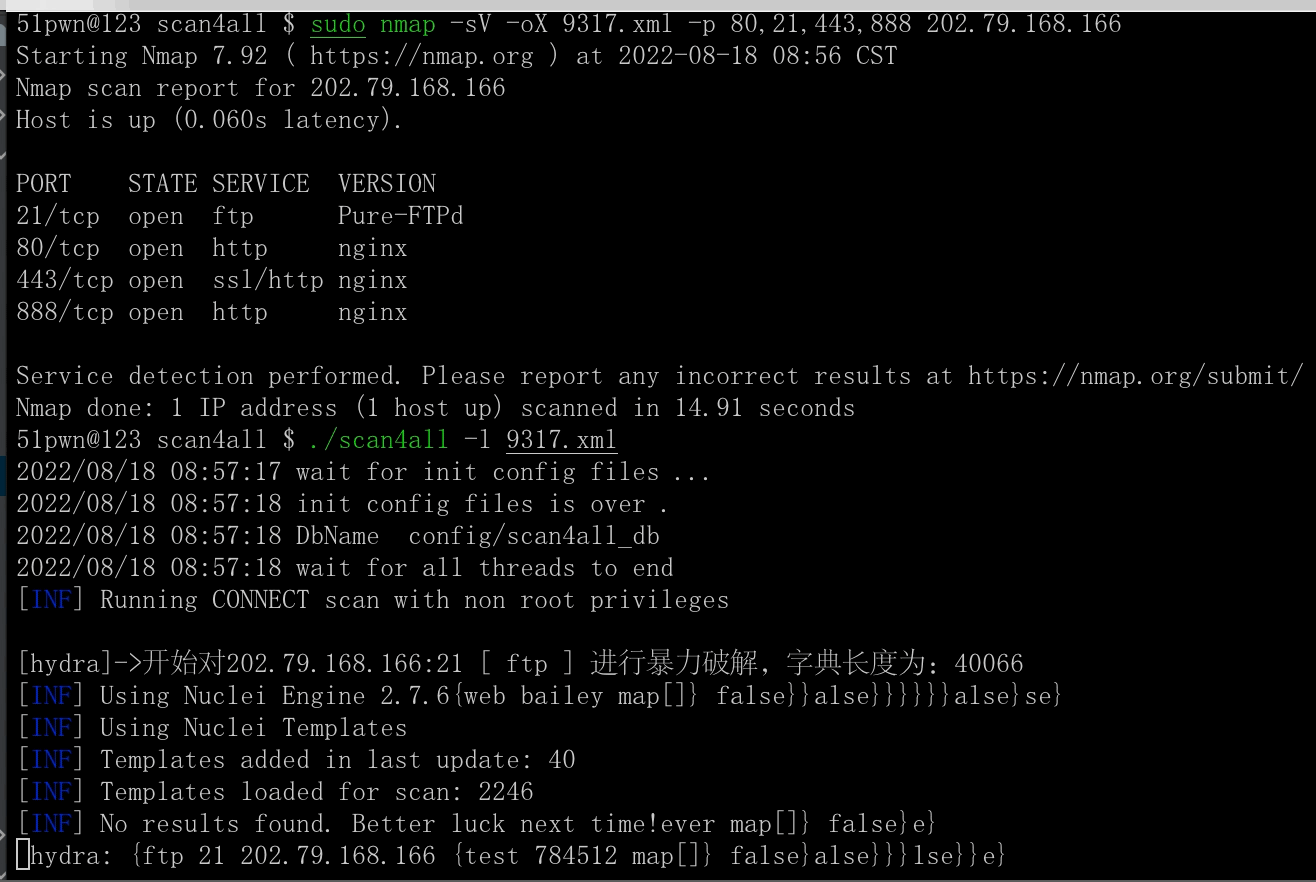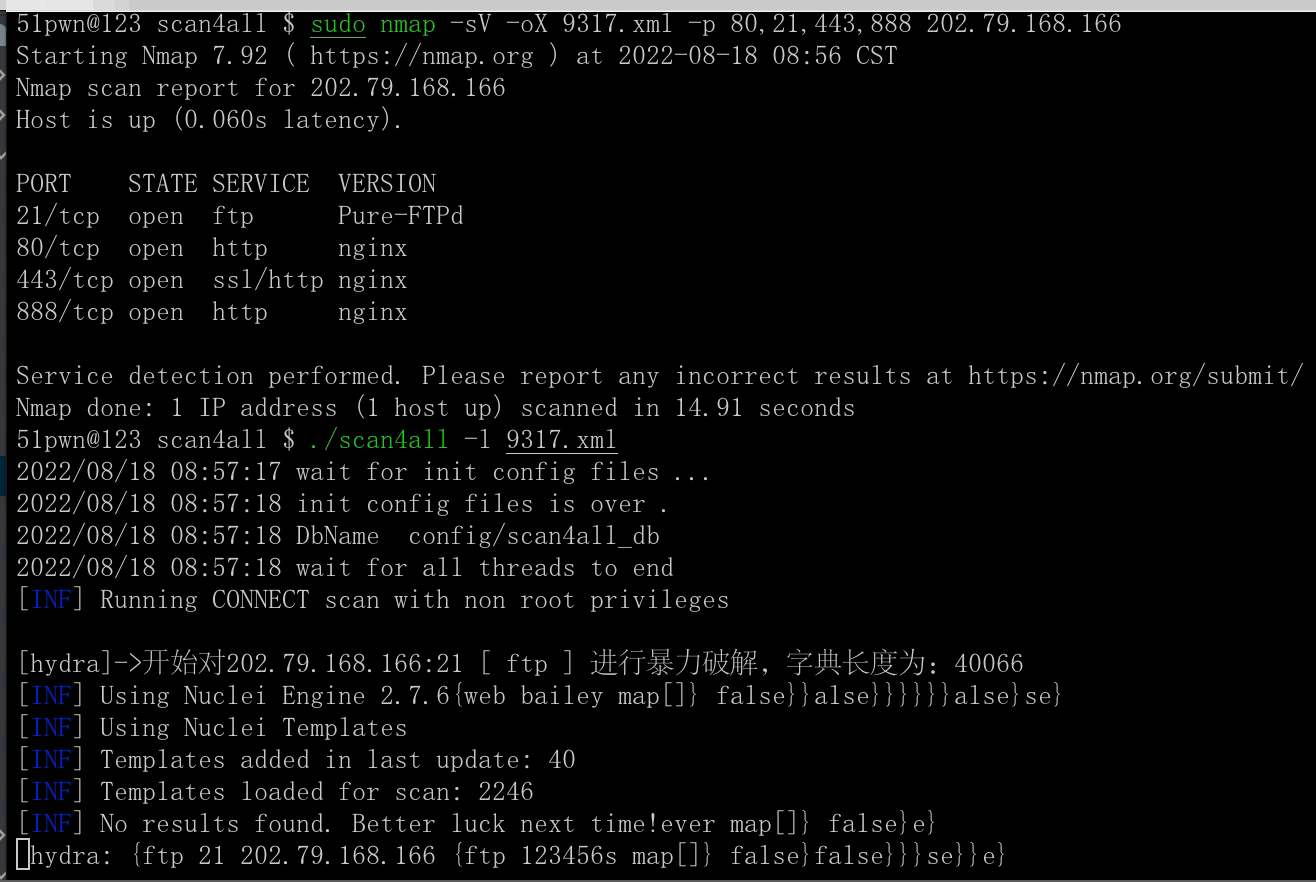
noScan=true ./scan4all -l list.txt -v
# nmap result default noScan=true
./scan4all -l nmapRssuilt.xml -v
- Fast 15000+ POC detection capabilities, PoCs include:
Nuclei Templates Top 10 statistics
| TAG | COUNT | AUTHOR | COUNT | DIRECTORY | COUNT | SEVERITY | COUNT | TYPE | COUNT |
|---|
| cve | 1430 | daffainfo | 631 | cves | 1407 | info | 1474 | http | 3858 |
| panel | 655 | dhiyaneshdk | 584 | exposed-panels | 662 | high | 1009 | file | 76 |
| edb | 563 | pikpikcu | 329 | vulnerabilities | 509 | medium | 818 | network | 51 |
| lfi | 509 | pdteam | 269 | technologies | 282 | critical | 478 | dns | 17 |
| xss | 491 | geeknik | 187 | exposures | 275 | low | 225 | | |
| wordpress | 419 | dwisiswant0 | 169 | misconfiguration | 237 | unknown | 11 | | |
| exposure | 407 | 0x_akoko | 165 | token-spray | 230 | | | | |
| cve2021 | 352 | princechaddha | 151 | workflows | 189 | | | | |
| rce | 337 | ritikchaddha | 137 | default-logins | 103 | | | | |
| wp-plugin | 316 | pussycat0x | 133 | file | 76 | | | | |
281 directories, 3922 files.
- vscan POC
- vscan POC includes: xray 2.0 300+ POC, go POC, etc.
- scan4all POC
-
Support 7000+ web fingerprint scanning, identification:
- httpx fingerprint
- vscan fingerprint
- vscan fingerprint: including eHoleFinger, localFinger, etc.
- scan4all fingerprint
-
Support 146 protocols and 90000+ rule port scanning
- Depends on protocols and fingerprints supported by nmap
-
Fast HTTP sensitive file detection, can customize dictionary
-
Landing page detection
-
Supports multiple types of input - STDIN/HOST/IP/CIDR/URL/TXT
-
Supports multiple output types - JSON/TXT/CSV/STDOUT
-
Highly integratable: Configurable unified storage of results to Elasticsearch [strongly recommended]
-
Smart SSL Analysis:
- In-depth analysis, automatically correlate the scanning of domain names in SSL information, such as *.xxx.com, and complete subdomain traversal according to the configuration, and the result will automatically add the target to the scanning list
- Support to enable *.xx.com subdomain traversal function in smart SSL information, export EnableSubfinder=true, or adjust in the configuration file
-
Automatically identify the case of multiple IPs associated with a domain (DNS), and automatically scan the associated multiple IPs
-
Smart processing:
-
- When the IPs of multiple domain names in the list are the same, merge port scans to improve efficiency
-
- Intelligently handle http abnormal pages, and fingerprint calculation and learning
-
Automated supply chain identification, analysis and scanning
-
Link python3 <a href=https://github.com/hktalent/log4j-scan>log4j-scan
- This version blocks the bug that your target information is passed to the DNS Log Server to avoid exposing vulnerabilities
- Added the ability to send results to Elasticsearch for batch, touch typing
- There will be time in the future to implement the golang version
how to use?
mkdir ~/MyWork/;cd ~/MyWork/;git clone https://github.com/hktalent/log4j-scan
- Intelligently identify honeypots and skip Targets. This function is disabled by default. You can set EnableHoneyportDetection=true to enable
- Highly customizable: allow to define your own dictionary through config/config.json configuration, or control more details, including but not limited to: nuclei, httpx, naabu, etc.
- support HTTP Request Smuggling: CL-TE、TE-CL、TE-TE、CL_CL、BaseErr



 ghosttroops/scan4all
