
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-12139-WordPress-Integrate-Google-Drive-Exploit — Golang PoC exploit for CVE-2025-12139 targeting the Integrate Google Drive WordPress plugin. Extracts sensitive OAuth credentials (Client ID, Secret, Access Tokens) from unauthenticated endpoints, enabling potential Google Drive account takeover. | Kitploit
Tools/GitHubGitHub/galaxy-sc/cve-2025-12139-wordpress-integrate-google-drive-exploit
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubgalaxy-sc/cve-2025-12139-wordpress-integrate-google-drive-exploit

CVE-2025-12139-WordPress-Integrate-Google-Drive-Exploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Golang PoC exploit for CVE-2025-12139 targeting the Integrate Google Drive WordPress plugin. Extracts sensitive OAuth credentials (Client ID, Secret, Access Tokens) from unauthenticated endpoints, enabling potential Google Drive account takeover.

View Repository
149 months agoNot yet reviewed

CVE-2025-12139: Integrate Google Drive WordPress Plugin - Information Disclosure Exploit

Description

This is a Golang Proof of Concept (PoC) exploit for CVE-2025-12139. The vulnerability exists in the Integrate Google Drive plugin (versions <= 1.5.3) for WordPress. It allows unauthenticated attackers to retrieve sensitive information, including Google Client ID, Client Secret, and OAuth Access Tokens, potentially leading to full Google Drive account takeover.

Vulnerability Details

  • CVE: CVE-2025-12139
  • Vulnerability Type: Information Disclosure (via wp_localize_script)
  • Vendor: SoftLab
  • Affected Version: <= 1.5.3
  • Tested On: Linux / Windows
  • Google Dork: inurl:"/wp-content/plugins/integrate-google-drive"

Proof of Concept

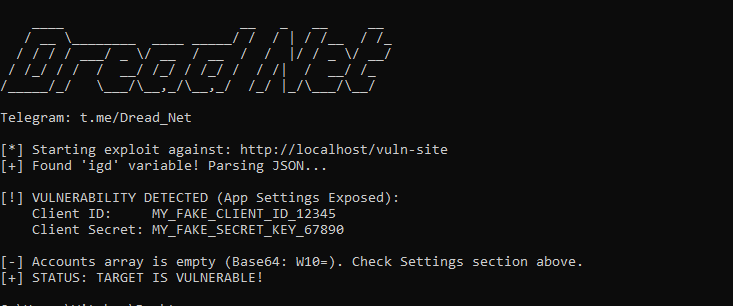
Here is the exploit in action, extracting sensitive Client ID and Secret Key: Exploit Output Screenshot

Usage

go run exploit.go -u https://target-site.com
Download Tool