
 gagaltotal/cve-2026-44825-apache-solr-scanner
Apache Solr instances that may be affected by CVE-2026-44825, related to Velocity Template Remote Code Execution (RCE) conditions.

This repository contains a Go-based scanner for detecting and testing Apache Solr instances that may be affected by CVE-2026-44825, related to Velocity Template Remote Code Execution (RCE) conditions.
The tool can scan a single target or a list of targets, detect Solr endpoints, attempt authentication checks, and optionally run exploit or interactive RCE workflow modes.
This project is intended for authorized security research, internal validation, and defensive testing in environments where explicit permission has been granted.
The scanner is not intended for unauthorized access or abuse of third-party systems.
From the project root, run:
go build -o solr_scanner .
This will produce the binary named solr_scanner.
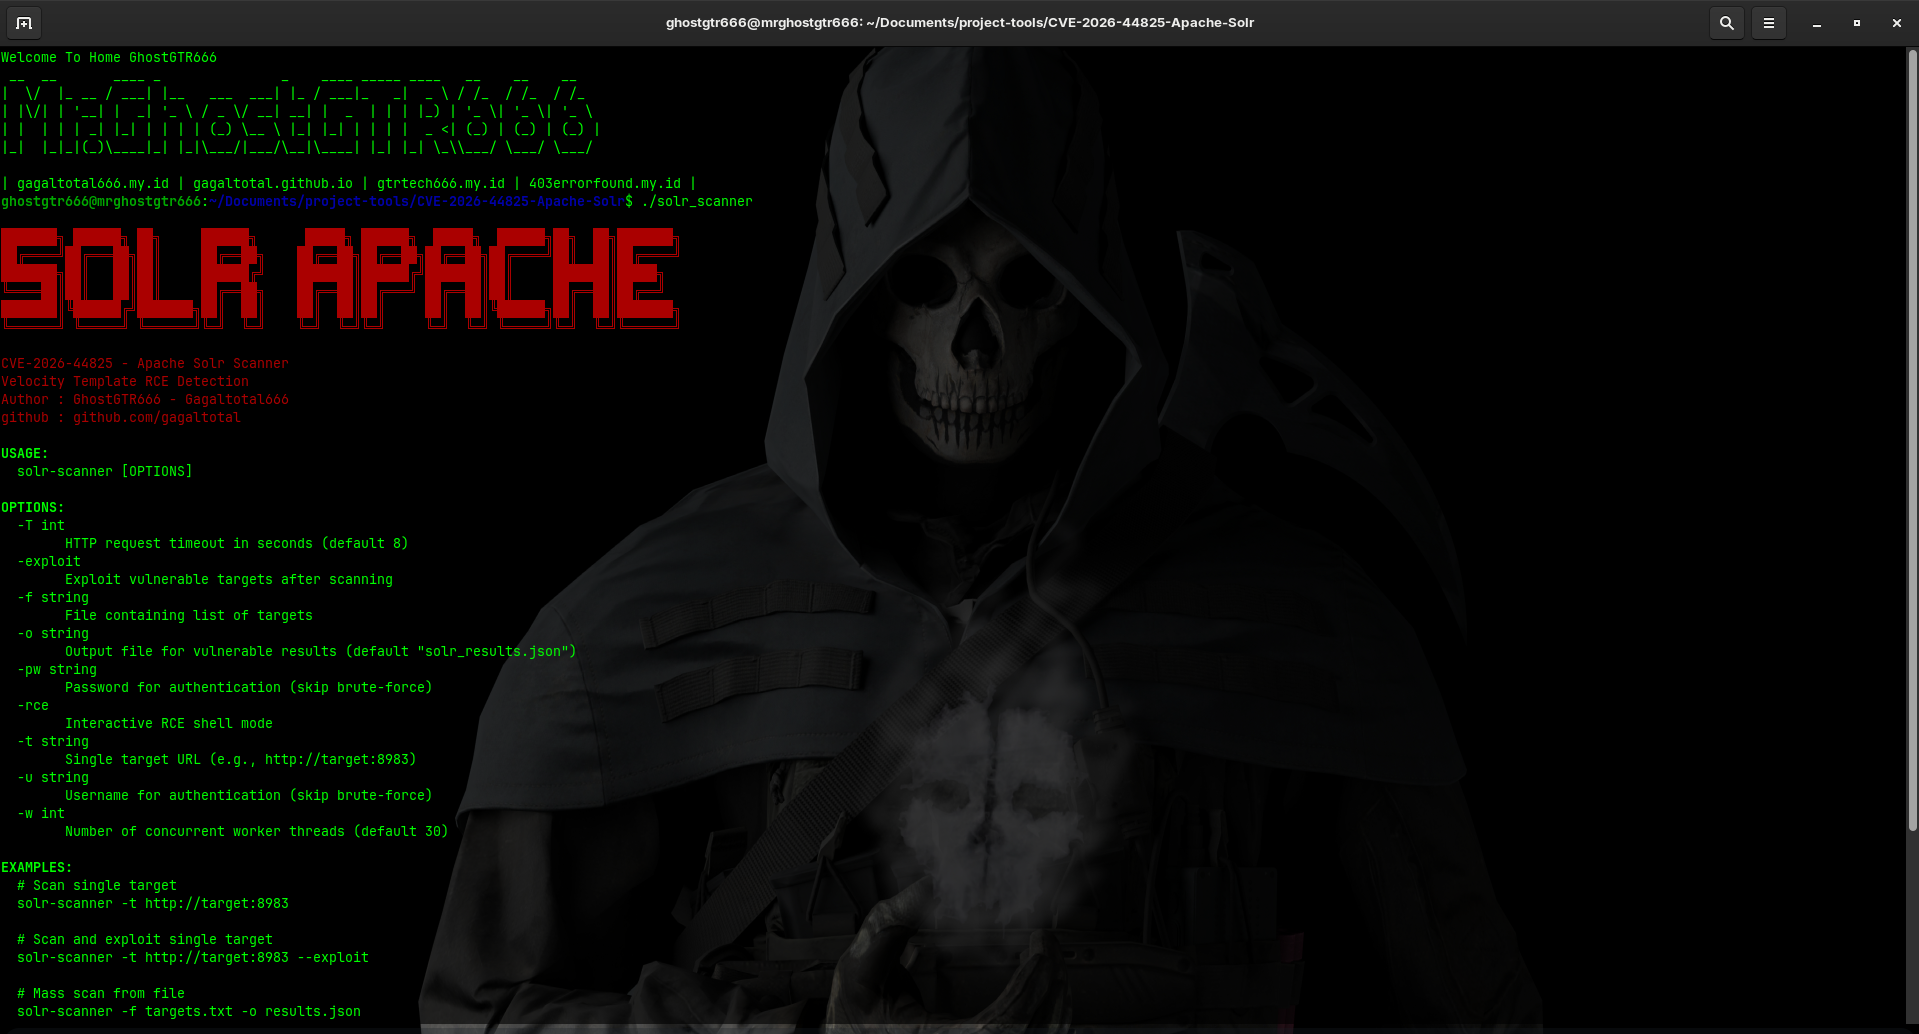
./solr_scanner -t http://target:8983
./solr_scanner -f targets.txt
./solr_scanner -t http://target:8983 --exploit
./solr_scanner -t http://target:8983 --rce
./solr_scanner -t http://target:8983 --rce -u admin -pw SolrRocks
Results are written to JSON by default in the file specified by -o, which defaults to:
solr_results.json
Use this tool only in environments where you have explicit authorization to test. The maintainers are not responsible for misuse or any unauthorized activity conducted with this software.
