
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
cve-2026-24858 — Python helper to scan Fortinet web management for CVE-2026-24858 SSO authentication bypass and optionally send explicit payloads with user authorization. | Kitploit
Tools/GitHubGitHub/gagaltotal/cve-2026-24858
Vulnerability ScannersExploitationWeb Application ExploitationPenetration TestingAuthentication
GitHubgagaltotal/cve-2026-24858

cve-2026-24858

Python helper to scan Fortinet web management for CVE-2026-24858 SSO authentication bypass and optionally send explicit payloads with user authorization.

View Repository
1247 months agoNot yet reviewed
Website

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-24858 PoC helper

CVE-2026-24858 - Administrative FortiCloud SSO authentication bypass

This repository contains a conservative Python helper for scanning Fortinet web management indicators and an optional (explicit) payload sender. The exploit/payload sender is disabled by default and requires an explicit flag to run.
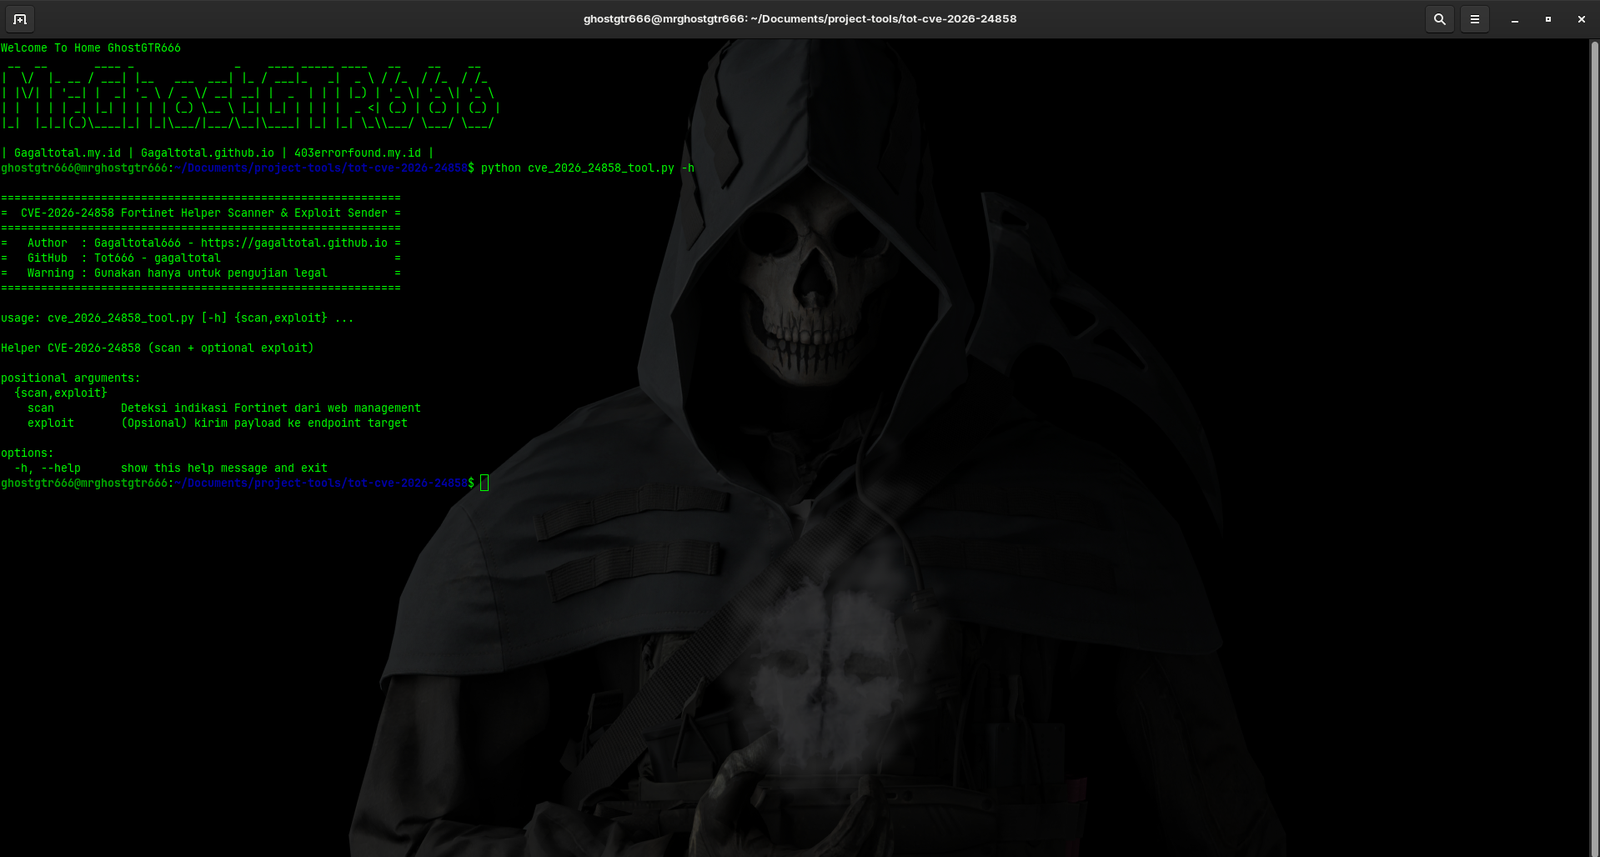
Screen Capture

Usage examples:

  • Install dependencies:
root@kitploit:~
python3 -m pip install -r requirements.txt
  • Scan the target (default HTTPS port 443):
root@kitploit:~
python3 cve_2026_24858_tool.py scan --target 192.168.2.3
  • Scan the target (default HTTPS port 443) with verbose:
root@kitploit:~
python3 cve_2026_24858_tool.py scan --target 192.168.2.3 --versbose
  • Send a payload (REQUIRES --enable-exploit and a payload file):
root@kitploit:~
python3 cve_2026_24858_tool.py exploit --target 192.168.2.3 --endpoint /vuln/path \
  --payload-file ./payload.bin --enable-exploit

Warnings:

  • Only run against systems you own or have written authorization to test.
  • The exploit sender will POST the exact bytes from --payload-file to the specified endpoint; the tool does not craft or invent exploit payloads.

Additional options:

  • --verbose: print response headers and a body snippet (scan & exploit).
  • --dump-body: print the full response body (may be large).
  • --save-response <file>: save the full response body to the given file path.

Example: save exploit response to a file while printing headers:

root@kitploit:~
python3 cve_2026_24858_tool.py exploit --target 192.168.2.3 --endpoint /vuln/path \
  --payload-file ./payload.bin --enable-exploit --verbose --save-response ./resp.html
Download Tool