 francoismichel/ssh3
Fast, secure shell protocol built on HTTP/3, QUIC, and TLS 1.3. Supports OAuth2, OpenID Connect, and classical SSH authentication with UDP port forwarding and hidden server capabilities.

[!NOTE] SSH3 is probably going to change its name. It is still the SSH Connection Protocol (RFC4254) running on top of HTTP/3 Extended connect, but the required changes are heavy and too distant from the philosophy of popular SSH implementations to be considered for integration. The specification draft has already been renamed ("Remote Terminals over HTTP/3"), but we need some time to come up with a nice permanent name.
SSH3 is a complete revisit of the SSH protocol, mapping its semantics on top of the HTTP mechanisms. It comes from our research work and we (researchers) recently proposed it as an Internet-Draft (draft-michel-remote-terminal-http3-00).
In a nutshell, SSH3 uses QUIC+TLS1.3 for secure channel establishment and the HTTP Authorization mechanisms for user authentication. Among others, SSH3 allows the following improvements:
[!TIP] Quickly want to get started ? Checkout how to install SSH3. You will learn to setup an SSH3 server and use the SSH3 client.
Faster for session establishment, not throughput ! SSH3 offers a significantly faster session establishment than SSHv2. Establishing a new session with SSHv2 can take 5 to 7 network round-trip times, which can easily be noticed by the user. SSH3 only needs 3 round-trip times. The keystroke latency in a running session is unchanged.
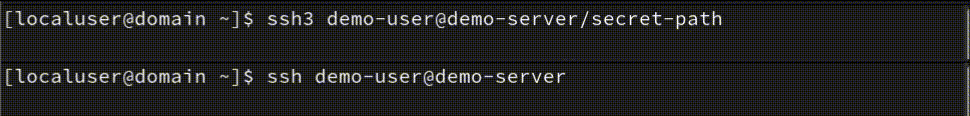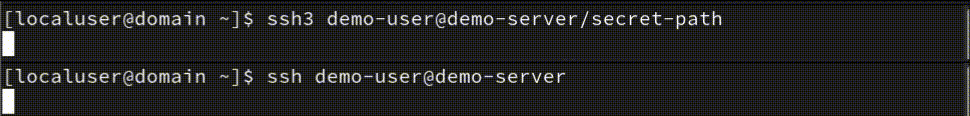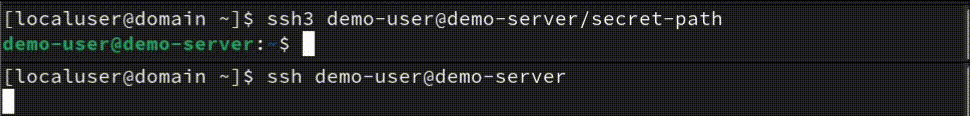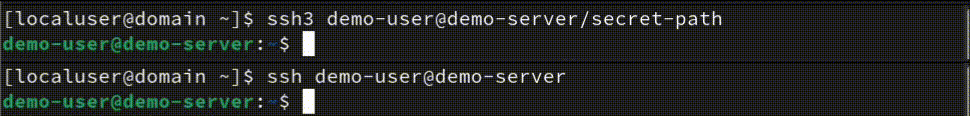 SSH3 (top) VS SSHv2 (bottom) session establishement with a 100ms ping towards the server.
While SSHv2 defines its own protocols for user authentication and secure channel establishment, SSH3 relies on the robust and time-tested mechanisms of TLS 1.3, QUIC and HTTP. These protocols are already extensively used to secure security-critical applications on the Internet such as e-commerce and Internet banking.
SSH3 already implements the common password-based and public-key (RSA and EdDSA/ed25519) authentication methods. It also supports new authentication methods such as OAuth 2.0 and allows logging in to your servers using your Google/Microsoft/Github accounts.
While SSH3 shows promise for faster session establishment, it is still at an early proof-of-concept stage. As with any new complex protocol, expert cryptographic review over an extended timeframe is required before reasonable security conclusions can be made.
We are developing SSH3 as an open source project to facilitate community feedback and analysis. However, we cannot yet endorse its appropriateness for production systems without further peer review. Please collaborate with us if you have relevant expertise!
Given the current prototype state, we advise testing SSH3 in sandboxed environments or private networks. Be aware that making experimental servers directly Internet-accessible could introduce risk before thorough security vetting.
While hiding servers behind secret paths has potential benefits, it does not negate the need for rigorous vulnerability analysis before entering production. We are excited by SSH3's future possibilities but encourage additional scrutiny first.
Using SSH3, you can avoid the usual stress of scanning and dictionary attacks against your SSH server. Similarly to your secret Google Drive documents, your SSH3 server can be hidden behind a secret link and only answer to authentication attempts that made an HTTP request to this specific link, like the following:
ssh3-server -bind 192.0.2.0:443 -url-path <my-long-secret>
By replacing <my-long-secret> by, let's say, the random value M3MzkxYWMxMjYxMjc5YzJkODZiMTAyMjU, your SSH3 server will only answer to SSH3 connection attempts made to the URL https://192.0.2.0:443/M3MzkxYWMxMjYxMjc5YzJkODZiMTAyMjU and it will respond a 404 Not Found to other requests. Attackers and crawlers on the Internet can therefore not detect the presence of your SSH3 server. They will only see a simple web server answering 404 status codes to every request.
NOTE WELL: placing your SSH3 server behind a secret URL may reduce the impact of scanning attacks but will and must never replace classical authentication mechanisms. The secret link should only be used to avoid your host to be discovered. Knowing the secret URL should not grant someone access to your server. Use the classical authentication mechanisms described above to protect your server.
SSH3 provides new feature that could not be provided by the SSHv2 protocol.
This SSH3 implementation already provides many of the popular features of OpenSSH, so if you are used to OpenSSH, the process of adopting SSH3 will be smooth. Here is a list of some OpenSSH features that SSH3 also implements:
~/.ssh/authorized_keys on the serverknown_hosts mechanism when X.509 certificates are not used.ssh-agent for public key authentication-proxy-jump parameter). If A is an SSH3 client and B and C are both SSH3 servers, you can connect from A to C using B as a gateway/proxy. The proxy uses UDP forwarding to forward the QUIC packets from A to C, so B cannot decrypt the traffic A<->C SSH3 traffic.~/.ssh/config on the client and handles the Hostname, User, Port and IdentityFile config options (the other options are currently ignored). Also parses a new UDPProxyJump that behaves similarly to OpenSSH's ProxyJump.