 fortalice/bofhound
Generate BloodHound compatible JSON from logs written by ldapsearch BOF, pyldapsearch and Brute Ratel's LDAP Sentinel

⛔🚧 This repo is no longer maintained. To submit an issue, pull request, or obtain the lastest version, reference https://github.com/coffeegist/bofhound 🚧⛔
 _____________________________ __    __    ______    __    __   __   __   _______
|   _   /  /  __   / |   ____/|  |  |  |  /  __  \  |  |  |  | |  \ |  | |       \
|  |_)  | |  |  |  | |  |__   |  |__|  | |  |  |  | |  |  |  | |   \|  | |  .--.  |
|   _  <  |  |  |  | |   __|  |   __   | |  |  |  | |  |  |  | |  . `  | |  |  |  |
|  |_)  | |  `--'  | |  |     |  |  |  | |  `--'  | |  `--'  | |  |\   | |  '--'  |
|______/   \______/  |__|     |__|  |___\_\________\_\________\|__| \___\|_________\

                              by Fortalice ✪
BOFHound is an offline BloodHound ingestor and LDAP result parser compatible with TrustedSec's ldapsearch BOF, the Python adaptation, pyldapsearch and Brute Ratel's LDAP Sentinel.
By parsing log files generated by the aforementioned tools, BOFHound allows operators to utilize BloodHound's beloved interface while maintaining full control over the LDAP queries being run and the spped at which they are executed. This leaves room for operator discretion to account for potential honeypot accounts, expensive LDAP query thresholds and other detection mechanisms designed with the traditional, automated BloodHound collectors in mind.
Blog - Granularize Your AD Recon Game
Blog - Granularize Your AD Recon Game Part 2
BOFHound can be installed with pip3 install bofhound or by cloning this repository and running pip3 install .
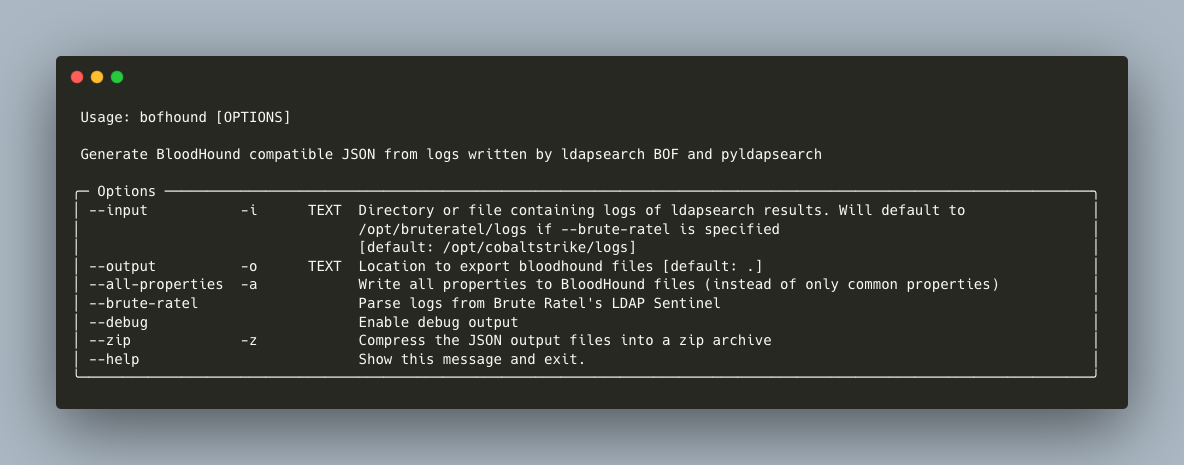
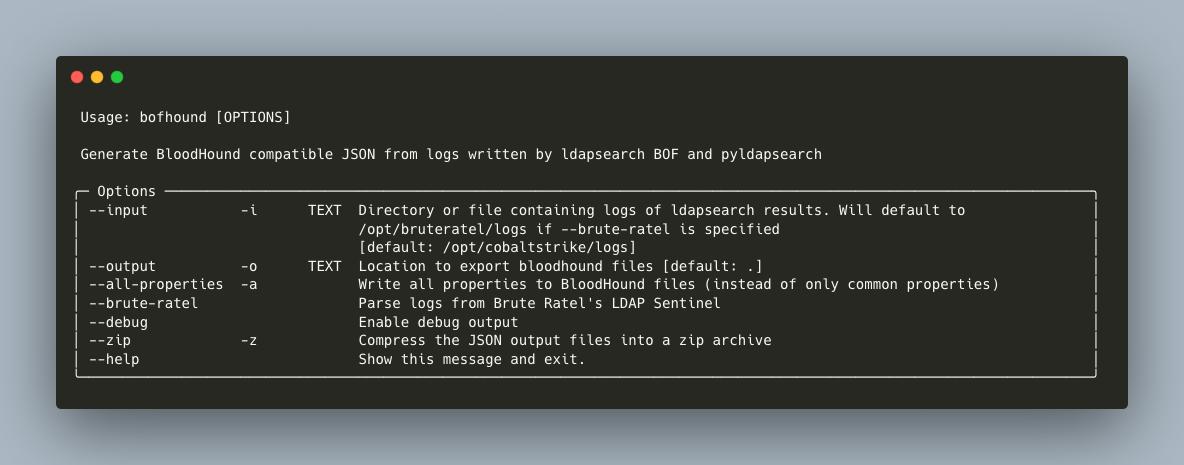
Parse ldapseach BOF results from Cobalt Strike logs (/opt/cobaltstrike/logs by default) to /data/
bofhound -o /data/
Parse pyldapsearch logs and only include all properties (vs only common properties)
bofhound -i ~/.pyldapsearch/logs/ --all-properties
Parse LDAP Sentinel data from BRc4 logs (will change default input path to /opt/bruteratel/logs)
bofhound --brute-ratel
The following attributes are required for proper functionality:
samaccounttype
dn
objectsid
Get All the Data (Maybe Run BloodHound Instead?)
ldapsearch (objectclass=*) *,ntsecuritydescriptor
Retrieve All Schema Info
ldapsearch (schemaIDGUID=*) name,schemaidguid -1 "" CN=Schema,CN=Configuration,DC=windomain,DC=local
Retrieve Only the ms-Mcs-AdmPwd schemaIDGUID
ldapsearch (name=ms-mcs-admpwd) name,schemaidguid 1 "" CN=Schema,CN=Configuration,DC=windomain,DC=local
bofhound uses Poetry to manage dependencies. Install from source and setup for development with:
git clone https://github.com/fortalice/bofhound
cd bofhound
poetry install
poetry run bofhound --help






