A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
reburp turns Burp Suite into something you can script. It loads as a Java extension and serves
the Montoya API
over an HTTP REST API on http://127.0.0.1:9090, with an OpenAPI spec and Swagger UI. Anything
you would click in Burp - reading proxy history, sending a request, editing scope, running a
scan, decoding a token - becomes a JSON call an agent or a curl line can make.
It pairs with the burp-interaction agent skill so an AI
assistant can drive Burp directly.
Burp features your agent can now drive over REST:
Grab the latest reburp-*.jar from Releases, or
build it from source (requires Java 17+).
Each reburp release is built against a minimum Burp Suite (Montoya) version. On an older Burp, grab the matching jar from Releases.
git clone https://github.com/forefy/reburp.git
cd reburp
./gradlew shadowJar
# Output: build/libs/reburp.jar  (plus a versioned copy, reburp-<version>.jar)
Load reburp.jar rather than the versioned copy. Burp reloads an extension from the path
it was loaded from, and the versioned name changes on every release, so the unversioned one
keeps reloading after an upgrade instead of quietly leaving you on the previous build.
If your JAVA_HOME isn't set, point it at your JDK:
JAVA_HOME=/path/to/jdk17 ./gradlew shadowJar
build/libs/reburp.jar (or the reburp-*.jar you downloaded from Releases)A reburp tab appears in Burp showing every REST call as it happens.
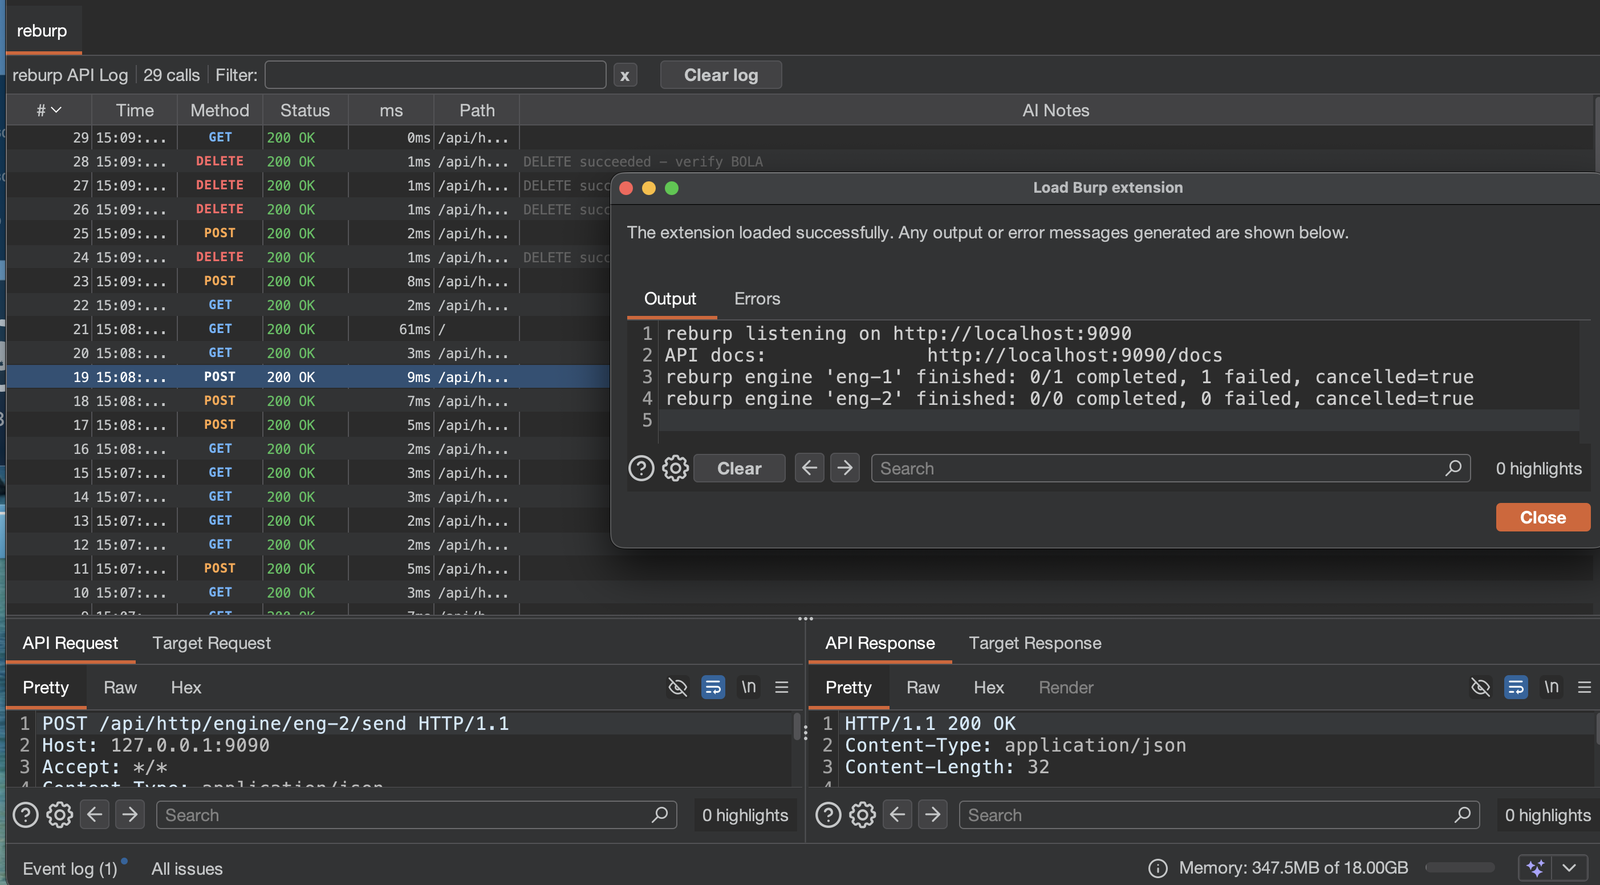
Each row is one REST call. Selecting it shows the API request and response, plus the request and response reburp sent to the target on your behalf.
Once loaded, open in your browser:
The spec is the source of truth for request and response shapes.
| Group | Prefix | Highlights |
|---|---|---|
| Status | /api/status | Extension info, Burp version |
| Proxy | /api/proxy/ | History, search, annotate, intercept toggle, WebSocket history |
| Site Map | /api/sitemap/ | List, search |
| Scope | /api/scope/ | Check URL in scope, add/remove scope rules |
| HTTP | /api/http/ | Send HTTP/1.1 & HTTP/2, auth-token injection, parse, diff, params, reflection, insertion points, cookies |
| Messages | /api/http/message/ | Inspect and rewrite requests and responses: headers, parameters, markers, MIME types, timing |
| Scanner | /api/scanner/ | Issues, start audit/crawl, task status (Pro only) |
| Collaborator | /api/collaborator/ | Generate payloads, poll interactions (Pro only) |
| Repeater / Intruder | /api/repeater/, /api/intruder/ | Send requests to Repeater and Intruder |
| Request Engine | /api/http/engine/ | High-throughput async request engine: resource pools, concurrency limit, throttle, retries, live stats, pause/resume/cancel, results (Burp 2026.x) |
| Config | /api/config/ | Get/set project & user options, task engine state |
| Match & Replace | /api/proxy/match-replace/ | List, add, remove proxy match-and-replace rules |
| Sessions | /api/sessions/ | List and delete session-handling rules (Burp has no add-header action) |
| Engagement | /api/engagement/ | CSRF PoC generator, content discovery, find references, send to decoder |
| Bambda | /api/bambda/ | Import Bambda scripts, generate filter chains |
| Organizer | /api/organizer/ | List items, send requests to the Organizer |
# Is the extension up?
curl -s http://127.0.0.1:9090/api/status

# Last 10 proxy entries
curl -s "http://127.0.0.1:9090/api/proxy/history?limit=10"

# Send a request through Burp
curl -s http://127.0.0.1:9090/api/http/send \
  -H 'Content-Type: application/json' \
  -d '{"host":"example.com","port":443,"use_https":true,"method":"GET","path":"/"}'

# Add a host to scope
curl -s http://127.0.0.1:9090/api/scope/include \
  -H 'Content-Type: application/json' \
  -d '{"url":"https://example.com"}'
The REST server binds 127.0.0.1 only, but the port is unauthenticated and responds to
any origin. Anything that can reach localhost:9090 can drive Burp, including a web page
open in your browser. Treat the port as trusted-local-only and never expose it beyond loopback.
Because of that, OS command execution is off by default. /api/utils/shell/execute and
/api/utils/shell/execute-raw return 403 unless the extension sees this in Burp's own process
environment:
REBURP_ENABLE_SHELL=1
With it set, any origin that can reach the port gets remote code execution on the host. Enable it
only when you accept that. Every invocation is written to the extension output tab.
GET /api/utils/shell/status reports whether it is on and never requires it to be.
The "full Montoya API" claim is verified mechanically by tools/api_coverage.py,
which the CI build workflow runs on every push and fails if any mappable
method is left unexposed. Behaviour is exercised separately by tools/smoke_test.py against a loaded extension.
9090. Change port in BurpRestApiExtension.kt and rebuild if needed.compileOnly - it is not bundled; Burp provides it at runtime.{ "error": "..." }.OpenApiSpec.kt plus fragments in docs/. To add a route
group, write a *Paths() and *Schemas() fragment and list it in docs/OpenApiSpecExtra.kt.Issues and pull requests are welcome. Please run python3 tools/api_coverage.py and
./gradlew shadowJar before opening a PR. New route groups should ship with their OpenAPI fragment
so the docs stay complete.
| Issues |
/api/issues/ |
| Create custom audit issues |
| Events | /api/events/ | Turn passive traffic observers on and off, then read the captured events |
| Extension Data | /api/extension-data/ | Typed key/value storage held in the Burp project file |
| Preferences | /api/preferences/ | Persisted extension preferences by type |
| Logging | /api/logging/ | Write to the extension output and error tabs and Burp's event log |
| Activity Log | /api/log/ | Query reburp's own persisted call log |
| AI | /api/ai/ | Burp AI status and chat (where available) |
| Meta | /api/meta/ | Burp version components, extension load info, enum vocabularies |
| Utilities | /api/utils/ | URL encode/decode, base64, hash, JWT decode, random string, decompress |
| Numbers | /api/utils/number/ | Convert between binary, octal, decimal, hex and arbitrary radixes |
| JSON | /api/utils/json/ | Validate, read and edit by pointer, inspect structure, normalise |
| Bytes | /api/utils/bytes/ | Search, slice, append, allocate and inspect byte buffers |
| Ranking | /api/utils/rank | Rank proxy history by how anomalous each exchange looks |
| Shell | /api/utils/shell/ | OS command execution. Disabled by default, see Security |