
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
PoC-CVE-2024-24035 — Proof-of-concept exploit for DOM-based Cross-Site Scripting (XSS) vulnerability in SIL 3.1 via the 'hmessage' parameter, demonstrating the attack vector for security testing. | Kitploit
Tools/GitHubGitHub/elizeuopain/poc-cve-2024-24035
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubelizeuopain/poc-cve-2024-24035

PoC-CVE-2024-24035

Proof-of-concept exploit for DOM-based Cross-Site Scripting (XSS) vulnerability in SIL 3.1 via the 'hmessage' parameter, demonstrating the attack vector for security testing.

View Repository
112 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2024-24035

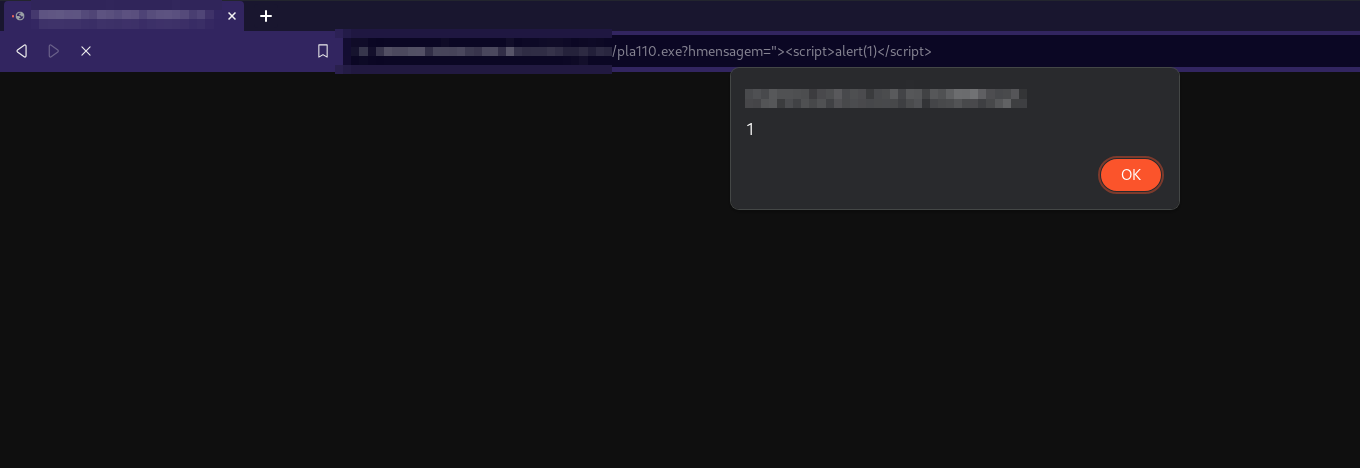
Title The SIL 3.1 is vulnerable to Cross Site Scripting (XSS) in the "hmessage" parameter.

Date: 2024-01-14

Author: Elizeu Das Dores

Vendor Homepage: https://www.setorinformatica.com/

Version: 3.1

POC CVE-2024-24035

The "hmessage" parameter is vulnerable to DOM Based Cross Site Scripting (XSS). dom xss
Download Tool