
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
s3crets_scanner — Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and supporting scheduled or on-demand scans. | Kitploit
Tools/GitHubGitHub/eilonh/s3crets_scanner
Cloud Infrastructure SecurityVulnerability ScannersCloud SecuritySecret Detection
GitHubeilonh/s3crets_scanner

s3crets_scanner

Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and supporting scheduled or on-demand scans.

View Repository
57162343 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

S3cret Scanner: Hunting For Secrets Uploaded To Public S3 Buckets

  • S3cret Scanner tool designed to provide a complementary layer for the Amazon S3 Security Best Practices by proactively hunting secrets in public S3 buckets.
  • Can be executed as scheduled task or On-Demand

Automation workflow

The automation will perform the following actions:

  1. List the public buckets in the account (Set with ACL of Public or objects can be public)
  2. List the textual or sensitive files (i.e. .p12, .pgp and more)
  3. Download, scan (using truffleHog3) and delete the files from disk, once done evaluating, one by one.
  4. The logs will be created in logger.log file.

Prerequisites

  1. Python 3.6 or above
  2. TruffleHog3 installed in $PATH
  3. An AWS role with the following permissions:
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Sid": "VisualEditor0",
            "Effect": "Allow",
            "Action": [
                "s3:GetLifecycleConfiguration",
                "s3:GetBucketTagging",
                "s3:ListBucket",
                "s3:GetAccelerateConfiguration",
                "s3:GetBucketPolicy",
                "s3:GetBucketPublicAccessBlock",
                "s3:GetBucketPolicyStatus",
                "s3:GetBucketAcl",
                "s3:GetBucketLocation"
            ],
            "Resource": "arn:aws:s3:::*"
        },
        {
            "Sid": "VisualEditor1",
            "Effect": "Allow",
            "Action": "s3:ListAllMyBuckets",
            "Resource": "*"
        }
    ]
}
  1. If you're using a CSV file - make sure to place the file accounts.csv in the csv directory, in the following format:
Account name,Account id
prod,123456789
ci,321654987
dev,148739578

Getting started

Use pip to install the needed requirements.

# Clone the repo
git clone <repo>

# Install requirements
pip3 install -r requirements.txt

# Install trufflehog3
pip3 install trufflehog3

Usage

ArgumentValuesDescriptionRequired
-p, --aws_profileThe aws profile name for the access keys✓
-r, --scanner_roleThe aws scanner's role name✓
-m, --methodinternalthe scan type✓
-l, --last_modified1-365Number of days to scan since the file was last modified; Default - 1✗

Usage Examples

python3 main.py -p secTeam -r secteam-inspect-s3-buckets -l 1
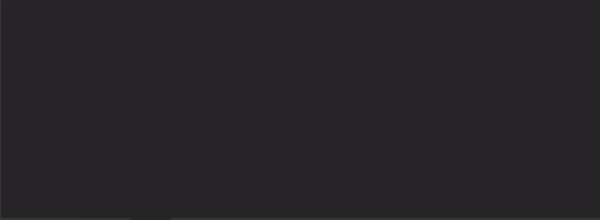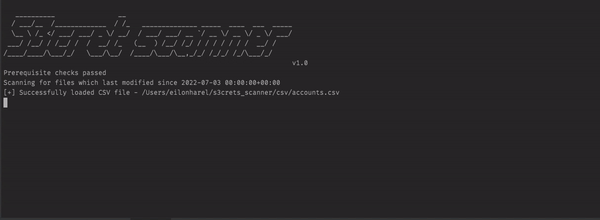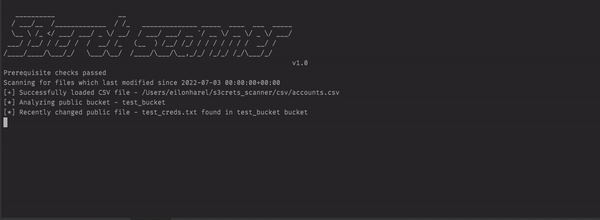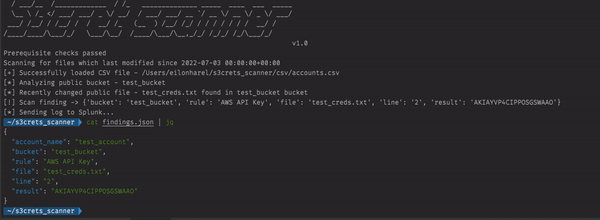
Demo


References

Medium


Contributing

Pull requests and forks are welcome. For major changes, please open an issue first to discuss what you would like to change.


License

License

Download Tool