
 egebalci/amber
Reflective PE packer.


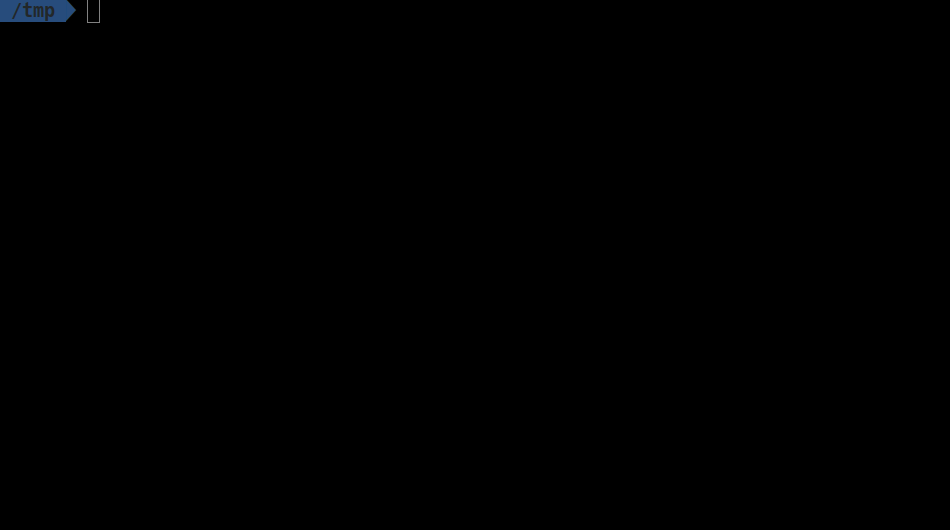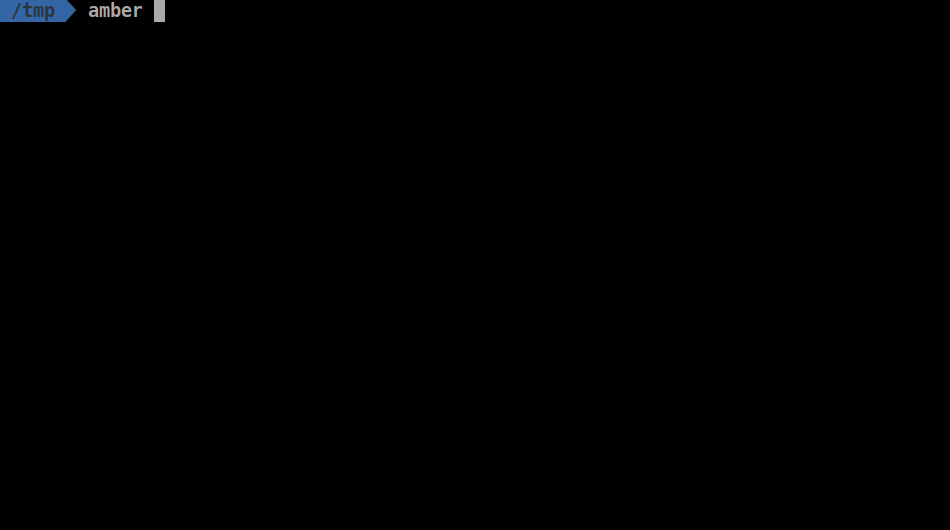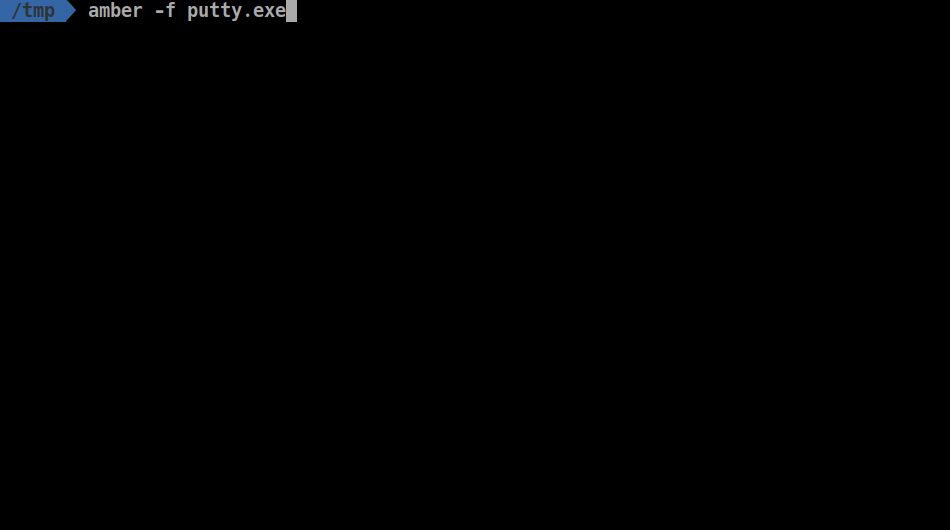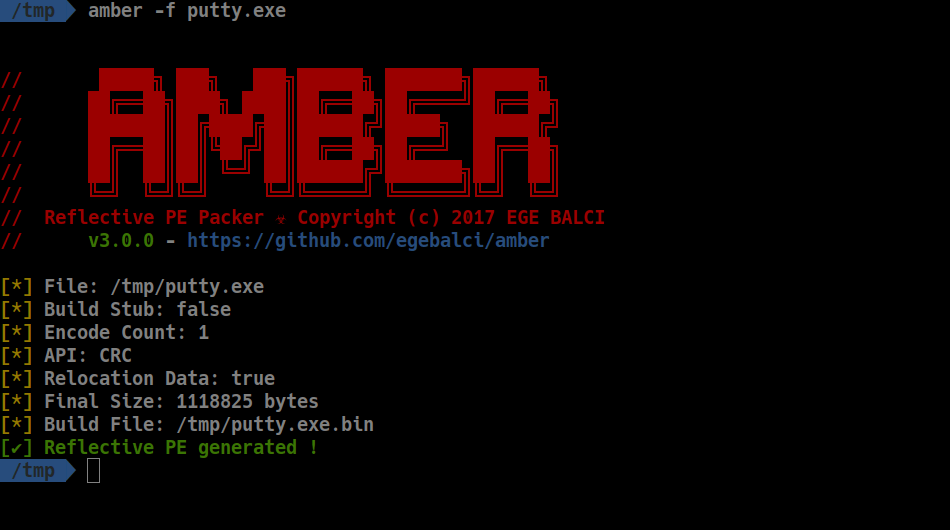
Amber is a position-independent(reflective) PE loader that enables in-memory execution of native PE files(EXE, DLL, SYS...). It enables stealthy in-memory payload deployment that can be used to bypass anti-virus, firewall, IDS, IPS products, and application white-listing mitigations. Reflective payloads generated by Amber can either be staged from a remote server or executed directly in memory much like a generic shellcode. By default, every generated payload is encoded using the new generation SGN encoder. Amber uses CRC32_API and IAT_API for inconspicuously resolving the Windows API function addresses. After the PE file is loaded and executed in memory, the reflective payload is erased for evading memory scanners.
Pre-compiled binaries can be found under releases.
Building From Source
The only dependency for building the source is the keystone engine, follow these instructions for installing the library. Once libkeystone is installed on the system, simply just go get it ツ
go install github.com/EgeBalci/amber@latest
Docker Install
docker pull egee/amber
docker run -it egee/amber
The following table lists switches supported by the amber.
| Switch | Type | Description |
|---|---|---|
| -f,--file | string | Input PE file. |
| -o,--out | string | Output binary payload file name. |
| -e | int | Number of times to encode the generated reflective payload |
| --iat | bool | Use IAT API resolver block instead of CRC API resolver block |
| -l | int | Maximum number of bytes for obfuscation (default 5) |
| --sys | bool | Perform raw syscalls. (only x64) |
| --scrape | bool | Scrape magic byte and DOS stub from PE. |
Example Usage
amber -f test.exe
amber -e 10 --iat -f test.exe
Docker Usage
docker run -it -v /tmp/:/tmp/ amber -f /tmp/file.exe

