
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
karma_v2 — ⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾ is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework) | Kitploit
Tools/GitHubGitHub/dheerajmadhukar/karma_v2
OSINT (Open Source Intelligence)ReconnaissanceVulnerability AnalysisDNS & Subdomain EnumerationInformation GatheringSubdomain EnumerationCrawler
GitHubdheerajmadhukar/karma_v2

karma_v2

⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾ is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)

View Repository
1.0k185182 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share
Website

karma_v2

⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾

𝚔𝚊𝚛𝚖𝚊 𝚟𝟸 is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)
Follow on Twitter Version Build Build Donate

𝚔𝚊𝚛𝚖𝚊 𝚟𝟸 can be used by Infosec Researchers, Penetration Testers, Bug Hunters to find deep information, more assets, WAF/CDN bypassed IPs, Internal/External Infra, Publicly exposed leaks and many more about their target. Shodan Premium API key is required to use this automation. Output from the 𝚔𝚊𝚛𝚖𝚊 𝚟𝟸 is displayed to the screen and saved to files/directories.

ℹ Regarding Premium Shodan API, Please see the Shodan site for more information.

Shodan website: Shodan Website API : Developer API

Features

  • Powerful and flexible results via Shodan Dorks
  • SSL SHA1 checksum/fingerprint Search
  • Only hit In-Scope IPs
  • Verify each IP with SSL/TLS certificate issuer match RegEx
  • Provide Out-Of-Scope IPs
  • Find out all ports including well known/uncommon/dynamic
  • Grab all targets vulnerabilities related to CVEs
  • Banner grab for each IP, Product, OS, Services & Org etc.
  • Grab favicon Icons
  • Generate Favicon Hash using python3 mmh3 Module
  • Favicon Technology Detection using nuclei custom template
  • ASN Scan
  • BGP Neighbour
  • IPv4 & IPv6 Profixes for ASN
  • Interesting Leaks like Indexing, NDMP, SMB, Login, SignUp, OAuth, SSO, Status 401/403/500, VPN, Citrix, Jfrog, Dashboards, OpenFire, Control Panels, Wordpress, Laravel, Jetty, S3 Buckets, Cloudfront, Jenkins, Kubernetes, Node Exports, Grafana, RabbitMQ, Containers, GitLab, MongoDB, Elastic, FTP anonymous, Memcached, DNS Recursion, Kibana, Prometheus, Default Passwords, Protected Objects, Moodle, Spring Boot, Django, Jira, Ruby, Secret Key and many more...

Installation

1. Clone the repo

# git clone https://github.com/Dheerajmadhukar/karma_v2.git

2. Install shodan & mmh3 python module

# python3 -m pip install shodan mmh3

3. Install JSON Parser [JQ]

# apt install jq -y

4. Install httprobe @tomnomnom to probe the requests

# go install -v github.com/tomnomnom/httprobe@master

5. Install Interlace @codingo to multithread [Follow the codingo interlace repo instructions]

# git clone https://github.com/codingo/Interlace.git & install accordingly. 

6. Install nuclei @projectdiscovery

# go install -v github.com/projectdiscovery/nuclei/v2/cmd/nuclei@latest

7. Install lolcat

# apt install lolcat -y

8. Install anew

# go install -v github.com/tomnomnom/anew@master

Ok, how do I use it?

# cat > .token
SHODAN_PREMIUM_API_HERE

Usage

You can use this command to check help:

$ bash karma_v2 -h
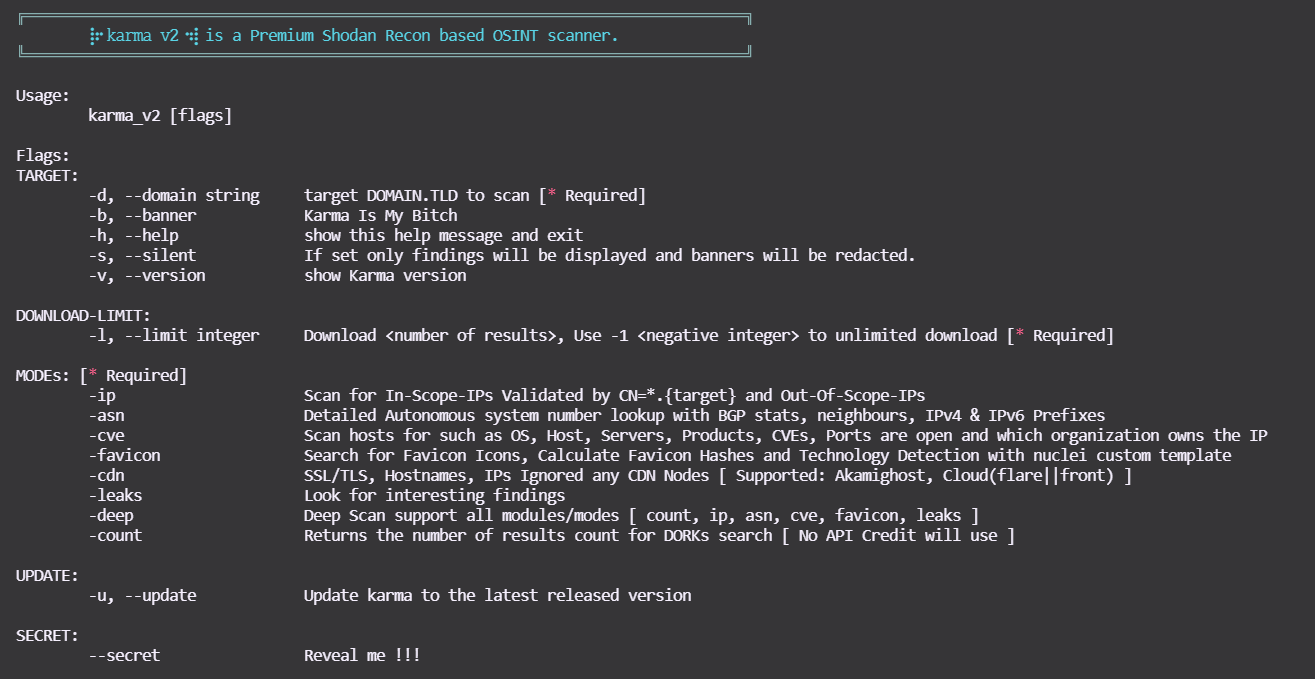
karma_v2

MODEs

MODEExamples
-ip bash karma_v2 -d <DOMAIN.TLD> -l <INTEGER> -ip
-asn bash karma_v2 -d <DOMAIN.TLD> -l <INTEGER> -asn
-cve bash karma_v2 -d <DOMAIN.TLD> -l <INTEGER> -cve
-cveid bash karma_v2 -d <DOMAIN.TLD> -l <INTEGER> -cveid CVE-2021-34473
-favicon bash karma_v2 -d <DOMAIN.TLD> -l <INTEGER> -favicon
-leaks bash karma_v2 -d <DOMAIN.TLD> -l <INTEGER> -leaks
-deep bash karma_v2 -d <DOMAIN.TLD> -l <INTEGER> -deep
-count bash karma_v2 -d <DOMAIN.TLD> -l <INTEGER> -count

Demo

  • karma_v2 [mode -ip] asciicast

  • karma_v2 [mode -asn] asciicast

  • karma_v2 [mode -cve] asciicast

  • karma_v2 [mode -favicon] asciicast

  • karma_v2 [mode -leaks]

asciicast


  • karma_v2 [mode -deep]

-deep support all the above modes e.g. -count,-ip,-asn,-favicon,-cve,-leaks !


Output

output/bugcrowd.com-YYYY-MM-DD/ 

.
├── ASNs_Detailed_bugcrowd.com.txt
├── Collect
│   ├── host_domain_domain.tld.json.gz
│   ├── ssl_SHA1_12289a814...83029f8944b6088d60204a92e_domain.tld.json.gz
│   ├── ssl_SHA1_17537bf84...73cb1d684a495db7ea5aa611b_domain.tld.json.gz
│   ├── ssl_SHA1_198d6d4ec...681b77585190078b07b37c5e1_domain.tld.json.gz
│   ├── ssl_SHA1_26a9c5618...d60eae2947b42263e154d203f_domain.tld.json.gz
│   ├── ssl_SHA1_3da3825a2...3b852a42470410183adc3b9ee_domain.tld.json.gz
│   ├── ssl_SHA1_4d0eab730...68cf11d2db94cc2454c906532_domain.tld.json.gz
│   ├── ssl_SHA1_8907dab4c...12fdbdd6c445a4a8152f6b7b7_domain.tld.json.gz
│   ├── ssl_SHA1_9a9b99eba...5dc5106cea745a591bf96b044_domain.tld.json.gz
│   ├── ssl_SHA1_a7c14d201...b6fd4bc4e95ab2897e6a0bsfd_domain.tld.json.gz
│   ├── ssl_SHA1_a90f4ddb0...85780bdb06de83fefdc8a612d_domain.tld.json.gz
│   ├── ssl_domain_domain.tld.json.gz
│   ├── ssl_subjectCN_domain.tld.json.gz
│   └── ssl_subject_domain.tld.json.gz
|   └── . . .
├── IP_VULNS
│   ├── 104.x.x.x.json.gz
│   ├── 107.x.x.x.json.gz
│   └── 99.x.x.x.json.gz
|   └── . . .
├── favicons_domain.tld.txt
├── host_enum_domain.tld.txt
├── ips_inscope_domain.tld.txt
├── main_domain.tld.data
├── . . . 

karma_v2 Newly Added Shodan Dorks

Download Tool