
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD Security Risks, with PoCs, remediation, and interview-ready summaries.

<div align="center"> # CICD-Goat VAPT Writeup </div> > A full vulnerability assessment & penetration test against [OWASP CICD-Goat](https://github.com/cider-security-research/cicd-goat) — a deliberately vulnerable CI/CD environment (Jenkins, Gitea, GitLab, CTFd) — mapped end-to-end against the **OWASP Top 10 CI/CD Security Risks**. <div align="center"> [](https://github.com/cider-security-research/cicd-goat) [](./findings) [](./ctfd/challenge-cross-reference.md) [](./LICENSE.md) [](https://linkedin.com/in/dheerajkumarjayaswal) [](https://github.com/dheeraj-jayaswal) </div> --- ## 🧭 How This Fits With My Other Repos | Repository | What's in it | |---|---| | **[CICD-Goat-Vapt-Writeup](https://github.com/dheeraj-jayaswal/CICD-Goat-Vapt-Writeup)** *(this repo)* | Full VAPT writeup against OWASP CICD-Goat — 16 findings including CVE-2024-23897, mapped to the OWASP Top 10 CI/CD Security Risks, with PoCs and interview-ready summaries | | [From-Dev-To-Attacker](https://github.com/dheeraj-jayaswal/From-Dev-To-Attacker) | My flagship field journal — 67 original write-ups on vulnerability patterns, written from a developer's lens, with enterprise domain-impact framing across Income Tax, Banking, Retail, E-commerce, Freight Logistics, and Education | | [From-Pentester-To-Red-Teamer](https://github.com/dheeraj-jayaswal/From-Pentester-To-Red-Teamer) | My structured 24-month roadmap for transitioning from Web/API pentesting into Red Teaming — phases, labs, certifications, and progress tracked openly as I work through it | | [AppSec-From-The-Trenches](https://github.com/dheeraj-jayaswal/AppSec-From-The-Trenches) | Pentest tools & methodology reference — how I actually use Burp Suite, Nmap, Metasploit, Hydra, Hashcat, and more, plus my WAPT methodology | | [API-From-The-Trenches](https://github.com/dheeraj-jayaswal/API-From-The-Trenches) | Deep-dive API security series — OWASP API Top 10 coverage, BOLA, JWT attacks, GraphQL testing, full methodology | | [Bug-Bounty-Hunting-Companion](https://github.com/dheeraj-jayaswal/Bug-Bounty-Hunting-Companion) | Real, publicly-disclosed bug bounty reports broken into reproducible checklists | | [DarkWeb-From-The-Trenches](https://github.com/dheeraj-jayaswal/DarkWeb-From-The-Trenches) | Threat intelligence & dark web OSINT methodology — credential leak monitoring, ransomware tracking, pre-engagement TI | | [.pcap-Arsenal](https://github.com/dheeraj-jayaswal/.pcap-Arsenal) | Packet captures organized by protocol, for Web/API/Network-layer analysis and learning | | [Pentest-Engagement-Playbook](https://github.com/dheeraj-jayaswal/Pentest-Engagement-Playbook) | Consultant-grade scoping, ROE, severity rationale, and executive reporting templates — the client-facing operational playbook behind an engagement | --- ## Why this exists Most CI/CD security writeups either stay purely theoretical (a slide explaining "poisoned pipeline execution") or purely CTF-flag-chasing (a one-line "here's the flag, next"). This repo tries to do neither: every finding below is a **fully validated, PoC-backed vulnerability**, mapped to a specific [OWASP CI/CD-SEC](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/02-owasp-top10-cicd-mapping.md) risk category, written the way you'd actually want to explain it in an interview or a real client report — including the dead ends, the wrong assumptions, and how they got corrected. If you're studying for an AppSec/DevSecOps/CI-CD-security interview, prepping for a pentest engagement involving a CI/CD toolchain, or just want a concrete, hands-on tour of what "Poisoned Pipeline Execution" or "Insufficient Credential Hygiene" actually looks like on the wire — this is written for you. ## Target environment | Field | Value | |---|---| | Target | [OWASP CICD-Goat](https://github.com/cider-security-research/cicd-goat) — local Docker Compose deployment | | Engagement type | Authorized self-directed learning lab (grey-box) | | Tech stack | Jenkins 2.332.1, Gitea 1.16.5, GitLab 15.11.13-ee, CTFd, Docker Compose | | Scope | `localhost:3000` (Gitea), `:8080`/`:50000` (Jenkins), `:4000` (GitLab), `:8000` (CTFd), `:8008` (prod-sim) | | Methodology | Phase 0–3 (Scope → Fingerprinting → Vulnerability ID → Exploitation) | Full rules of engagement: [`docs/00-engagement-overview.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/00-engagement-overview.md). > ⚠️ **All testing in this repo was performed against the tester's own local, disposable, intentionally-vulnerable Docker Compose lab.** No production systems, shared infrastructure, or third-party data were involved. Spin up your own copy of CICD-Goat from the [official repo](https://github.com/cider-security-research/cicd-goat) before trying any of this yourself. ## Results at a glance | ID | Title | Severity | OWASP CI/CD Mapping | CTFd Flag | |---|---|---|---|---| | [F-010](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-010-jenkins-secrets-exposure-console-logs.md) | Secrets exposure in Jenkins build console logs → credential theft → unauthorized repo write | **CRITICAL** | CICD-SEC-6, -4, -2 | flag1, flag2 | | [F-013](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-013-insecure-automerge-bypass.md) | Insecure auto-merge logic bypasses code review (PR-wide word-diff heuristic) | **CRITICAL** | CICD-SEC-1, -5 | flag10 | | [F-016](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-016-CVE-2024-23897-jenkins-cli-arbitrary-file-read.md) | CVE-2024-23897 — Jenkins CLI arbitrary file read on the controller | **CRITICAL** | CICD-SEC-7 | flag8 | | [F-017](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-017-gitlab-runner-token-secret-theft.md) | GitLab shared-runner registration token → instance-wide CI/CD secret theft | **CRITICAL** | CICD-SEC-2, -6 | flag11 | | [F-019](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-019-jenkins-controller-rce-agent-label-override.md) | Jenkins controller-node code execution via agent label override | **CRITICAL** | CICD-SEC-5, -4 | flag5 | | [F-018](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-018-decoupled-pipeline-branch-exclusion-bypass.md) | Decoupled pipeline repo + branch exclusion filter bypass | HIGH | CICD-SEC-4, -6 | flag3 | | [F-020](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-020-shared-agent-filesystem-credential-leak.md) | Shared agent filesystem exposes FreeStyle job credential | HIGH | CICD-SEC-6, -5 | flag6 | | [F-021](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-021-checkov-sast-config-override-bypass.md) | Checkov SAST config override enables undetected IaC misconfiguration | HIGH | CICD-SEC-1, -8 | flag7 | | [F-014](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-014-flask-secret-key-cicd-variable.md) | Flask session secret key derived from a CI/CD pipeline variable | HIGH | CICD-SEC-6 | flag11 (via F-017) | Plus **6 informational / supporting findings** (positive controls, RBAC boundary confirmations, minor info-disclosure) in [`findings/informational/`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational). ### How the findings chain together Several findings aren't independent — one directly enables or completes another. This is the part that tends to impress in an interview more than any single finding on its own: 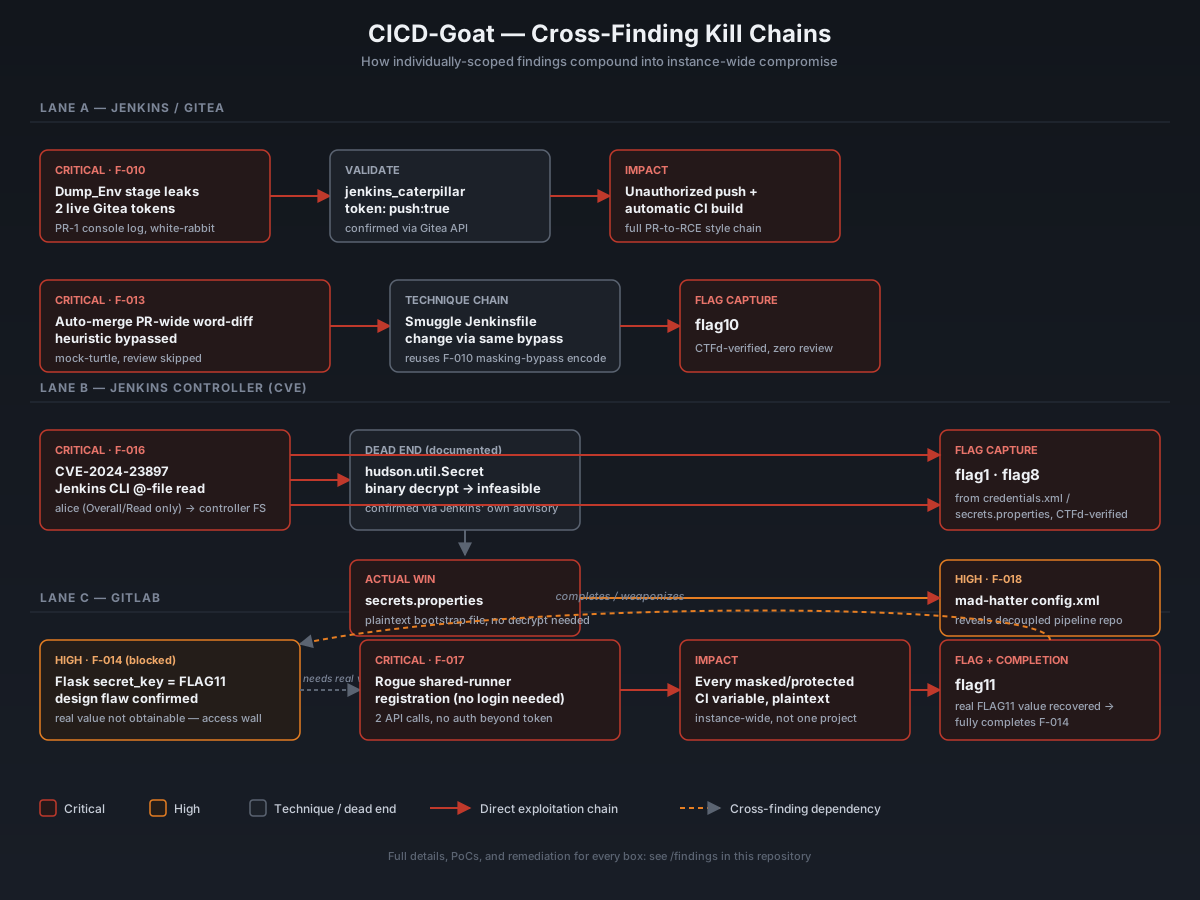 **9 of 11 CTFd challenges solved and flag-verified** — see the full [challenge cross-reference](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/ctfd/challenge-cross-reference.md), including an honestly-documented case (Dormouse/flag9) where the access-control boundary held under sustained attack. ## Full Table of Contents Every file below is directly linked — the folder tree just shows how they're organized. ### 📋 Engagement Docs | File | What's in it | |---|---| | [`docs/00-engagement-overview.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/00-engagement-overview.md) | Rules of engagement, scope, tech stack | | [`docs/01-methodology.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/01-methodology.md) | Phase-by-phase testing methodology used throughout | | [`docs/02-owasp-top10-cicd-mapping.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/02-owasp-top10-cicd-mapping.md) | Full CICD-SEC-1 through -10 reference taxonomy | | [`docs/03-remediation-roadmap.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/03-remediation-roadmap.md) | Prioritized, actionable remediation checklist | | [`docs/04-interview-prep.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/04-interview-prep.md) | Spoken-style summaries of every finding + likely follow-up questions | | [`docs/05-lessons-learned.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/05-lessons-learned.md) | Retrospective — what worked, what didn't, what to do differently next time | ### 🔍 Recon | File | What's in it | |---|---| | [`recon/01-fingerprinting.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/recon/01-fingerprinting.md) | Phase 1 — unauthenticated fingerprinting of every service in scope | | [`recon/02-authenticated-enumeration.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/recon/02-authenticated-enumeration.md) | Phase 2 — authenticated enumeration once initial access was gained | ### 🚨 Critical & High Findings | File | |---| | [F-010 — Jenkins secrets exposure via console logs](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-010-jenkins-secrets-exposure-console-logs.md) | | [F-013 — Insecure auto-merge bypass](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-013-insecure-automerge-bypass.md) | | [F-014 — Flask secret key from CI/CD variable](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-014-flask-secret-key-cicd-variable.md) | | [F-016 — CVE-2024-23897 Jenkins CLI arbitrary file read](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-016-CVE-2024-23897-jenkins-cli-arbitrary-file-read.md) | | [F-017 — GitLab runner token secret theft](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-017-gitlab-runner-token-secret-theft.md) | | [F-018 — Decoupled pipeline branch exclusion bypass](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-018-decoupled-pipeline-branch-exclusion-bypass.md) | | [F-019 — Jenkins controller RCE via agent label override](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-019-jenkins-controller-rce-agent-label-override.md) | | [F-020 — Shared agent filesystem credential leak](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-020-shared-agent-filesystem-credential-leak.md) | | [F-021 — Checkov SAST config override bypass](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-021-checkov-sast-config-override-bypass.md) | ### ℹ️ Informational / Supporting Findings | File | |---| | [F-006 — Private repo enumeration gap](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-006-private-repo-enumeration-gap.md) | | [F-007 — Additional Jenkins user](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-007-additional-jenkins-user.md) | | [F-009 — Job Read vs ExtendedRead](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-009-job-read-vs-extendedread.md) | | [F-011 — Correct withCredentials usage (positive control)](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-011-correct-withcredentials-usage.md) | | [F-012 — Credentials API connection drop](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-012-credentials-api-connection-drop.md) | | [F-015 — Anonymous registry enumeration](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-015-anonymous-registry-enumeration.md) | ### 🎯 CTFd | File | What's in it | |---|---| | [`ctfd/challenge-cross-reference.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/ctfd/challenge-cross-reference.md) | Full flag-by-flag cross-reference, including the blocked Dormouse/flag9 investigation and the Duchess/flag4 correction | ## Repo structure ``` . ├── docs/ # Engagement context, methodology, mappings, remediation, interview prep │ ├── 00-engagement-overview.md │ ├── 01-methodology.md │ ├── 02-owasp-top10-cicd-mapping.md │ ├── 03-remediation-roadmap.md │ ├── 04-interview-prep.md │ └── 05-lessons-learned.md ├── recon/ # Phase 1 & 2 — fingerprinting and authenticated enumeration │ ├── 01-fingerprinting.md │ └── 02-authenticated-enumeration.md ├── findings/ # One file per confirmed finding, full PoC + remediation │ ├── F-010-...md ... F-021-...md │ └── informational/ # INFO/LOW severity supporting observations ├── ctfd/ │ └── challenge-cross-reference.md └── LICENSE.md ``` ## Reading paths - **Just want the highlights?** Start with the [results table above](#results-at-a-glance), then read F-010, F-013, F-016, and F-017 — the four most complete end-to-end kill chains. - **Studying for an interview?** Go straight to [`docs/04-interview-prep.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/04-interview-prep.md) — one-paragraph, spoken-style summaries of every major finding, plus common follow-up questions. - **Building/hardening a CI/CD pipeline?** Go straight to [`docs/03-remediation-roadmap.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/03-remediation-roadmap.md) — a prioritized, actionable checklist. - **New to CI/CD security concepts?** Start with [`docs/02-owasp-top10-cicd-mapping.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/02-owasp-top10-cicd-mapping.md) for the reference taxonomy this whole repo is organized around. ## About OWASP Top 10 CI/CD Security Risks Every finding here is mapped against the [OWASP Top 10 CI/CD Security Risks (2023)](https://owasp.org/www-project-top-10-ci-cd-security-risks/) — a full reference table (CICD-SEC-1 through CICD-SEC-10) lives in [`docs/02-owasp-top10-cicd-mapping.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/02-owasp-top10-cicd-mapping.md), since it's referenced constantly throughout the individual findings. ## Disclaimer This repository documents testing performed **exclusively against a local, self-hosted, intentionally-vulnerable training lab** ([OWASP CICD-Goat](https://github.com/cider-security-research/cicd-goat)), for educational and portfolio purposes. Nothing here targets, references, or was tested against any production system, third-party service, or real credential. Do not use any technique in this repo against systems you do not own or have explicit written authorization to test. --- ## 🧠 Testing Philosophy > *"The best penetration testers think like developers first and attackers second. If you understand why code was written a certain way, you'll always find more than a scanner ever will."* I approach every engagement in three phases: **1. Understand before you attack** — Read the application. Use it as a real user. Understand the business logic before touching a single tool. **2. Manual first, tools second** — Automated scanners find what they're configured to find. The interesting bugs are always found by thinking, not scanning. **3. Report like a developer** — A finding that developers can't understand or reproduce is a finding that doesn't get fixed. --- ## 👤 About Me - 👤 **Name** — Dheeraj Kumar Jayaswal - 🌍 **Location** — Dublin, County Dublin, Ireland - 💼 **Role** — Principal Penetration Testing Consultant | VikingCloud (previously Technology Lead – Offensive Security, Infosys Limited) - 🎯 **Primary Focus** — Web Application & API Security — Offensive Security Consulting - 🏆 **Experience** — 16+ Years in IT | 9+ Years in Offensive Security - 🔎 **Edge** — Started as a full-stack developer (ASP.NET / SQL Server) — I think like a developer and attack like a hacker - 🎓 **Pursuing** — OSWE — OffSec Web Expert (OSCE3 track) - 🏢 **Domains** — Income Tax · Banking · Retail · E-commerce · Freight Logistics · Education - 📝 **Sharing** — Enterprise pentest field notes, methodology, and practical write-ups from real-world engagements --- ## 🏅 Certifications | Certification | Issuer | Status | |---|---|---| | Certified Ethical Hacker (CEH) | EC-Council | ✅ 2021 | | AWS Certified Solutions Architect – Associate | Amazon Web Services | ✅ 2022 | | AWS Certified Cloud Practitioner | Amazon Web Services | ✅ 2022 | | Executive Certificate in Cyber Security | IIT Kanpur | ✅ 2026 | | OSWE — OffSec Web Expert (OSCE3 track) | OffSec | 🔄 In Progress | **Future direction — Red Teaming:** OSCP → CRTO → OSEP, CRTP, CRTL, CRTE --- ## 📄 License This content is licensed under **[CC BY 4.0](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/LICENSE.md)**. You're welcome to reuse or adapt any of this write-up — just give clear attribution to **Dheeraj Kumar Jayaswal** with a link back to this repository. CICD-Goat itself is a separate project by [Cider Security](https://github.com/cider-security-research/cicd-goat) — go star the original. --- ## 🤝 Connect [LinkedIn](https://linkedin.com/in/dheerajkumarjayaswal) — open to consulting, collaboration, and security discussions. Feedback, corrections, and PRs (e.g. for flag9/Dormouse, or the Duchess/flag4 follow-up in the [CTFd cross-reference](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/ctfd/challenge-cross-reference.md)) are welcome — see [CONTRIBUTING.md](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/CONTRIBUTING.md).
