
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-2639-PipeVersion — Linux kernel local privilege escalation exploit for CVE-2022-2639 using pipe-primitive technique, bypassing KASLR, SMAP, SMEP, and KPTI. Tested on kernels 5.13, 5.4, and 4.18. | Kitploit
Tools/GitHubGitHub/devetop/cve-2022-2639-pipeversion
Privilege EscalationVulnerability AnalysisExploitationLearning & EducationBinary Exploitation
GitHubdevetop/cve-2022-2639-pipeversion

CVE-2022-2639-PipeVersion

Linux kernel local privilege escalation exploit for CVE-2022-2639 using pipe-primitive technique, bypassing KASLR, SMAP, SMEP, and KPTI. Tested on kernels 5.13, 5.4, and 4.18.

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share
View Repository
1 year agoNot yet reviewed

CVE-2022-2639 (using pipe primitive)

CVE-2022-2639: Linux kernel openvswitch local privilege escalation.

  • introduced in: e64457191a259537bbbfaebeba9a8043786af96f (v3.13)

  • fixed in: cefa91b2332d7009bc0be5d951d6cbbf349f90f8 (v5.18)

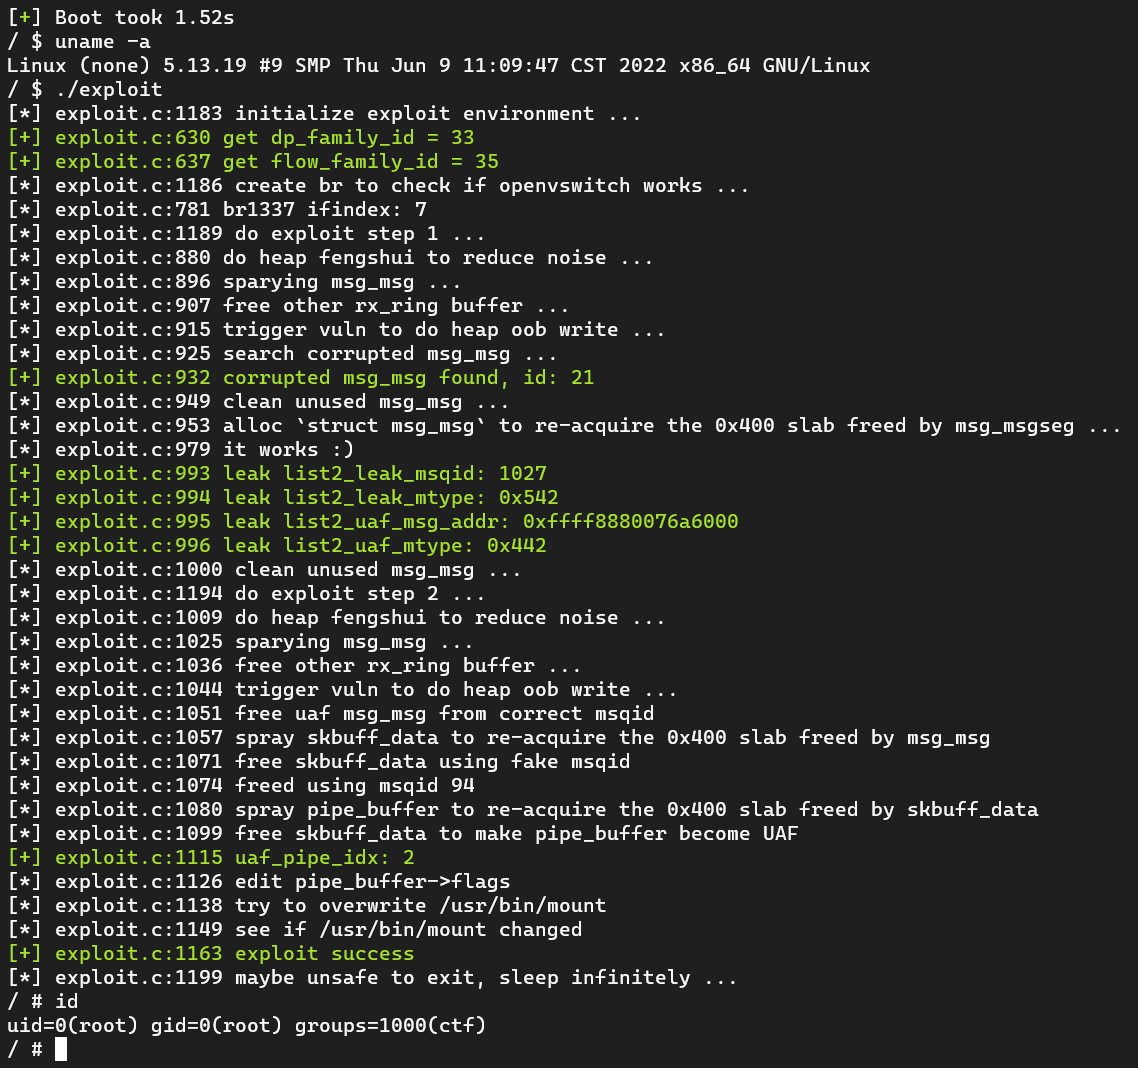
Using pipe-primitive to exploit CVE-2022-2639, so no kaslr leak nor smap smep ktpi bypass is needed :)

(Q: What is pipe-primitive? A: https://github.com/veritas501/pipe-primitive)

Chinese writeup: coming soon.

!! For educational / research purposes only. Use at your own risk. !!

Tested on 5.13, 5.4, 4.18.
Download Tool