 demining/vulnerable-to-debian-openssl-bug-cve-2008-0166
Search for BTC coins on earlier versions of Bitcoin Core with critical vulnerability OpenSSL 0.9.8 CVE-2008-0166

In this article, we will create a tool that will generate Bitcoin Addresses (P2PKH) using the CVE-2008-0166 vulnerability. This is a research project to find BTC coins on earlier versions of the Bitcoin Core software client.
Random number generator that generates predictable numbers CVE-2008-0166
VAIM-OpenSSL 0.9.8/1.0.0 Detected
The critical vulnerability version OpenSSL 0.9.8 CVE-2008-0166 was populated with process ID only. Due to differences between endianness and sizeof(long), the output is architecture dependent: 32 -bit big endian (for example, i386), 64 -bit big endian (for example, amd64, ia64), 32 -bit big endian (for example, powerpc , sparc). PID 0 is the core, and PID_MAX ( 32768 ) is not reached by porting, so there were 32767 possible random number streams for each architecture.
The Bitcoin Core software client uses the OpenSSL. Specifically, it uses a function «EC_KEY_generate_key()» to generate Bitcoin Addresses (like a key) to receive payments. Old versions of Bitcoin Core generate and store 100 keys in wallet.dat
A new key is generated only when a Bitcoin payment is received. Thus, the Bitcoin Core software client maintains a pool of 100 unused Bitcoin Keys (addresses) . The state of the internal random number generator depends on what other calls were made to the library OpenSSL prior to the call 'EC_KEY_generate_key()' . Challenges affecting the internal state of the RNG: «RAND_add(8)», «RAND_bytes(8)» и «RAND_bytes(32)».
So the research was to go through a lot of old bitcoin sources to find out what calls were made that affected the internal state of the RNG before the call «EC_KEY_generate_key()». The call path changes between versions of the Bitcoin Core software client
The study focused on the following versions:
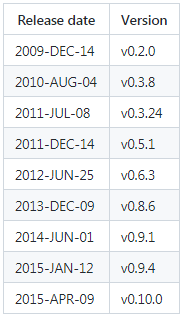 | Release date | Version |
Our goal is to generate private keys for each version of the Bitcoin Core software client, for each architecture (le32/le64), for each process ID and for Bitcoin Addresses (P2PKH), using a random number from a critical vulnerability. OpenSSL 0.9.8.
Ultimately, we will create a Bitcoin Address Generator (P2PKH) and everything will be saved to a file result.txt
 Everything will be stored in the Google Drive file storage
For this we will use the distribution kit «Ubuntu 18.04.5 LTS» from Google Colab
Earlier we recorded a video instruction : «TERMINAL in Google Colab create all the conveniences for working in GITHUB»
Open Google Colab in Terminal [TerminalGoogleColab]
Let’s run the command:
cat /etc/lsb-release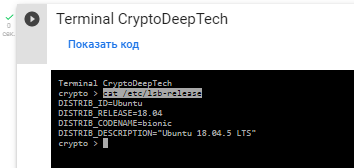 «Ubuntu 18.04.5LTS»
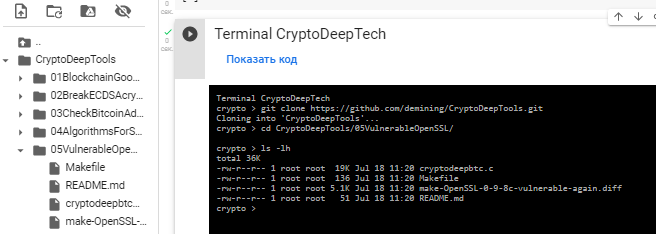
Let’s go to the «CryptoDeepTools» repository and take a look at the details
git clone https://github.com/demining/CryptoDeepTools.gitcd CryptoDeepTools/05VulnerableOpenSSL/
ls -lh
Update and install g++ libgmp3-dev libmpfr-dev
apt-get update