 cwjchoi01/cve-2026-3796
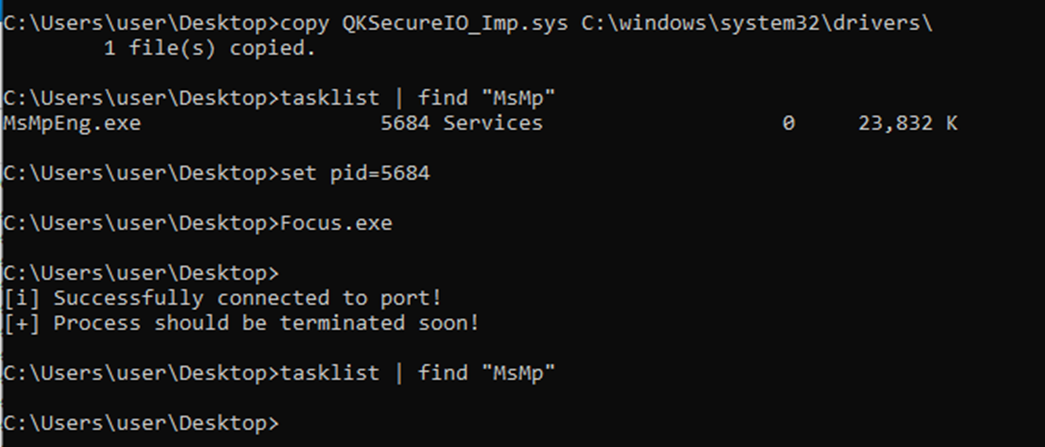
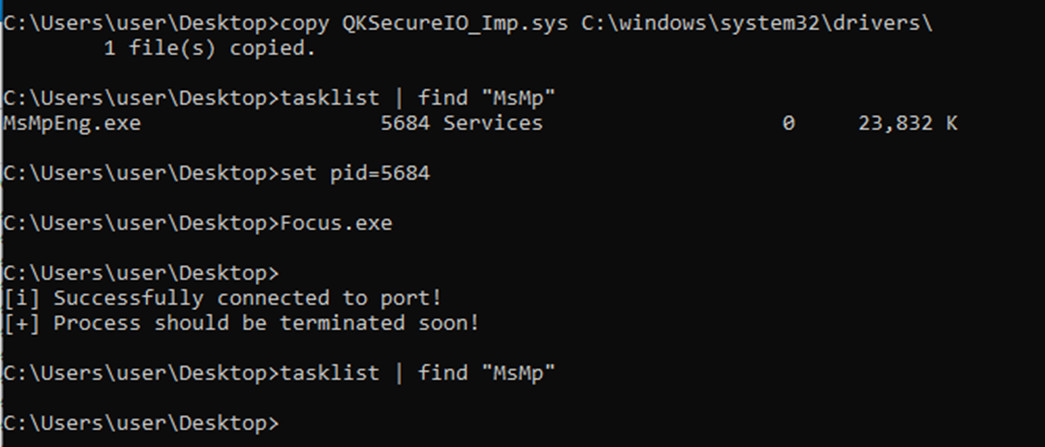
Proof-of-concept exploit for CVE-2026-3796, demonstrating arbitrary process termination via a vulnerable QAX driver. Includes usage instructions and is intended for educational and research purposes.

In QAX Virus Removal version dated 2025-10-22 and earlier, the affected driver QKSecureIO_Imp.sys rely on caller process's image to determine whether they are allowed to communicate to the mini filter driver. Attackers could
impersonate a legitimate caller process image through tactics such as DLL sideloading, Process Injection to send message with specific payload to the mini filter and perform
arbitrary process termination, such as protected process.
The application is used to remove virus. One of the imported function of the application's driver is ZwTerminateProcess, there is a lack of checking on the supplied process to kill, allowing arbitrary process termination. There is also a simple check by the driver on the caller process's identity, which can be bypassed using technique such as DLL sideloading.
x86C:\Windows\system32\driversset pid=<your_target_pid_to_kill>Note: The vulnerable driver will not be shared in this project.
This tool is for educational and research purposes only. Use it only on systems you own or have explicit permission to test. The author is not responsible for any misuse or damage caused by this program.