 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info

General information
Contents
SP605 board configuration
Software configuration
Examples
Using Python API
Practical DMA attacks
Option ROM attacks
Troubleshooting
Building project from the source code
This repository contains a set of tools and proof of concepts related to PCI-E bus and DMA attacks. It includes HDL design that implements software controllable PCI-E gen 1.1 endpoint device for Xilinx SP605 Evaluation Kit with Spartan-6 FPGA. In comparison with popular USB3380EVB this design allows to operate with raw Transaction Level Packets (TLP) of PCI-E bus and perform full 64-bit memory read/write operations. To demonstrate applied use cases of the design, there's a tool for pre-boot DMA attacks on UEFI based machines which allows to execute arbitrary UEFI DXE drivers during platform init.
There's a program that shows how to use pre-boot DMA attacks to inject Hyper-V VM exit handler backdoor into the virtualization-based security enabled Windows 10 and 11 running on UEFI Secure Boot enabled platform. Provided Hyper-V Backdoor PoC might be useful for reverse engineering and exploit development purposes, it provides an interface for inspecting of hypervisor state (VMCS, physical/virtual memory, registers, etc.) from the guest partition and perform guest to host VM escape attacks.
Another program shows how to use pre-boot DMA attacks to inject arbitrary user mode or kernel mode code into the Windows operating system by hijacking of its boot process using Boot Backdoor. This program is also can work with DMA Shell − it's Boot Backdoor payload that allows to execute console commands over the rogue PCI-E device, transfer files and load 3-rd party executables into the target operating system at the runtime.
💾 Hyper-V Backdoor part of this project has many other features and deployment options than described in this document, you can use it separately from DMA attack tools even without any special hardware: check its documentation
💾 Boot Backdoor part of this project has many other features and deployment options than described in this document, you can use it separately from DMA attack tools even without any special hardware: check its documentation
💾 Python tools from this project and FPGA designs for SP605, ZC706 and PicoEVB boards also can be used to deploy SMM Backdoor Next Gen with pre-boot DMA attack. Check its documentation for more technical details.
🛠️ Python tools and payloads from this project, including Hyper-V Backdoor and Boot Backdoor, also can be used with Xilinx Zynq-7000 SoC based boards. There's a separate project of DMA attacks design for Xilinx ZC706 evaluation kit.
🛠️ Python tools and payloads from this project, including Hyper-V Backdoor and Boot Backdoor, also can be used with PicoEVB development board. There's a separate Pico DMA project − fully autonomous pre-boot DMA attack hardware implant for M.2 slot that can run arbitrary UEFI DXE drivers as payload.
s6_pcie_microblaze.xise − Xilinx ISE project file.
microblaze/pcores/axis_pcie_v1_00_a/ − Custom peripheral module that allows connecting of PCI Express integrated endpoint block of Spartan-6 FPGA as raw TLP stream to MicroBlaze soft processor core.
sdk/srec_bootloader_0/ − Simple bootloader for MicroBlaze soft processor, it using SREC image format and onboard linear flash memory of SP605 to load and store main MicroBlaze program.
sdk/main_0/ − Main program for MicroBlaze soft processor, it forwards raw TLP packets of PCI-E bus into the TCP connection using onboard Ethernet port of SP605 and lwIP network stack.
python/pcie_lib.py − Python library to interact over the network with main MicroBlaze program running on SP605 board, it implements various low level and high level abstractions to work with TLP level of PCI-E from the Python code.
python/pcie_mem.py − Command line program that dumps host RAM into the screen or output file by sending MRd TLPs.
python/pcie_mem_scan.py − Command line program that scans target host for physical memory ranges accessible over PCI-E bus, it's useful for a security audit of IOMMU enabled platforms (examples: 1, 2, 3, 4).
python/uefi_backdoor_simple.py − Command line program for pre-boot DMA attack that injects dummy UEFI driver into the target machine boot sequence.
python/uefi_backdoor_hv.py − Command line program for pre-boot DMA attack that injects Hyper-V VM exit handler backdoor into the target system boot sequence.
python/uefi_backdoor_boot.py − Command line program for pre-boot DMA attack that injects Boot Backdoor into the target system boot sequence.
python/payloads/DmaBackdoorSimple/ − Source code of dummy UEFI DXE driver to use with uefi_backdoor_simple.py.
python/payloads/DmaBackdoorHv/ − Source code of UEFI DXE driver to use with uefi_backdoor_hv.py, it implements Hyper-V Backdoor functionality.
python/payloads/DmaBackdoorBoot/ − Source code of UEFI DXE driver to use with uefi_backdoor_boot.py, it implements Boot Backdoor functionality.
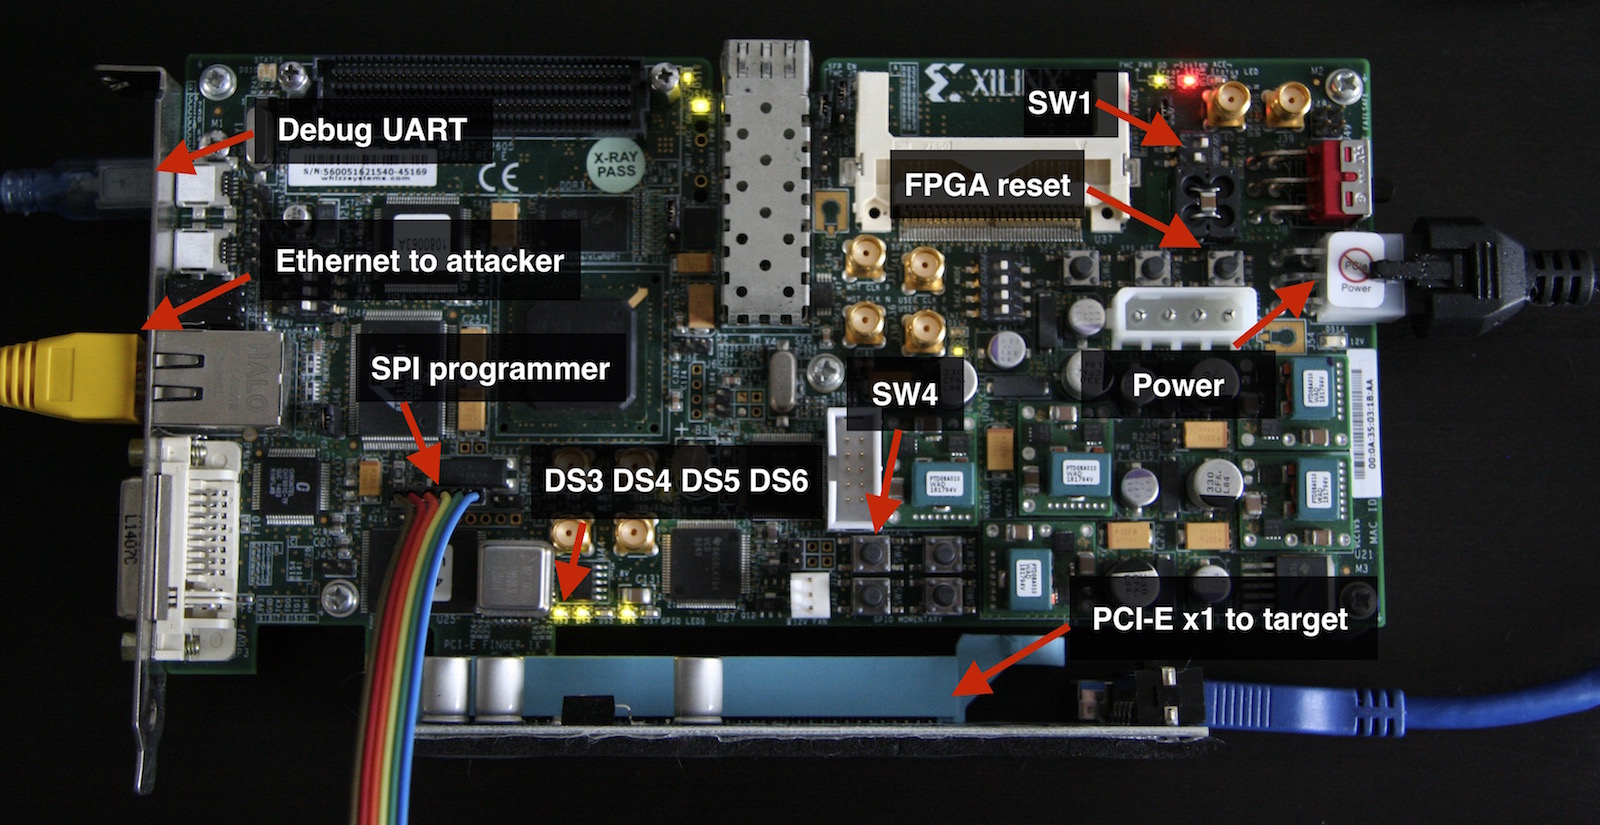
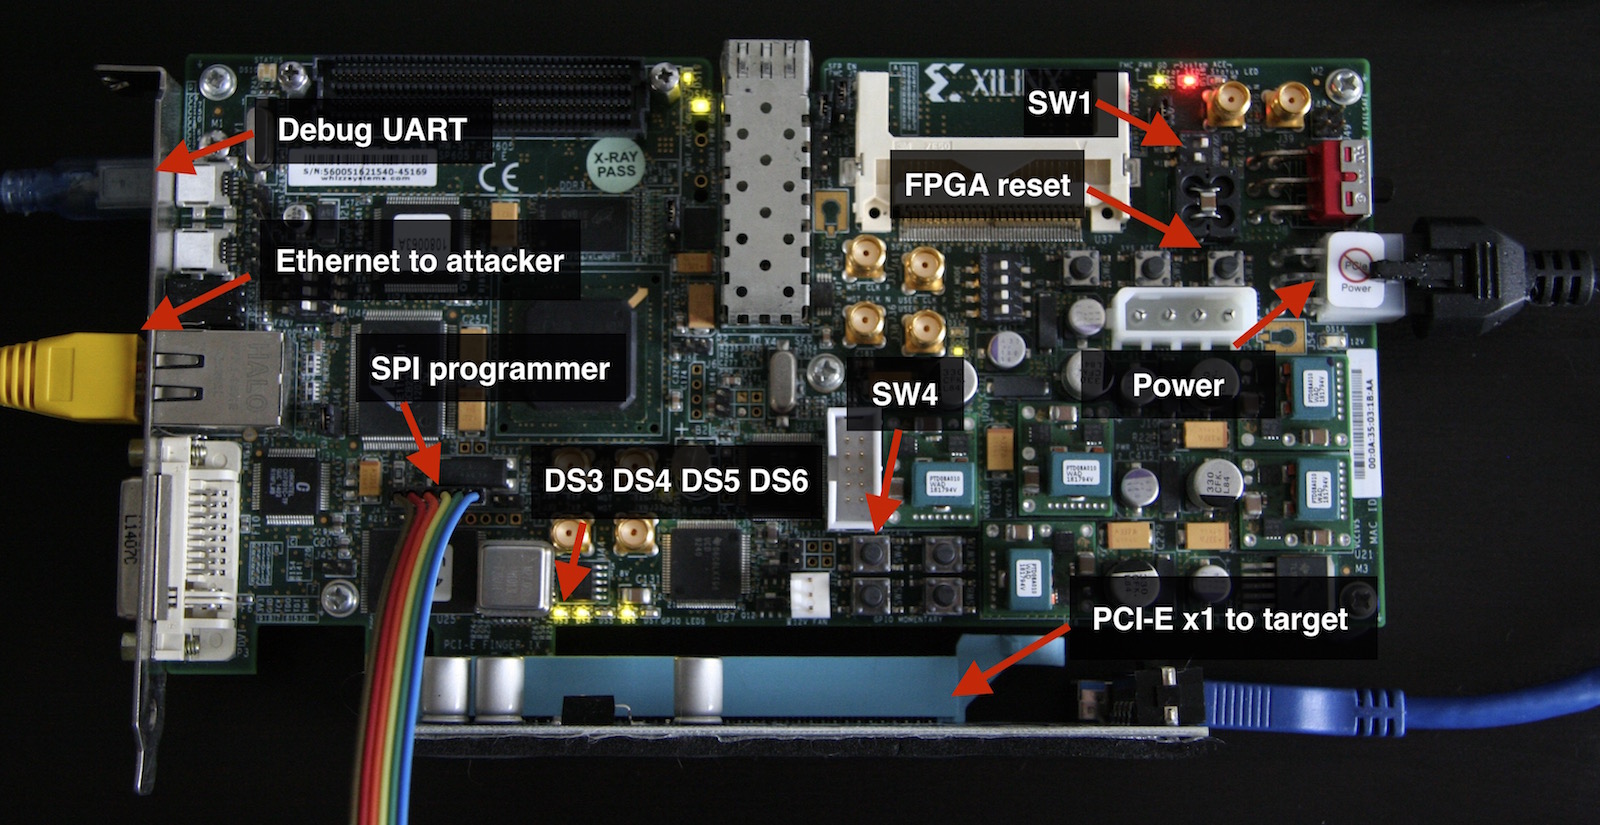
Xilinx UG526 document also known as SP605 Hardware User Guide is your best friend if you want to know more details about usage and configuration of this nice board.
SW1 switches into the 1-ON, 2-OFF position.