Offline simple-git evidence checker for CVE-2026-102826. Git configuration and package evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads.





Offline evidence checker for CVE-2026-102826 — simple-git configuration include command injection.
It compares simple-git version evidence that you supply (CLI values, JSON/CSV inventories, npm lockfiles, installed manifests) with the reviewed advisory rules, and can list lexical source review candidates. It never contacts websites, imports application code, runs Git or a package manager, or executes exploit payloads.
potentially_affected is not confirmed exploitability, and fixed_version_reported never attests an installed patch or safety. Every result retains exploitability: not_tested.unknown. unknown is neither a finding nor a clean result.Operate it only on evidence you are authorized to handle. Reports contain operator data; keep real targets, inventories and reports out of commits.
simplegit_rce_check.py can be copied and run alone. It bundles its own bounded input/reporting helpers and source lexer, and needs no companion repository at runtime.python simplegit_rce_check.py --version 4.0.0 --format json
python simplegit_rce_check.py --inventory examples/inventory.example.json --format html --output report.html
python simplegit_rce_check.py --csv-list inventory.csv --fail-on-finding
python simplegit_rce_check.py --help
python -m unittest -v
inventory.csv is your own file (see JSON and CSV inventories); the other inputs ship in examples/. The default output format is CSV on stdout. python -m unittest -v runs the local-only synthetic tests.
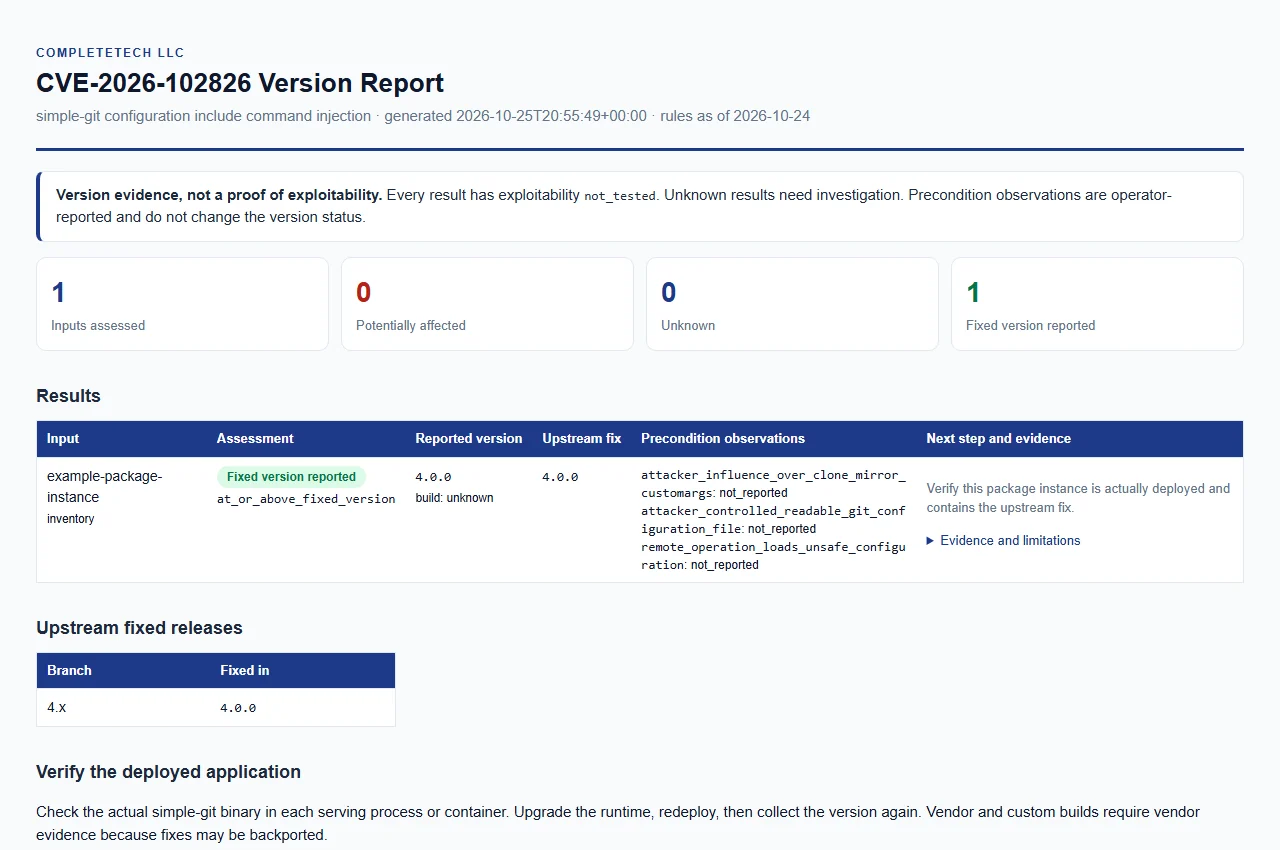
Open the synthetic example report. Example data only; this is not a live assessment.
The primary advisory and reviewed database were retrieved on 2026-10-24 (rules_as_of in every report).
| Example reported version | Result |
|---|---|
| 3.35.9 | potentially_affected |
| 3.36.0 | potentially_affected |
| 3.36.1 | unknown |
| 3.99.0 | unknown |
| 4.0.0 | fixed_version_reported |
| 4.0.1 | fixed_version_reported |
| 5.0.0 | unknown |
Do not invent affected status for hypothetical versions between 3.36.0 and 4.0.0. include.path and includeIf variants share this advisory.
| Status | Meaning |
|---|---|
potentially_affected | The reported version is in the documented affected interval (up to and including 3.36.0). Application preconditions and exploitability were not established; this is not confirmed exploitability. |
fixed_version_reported | The reported version is 4.0.0 or later within the reviewed 4.x fixed line. This describes a version claim only; it never attests an installed patch or safety. |
unknown | Anything else: versions outside the affected interval and fixed line (no safety or other-vulnerability conclusion is made), future lines (no patch claim is extrapolated), and missing, conflicting, malformed, prerelease, qualified or custom/vendor builds. |
Each row also carries a more specific version_status, such as in_documented_affected_range, at_or_above_fixed_version, outside_reviewed_range, version_not_disclosed, conflicting_versions, qualified_version_unverified, unrecognized_or_partial_version or vendor_build_unverified. The build_source value unknown (the default), upstream or official is compared as an upstream build; any other value, such as a vendor name, keeps the result unknown until independent patch evidence exists. Leading v prefixes are accepted.
Three optional observations describe advisory preconditions. They are supplied by the operator, unverified, and never change the package-version result.
| Observation | Meaning |
|---|---|
attacker_influence_over_clone_mirror_customargs | attacker influence over clone/mirror customArgs |
attacker_controlled_readable_git_configuration_file | attacker-controlled readable Git configuration file |
remote_operation_loads_unsafe_configuration | remote operation loads unsafe configuration |
Each observation is boolean or null (not reported). Absent observations do not establish mitigation. Optional lexical source inspection is separate from them, and file-pattern findings show review targets, not proven input taint.
At least one input is required. Modes can be combined in one run; every input produces its own rows. Unless noted, each input file must be named explicitly and is only read.
--version (alias --package-version) is repeatable. Each value is a separate instance, not evidence reconciliation for a single instance. --build-source and the observation flags (the observation key with underscores turned into hyphens, value true or false) apply to all CLI versions.
python simplegit_rce_check.py --version 3.36.0 --version 4.0.1 --format json
python simplegit_rce_check.py --version 4.0.0 --build-source "Example Vendor" --attacker-controlled-readable-git-configuration-file true
The second command stays unknown because the build is vendor-supplied.








