
 completetech-security/node-cve-2026-56846-check
Offline Node.js evidence checker for CVE-2026-56846: HTTP/2 retained header memory exhaustion. Single-file Python; JSON/CSV/HTML reports; no exploit payloads.





Offline evidence checker for CVE-2026-56846 — Node.js: HTTP/2 retained header memory exhaustion. It compares operator-reported Node.js runtime versions with the fixed releases named in the vendor's security release and writes a conservative, version-only triage report. Python 3.10+, standard library only; the executable can be copied alone.
Version evidence, not an exposure test. Results describe the versions you report. They do not establish that a vulnerable code path is reachable, that a deployed runtime has been patched, or that anything was exploited.
The checker:
--version, a JSON inventory or a CSV list) with the fixed releases for Node.js 22.x and 24.x;The checker never:
exploitability: not_tested;Hidden versions, custom builds, conflicting evidence and uncovered release lines remain unknown. A public URL is not an inventory.
# Assess one reported version and print JSON
python node_cve_2026_56846_check.py --version 22.23.2 --format json

# Assess the synthetic example inventory and save an HTML report
python node_cve_2026_56846_check.py --inventory examples/inventory.example.json --format html --output report.html

# Assess a CSV list (CSV is the default format) and exit 1 on a finding
python node_cve_2026_56846_check.py --csv-list inventory.csv --fail-on-finding

# Show all options, then run the local-only test suite
python node_cve_2026_56846_check.py --help
python -m unittest -v
There is no automatic scan of the current machine: you supply every version. --version is repeatable; each value describes a separate runtime.
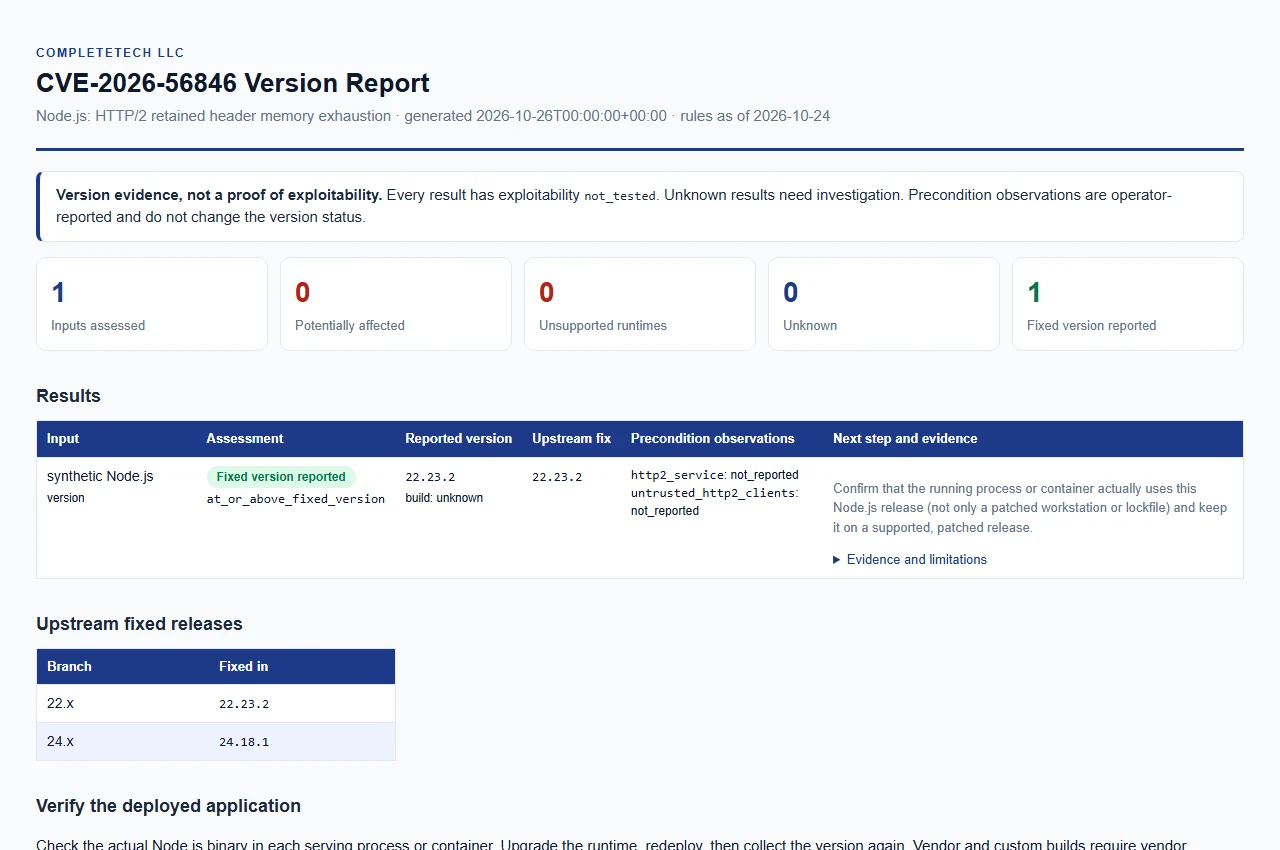
Open the synthetic example report. Example data only; this is not a live assessment.
Provide at least one input: --version, --inventory or --csv-list. Inputs can be combined in one run, and every input produces its own result row.
| Option | Purpose |
|---|---|
--version VERSION (alias --node-version) | Assess an explicitly supplied Node.js version offline. A leading v is accepted. Repeatable; each value is a separate runtime. |
--build-source SOURCE | Provenance of the --version builds, at most 512 characters. unknown (the default), upstream, official and official_upstream are compared as upstream releases (matched case-insensitively); any other value, such as a vendor name, yields unknown with vendor_build_unverified. |
--http2-service {true,false} | Operator observation applied to every --version input. |
--untrusted-http2-clients {true,false} | Operator observation applied to every --version input. |
--inventory FILE | JSON object or array of entries. Repeatable. |
--csv-list FILE | CSV list with a node_version column. Repeatable. |
--format {csv,json,html} | Report format. Default: csv. |
--output FILE | Save the report to a new file in an existing directory. Default: stdout. |
--force | Replace an existing output file. Inputs can never be overwritten, even with --force. |
--brand NAME | Organization name shown in the HTML report, at most 512 characters. Default: CompleteTech LLC. |
--fail-on-finding | Exit 1 when a result is potentially_affected or unsupported_runtime (see exit codes). |
--tool-version | Print the tool name and version. |
Existing reports are protected unless --force is explicit. --build-source, --brand and the two observation options are checked before any input is read.
An inventory file holds one object or an array of objects. Each record requires an integer schema_version of 1 and a string node_version. Optional fields are runtime (only "node" is accepted), label, build_source and the two observation keys, each a boolean or null. Unknown keys, duplicate keys, non-finite numbers and invalid types are rejected. See examples/inventory.example.json:
[
  {
    "schema_version": 1,
    "label": "example-service",
    "runtime": "node",
    "node_version": "22.23.2",
    "build_source": "unknown",
    "http2_service": null,
    "untrusted_http2_clients": null
  }
]
A CSV list needs a header row with a node_version column. Optional columns are label, build_source, http2_service and untrusted_http2_clients; observation cells hold exactly true, false or nothing. Duplicate or undocumented columns, rows with a different number of fields than the header, bare quotes in unquoted cells and NUL characters are rejected. Entries without a label are named after the file and row.
| Observation | Meaning |
|---|---|
http2_service | The operator reports an HTTP/2 service. |
untrusted_http2_clients | The operator reports untrusted HTTP/2 clients. |
