
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
DirtyFrag-Galaxy — One-click temporary KernelSU root (late-load) for Samsung Galaxy via DirtyFrag (CVE-2026-43284). No Shizuku/PC/ADB. | Kitploit
Tools/GitHubGitHub/coey0814/dirtyfrag-galaxy
Android SecurityPrivilege EscalationPersistence MechanismsExploitationMobile App PentestingPost-ExploitationMobile SecurityPayload Development
GitHubcoey0814/dirtyfrag-galaxy

DirtyFrag-Galaxy

One-click temporary KernelSU root (late-load) for Samsung Galaxy via DirtyFrag (CVE-2026-43284). No Shizuku/PC/ADB.

View Repository
532 days agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

DirtyFrag-Galaxy

한국어 · English

DirtyFrag Galaxy icon

One-click temporary KernelSU root (late-load) for Samsung Galaxy devices
via the DirtyFrag (CVE-2026-43284) exploit.
No Shizuku, no PC, no ADB — the app performs everything from the exploit to KernelSU late-load by itself.

Download latest APK

⚠️ WARNING

I am not responsible for bricked phones.

  • This tool uses a temporary (late-load) root and does not flash any partition, so it does not trip the KNOX warranty bit.
  • It works on DirtyFrag-vulnerable kernels. On a non-vulnerable or incompatible kernel it stops at the patch/primitive verification step and does not proceed to root acquisition.
  • Only run this on a device you own.
  • While root is active, some apps (banking / government / DRM) may detect root and refuse to run.
  • No warranty; use at your own risk.

Supported devices / kernels

The app selects a kernel module (KO) automatically based on the Android KMI family (androidNN) and the kernel major.minor shown by uname.

androidNN is not necessarily the same as the Android version number you see; it means the Android kernel / KMI family shown by uname -r.

Measured results so far:

DeviceModelKernelResult
Galaxy Z Fold8 UltraSM-F976N (q8q)6.12.58-android16✅ works (baseline)
Galaxy S25SM-S931N (pa1q)6.6.98-android15✅ works
Galaxy S24+SM-S926N (e2s)6.1.157-android14❌ CBC primitive NO-OP
  • What matters is not a plain major.minor, but whether the kernel primitive DirtyFrag needs actually exists and works.
  • So far it worked on 6.6.98-android15 and 6.12.58-android16; on 6.1.157-android14 the CBC primitive was a NO-OP and it did not work.
  • The kernel version number alone does not guarantee vulnerability. Vendor patches, backports, kernel tree differences and the exploit environment can change the result.
  • Upstream Linux CVE data has its own fix criteria, so we do not generalize as "6.1 = patched" or "6.6 = vulnerable".
  • On verified devices, we confirmed 50+ consecutive successful rooting attempts.

Bundled KOs

android12-5.10
android13-5.10
android13-5.15
android14-5.15
android14-6.1
android15-6.6
android16-6.12
android17-6.18

A KO for each KMI above is bundled. This does not guarantee operation on every target device/firmware.


Requirements

  • A Samsung Galaxy device whose kernel has the DirtyFrag primitive.
  • The KernelSU manager app — not bundled, install separately (tested v3.3.0).
  • (Recommended for modules) Zygisk-Next (tested v1.5.0) · LSPosed (tested LSPosed-it v2.2.0 / build 7854).
  • This app does not flash/modify any partition, so root is lost on reboot (enable auto-root to re-apply).

Usage

  1. Install the KernelSU manager app (separate).
  2. Install this app's APK from Releases.
  3. Open the app and tap 루팅 (ROOT). (exploit → temporary root → KernelSU late-load)
  4. When the root request appears, enable ROOT for this app (DirtyFrag Galaxy) in KernelSU manager > Superuser.

First run (no modules yet) — order matters

Modules can only be installed after root is acquired. Follow the order below.

  1. After step 4 the app auto-checks modules and, if missing, shows a "Module installation required" notification (+ an "Open manager" button). In KernelSU manager → Modules, install Zygisk-Next and LSPosed (zip).

  2. Return to the app — it is auto-detected (no need to press ROOT again). Once modules are ready, a "Soft restart required (for LSPosed to work)" notification appears.

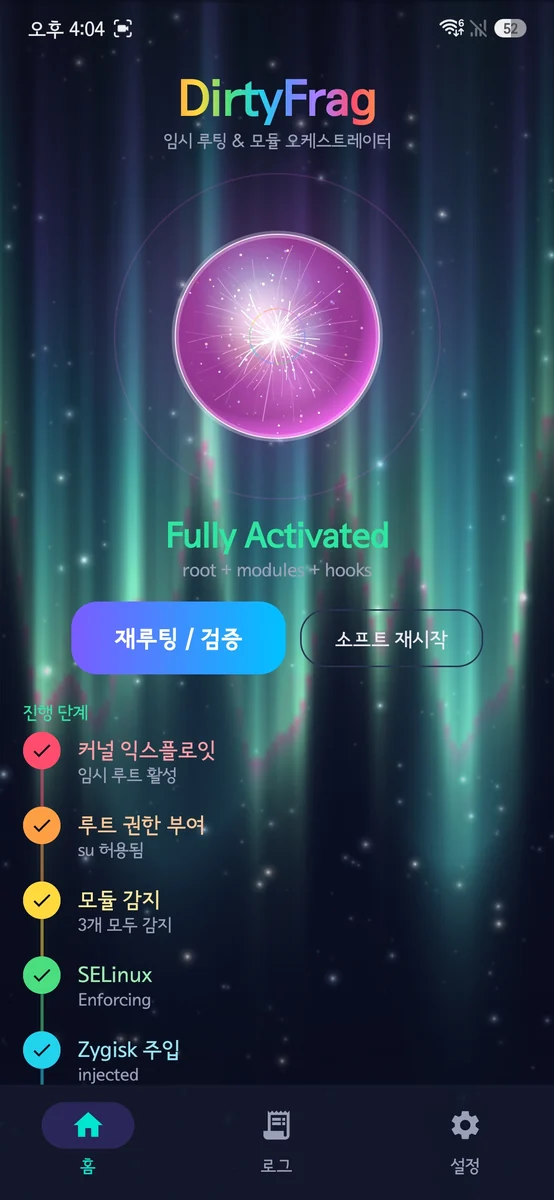
  3. Tap [Soft restart now] in the notification, or press 소프트 재시작 (SOFT RESTART) in the app. When done, the state becomes Fully Activated.

  4. Optionally enable Auto-root on boot to re-apply root automatically after each reboot.

Summary: root → install modules (notification-guided) → auto-detect → soft restart (notification / one tap). Rooting still completes even without modules; instead of a hard failure the app provides notifications, guidance, and a one-tap action.

Highlights

  • No Shizuku / PC / ADB — no pairing or external tools; the app performs everything from the exploit to KernelSU late-load.
  • 100% root success — on verified devices, 50+ consecutive attempts all succeeded.
  • Stable soft restart — once root is granted to this app in the manager, module staging + soft reboot run cleanly from a su context.
  • 7-state live verification + health panel — exploit / grant / modules / SELinux / Zygisk / LSPosed / restart.
  • Accurate LSPosed detection — based on the current system_server pid (logcat + lspd verbose, mtime-guarded), eliminating false positives/negatives.
  • Multi-KO auto-select — picks the KO matching the KMI and kernel version.
  • Optional permissive + no-reboot Enforcing restore — devices that do not need permissive just work; on devices that do (6.12) SELinux is switched back to Enforcing without a reboot after root + Zygisk + LSPosed are confirmed.
  • Auto-root on boot — foreground service + notifications.
  • First-run module guidance (notification) — rooting completes even with no modules; the app guides you with a "Module installation required" notification + "Open manager" button.
  • Auto-detect + soft-restart notification — returning from the manager auto-refreshes detection, and once root + modules are ready a "Soft restart required" notification (one-tap [Soft restart now]) appears.
  • Log tab / aurora visuals — detailed logs and status snapshots.

Auto-root on boot

Enable Auto-root on boot. After a reboot a foreground service runs exploit → su → module stage automatically and shows progress notifications.

Auto soft restart defaults to OFF (to avoid loops). When LSPosed activation is needed, run a soft restart once in the app.


Notes and limitations

  • On currently verified devices, 50+ consecutive rooting attempts all succeeded.
  • Results are not guaranteed on unverified devices or other firmware.
  • On a non-vulnerable or incompatible kernel, it stops with patch/primitive verification messages such as CBC page-cache primitive is a NO-OP ... Aborting..
  • The stage runs once only. ksud unload is never used (it hard-locks the device).

Demo videos

First-run rootingSoft restart

Animated WebP — plays automatically. (Click to view full size.)


Screenshots

Download Tool