 cappricio-securities/cve-2019-9670
mailboxd component in Synacor Zimbra Collaboration Suite 8.7.x before 8.7.11p10 has an XML External Entity injection (XXE) vulnerability, as demonstrated by Autodiscover/Autodiscover.xml.




Install Python3 and pip Instructions Here (If you can't figure this out, you shouldn't really be using this)
pip install CVE-2019-9670
CVE-2019-9670 -hWe integrated with the Telegram API to receive instant notifications for vulnerability detection.
CVE-2019-9670 --chatid <YourTelegramChatID>
@CappricioSecuritiesTools_bot and click startThis tool has multiple use cases.
CVE-2019-9670 -u http://example.com
CVE-2019-9670 -i urls.txt
CVE-2019-9670 -i urls.txt -o out.txt
CVE-2019-9670? Then Type Below command
CVE-2019-9670 -b
🚨 Disclaimer
This tool is created for security bug identification and assistance; Cappricio Securities is not liable for any illegal use. Use responsibly within legal and ethical boundaries. 🔐🛡️
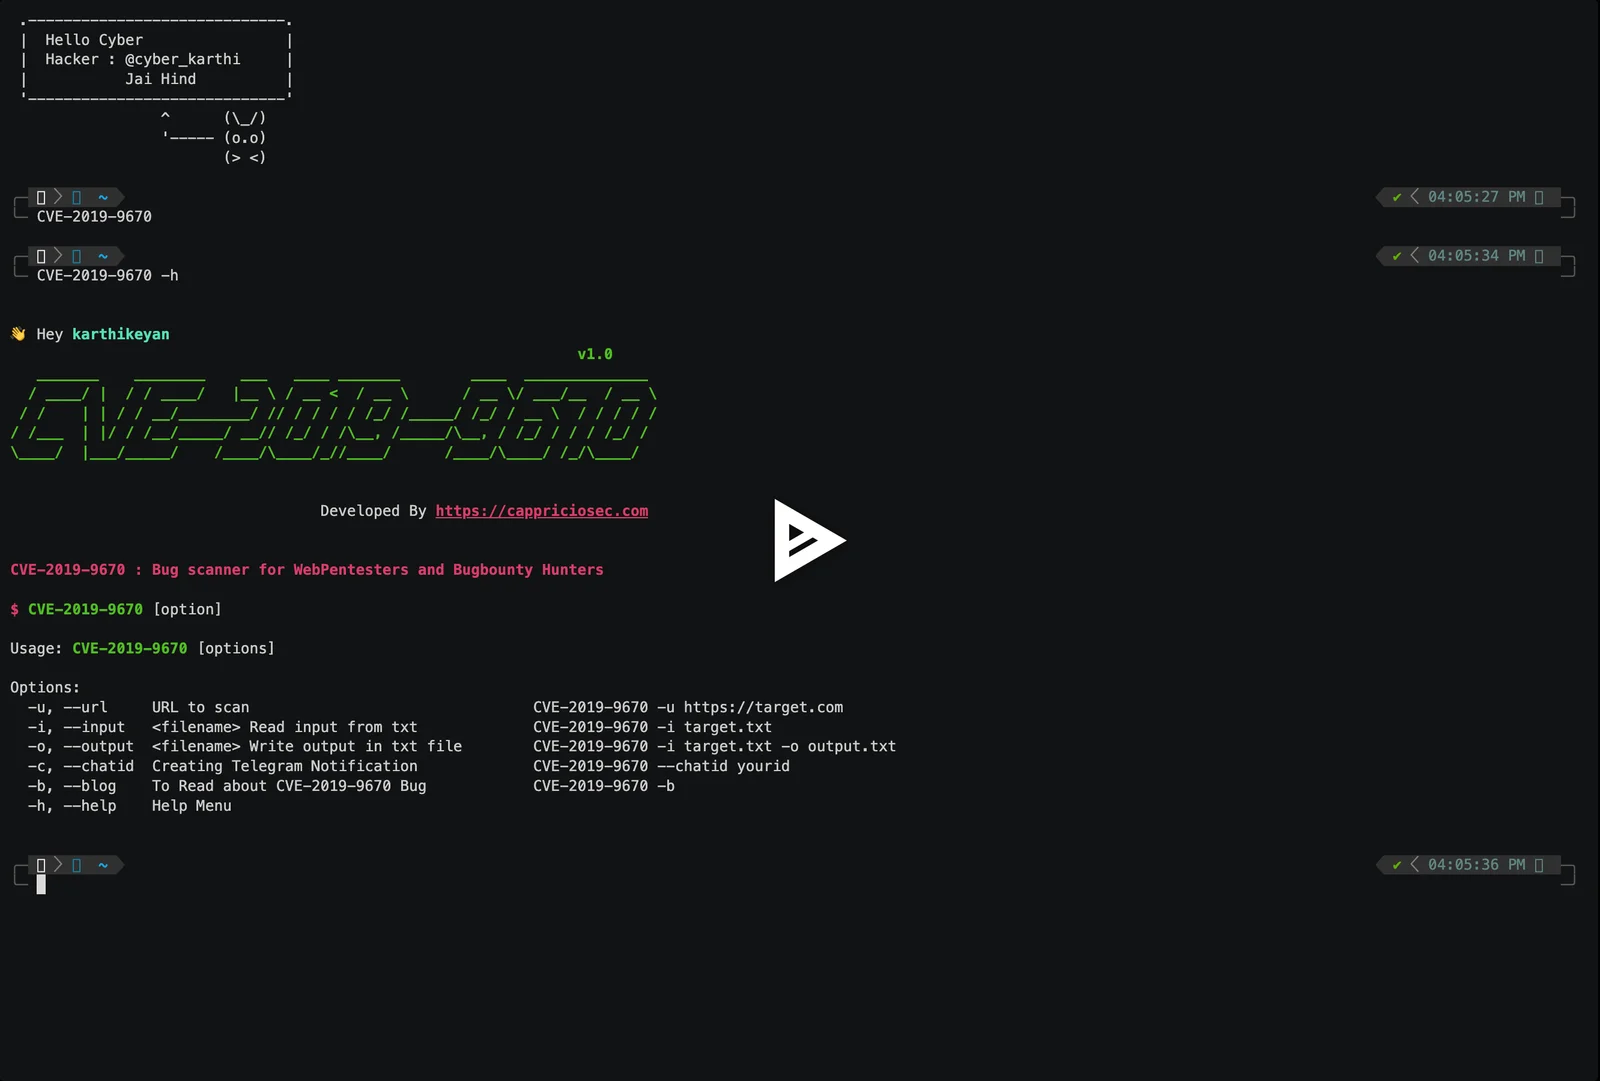
👋 Hey Hacker
                                                                v1.0
   _______    ________    ___   ____ _______        ____  ______________
  / ____/ |  / / ____/   |__ \ / __ <  / __ \      / __ \/ ___/__  / __ \\
 / /    | | / / __/________/ // / / / / /_/ /_____/ /_/ / __ \  / / / / /
/ /___  | |/ / /__/_____/ __// /_/ / /\__, /_____/\__, / /_/ / / / /_/ /
\____/  |___/_____/    /____/\____/_//____/      /____/\____/ /_/\____/

                                   Developed By https://cappriciosec.com


CVE-2019-9670 : Bug scanner for WebPentesters and Bugbounty Hunters

$ CVE-2019-9670 [option]

Usage: CVE-2019-9670 [options]
| Argument | Type | Description | Examples |
|---|---|---|---|
-u | --url | URL to scan | CVE-2019-9670 -u https://target.com |
-i | --input | filename Read input from txt | CVE-2019-9670 -i target.txt |
-o | --output | filename Write output in txt file | CVE-2019-9670 -i target.txt -o output.txt |
-c | --chatid | Creating Telegram Notification | CVE-2019-9670 --chatid yourid |
-b | --blog | To Read about CVE-2019-9670 Bug | CVE-2019-9670 -b |
-h | --help | Help Menu | CVE-2019-9670 -h |

If you have any feedback, please reach out to us at [email protected]