 buybitart/cloudflare-security-art
Cloudflare Free Plan security rules (Zero Trust approach) for small websites

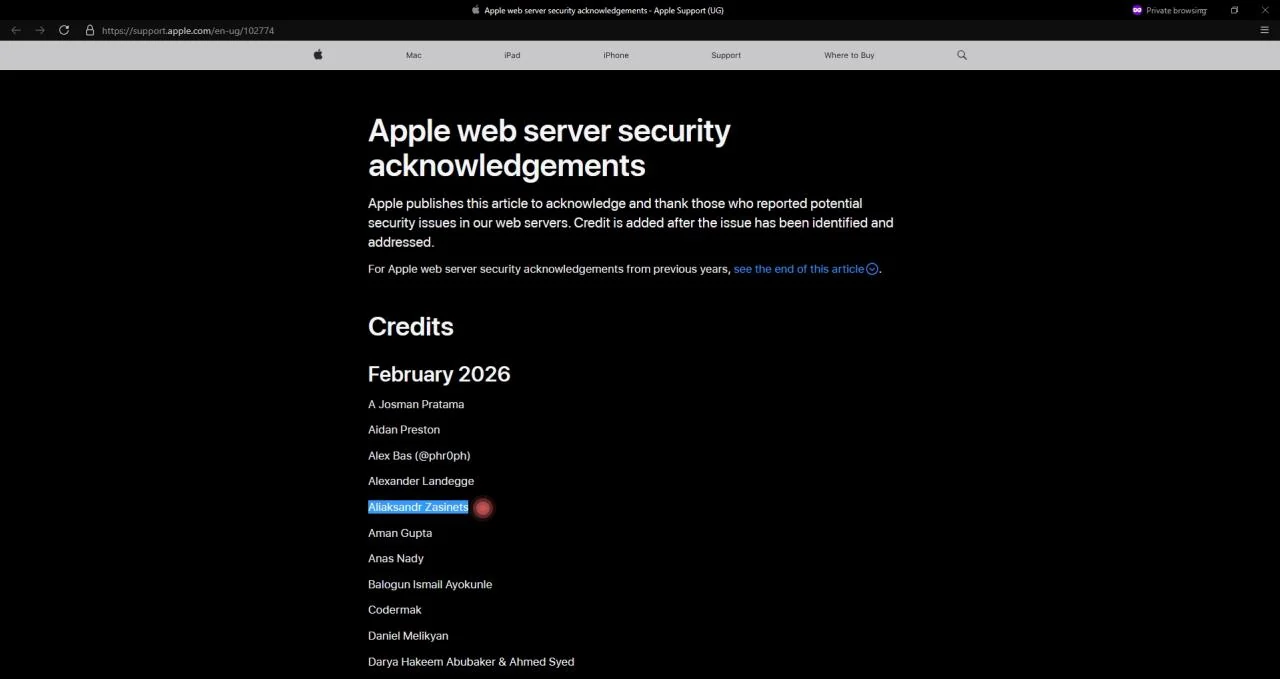
I’m Aksana (5Ksana), founder of the open-source BitcoinArt project. My husband, Aliaksandr (ALEX) Zasinets, helps with security, testing, and open-source tools. Aliaksandr is a QA Automation Engineer, Penetration Tester, and open-source security researcher. He works on website security, Cloudflare protection, WAF rules, DDoS protection, security headers, bot protection, and protection from bad scanners. Apple thanked Aliaksandr for finding and reporting security problems in web servers.
He is listed in Apple Security Acknowledgements:
https://support.apple.com/en-ug/102774
This repository, cloudflare-security-art, is a free security guide for small websites, artists, creators, and self-hosted projects using Cloudflare. If this project helps you protect your website, please support our open-source work through GitHub Sponsors:
https://github.com/sponsors/buybitart
Your support helps us test Cloudflare security rules, update this guide, write simple examples, and keep this project free. If this repo helped you, please also give it a star ⭐. It helps the project grow. Thank you! ❤️
This guide will help you protect your website using Cloudflare. It includes firewall rules, DDoS protection, security headers, and bot settings.
It includes:
My Cloudflare rule is:
AI bots try to copy your content!. See How AI is stealing your art and ‘Mass theft’: Thousands of artists call for AI art auction to be cancelled
"One of the main points of art is to dialogue with culture.
Even if unintentional, every piece of art reflects the unique background of its creator-shaped by food, religion, music, ethics, visual art, and more.Imagine a child raised in isolation, shown only paintings 16 hours a day, and punished if their weekly drawing doesn't replicate those images closely enough. They don’t know why they draw-they just mimic. They aren’t creating. They aren’t dialoguing with art.
A computer is even simpler. It doesn't feel, doesn't reflect, doesn't remember the sound of jazz in the 1920s or the first time it saw Warhol.
But a human artist does.
They carry experience, emotion, and intention. They borrow from the past, mix it with the present, and speak in their own voice. That’s art. That’s the difference.When art is just imitation for profit, it’s empty. But when it speaks-it matters."
AI pretend to be search engines, but they don't bring you visitors.
Some even use fake user agents, so basic Cloudflare settings may not stop them.
This rule blocks all bots by default, and then only allows useful bots that help your website get indexed.
| Step | Description |
|---|---|
| STEP 1 – Web Application Firewall (WAF) Rules | Blocks bots, crawlers, exploits and malicious requests (Parts 1‑5). |
| STEP 2 – DDoS L7 Protection & Rate Limiting | Adds Layer‑7 override and rate limits to stop floods. |
| STEP 3 – Bot Management | Configures Cloudflare bot settings to block AI and unwanted bots. |
| STEP 4 – Security Headers | Sets recommended HTTP headers to harden the site. |
[!IMPORTANT]
It is also recommended to disable theBot Fight Modefeature in theSecuritytab.
This guide already blocks all unwanted bots and AI crawlers while allowing only the important and trusted bots used for indexing your site such as:
- bing
- slurp
- duckduckbot
- cloudflare
Because of this, there is no need to enable Bot Fight Mode as it could interfere with these allowed bots and disrupt proper indexing.
Copy these expressions into your Cloudflare dashboard for custom WAF rules.
Read Create a custom rule in the dashboard.
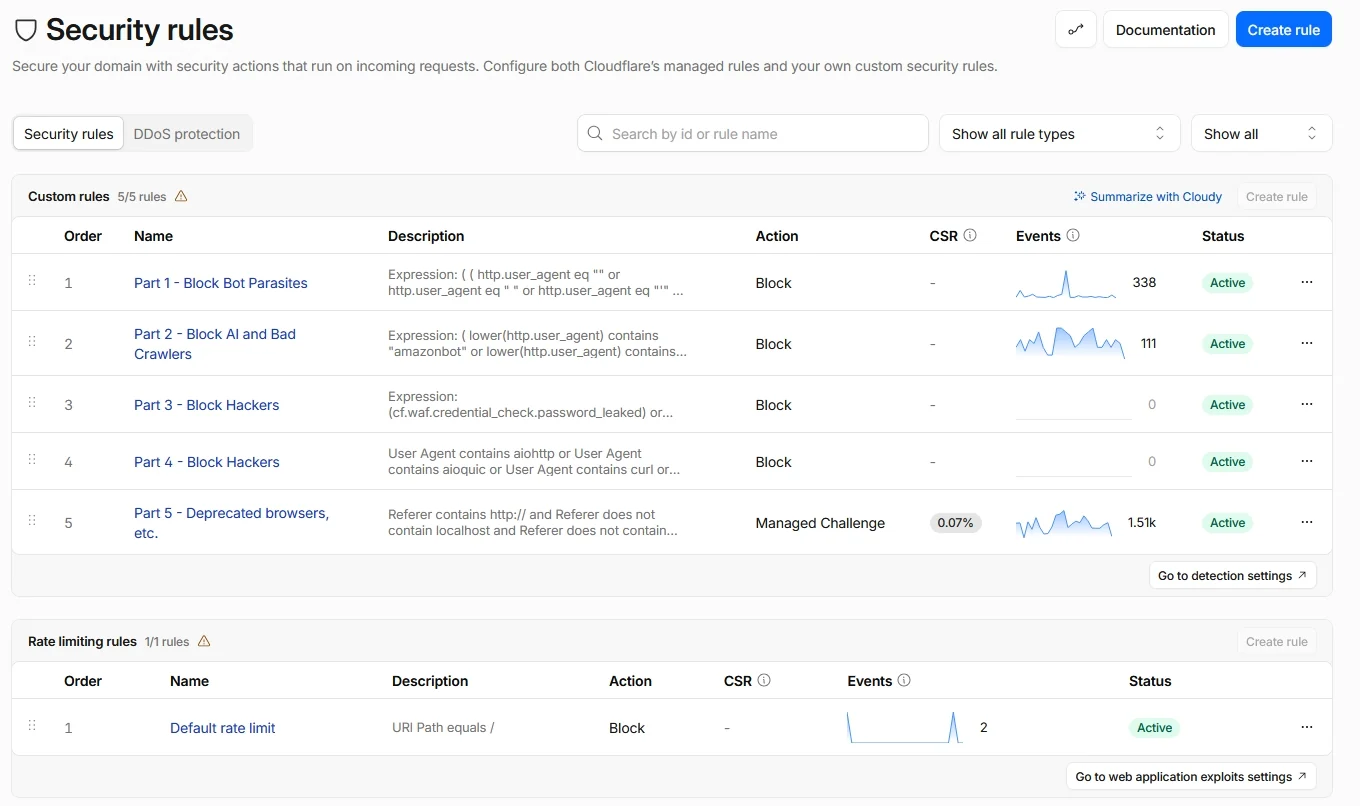
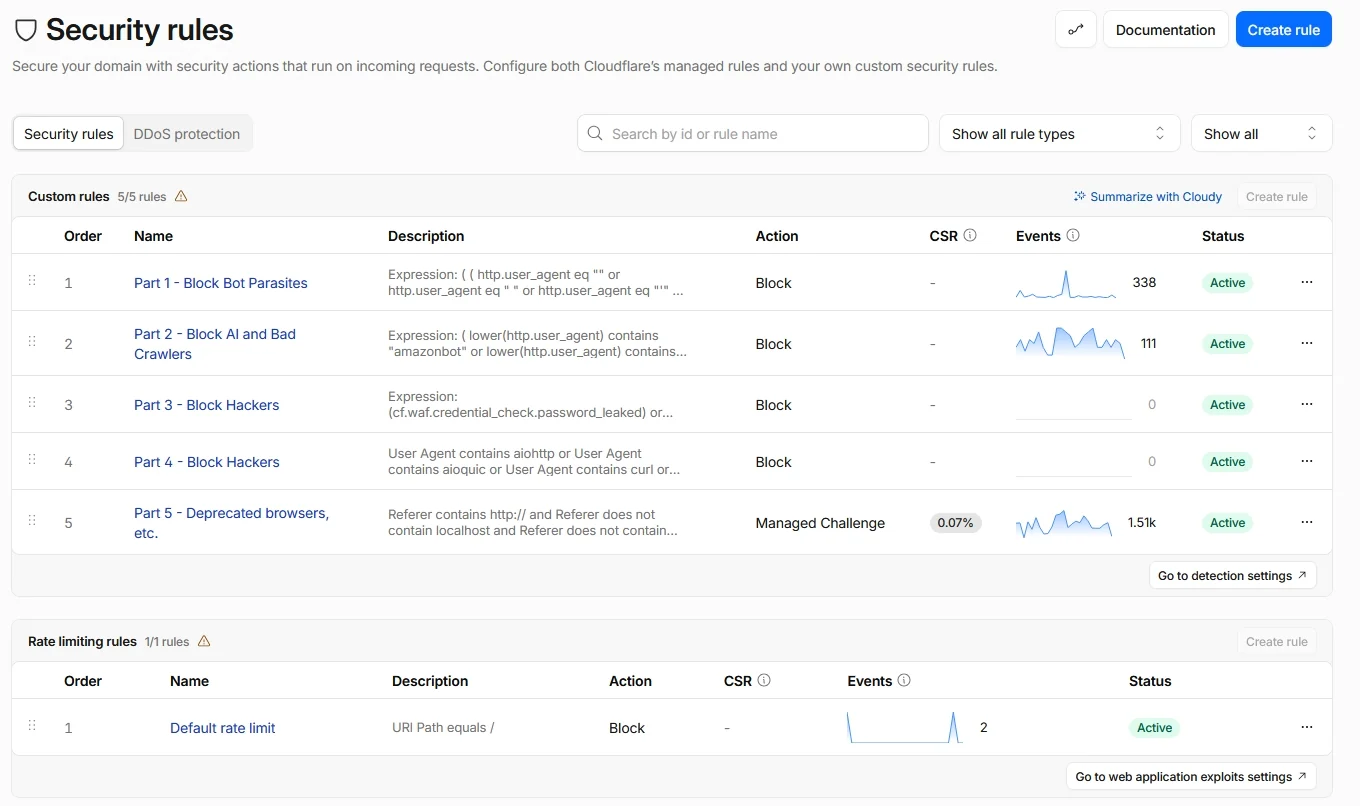
This rule stops bad automated web traffic by checking each request and blocking empty or strange User‑Agent names like headless browsers or scanners and traffic from certain IP groups that use "siteaudit" and Host headers that have ":80" or ":443" and wrong Cloudflare cookies and any Cloudflare client.bot that is not a verified search crawler or an ACME challenge and any HTTP/1.0 or HTTP/1.1 request unless it asks for "/robots.txt" or comes from a real search bot or an ACME check.
NOTE🔒 This rule stops about 90% of all threats. It cuts off bad bot traffic before it reaches the application.
Action: Block
(
  (
  http.user_agent eq ""
  or http.user_agent eq " "
  or http.user_agent eq "'"
  or http.request.headers["user-agent"][0] eq ""
  or lower(http.user_agent) contains "puppeteer"
  or lower(http.user_agent) contains "phantomjs"
  or lower(http.user_agent) contains "selenium"
  or lower(http.user_agent) contains "slimerjs"
  or lower(http.user_agent) contains "nightmare"
  or lower(http.user_agent) contains "casperjs"
  or lower(http.user_agent) contains "pyppeteer"
  )
  or (ip.src.asnum in {135061 23724 4808} and http.user_agent contains "siteaudit")
  or (http.host contains ":80")
  or (http.host contains ":443")
  or (
    http.cookie contains "cf_use_ob="
    and not http.cookie contains "0"
    and not http.cookie contains "80"
    and not http.cookie contains "443"
    and not cf.client.bot
  )
  or (
    cf.client.bot
    and not (
      (
        cf.verified_bot_category in {"Search Engine Crawler"}
        and (
          lower(http.user_agent) contains "google"
          or lower(http.user_agent) contains "bing"
          or lower(http.user_agent) contains "slurp"
          or lower(http.user_agent) contains "duckduckbot"
          or lower(http.user_agent) contains "cloudflare"
