Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
checkov — Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes, CloudFormation, and container images during build-time. | Kitploit
Tools/GitHubGitHub/bridgecrewio/checkov
Cloud Infrastructure SecurityStatic AnalysisVulnerability ScannersContainer SecurityStatic Code Analysis (SAST)Vulnerability AnalysisCode AnalysisServerless SecurityConfiguration AuditingCloud SecurityDevSecOps
8.9k1.4k921 day agoReviewed by Kitploit
Secret Detection
Supply Chain Security
Misconfiguration
Database Security
Top in Cloud Infrastructure Security #4
Top in Cloud Security #4
Top in Code Analysis #18
Top in Configuration Auditing #5
Top in Database Security #13
Top in DevSecOps #5
Top in Misconfiguration #5
Top in Secret Detection #16
Top in Serverless Security #6
Top in Static Code Analysis (SAST) #15
Top in Vulnerability Analysis #17
Top in Vulnerability Scanners #17
GitHubbridgecrewio/checkov

checkov

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes, CloudFormation, and container images during build-time.
View RepositoryWebsite

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

checkov

Maintained by Prisma Cloud build status security status code_coverage docs PyPI Python Version Terraform Version Downloads Docker Pulls slack-community

Checkov is a static code analysis tool for infrastructure as code (IaC) and also a software composition analysis (SCA) tool for images and open source packages.

It scans cloud infrastructure provisioned using Terraform, Terraform plan, Cloudformation, AWS SAM, Kubernetes, Helm charts, Kustomize, Dockerfile, Serverless, Bicep, OpenAPI, ARM Templates, or OpenTofu and detects security and compliance misconfigurations using graph-based scanning.

It performs Software Composition Analysis (SCA) scanning which is a scan of open source packages and images for Common Vulnerabilities and Exposures (CVEs).

Checkov also powers Prisma Cloud Application Security, the developer-first platform that codifies and streamlines cloud security throughout the development lifecycle. Prisma Cloud identifies, fixes, and prevents misconfigurations in cloud resources and infrastructure-as-code files.
Table of contents

  • Features
  • Screenshots
  • Getting Started
  • Disclaimer
  • Support
  • Migration - v2 to v3

Features

  • Over 1000 built-in policies cover security and compliance best practices for AWS, Azure and Google Cloud.
  • Scans Terraform, Terraform Plan, Terraform JSON, CloudFormation, AWS SAM, Kubernetes, Helm, Kustomize, Dockerfile, Serverless framework, Ansible, Bicep, ARM, and OpenTofu template files.
  • Scans Argo Workflows, Azure Pipelines, BitBucket Pipelines, Circle CI Pipelines, GitHub Actions and GitLab CI workflow files
  • Supports Context-awareness policies based on in-memory graph-based scanning.
  • Supports Python format for attribute policies and YAML format for both attribute and composite policies.
  • Detects AWS credentials in EC2 Userdata, Lambda environment variables and Terraform providers.
  • Identifies secrets using regular expressions, keywords, and entropy based detection.
  • Evaluates Terraform Provider settings to regulate the creation, management, and updates of IaaS, PaaS or SaaS managed through Terraform.
  • Policies support evaluation of variables to their optional default value.
  • Supports in-line suppression of accepted risks or false-positives to reduce recurring scan failures. Also supports global skip from using CLI.
  • Output currently available as CLI, CycloneDX, JSON, JUnit XML, CSV, SARIF and github markdown and link to remediation guides.

Screenshots

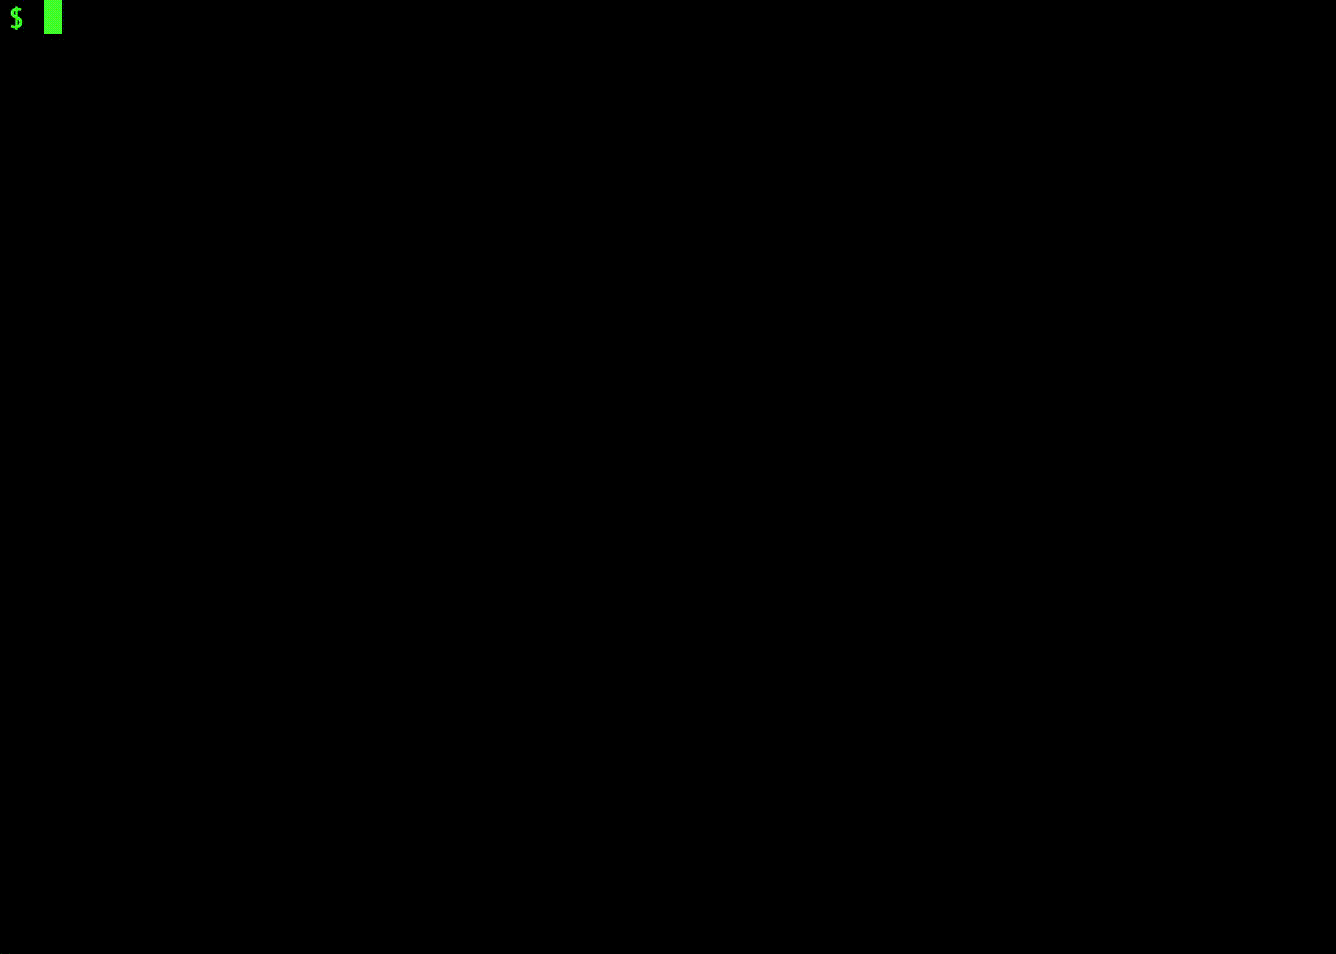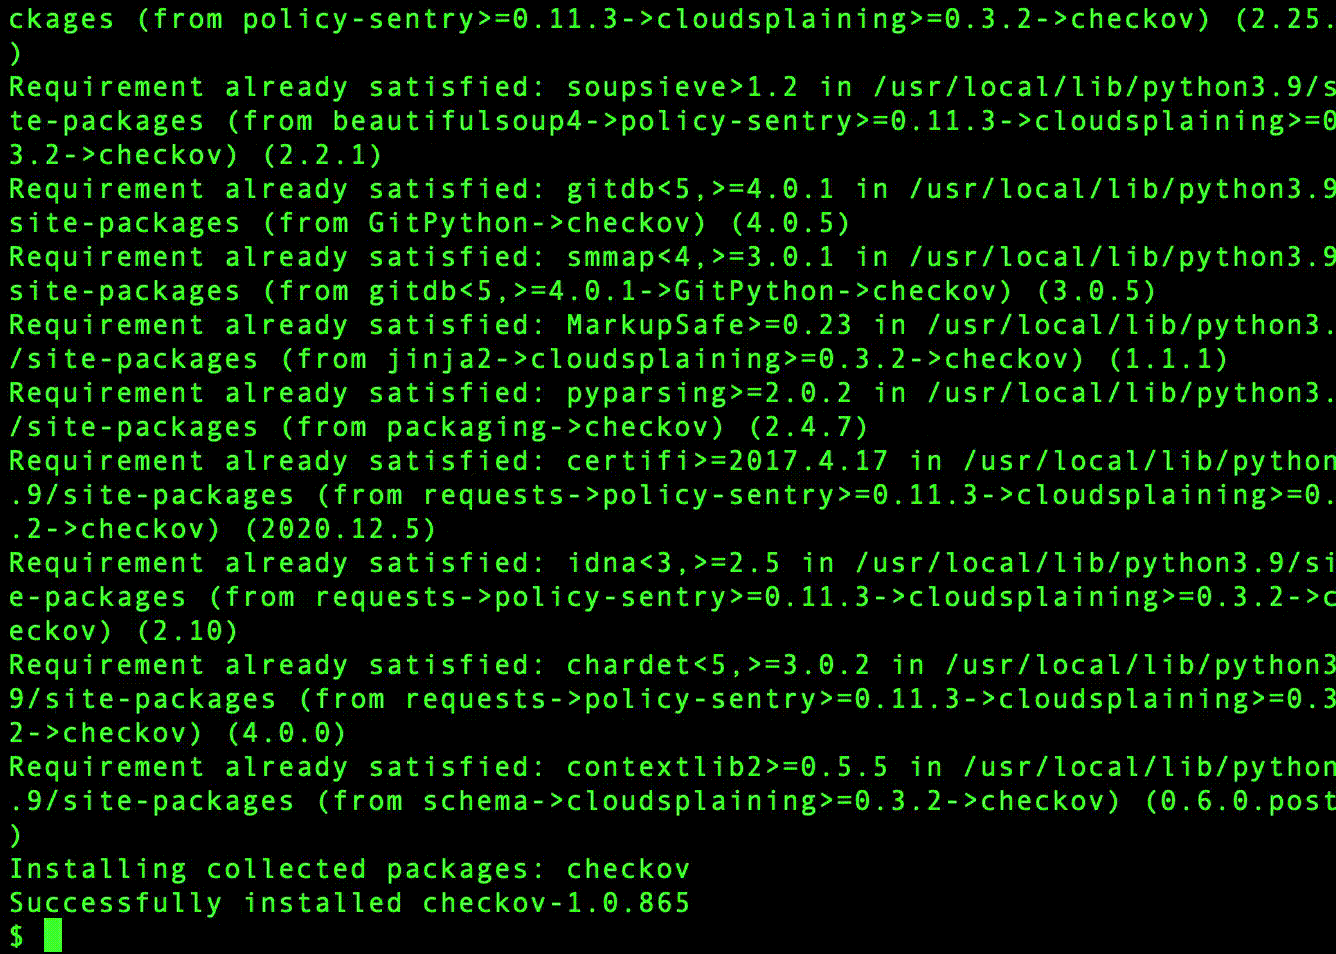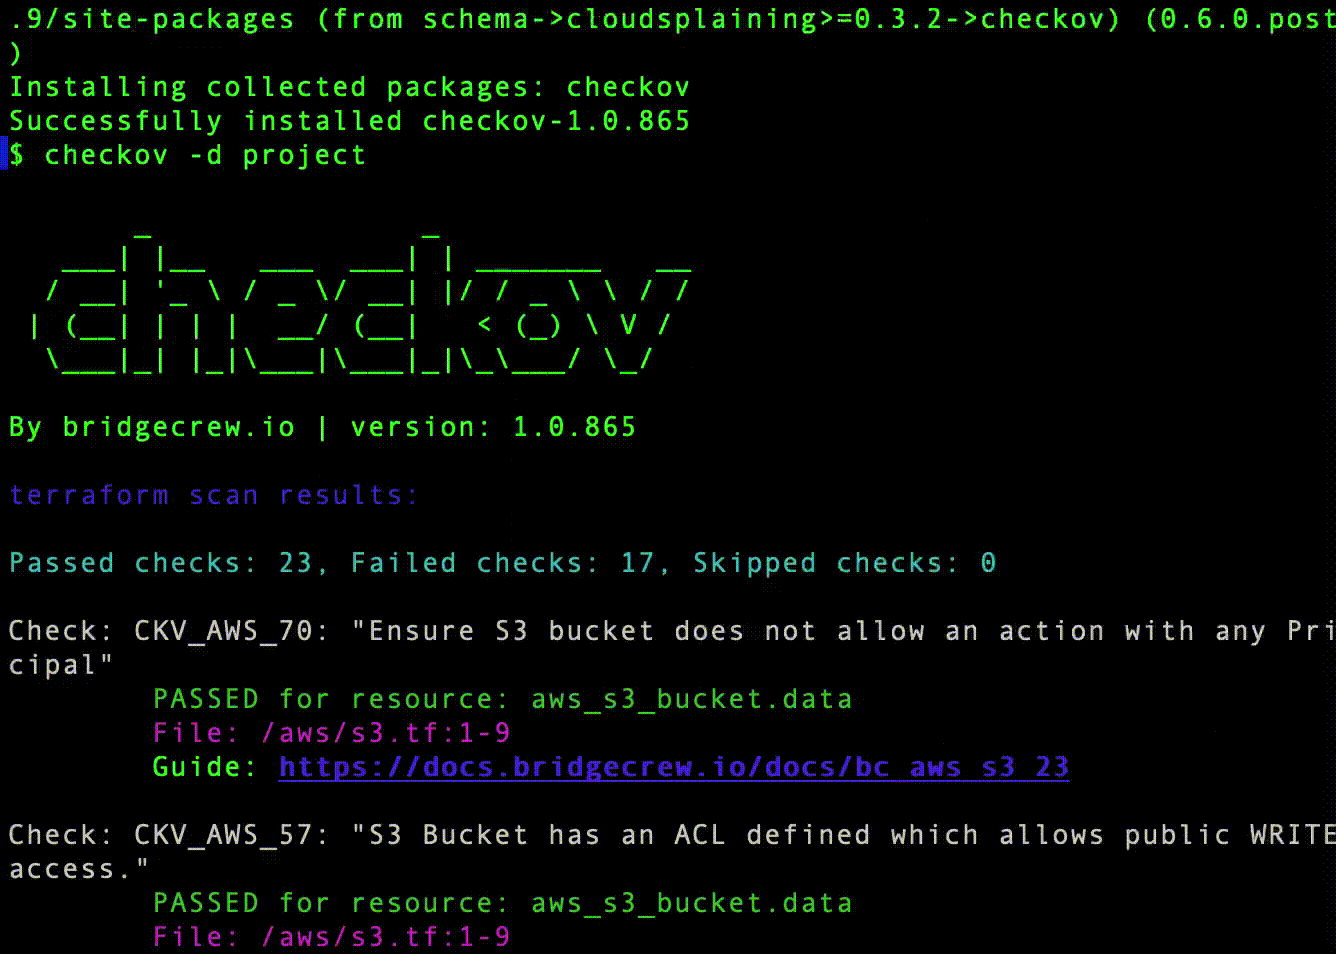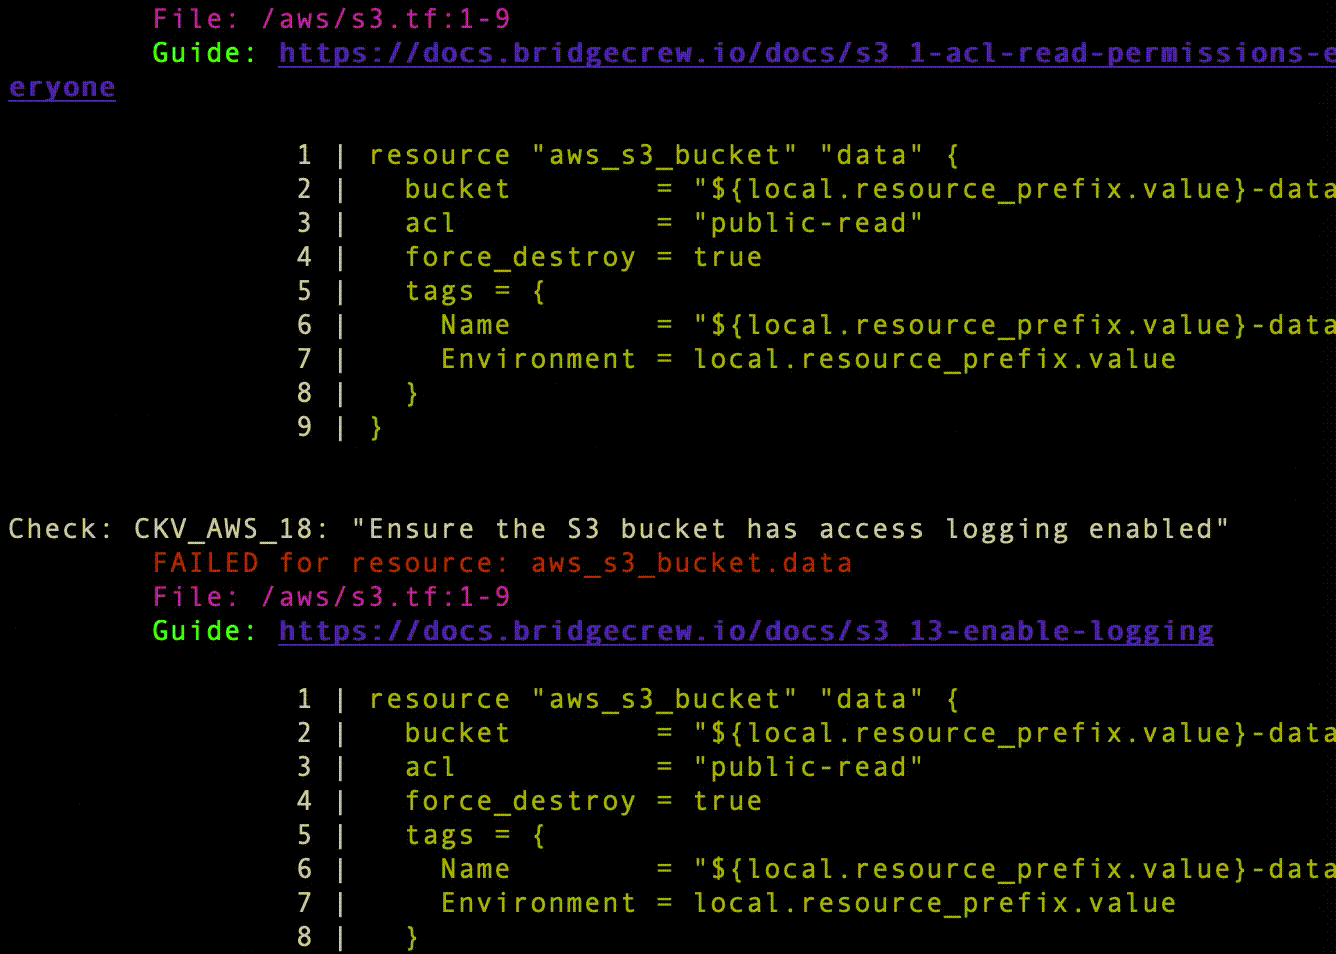
Scan results in CLI

scan-screenshot

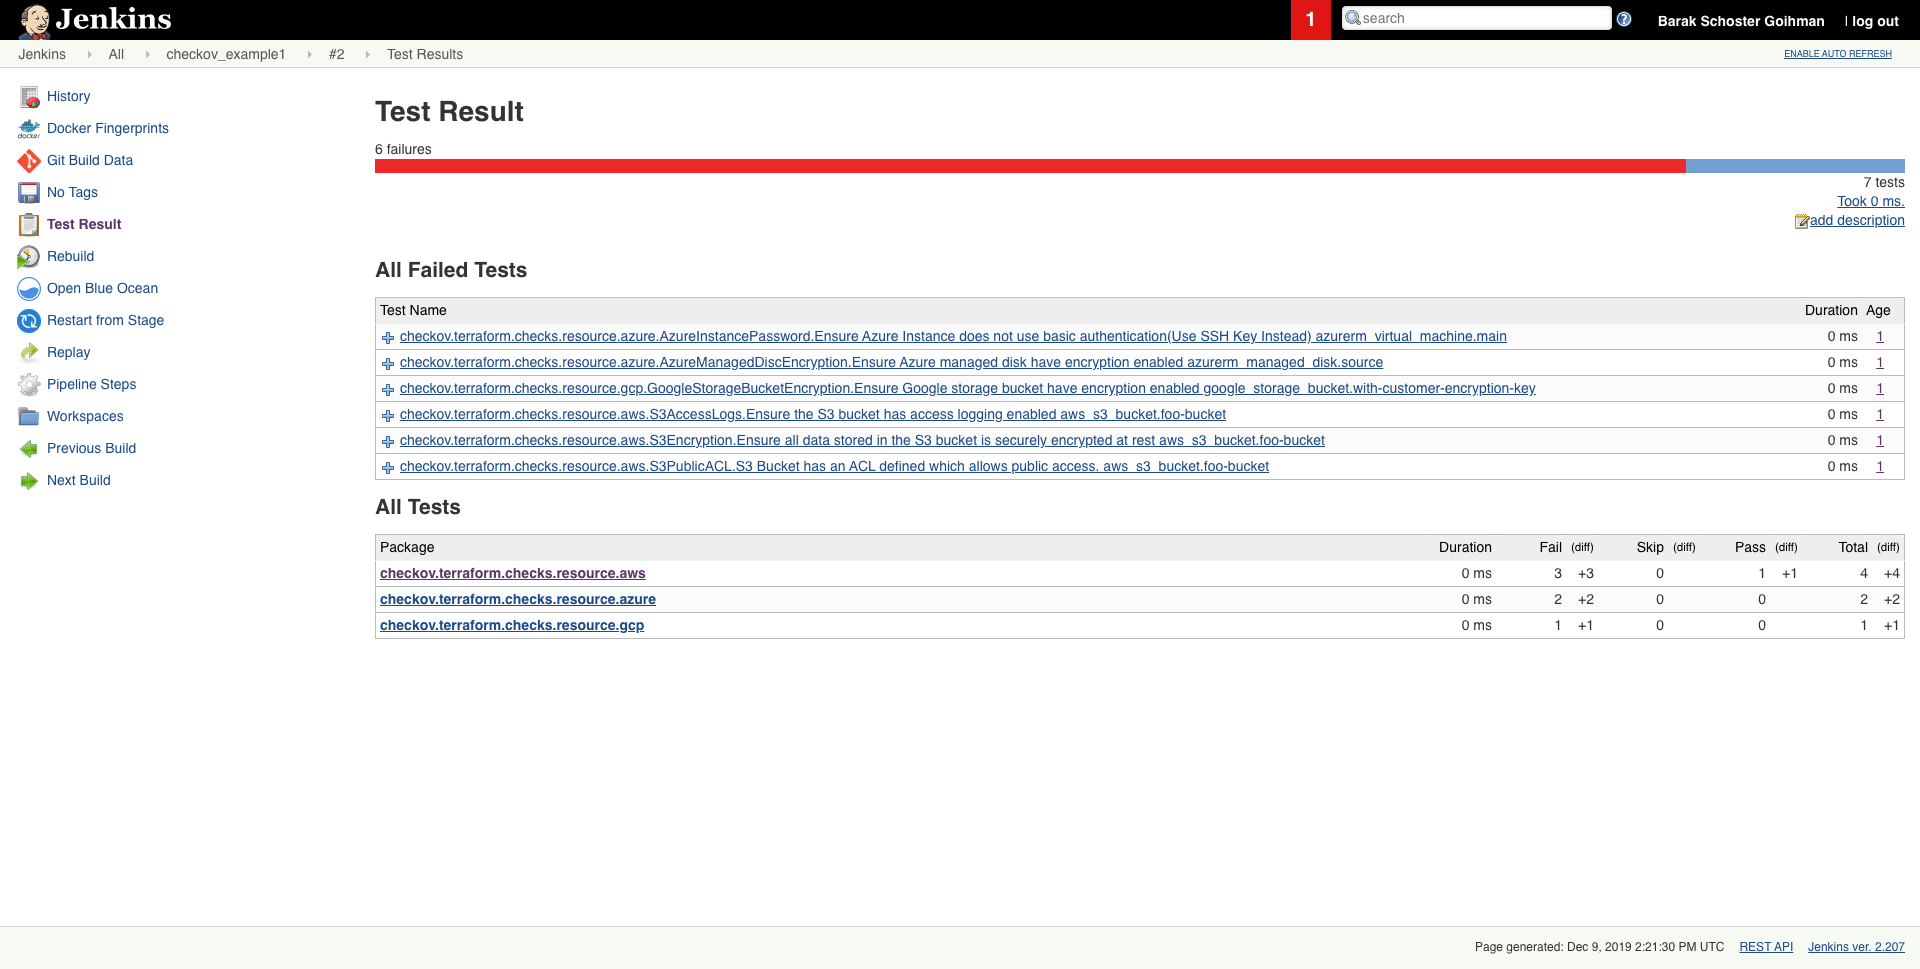
Scheduled scan result in Jenkins

jenikins-screenshot

Getting started

Requirements

  • Python >= 3.9, <=3.12
  • Terraform >= 0.12

Installation

To install pip follow the official docs

pip3 install checkov

Certain environments (e.g., Debian 12) may require you to install Checkov in a virtual environment

# Create and activate a virtual environment
python3 -m venv /path/to/venv/checkov
cd /path/to/venv/checkov
source ./bin/activate

# Install Checkov with pip
pip install checkov

# Optional: Create a symlink for easy access
sudo ln -s /path/to/venv/checkov/bin/checkov /usr/local/bin/checkov

or with Homebrew (macOS or Linux)

brew install checkov

Enabling bash autocomplete

source <(register-python-argcomplete checkov)

Upgrade

if you installed checkov with pip3

pip3 install -U checkov
Download Tool