
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
teamcity-CVE-2026-63077-pcap — teamcity teamcity-CVE-2026-63077 exploitation pcap | Kitploit
Tools/GitHubGitHub/boredhackerblog/teamcity-cve-2026-63077-pcap
Packet Sniffing & AnalysisVulnerability AnalysisExploitationNetwork SecurityIntrusion Detection
GitHubboredhackerblog/teamcity-cve-2026-63077-pcap

teamcity-CVE-2026-63077-pcap

teamcity teamcity-CVE-2026-63077 exploitation pcap

View Repository
61 month agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

teamcity-CVE-2026-63077-pcap

teamcity teamcity-CVE-2026-63077 exploitation pcap

info: https://blog.jetbrains.com/teamcity/2026/07/cve-2026-63077/

https://www.rapid7.com/blog/post/ra-unauthenticated-rce-in-jetbrains-teamcity-cve-2026-63077/

Target: teamcity server 2025.11.3 (docker) 192.168.64.31 port 8111

Exploit: https://github.com/sfewer-r7/CVE-2026-63077 - ran from 192.168.64.32 w/ command to curl webhook.site

pcap might be useful for testing suricata rules.
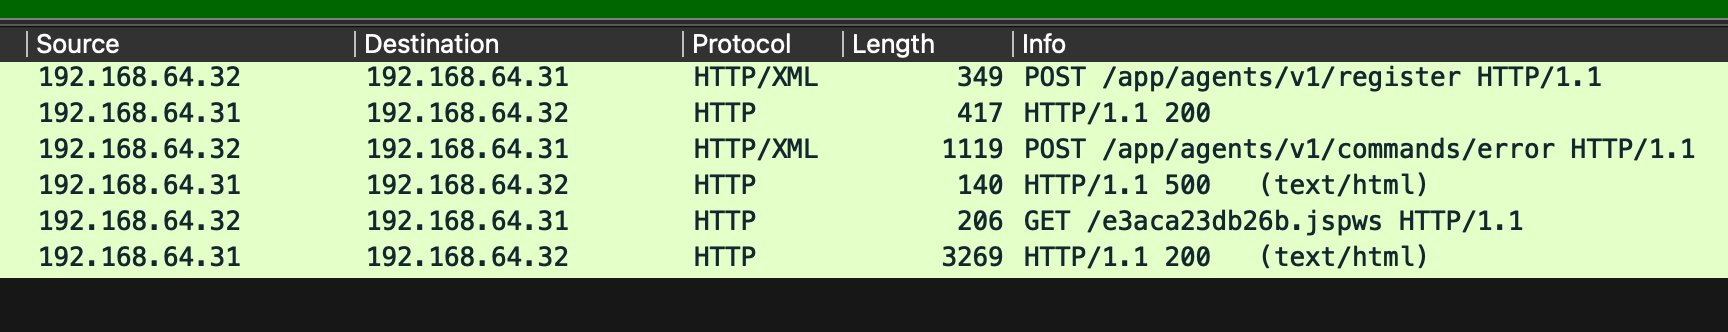
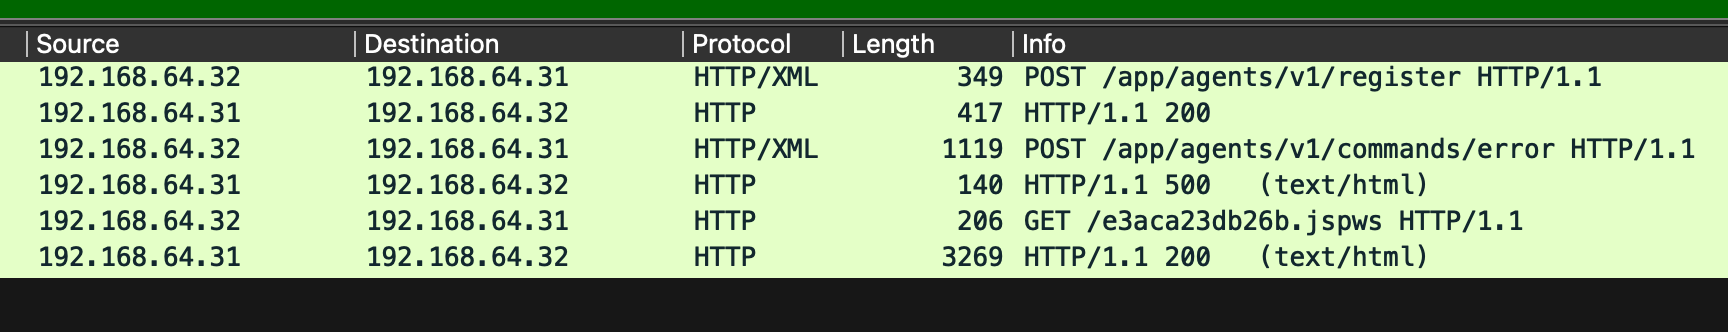
wireshark screenshot

from_honeypot* files - tar has java samples that were dropped. pcap has traffic associated with the exploitation. obviously, the files are from honeypot/real attacks.

Download Tool