 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a compromised host.

Blue Pigeon: Bluetooth-based Data Exfiltration and Proxy Tool for Red Teamers
The Components | Dissecting the Pidgey apart
1. Blue Pigeon - The Mobile Applicaton
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a compromised host.
Inspired by the Rock Dove's ability to carry messages back to its home, Blue Pigeon mimics the homing behaviour and delivers messages/payloads between the agent (compromised host) and its nest (mobile application and subsequently proxied to C2 server).
Blue Pigeon is developed as an Android application for the Red Teamer to deploy within vicinity of the compromised host and is particularly useful for Red Team operations where communications over traditional channels (i.e., web, e-mail, DNS) are not available.
Expanding on the “Exfiltration over Alternative Protocol” technique (ID: T1048) under the Exfiltration tactic of the MITRE AT&CK framework, Blue Pigeon provides a novel way of establishing Command and Control and performing data exfiltration as an Action on Objective of the Cyber Kill Chain by utilizing Bluetooth File Sharing as the exfiltration medium.
Blue Pigeon is created by @mahchiahui, @jingloon and @cloudkanghao
(Source: https://spectrum.ieee.org/tech-history/silicon-revolution/consider-the-pigeon-a-surprisingly-capable-technology)
Establishing Command and Control and performing data exfiltration are key phases in the Cyber Kill Chain, but they often come with their complications and severe implications if done wrongly. In a Red Team operation, a misfired attempt could leave permanent traces in the network activity logs and raise alarm to the detection mechanisms.
In some of our Red Teaming exercises, we found ourselves in need of a way to exfiltrate data and communicate with the compromised host without having to go through the traditional channels (i.e., web, email, DNS).
With few solutions available to address this need we explored various exfiltration ideas based on wireless/radio-comms vectors. As a result, Blue Pigeon was created to expand our Red Team toolset.
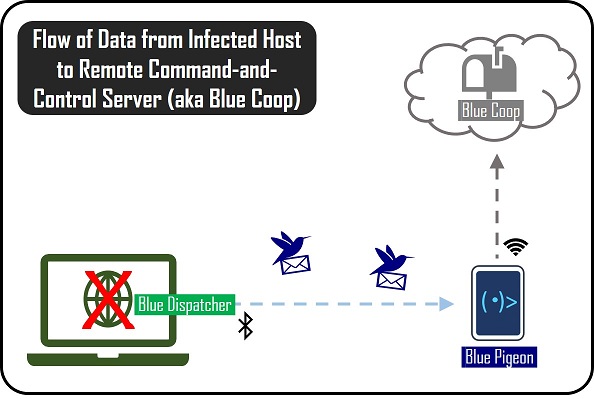
Blue Pigeon runs as a foreground service within an Android mobile phone. When the Red Teamer/Malicious Insider deploys the phone into proximity to the compromised host (infected with Blue Dispatcher payload), Blue Pigeon will be able to serve as an exfiltration point and command relay proxy to a remote C2 server (a.k.a Blue Coop).
Click here for a demo video of Blue Pigeon in action
Blue Pigeon was engineered with the following key requirements:
Blue Pigeon must allow data exfiltration while evading detection on various levels:
Evading network traffic detection: Data exfiltration from the compromised host cannot go through traditional communication channels as they are likely to be logged and monitored by standard Endpoint Detection and Response. (and there already are many other better options, why reinvent the wheel, right?)
Evading human detection: Data exfiltration must happen without any visual indicators on the victim's machine, as he is expected to still be using the compromised machine in the worst-case scenario.
Blue Pigeon must maintain stealth, i.e. staying inconspicuous deployed on the field.
Chunky laptops, Raspberry Pis and homebrew hacker kits are a straight No-Go as it limits the possibilities and feasibility of deployment. We need a small and innocent looking pigeon, not a freakin' alpha male peacock!
Blue Pigeon hides within a typical Android phone that the Red Teamer/Malicious Insider can bring into the field. No one ever suspects a mobile phone...
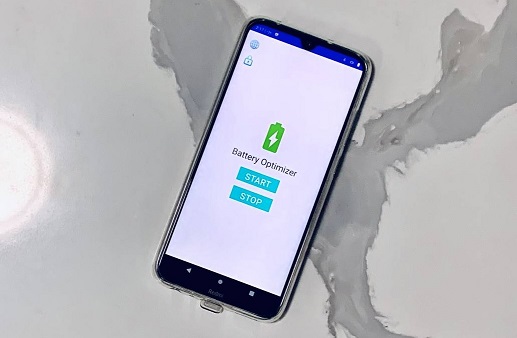
In the rare event where the Red Teamer is challenged for inspection, Blue Pigeon can be disguised as an inconspicuous application to suit the context of the operation. In the base proof-of-concept, the mobile application is disguised as a Battery Optimizer app. Feel free to fork the repo and take Blue Pigeon out for an aesthetic makeover!
Blue Pigeon should avoid causing the Red Teamer to reveal any tell-tale signs of an exfiltration attempt while deploying the phone.
The Red Teamer only needs to launch the application and bring the phone within proximity of the compromised machine.
Blue Pigeon runs in the background of the mobile phone and does not require the screen to be kept active.
Blue Pigeon automatically consumes incoming messages and does not require the Red Teamer to manually accept the file transfer request pop-up (it won't even pop up actually).
Blue Pigeon must maintain maximum availability to (and only to) the compromised host while being deployed.
Blue Pigeon must be able to stay alive to catch incoming messages without regular intervention by the Red Teamer.
Blue Pigeon must be able to withstand malicious requests/DoS attempts and maintain availability to the intended host.
Blue Pigeon is capable of permanently staying in discoverable mode for the compromised host to scan and connect to.
HMAC-based authentication and filename randomization are employed to mitigate against DoS and replay attacks. Blue Pigeon only accepts the file transfer requests after authenticating with a configurable secret passphrase.
Blue Pigeon is designed as a three-part framework comprising of following the components:

