
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-49113-Checker — Checks if a system is potentially vulnerable to CVE-2024-49113 (LDAP Nightmare) by testing RPC connectivity, LDAP ports, Netlogon service, and LDAP callback verification. | Kitploit
Tools/GitHubGitHub/barcrange/cve-2024-49113-checker
Vulnerability ScannersVulnerability AnalysisInformation GatheringNetwork SecurityPenetration Testing
GitHubbarcrange/cve-2024-49113-checker

CVE-2024-49113-Checker

Checks if a system is potentially vulnerable to CVE-2024-49113 (LDAP Nightmare) by testing RPC connectivity, LDAP ports, Netlogon service, and LDAP callback verification.

View Repository
1061 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2024-49113-Checker

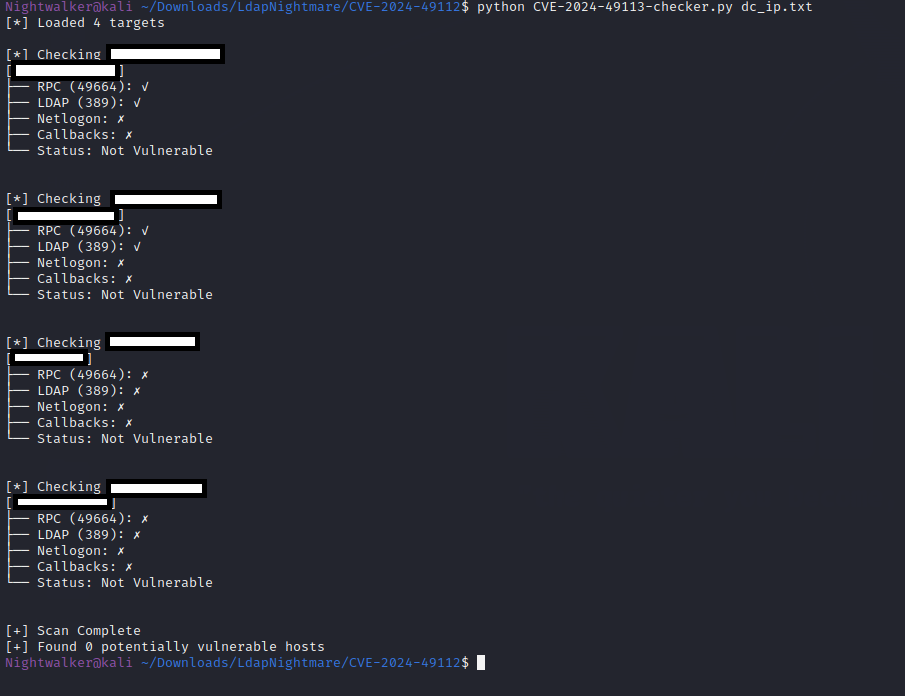
Script to test whether your environment is potentially vulnerable to CVE-2024-49113 (LDAP Nightmare). This script performs:
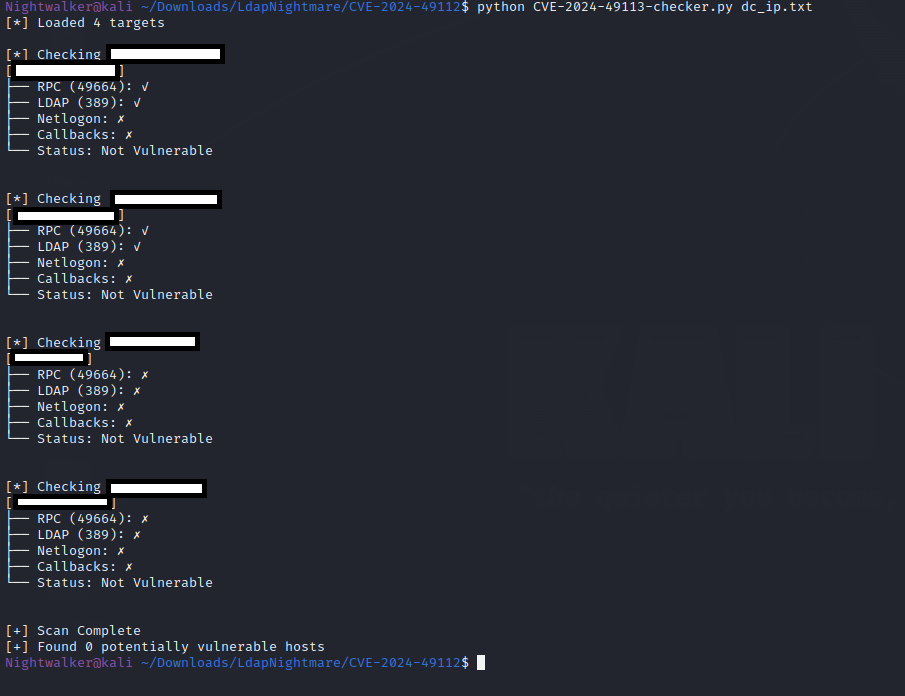
  • RPC connectivity checks
  • LDAP port tests
  • Netlogon service validation
  • LDAP callback verification

picha

root@kitploit:~
usage : python CVE-2024-49113-checker.py <target>
root@kitploit:~
Example
 # Scan a single IP
python CVE-2024-49113-checker.py 192.168.1.1

# Scan a subnet
python CVE-2024-49113-checker.py 192.168.1.0/24

# Scan from a file
python CVE-2024-49113-checker.py ips.txt -o vulnerable_hosts.txt

Note: This tool does NOT exploit the vulnerability; it only checks for conditions that may make exploitation possible.

Download Tool